

Claude Code Adds AGENTS.md Fallback, Cutting Instruction File Sprawl
Claude Code now supports AGENTS.md, giving development teams a shared instruction format across multiple AI coding agents and reducing configuration drift.
GitHub Separates Who Writes Code From Who Runs Your CI
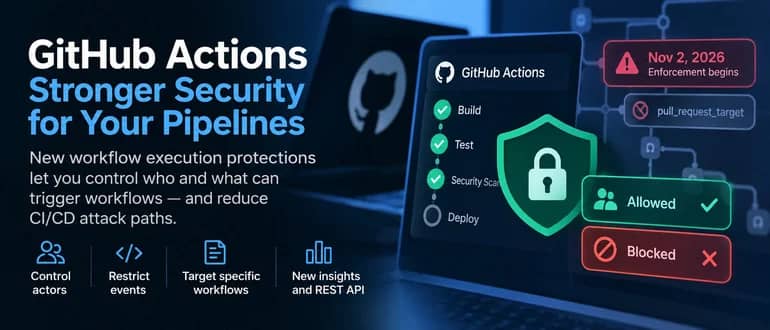
GitHub’s new workflow execution protections let teams control who and what can trigger Actions workflows, reducing CI/CD attack paths and tightening pipeline security.
Anthropic Adds a Coordinator to Claude Projects for Running AI Work in Parallel
Anthropic’s redesigned Claude Projects coordinates parallel Claude Code sessions, delegates work across branches and brings the results back through familiar pull-request review workflows.
Java 27 Tackles Post-Quantum Security and a Faster Patch Cadence
Java 27 strengthens enterprise security with monthly critical patch updates and post-quantum TLS 1.3 support, helping organizations prepare for AI-driven threats and future quantum risks.
More JFrog Artifactory Bugs Are Under Attack, and All Three Have Patches
Attackers are actively exploiting three JFrog Artifactory flaws, exposing how slow patching can turn artifact repositories into software supply chain attack paths.
GitLab’s Critical Patch Closes a Path Traversal Flaw Attackers Are Already Probing
GitLab patches two critical flaws, including a CVSS 10.0 unauthenticated file-read vulnerability, putting self-managed instances under urgent pressure to upgrade.
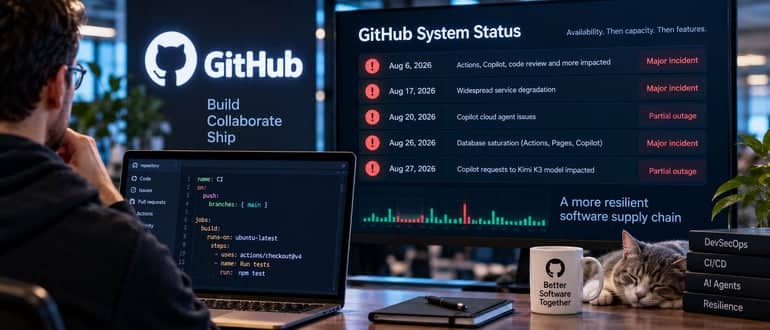
GitHub’s August Outages Show Growth Is Outpacing Infrastructure
GitHub’s August 2026 report details five outages tied to Actions and Copilot growth outpacing infrastructure. Here’s what platform teams should know.
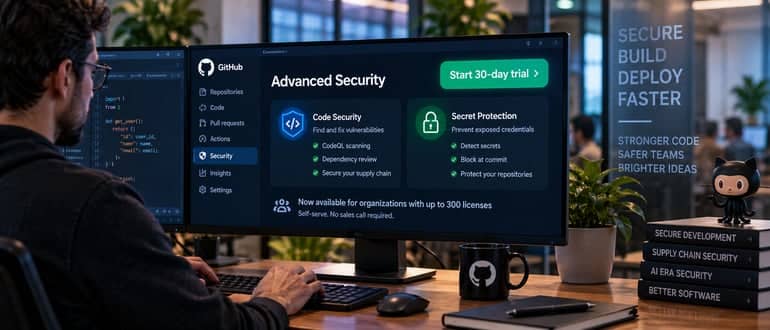
GitHub Widens the Door on Advanced Security Trials
GitHub raised its self-serve Advanced Security trial cap from 100 to 300 licenses, letting more mid-size Enterprise Cloud orgs test for free.
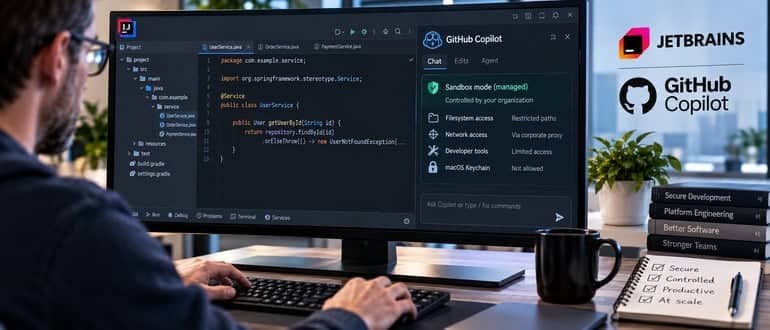
GitHub Puts Guardrails on Copilot’s Sandbox Inside JetBrains IDEs
JetBrains IDEs are where a lot of enterprise backend work happens — Java, Kotlin, Spring, big monorepos with a lot to break. So when an AI coding agent starts running shell commands inside that environment, the question isn’t whether it’s useful. It’s what happens if it touches the wrong file, the wrong network path, or […]
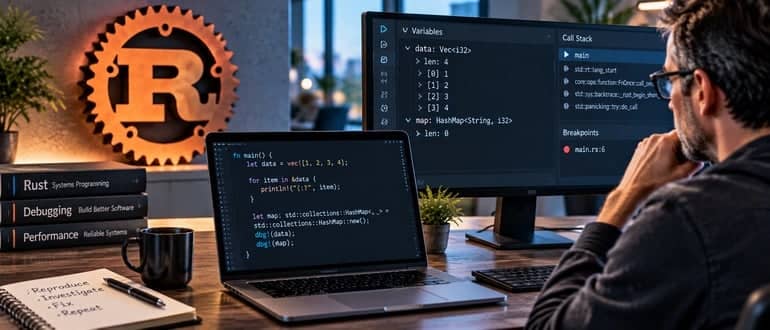
Rust’s First Debugging Survey Shows Most Developers Skip the Debugger Entirely
Most Rust developers don’t use a debugger. That’s the headline finding from the Rust compiler team’s first dedicated debugging survey, and it’s worth sitting with for a second. Rust has spent years building a reputation as the language that catches your mistakes before you ship them. The compiler is famously strict. The type system is […]
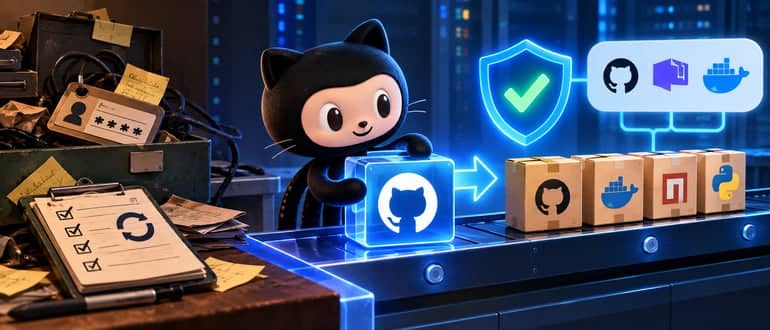
GitHub Quietly Fixes One of Dependabot’s Oldest Headaches
GitHub Dependabot can now authenticate to GitHub-hosted package registries without personal access tokens, reducing credential management and supply chain security risk.
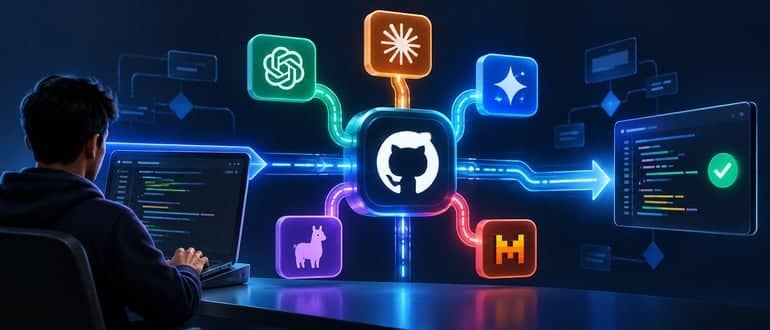
GitHub’s New Copilot Feature Takes the Guesswork Out of Picking AI Models
GitHub’s Project HydraFusion brings multi-model orchestration to Copilot, automatically routing coding tasks across AI models to balance quality, cost and complexity.
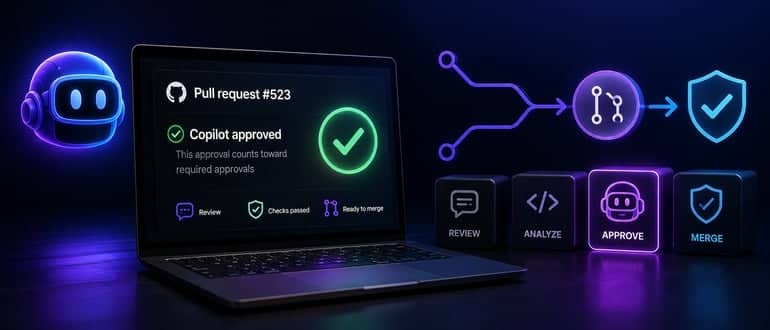
GitHub Puts Copilot in the Approval Seat for Pull Requests
GitHub Copilot can now submit binding pull request approvals, moving AI code review from advisory feedback into the merge decision itself.
Debian’s AI Vote Bets on Accountability Instead of a Ban
Debian’s new AI contribution policy avoids bans and mandatory disclosure, instead making developers responsible for reviewing AI-generated work and protecting sensitive data.
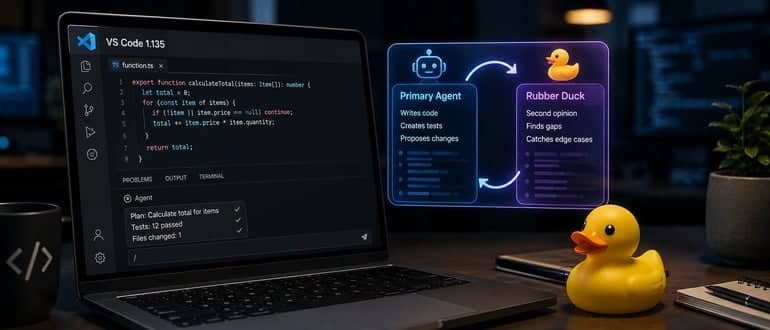
VS Code 1.135 Gives AI Coding Agents a Second Opinion
VS Code 1.135 adds Rubber Duck AI review, persistent agent sessions, Agent Host infrastructure and clearer token usage as Microsoft builds a more agentic IDE.
A Simple Website Summary Just Exposed the Limits of AI Coding Guardrails
Claude Code’s Auto Mode was bypassed in an attack chain that turned a routine webpage summary into remote code execution, highlighting the limits of AI agent guardrails.
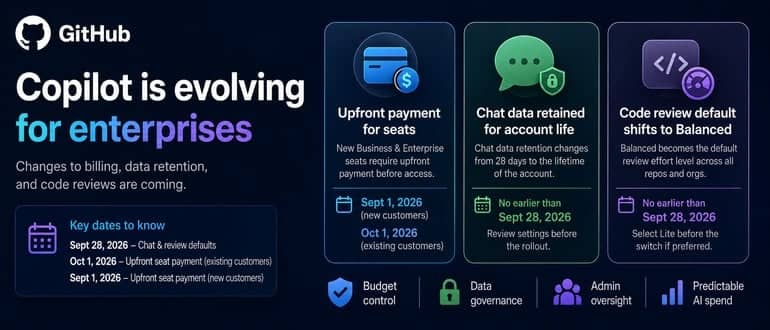
GitHub Tightens Copilot’s Billing and Governance Rules Ahead of a Busy Fall
GitHub Copilot is tightening enterprise controls with upfront seat billing, longer chat retention and a Balanced code review default.
npm v12 Shuts Down a Popular Malware Trick — But the Threat Isn’t Going Away
For years, one of the easiest ways to sneak malware onto a developer’s machine has been to hide in plain sight. Install a package from npm, and any lifecycle script bundled with it runs automatically — no review, no approval, no second look. Attackers have known this for a long time, and they’ve used it […]
AI Agents Are Writing Code Faster Than Anyone Can Review It. Tessl Is Betting On Standards To Close That Gap
Every team that has turned coding agents loose on real work has run into the same wall. The agents write fast. They write a lot. And somewhere between the tenth and twentieth pull request of the day, the humans responsible for reviewing that code start falling behind. That’s not a hypothetical. It’s the operating reality […]
GitHub Sharpens CodeQL’s Eye on Actions Workflows and Modern JavaScript
GitHub Actions pipelines have become one of the quieter attack surfaces in software development. They pull in third-party actions, cache dependencies, and pass secrets between jobs, often without anyone reviewing the workflow file as closely as they’d review application code. That gap is exactly where cache-poisoning and output-clobbering attacks live, and it’s why GitHub keeps […]
LangChain’s dcode Isn’t New. Its Governance Play for Sensitive Code Is
Enterprises are running into the same wall with AI coding agents: the tools that write code fastest are usually the ones IT trusts least with sensitive codebases. Legacy modernization projects — COBOL migrations, .NET upgrades, decade-old frameworks nobody wants to touch by hand — are exactly where agentic coding tools could help most, and exactly […]
Claude Code’s Temporary Usage Boost Expires Tonight. Here’s What Actually Changes
Anthropic’s temporary 50% increase to Claude Code weekly usage limits expires August 19, reducing available capacity for developers and DevOps teams without lowering subscription prices.
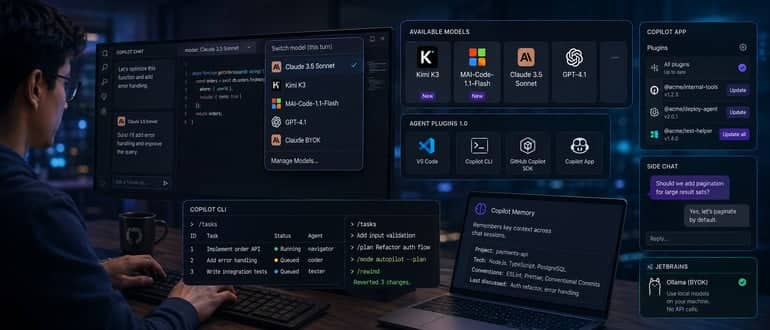
GitHub Copilot’s Latest Update Bets on Model Choice, Not Model Loyalty
GitHub’s latest Copilot updates add Kimi K3, MAI-Code-1.1-Flash, Agent Plugins 1.0, model switching, CLI improvements, and local Ollama support.