
 AI
Beyond SLSA and Sigstore: Securing the Developer Origin in the Age of Agentic Coding
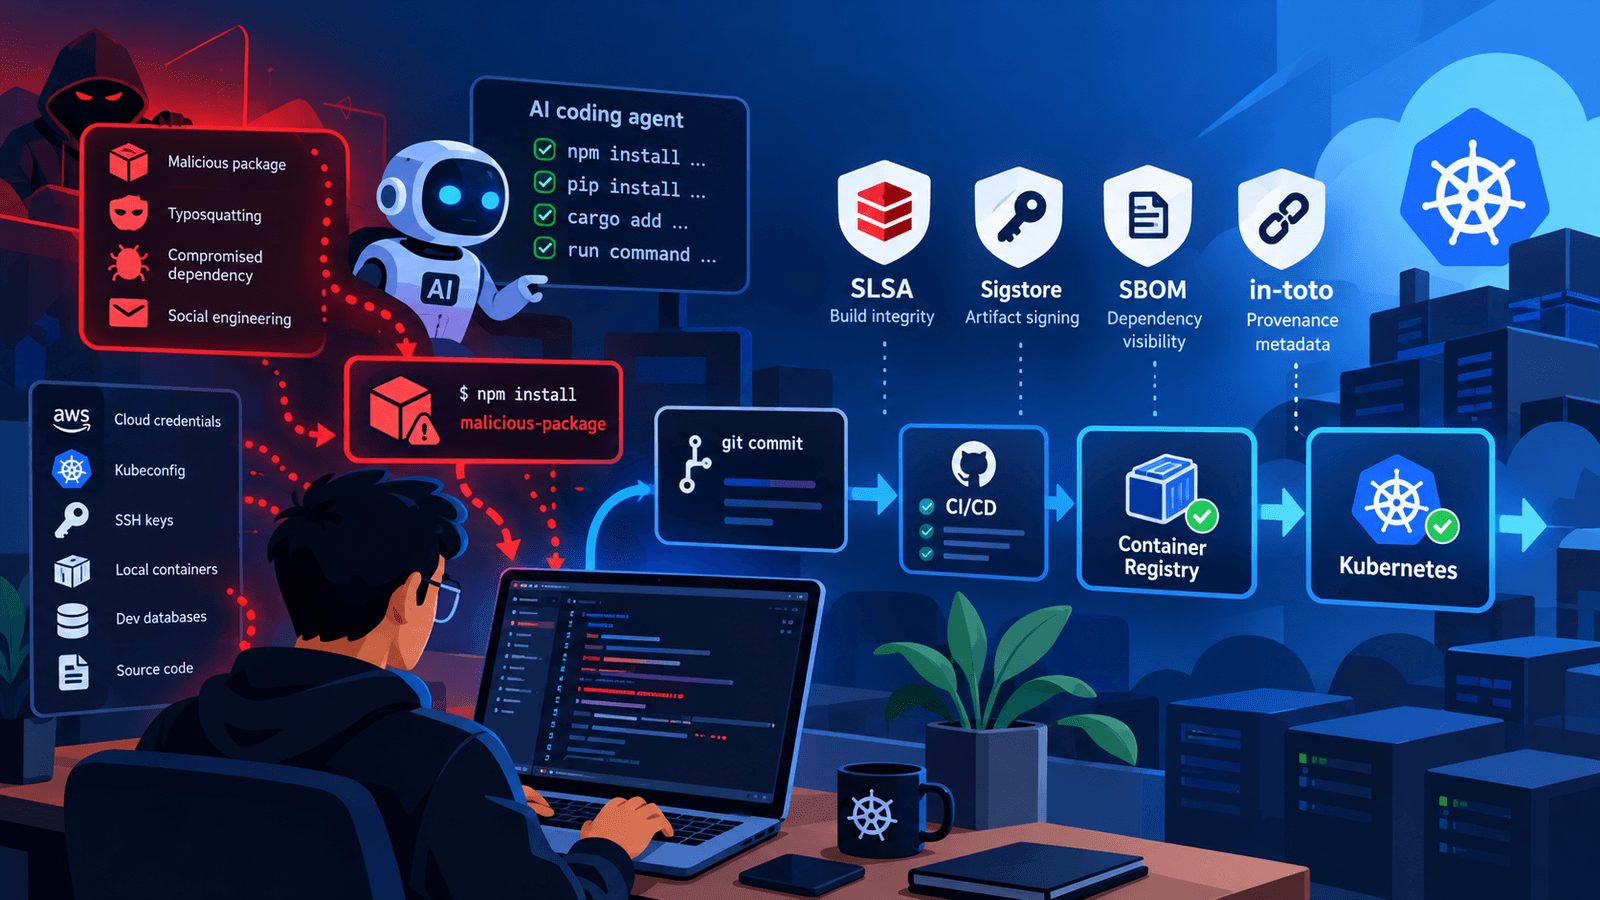
SLSA, Sigstore and SBOMs have strengthened software supply chain security, but attackers are increasingly targeting developer workstations before code reaches the CI/CD pipeline. With autonomous AI coding agents installing dependencies, executing commands and accessing sensitive credentials, endpoint security is becoming a critical cloud-native concern. Securing the software supply chain now requires protection from the developer’s IDE all the way to Kubernetes production workloads.