

AWS Delivers AI Service to Discover Vulnerabilities and Generate Patches
Amazon Web Services (AWS) has made generally available a service through which it finds and validates code vulnerabilities and provides a patch that DevSecOps teams can then automatically apply or set up a pull request to implement. Dr. Neha Rungta, director of applied science at AWS, said the AWS Continuum service for code vulnerabilities is […]
Why Continuous Vulnerability Management Belongs in Every DevSecOps Strategy
DevSecOps is part of the larger shift-left IT paradigm, which aims to identify and address vulnerabilities before they lead to security incidents. NIST’s guidance on secure software development emphasizes integrating security throughout the development lifecycle, rather than treating it as a separate concern addressed late in development or after deployment. By prioritizing a proactive approach […]
Gheist Hackers Abuse GitHub Tokens to Steal Repository Secrets
The evolving Gheist campaign uses stolen GitHub tokens and malicious Actions workflows to extract repository secrets and cloud credentials. While GitHub protections have blocked observed attacks on public repositories, private environments remain exposed.
Hackers Inject Credential-Stealer, RAT Into LiteLLM
Attackers compromised a version of LiteLLM this week by injecting malicious code into all seven of its published Python wheels on PyPI, delivering a package that included an infostealer to exfiltrate credentials and secrets and a remote access trojan (RAT) that could let bad actors run arbitrary code on infected machines. The compromised version – […]
GitHub Puts a Firewall Between npm and Your CI Runners
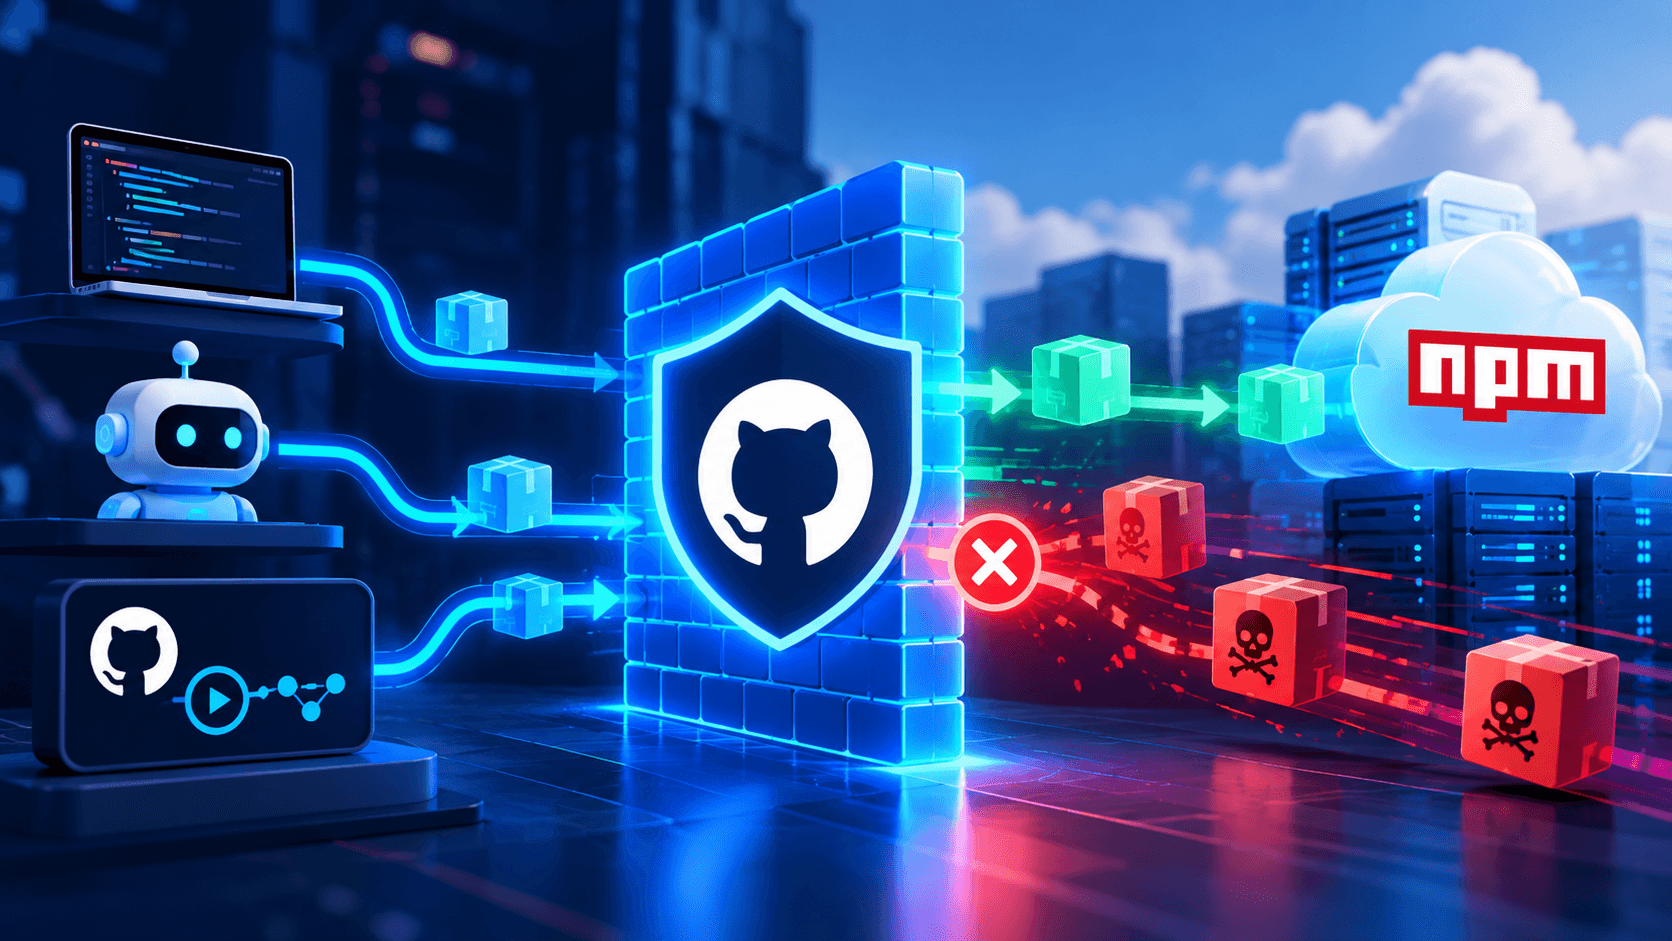
GitHub’s new package firewall puts enterprise security policies between npm registries and the developers, CI runners and AI coding agents consuming packages. With malware detection, attestation checks and package-age restrictions, it aims to stop malicious dependencies before installation.

Cohere Plans to Acquire Aisle to Add AI-Powered Code Security
Enterprise AI platform provider Cohere announced it has signed a letter of intent to acquire Aisle, a cybersecurity startup whose AI agent platform discovers source-code vulnerabilities and generates proposed fixes. The proposed acquisition would also establish a dedicated cybersecurity business called Cohere Cyber. Aisle’s platform analyzes software for previously unknown vulnerabilities, validates potential findings, evaluates […]
Chainguard Debuts a Security-First Agent Platform
Open source security company Chainguard has released Workspaces, a service designed to provide a safe space for agents to do their thing without disrupting the security of existing operations. The market for platforms to host agents is large and growing daily, though Chainguard’s expertise in security solves a major problem with running agents, namely managing […]
Survey: Lack of Confidence in Software Supply Chain Security Runs High
A survey of 400 platform and security engineers in the U.S and United Kingdom (UK), finds nearly three quarters (73%) are either only moderately confident (58%) or not confident (15%) in the ability of their existing tools for managing software artifacts to prevent attacks against their organization’s software supply chain. Conducted by Cloudsmith, a provider […]
Blitzy Makes Sandbox for Reverse Engineering Code Available at No Cost
Blitzy has made available a sandbox where DevOps teams can reverse-engineer up to one million lines of code, generate up to 25,000 lines of tested end-to-end code, and identify security vulnerabilities across a codebase at no cost. Dan Ochs, director of AI solutions consulting for Blitzy, said the provider’s Proactive Insights platform uses multiple artificial […]
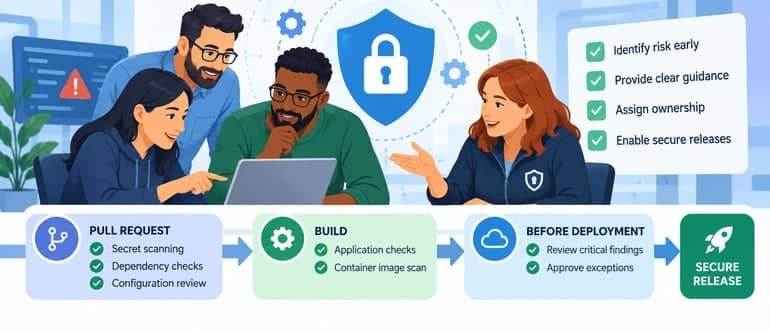
DevSecOps Teams as Partners in Secure Software Delivery
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable.
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee.
New npm Threat Bypasses Install Script Protections
A malicious npm package that has been downloaded millions of times comes with a new way of spreading the malware that makes it easier to bypass security protections, say researchers with security vendor Checkmarx. Rather than using more common preinstall or postinstall scripts, the bad actors instead created a malicious package – indexed-btree – that […]
Harness Previews Revamped Platform for the Agentic Engineering Era
Harness today previewed a revamped user interface for its platform for managing software deployments that makes it simpler for software engineers to manage teams of artificial intelligence (AI) agents using a forthcoming Harness Software Factory platform. Speaking at an {unscripted} NYC 2026 event, Harness CEO Jyoti Bansal told conference attendees the Harness Software Factory will […]
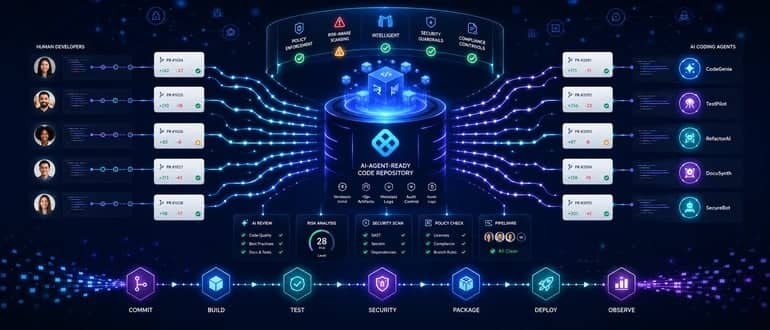
Flaw in DeepSeek Harness AI Coding Tool Let Agents Disable Their Sandbox
News of the now-fixed vulnerability comes amid growing concerns that AI vendors do not in have complete control of their autonomous agents.
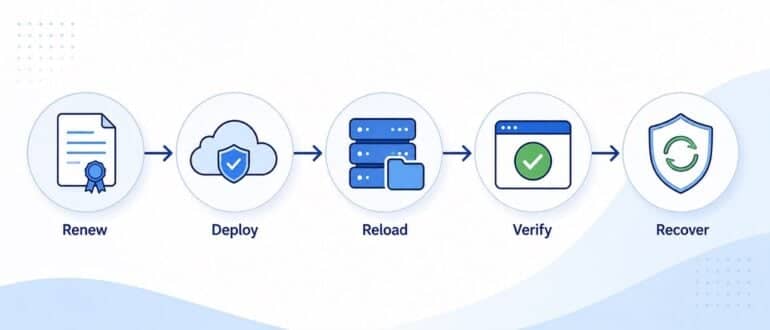
Certificate Renewal Is a Deployment Workflow, Not a Cron Job
Certificate renewal is often treated as a scheduled task: run an ACME client, obtain a new certificate, and move on. In practice, that view is too narrow for production systems. A certificate is not useful because it exists on disk. It is useful because the right service is presenting it to users. Between issuance and […]
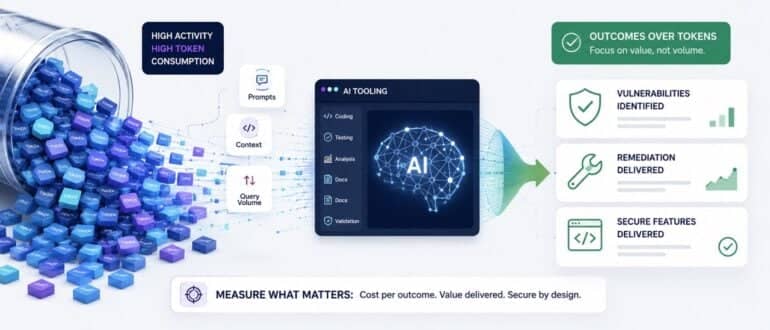
Why “Tokenmaxxing” Was Always the Wrong Way for Developers to Measure AI Productivity
The term “tokenmaxxing” left the developer lexicon just as quickly as it arrived, and like most viral technology concepts, it means different things depending on who’s using it. In practice, the term is being applied in two ways: maximizing total token consumption as a proxy for AI adoption and effort, or optimizing output per token […]
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets developers whitelist particular built-in Node modules or limit what the script can access. During that time, vm2 has been the default for safely […]
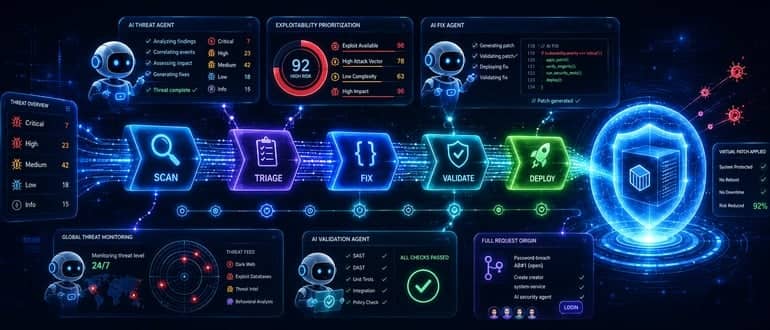
Harness Adds AI Agents to Automate DevSecOps Workflows at Machine Speed
Harness today added multiple artificial intelligence (AI) agents and a virtual patching capability to its portfolio to automate DevSecOps workflows at a time when the number of vulnerabilities being discovered in code continues to exponentially increase. The AI agents include one that has been added to the static application security testing (SAST) tool that Harness […]
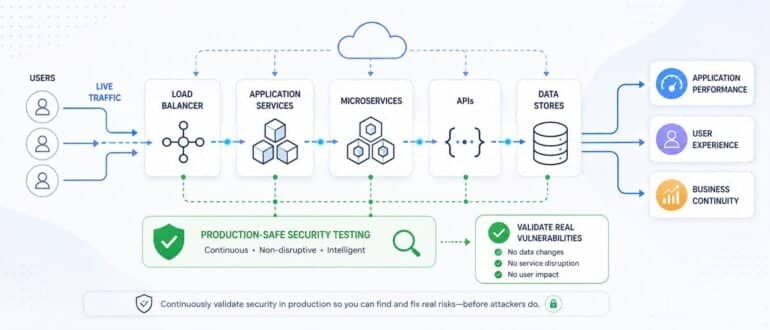
Production-Safe Testing: The Missing Piece in Most DevSecOps Strategies
Most DevSecOps teams invest heavily in security before deployment, yet attackers target the production environment where applications, APIs, and user behavior are constantly changing. If security validation stops before release, critical risks can remain hidden until they are exploited. The gap is more common than many organizations realize. A survey found that over 70% of […]
LiteLLM Attack Affected 2,500 Companies, 434,000 CI/CD Pipelines: CloudSEK
The massive supply-chain attack that compromised LiteLLM in the spring affected more than 2,500 companies and exposed about 434,000 CI/CD pipelines, with victims ranging from top-tier IT and AI companies to cybersecurity firms, SaaS, and enterprises. It rolled up a lot of victims, but also was a high-profile example of the growing trend of threat […]
‘Flooding Dropper’ Is Hitting npm With a Tidal Wave of Malicious Packages
Threat researchers at Sonatype are warning developers of an expanding campaign that is generating a wide range of npm accounts and dropping small numbers of malicious packages from each one, essentially flooding the zone with a broadly distributed and automated campaign to make it difficult for defenders to keep up. So far, the campaign – […]
RapidFort Extends Open Source Software Security Reach to Runtime Environments
RapidFort today at the Black Hat USA conference announced it has extended its ability to secure open source software to the runtimes that DevOps teams deploy in production environments. Michael Wood, chief marketing officer for RapidFort, said the RapidFort Runtime platform makes it possible to now monitor open source software deployed within a container image […]
Fast-Moving Shai-Hulud Attack Infects npm Packages with 2 Billion Monthly Downloads
Researchers at Aikido Security and Endor Labs are tracking a fast-spreading supply-chain attack that is compromising a wide range of npm software packages that combined have more than 2 billion installs a month and is stealing a wide range of secrets and other information. According to Ilyas Makari, malware researcher with Aikido, the bad actor […]