


Perforce Applies Machine Learning to Generate Synthetic Data for App Testing
Perforce Software has added a tool that leverages artificial intelligence (AI) to make it simpler for application development teams to generate synthetic data for application testing purposes. Mayank Ahluwalia, a senior product manager for Perforce Delphix, said Delphix Synthetic Data makes use of machine learning algorithms to generate synthetic data for specific use cases. It […]

Blitzy Makes Sandbox for Reverse Engineering Code Available at No Cost
Blitzy has made available a sandbox where DevOps teams can reverse-engineer up to one million lines of code, generate up to 25,000 lines of tested end-to-end code, and identify security vulnerabilities across a codebase at no cost. Dan Ochs, director of AI solutions consulting for Blitzy, said the provider’s Proactive Insights platform uses multiple artificial […]

Talentica Software Unfurls Managed AI Service to Optimize Software Delivery
Talentica Software this week launched a managed software delivery service that leverages artificial intelligence (AI) to enable DevOps teams to deploy applications developed using AI coding tools at scale. Company CTO Manjusha Madabushi said the DevX AI Pods service makes use of a set of AI agents that Talentica has trained to provide the context […]

New npm Threat Bypasses Install Script Protections
A malicious npm package that has been downloaded millions of times comes with a new way of spreading the malware that makes it easier to bypass security protections, say researchers with security vendor Checkmarx. Rather than using more common preinstall or postinstall scripts, the bad actors instead created a malicious package – indexed-btree – that […]
StackHawk Delivers Wingman to Fix Vulnerabilities as Developers Write Code
StackHawk this week launched Wingman, an artificial intelligence (AI) tool that makes it possible for application developers to automatically fix vulnerability issues as code is being written. Wingman is designed to install into Claude Code, Cursor, GitHub Copilot, Codex, and Antigravity. It scans the live application, interprets findings, and fixes vulnerabilities in a way that […]
Test Creation Was Never the Bottleneck
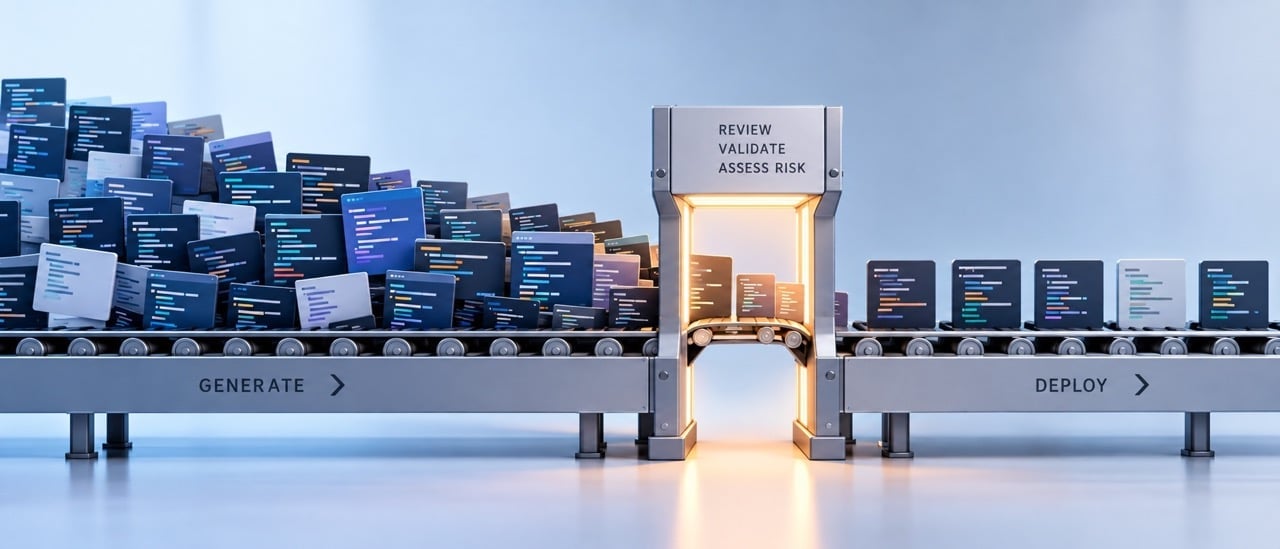
Something specific happened to software delivery in the past two years. The 2026 survey data is unusually clear about what it was. Sonar’s 2026 State of Code Developer Survey found that AI-generated or AI-assisted code accounted for 42% of code committed by respondents, with developers projecting that share to reach 65% by 2027. GitLab’s 2026 […]

Tricentis Preps Wave of Additional AI Testing Capabilities
Tricentis is providing early access to multiple artificial intelligence (AI) capabilities that it is gearing up to roll out later this year via a Tricentis Transform initiative, including an autonomous AI agent, dubbed Aida, that explores web and Windows desktop applications to surface defects, weaknesses and other potential gaps without requiring DevSecOps teams to create […]

CI/CD for AI-Enabled Applications: Why Traditional Deployment Pipelines Need to Evolve
Traditional CI/CD pipelines are optimized around a familiar assumption: source code changes, automated tests validate the change, a build artifact is produced, and the application is promoted through environments. AI-enabled applications complicate that model because production behavior can change even when application code does not. A new model version, feature transformation, prompt configuration, retrieval index […]

Why Self-Healing Tests Need a Deployment Gate
When an end-to-end test fails after a front-end change, the repair often looks routine. A class name changed. A button moved. A selector that used to be unique now matches two elements. A self-healing system inspects the page, proposes a new locator, reruns the test, and gets a green result. That green result is useful, […]

Harness Adds AI Agents to Automate DevSecOps Workflows at Machine Speed
Harness today added multiple artificial intelligence (AI) agents and a virtual patching capability to its portfolio to automate DevSecOps workflows at a time when the number of vulnerabilities being discovered in code continues to exponentially increase. The AI agents include one that has been added to the static application security testing (SAST) tool that Harness […]
Production-Safe Testing: The Missing Piece in Most DevSecOps Strategies
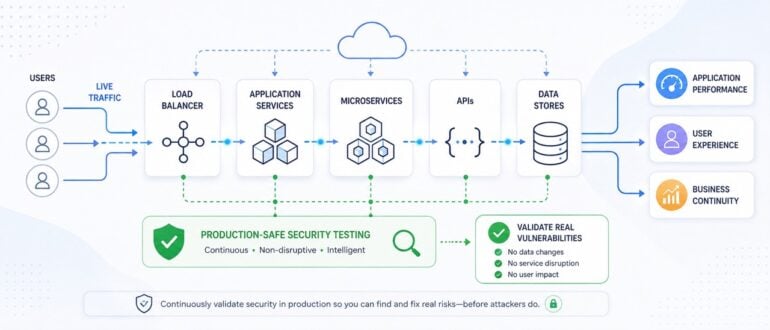
Most DevSecOps teams invest heavily in security before deployment, yet attackers target the production environment where applications, APIs, and user behavior are constantly changing. If security validation stops before release, critical risks can remain hidden until they are exploited. The gap is more common than many organizations realize. A survey found that over 70% of […]

ProjectDiscovery Brings Open Source AI Testing to Vulnerability Discovery
ProjectDiscovery has made available an autonomous security testing platform that leverages an open source artificial intelligence (AI) testing framework to detect and validate vulnerabilities at a lower total cost. Company CEO Rishi Sharma said version 1.0 of the Neo platform is also available via a cloud service that makes it possible for DevSecOps teams to […]
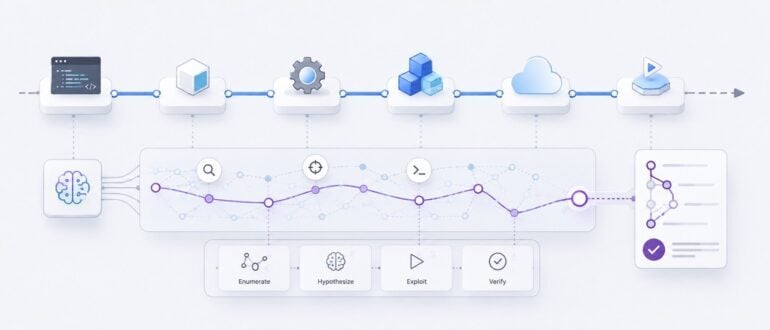
Why CI/CD Security Testing Is Going Autonomous (and Why It Should Stay Local)
Continuous integration and delivery changed the tempo of software. Teams merge dozens of times a day, infrastructure is redefined on every commit, and a new build can reach production in minutes. Security testing never caught up with that tempo. It still lives in two modes that both fight the pipeline instead of moving with it. […]

Survey Surfaces Rising Tide of Production Issues Traced Back to AI Code
A survey of 400 business and engineering executives finds 80% have traced a production incident, outage, or customer-impacting defect to code generated by artificial intelligence (AI) tools in the past 12 months. Conducted by Wakefield Research on behalf of Sauce Labs, a provider of an application testing platform, the survey finds 83% of respondents work […]
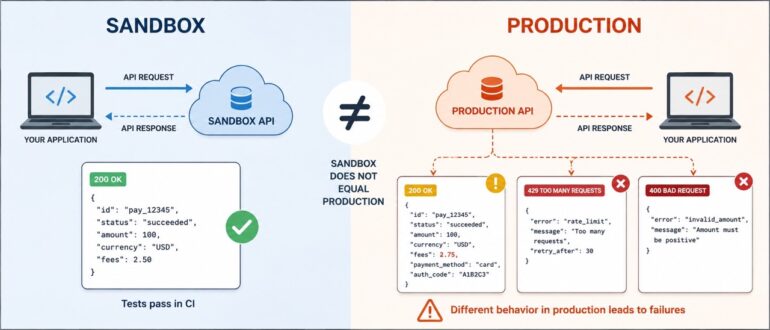
Sandbox Testing for API-Heavy Systems: What Changes When You Don’t Own the Dependency
Sandbox testing works well when your team controls both sides of the integration. You define the service, you define the mock, you know exactly what the sandbox should return. That setup holds up fine for internal microservices and first-party APIs. It starts to break down when you don’t own the dependency. Payment processors, identity providers, […]

Fast-Moving Shai-Hulud Attack Infects npm Packages with 2 Billion Monthly Downloads
Researchers at Aikido Security and Endor Labs are tracking a fast-spreading supply-chain attack that is compromising a wide range of npm software packages that combined have more than 2 billion installs a month and is stealing a wide range of secrets and other information. According to Ilyas Makari, malware researcher with Aikido, the bad actor […]

Tricentis Acquires Tabnine to Gain Knowledge Graph for AI Testing Agents
Tricentis today revealed it is acquiring Tabnine to gain access to a knowledge graph that will be used to provide context to AI agents that have been trained to automate a range of testing tasks. Once the acquisition is complete, Tricentis plans to integrate the knowledge graph developed by Tabnine, dubbed the Enterprise Context Engine, […]

Validation Debt That Your Dashboards Are Not Showing
The gap between how fast AI writes code and how reliably teams verify it is quietly becoming a balance-sheet risk. Enterprise leaders are learning to measure it before it forces repayment. Every engineering organization that adopted AI coding assistants over the past two years has quietly taken on a liability that never appears on the […]

FakeGit Targets AI Coding Agents with Malicious GitHub Repos
Threat actors continue to find new ways to incorporate AI into schemes aimed at luring developers into downloading malware from fake repositories. The latest example involves almost 7,600 malicious GitHub repositories that are being used to distribute a loader and an information-stealer. The FakeGit campaign is nothing new, with Oleg Zaytsev, lead security researcher with […]
AI-Native Testing Is Now a Core Quality Engineering Discipline
Predictions from some of the most prominent voices in the technology industry suggest that software engineering could become increasingly obsolete within a year, jolting the developer community in ways that are still unfolding. The ripple effect spreads further across social media and news outlets, with some leaders urging developers to start seriously considering alternative career […]
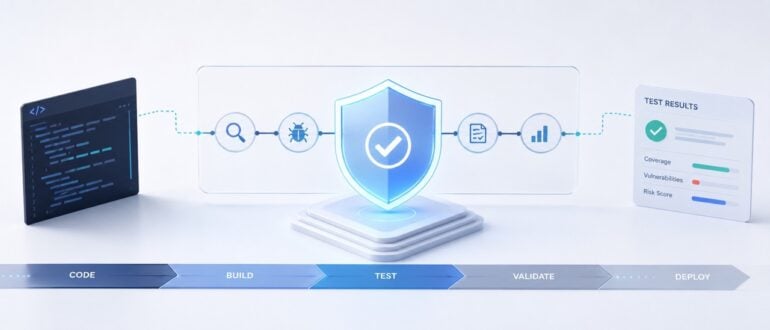
Why You Need AI Agent Security Validation in Software Testing
Engineering teams have been racing for the last two years to deploy AI agents that can find bugs faster than any QA team ever could. Autonomous testing agents can crawl through codebases, identify vulnerabilities, and generate test coverage reports while developers finally get to take a breath. The irony is that while development teams enjoy […]

SmartBear Tightens Integration Between AI Coding and Testing Tools
SmartBear this week revealed it is narrowing the divide between coding and testing by integrating its platform with artificial intelligence (AI) coding tools. Sheryl Koenigsberg, senior vice president of product marketing at SmartBear, said integrations with AI coding tools from Anthropic, Atlassian, GitHub, and Amazon Web Services (AWS) will make it simpler for application developers […]

From AI Hype to AI Assurance: How Engineering Teams Can Safely Ship AI-Enabled Software
AI has moved very quickly from experimentation to production. A few years ago, many organizations were still asking whether AI could improve their products or internal workflows. Today, the question is different: how can teams ship AI-enabled software safely, reliably, and responsibly? That shift matters because AI is no longer just a research project or […]