

Agentic CI/CD is Not Automation: Why the Distinction Will Define DevOps in 2026
There is a dangerous conflation happening across our industry right now. Teams are plugging LLM-powered agents into their deployment pipelines, calling it “agentic CI/CD,” and treating it as the next logical step after shell scripts and Terraform modules. It is not. Automation executes predefined instructions. An agent reasons about context, makes decisions, and takes actions […]
Bad Actor Drops 36 Malicious Packages in npm, Targets Guardarian Users
The npm code repository is again being used by a bad actor to launch a supply chain attack that includes three dozen malicious packages that appear as Strapi CMS plugins but deliver a range of threats. Strapi is a popular open source headless Node.js content management system developers use to build, manage, and expose content […]
Is Your AI Agent Secure? The DevOps Case for Adversarial QA Testing
Adversarial QA testing helps validate AI agents under real-world conditions, exposing risks like prompt injection and logic failures.
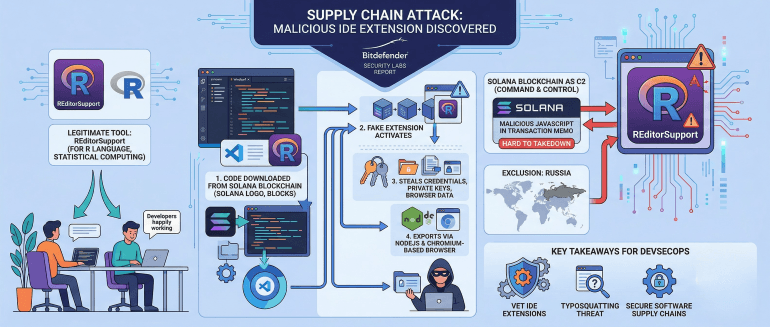
Latest Typosquatting Attack Targeting VS Code Tools Hits Windsurf IDE
Cybersecurity researchers from Bitdefender, a provider of an endpoint detection and response (EDR) platform, have discovered an extension to the Windsurf integrated development environment (IDE) that steals credentials and data after code is downloaded from the Solana blockchain platform. Silviu Stahie, a security analyst for Bitdefender, said the extension makes use of typosquatting tactics to […]
GitHub to Leverage User Code for AI Model Training, Allows Opt-Out
GitHub is preparing a significant change to how it trains the AI models behind its Copilot coding assistant. Beginning April 24, the Microsoft-owned platform will collect user interaction data by default to improve its AI systems, unless users actively disable the setting. The update applies to individuals using Copilot Free, Pro, and Pro+ tiers. Enterprise […]
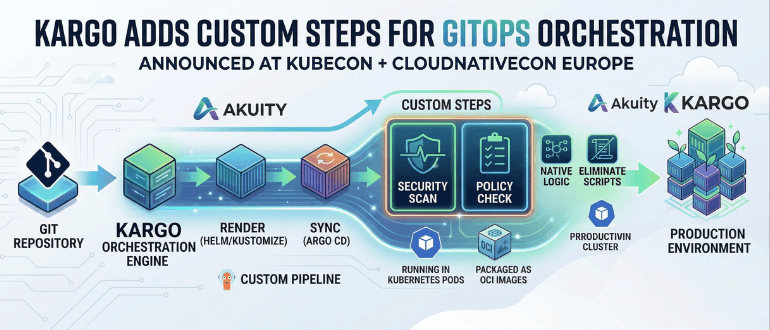
Akuity Adds Ability to Customize Kargo Pipelines
Akuity this week at the KubeCon + CloudNativeCon Europe conference revealed it has added an ability to customize the steps used to promote applications into a production environment using a Kargo orchestration engine it developed to manage software using a GitOps workflow. Company CEO Hong Wang said the Custom Steps capability added to Kargo will […]
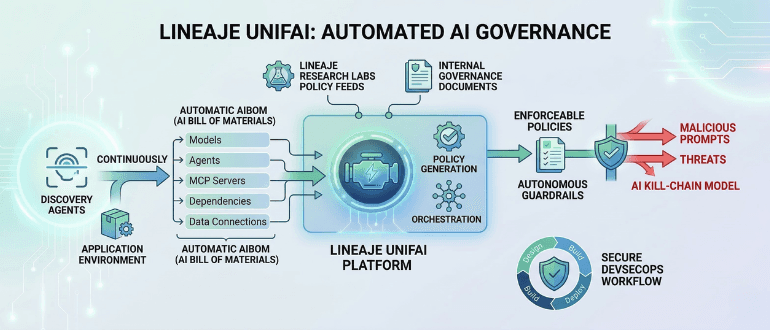
Lineaje Adds Ability to Automatically Apply Governance Policies to AI Components
Lineaje this week unfurled a platform that automatically discovers the artificial intelligence components of an application, defines security and governance policies, and then autonomously generates guardrails. At the core of the Lineaje UnifAI platform are a set of artificial intelligence (AI) capabilities that are integrated with an orchestration framework for applying governance policies that has […]
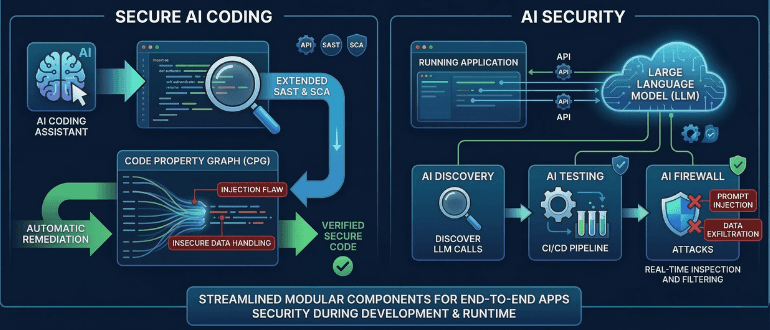
Harness Extends AI Security Reach Across Entire DevOps Workflow
Harness today added an ability to automatically secure code as it is being written by an artificial intelligence (AI) coding tool in addition to adding a module to its DevOps platform that discovers, tests, and protects AI components within applications. Secure AI Coding is an extension of the static application security testing (SAST) and software […]
The Green Side of Observability: Why Less Data Can Mean More Insight
Observability can generate massive data volumes. Learn how sustainable observability reduces telemetry waste, lowers costs and improves insight.
Zero Downtime Multicloud Migrations for Observability Control Planes
Most platform teams aren’t deciding whether they’ll run across multiple clouds. They already are, or they’ll be soon. The real question is how to migrate critical systems without turning on-call into a guessing game. Observability raises the stakes more than almost any other domain. An observability control plane isn’t just a dashboard. It’s the operational […]
How We Got Here: Alert Fatigue to Decision Fatigue
AI and observability reduced alert fatigue, but decision fatigue remains. Decision architecture helps DevOps teams scale operational judgment.
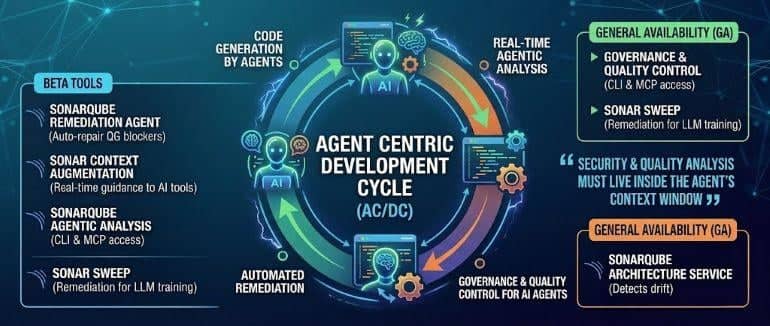
Sonar Unfurls Framework for Managing DevOps Workflows in the Age of AI
Sonar this week launched an Agent Centric Development Cycle (AC/DC) framework that promises to modernize continuous integration (CI) in the age of artificial intelligence (AI) coding. Announced at an online Sonar Summit, the AC/DC framework incorporates multiple tools and platforms the company has developed to better secure software supply chains, including now in beta Sonar […]
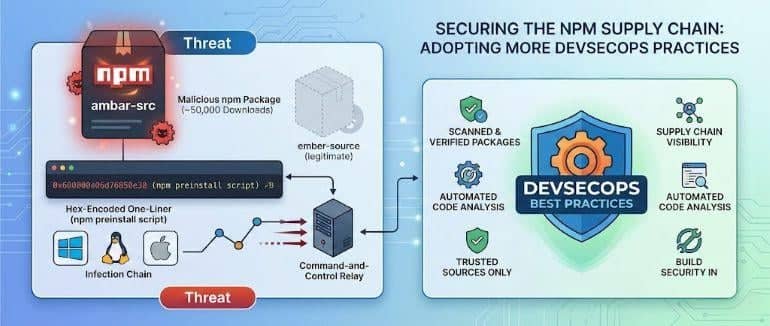
Malicious NPM Package Gets Downloaded 50K Times Before Discovery
A malicious package downloaded approximately 50,000 times from a node package manager (npm) is providing an object lesson for adopting more DevSecOps best practices. Security researchers from Tenable discovered a “ambar-src” package that was first published Feb. 13 and then updated again before being discovered. It is aimed at developers building JavaScript applications on Windows, […]
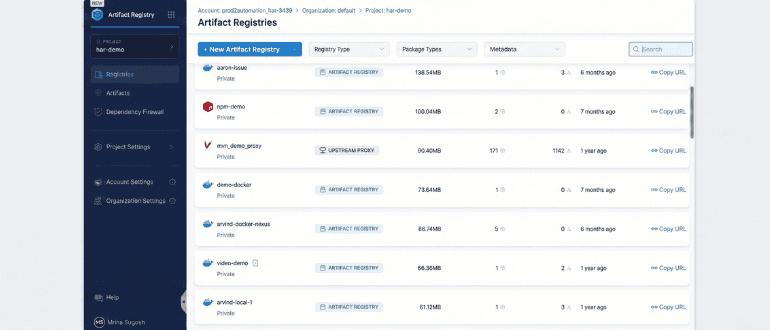
Harness Makes Registry for Integrating Artifacts into DevOps Workflows Available
Harness today made generally available an Artifact Registry it has added to its portfolio of DevOps tools and platforms. At the same time, Harness also revealed it has added a Dependency Firewall to the registry that enables DevSecOps teams to enforce controls at the point of ingestion. Rather than relying on downstream scans after a […]
GitOps Implementation at Enterprise Scale — Moving Beyond Traditional CI/CD
Traditional CI/CD pipelines hit scaling limits. Learn how GitOps improves deployment reliability, security, and DORA metrics—and what it takes to migrate successfully.
Checkmarx Extends Vulnerability Detection to AI Coding Tool from AWS
Checkmarx this week revealed it has added support for the Kiro artificial intelligence (AI) coding tool provided by Amazon Web Services (AWS) to its Checkmarx Developer Assist that leverages AI to surface vulnerabilities before code is committed. The Checkmarx IDE extension for Kiro is designed to be activated from within the Developer Assist tab that […]
Bridging the Dev–Security Gap With Smarter Authorization
Software teams have always lived with a built-in tension – developers push to ship fast, while security teams pump the brakes to assess risk. Now, with AI flooding the enterprise, that friction is spiking. One recent survey found a staggering 322% jump in privilege-escalation risks tied to AI-generated code. The root problem isn’t new – […]
Arcjet SDKs Make It Simpler for Developers to Include Security Functions
Arcjet this week made available a software development kit (SDK) that makes it simpler for JavaScript developers to embed capabilities such as bot detection, rate limiting, email validation, attack protection and data redaction directly within their applications. Company CEO David Mytton said the release of v1.0 of its Arcjet JavaScript SDK makes it possible for […]
CodeHunter API Integrates Deterministic AI Models into DevSecOps Workflows
CodeHunter, a provider of behavioral malware analysis and threat intelligence tools, today announced it is making available an application programming interface (API) to make it simpler to embed the capabilities it provides within a DevSecOps workflow. At its core, CodeHunter makes use of a set of deterministic AI models that it has developed to analyze […]
Rein Security Emerges to Analyze Reachability of Application Vulnerabilities
Rein Security has emerged from stealth to launch an application security platform capable of determining the reach of a vulnerability based on which libraries and application programming interfaces are actually running in a production environment. Fresh off raising $8 million in seed funding. Rein Security CEO Matan Bar Efrat said DevSecOps teams can now gain […]
The 10-Layer Monitoring Framework That Saved Our Clients From 3 a.m. Pages
A practical 10-layer monitoring framework for Kubernetes and VM environments that prioritizes what to watch—system, application, HTTP/RUM, databases, caches, queues, tracing, SSL, external deps, and log patterns—to prevent outages and reduce noisy alerts.
Why Responsible AI Isn’t Optional in DevOps — it is the Next Frontier of Ownership
The integration of AI in DevOps brings both opportunities and accountability challenges. This article explores the implications of AI decision-making within CI/CD pipelines and emphasizes the need for governance frameworks to ensure responsible AI use while maintaining trust and efficiency.
Survey Surfaces Disconnect Between DevOps Metrics and Business KPIs
A survey of 418 DevOps professionals finds that while DevOps teams closely monitor and observe the performance of applications, not nearly as many are able to correlate the value of those efforts to the business. Conducted by Catchpoint, a unit of LogicMonitor, the survey finds more than two-thirds (67%) believe application degradations are either always […]