Identity and Access Management
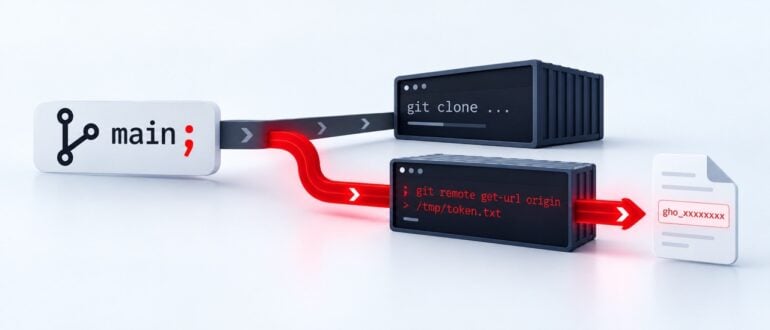
A Semicolon in a Branch Name Was All It Took to Steal an AI Agent’s GitHub Token
 Canio Campaniello | | AI agent security, command injection, credential security, GitHub security, least-privilege, OpenAI Codex
AI coding agents don't just suggest code anymore. Tools like OpenAI's Codex spin up a real container, clone a real repository, and authenticate with a real GitHub credential to get the job ...
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
 Jaime Hampton | | Aikido Security, application security, CI/CD, devsecops, gitlab, Software Supply Chain
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner ...
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
 Jeff Burt | | CrowdSec, EDR, github, Mini Shai-Hulud, NPM security, OAuth tokens, supply chain attacks, TanStack compromise, TeamPCP
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee ...
Cybersecurity Researchers Uncover Flaw in Google AI Coding Tool

Cybersecurity researchers from Pillar Security this week revealed how a prompt injection inserted into a GitHub repository was used to gain Editor-level access to an internal Google Cloud project using a flaw ...
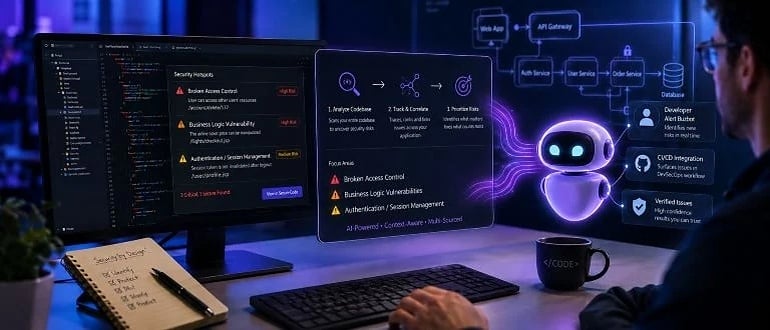
Sonar AI Agent Discovers Vulnerabilities Hidden in Business Logic Workflows
Sonar today made available an artificial intelligence (AI) agent designed to discover vulnerabilities and business logic flaws that pose the greatest risk to an organization should they be exploited. The SonarQube Hunter ...
Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
Jeff Burt | | arrayref, information stealing, North Korea, Rust programming language, software supply chain attacks, StepSecurity, typosquatting, Wiz ResearchSecurity researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more ...
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Jeff Burt | | Activepieces, AI security, C/C++, Endor Labs, isolated-vm, JavaScript security, Mastra, n8n, Node.js security, remote code execution, Sandbox, software vulnerability, TOCTOU, V8 Isolate, vm2Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets ...

Attackers Can Exploit a Claude Code RCE Flaw to Take Command of System
Jeff Burt | | agentic AI, AI (Artificial Intelligence), AI security risks, Anthropic Claude Code, automated parsers, deeplinkA dangerous vulnerability found in Anthropic’s popular Claude Code developer model could have allowed bad actors to grab control of a victim’s system by luring them into clicking on a crafted malicious ...
Massive VS Code Secrets Leak Puts Focus on Extensions, AI: Wiz
Researchers with cybersecurity firm Wiz earlier this year discovered, almost by chance, a significant supply chain risk and massive secrets leak in the Visual Studio Code and OpenVSX marketplaces that they said ...


Venafi Adds Ability to Prevent Unauthorized Code From Running
Venafi added an ability to prevent unauthorized code from running in IT environments that make use of its machine identity management platform ...
Sonar Adds Secrets Detection to Code Analysis Portfolio
Sonar has added a secrets detection capability to its portfolio of tools for analyzing code and DevOps workflows ...

