
DevSecOps
Survey: Lack of Confidence in Software Supply Chain Security Runs High

A survey of 400 platform and security engineers in the U.S and United Kingdom (UK), finds nearly three quarters (73%) are either only moderately confident (58%) or not confident (15%) in the ...
Blitzy Makes Sandbox for Reverse Engineering Code Available at No Cost
Blitzy has made available a sandbox where DevOps teams can reverse-engineer up to one million lines of code, generate up to 25,000 lines of tested end-to-end code, and identify security vulnerabilities across ...
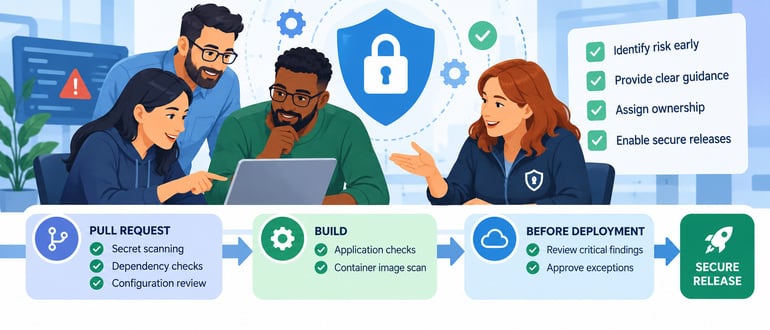
DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
 Jeff Burt | | CrowdSec, EDR, github, Mini Shai-Hulud, NPM security, OAuth tokens, supply chain attacks, TanStack compromise, TeamPCP
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee ...
New npm Threat Bypasses Install Script Protections
A malicious npm package that has been downloaded millions of times comes with a new way of spreading the malware that makes it easier to bypass security protections, say researchers with security ...
Harness Previews Revamped Platform for the Agentic Engineering Era
Harness today previewed a revamped user interface for its platform for managing software deployments that makes it simpler for software engineers to manage teams of artificial intelligence (AI) agents using a forthcoming ...
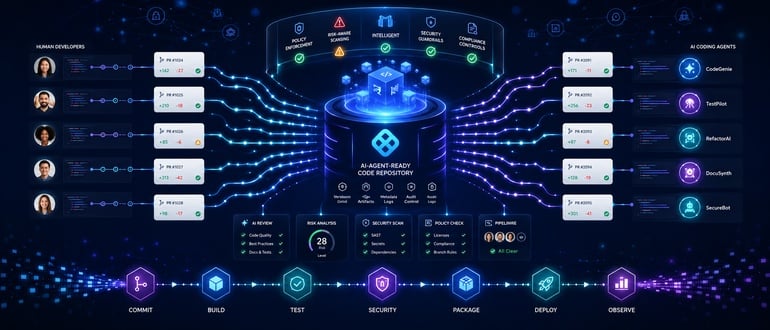
Flaw in DeepSeek Harness AI Coding Tool Let Agents Disable Their Sandbox
Jeff Burt | | agentic AI security, AI coding agents, AI sandbox, API Keys, DeepSeek Harness, OX Security, VulnCheckNews of the now-fixed vulnerability comes amid growing concerns that AI vendors do not in have complete control of their autonomous agents ...
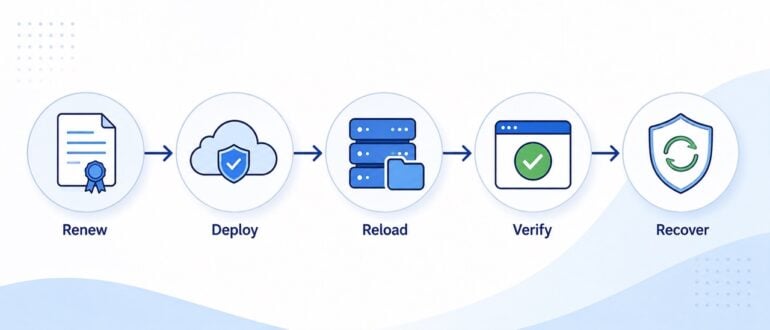
Certificate Renewal Is a Deployment Workflow, Not a Cron Job
 Franz Alliod | | automation, certificate management, Certificate Renewal, devops, kubernetes, security
Certificate renewal is often treated as a scheduled task: run an ACME client, obtain a new certificate, and move on. In practice, that view is too narrow for production systems. A certificate ...
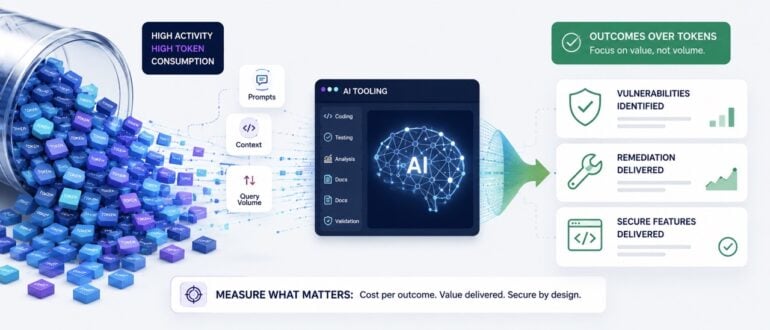
Why “Tokenmaxxing” Was Always the Wrong Way for Developers to Measure AI Productivity
 Drew Thompson | | ai, AI Development, AI security, application security, developer productivity, software development
The term "tokenmaxxing" left the developer lexicon just as quickly as it arrived, and like most viral technology concepts, it means different things depending on who's using it. In practice, the term ...
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Jeff Burt | | Activepieces, AI security, C/C++, Endor Labs, isolated-vm, JavaScript security, Mastra, n8n, Node.js security, remote code execution, Sandbox, software vulnerability, TOCTOU, V8 Isolate, vm2Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets ...

Harness Adds AI Agents to Automate DevSecOps Workflows at Machine Speed
Harness today added multiple artificial intelligence (AI) agents and a virtual patching capability to its portfolio to automate DevSecOps workflows at a time when the number of vulnerabilities being discovered in code ...
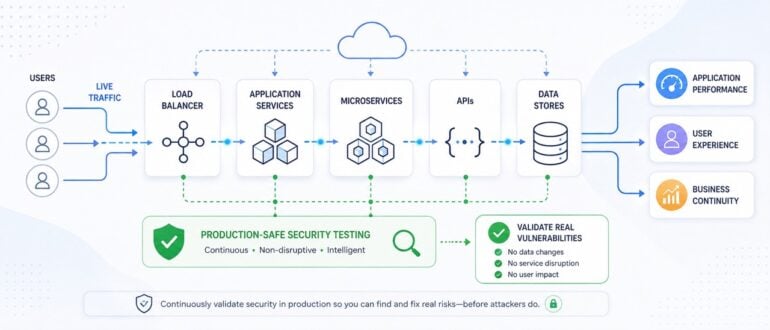
Production-Safe Testing: The Missing Piece in Most DevSecOps Strategies
 Dharmesh Acharya | | application security, continuous security, devsecops, Production-Safe Testing, security testing
Most DevSecOps teams invest heavily in security before deployment, yet attackers target the production environment where applications, APIs, and user behavior are constantly changing. If security validation stops before release, critical risks ...

