

Clinical Trials: Programming for Scale, Speed and Success
According to the Journal of the American Medical Association (JAMA), the median cost of bringing a new drug to market is $985 million and the average cost is $1.3 billion. However, those in health care hoping to harness promising new treatments, and patients facing steep prescription costs, see this as progress. After all, previous studies […]
Rust in Linux 5.20 | Deepfake Hiring Fraud | IBM WFH ‘New Normal’
In this week’s The Long View: Linus says next release will support Rust, FBI warns scammers are getting hired in deepfake interviews, and 80% of IBM staff stay at home.
Buildkite Adds Analytics Tools to Identify Flaky App Tests
Buildkite has added an analytics tool to its continuous integration/continuous delivery (CI/CD) platform that identifies flaky tests. Buildkite’s co-CEO Keith Pitt said the company’s Test Analytics tool enables continuous performance monitoring and real-time insights for test suites that, when not properly written, only serve to waste DevOps teams’ time. Rather than eliminating those tests, most […]
Moving From Lift-and-Shift to Cloud-Native
Analyst firm Forrester recently predicted that 2022 “will see big organizations move decisively away from lift-and-shift approaches to the cloud, embracing cloud-native technologies instead.” According to Gartner, more than 85% of enterprises “will embrace a cloud-first principle by 2025 and will not be able to fully execute on their digital strategies without the use of […]
The Two Types of Code Vulnerabilities
Spell checkers, grammar checkers and predictive keyboards all help reduce errors in written communication, but in a creative medium where writers need to innovate new expressions, nothing can eliminate all errors. The same is true in the code we write. Of course, your code is probably perfect but, on average, all code has bugs. Some […]
Survey Reveals High Cost of Application Modernization
A survey of 250 software developers and architects in the U.S. found nearly three-quarters of respondents (74%) reported that the average cost of an application modernization project is nearly $1.5 million, with 79% noting that at least one of these projects has failed. Conducted by Wakefield Research on behalf of vFunction, a provider of a […]
Salesforce Adds RPA Bots to MuleSoft Integration Platform
Salesforce today announced that it is now using robotic process automation (RPA) to connect disparate data via a no-code tool developed by its MuleSoft unit. Shaun Clowes, chief product officer for MuleSoft, said bots created using an RPA-infused integration platform can now automate much of the effort previously required to integrate data residing in different […]
GitLab To Embed Observability in CI/CD Platform
The latest version of the GitLab continuous integration/continuous delivery (CI/CD) platform added a range of monitoring and visualization capabilities as part of an effort to embed a full set of observability capabilities in the core platform within the coming year. As part of that effort, the latest version of GitLab, 15.1, has now added support […]
CodeSee Unveils Open Source Hub
CodeSee today launched a free Open Source Hub (OSH) community through which developers can more easily analyze the codebase that makes up an open source software project. Shanea Leven, CodeSee CEO, said that capability is crucial because making it easier to explore open source codebases reduces the level of effort required for developers to understand […]
Common RDS Misconfigurations DevSecOps Teams Should Know
Relational databases have become the option of choice for organizations wishing to streamline and scale the use, storage and retrieval of data. Many organizations choose AWS Relational Database Service (RDS) to forego the resource-intensive tasks related to database administration including management and continuous oversight. RDS is a fully managed service that simplifies and automates these […]
Quick! Define DevSecOps: Let’s Call it Development Security
For a good long while, DevSecOps referred specifically to vendors like Veracode that did static application security scanning, dynamic application security scanning, software composition analysis and some form of runtime monitoring (usually interactive scanning). Then we realized that DevSecOps was potentially a lot more than that and, like DevOps, we drove the word to encompass […]
Hasura SDK Integrates GraphQL Platform With More Data Sources
At its HasuraCon ’22 conference, Hasura today announced the early release of a software development kit (SDK) that extends the reach of its GraphQL platform to additional data sources. In addition, Hasura is making generally available integrations with the GitHub repository, support for OpenTelemetry Traces within the Hasura Cloud Platform and Microsoft SQL event triggers. […]
Dynatrace Adds Synthetic Tests to Validate App Experiences
Dynatrace today extended the application release management capabilities it provides to include synthetic tests for validating and assuring user experiences. Saif Gunja, director of product marketing for Dynatrace, said the user experience validation and user experience assurance (UXA) capability spans everything from application availability and performance to actual engagement with specific features based on the […]
Chip-to-Cloud IoT: A Step Toward Web3
During the first six months of 2021, IoT devices were breached 1.51 billion times, a significant increase from only 639 million breaches observed for the entirety of 2020. This problem can be attributed to the widespread adoption of the internet-of-things (IoT) and the Windows Server Message Block (SMB), and neither can be avoided in the […]
Quality Is a Top Challenge for Data-Driven Projects
Software systems continue to produce more and more data. And making use of it has proven benefits — so much so that many analysts have, over the years, referred to data as the new oil. As a result, the majority of organizations are expending effort into refining their data — in fact, a recent study […]
ServiceNow Adds Lightstep Notebooks to Visualize Observability Data
ServiceNow today added a visualization tool to its Lightstep observability platform that will make it simpler for DevOps teams to correlate metrics, logs and traces. Ben Sigelman, general manager for Lightstep at ServiceNow, said Lightstep Notebooks will make it easier for DevOps teams to make sense of the massive amounts of data collected by the […]
DevOps Connect: DevSecOps — Building a Modern Cybersecurity Practice
Malicious actors are constantly looking for new ways to gain access to sensitive data and corrupt systems. As software supply chain attacks are on the rise, security has become a top priority and a growing area in the regulatory and standards landscape. DevOps teams need to approach security as an ongoing part of the software […]
Creating Career Opportunities in Quality Engineering
Software testing is the thread that connects code to customers, ensuring that the code created by development teams works for users and supports customer loyalty. But as the demands of software development are transformed by DevOps and customer expectations rise, the career and role of the software tester is evolving rapidly. Customer expectations have made […]
What Is User Acceptance Testing and Why Is it so Important?
Anyone involved in software development knows how important it is to ensure a positive end-user experience. One way to do that is through the use of user acceptance testing (UAT). UAT is one of the types of testing that you can execute as part of your overall quality assurance process. Source It’s essential in helping […]
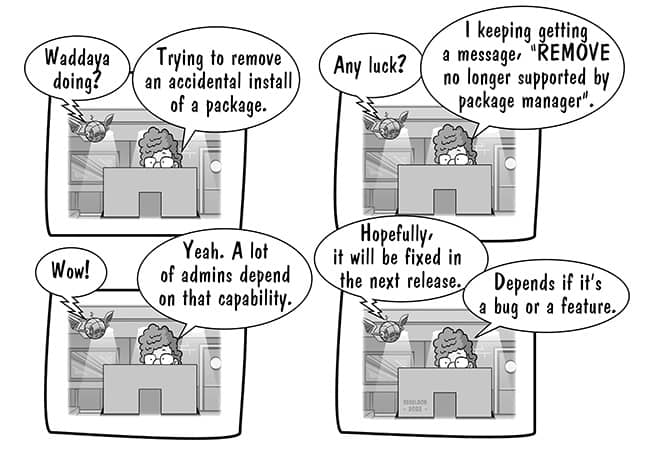
TechStrong Con: Open Source Software Community Needs Security Help
The only way to make significant improvements in the state of open source security is if more organizations that benefit from open source projects commit to making more resources available to achieve that goal. At the virtual TechStong Con event, executives on an Open Source and DevOps panel called for more contributions from enterprise IT […]
Developer’s Guide to Web Application Security
When it comes to security, there are many vulnerabilities that can leave your website or web app open to attack. In this article, we’ll go over 15 common web application security vulnerabilities and how you can prevent them. 1. Insufficient Cryptography Cryptography is a critical security measure that is used to protect data in transit […]