

Why Nano Updates Only Work if You Begin with the Latest and Greatest Software
Is there a silent threat of technical debt looming in your organization? You probably should take a deeper look. Modern software systems are composed of hundreds of interdependent components. How are you updating those components – system libraries, base containers, and app packages? Do it poorly, and you will trigger unintended side effects, like failing […]
The Developer’s Guide to Agentic AI: The Five Stages of Agent Lifecycle Management
Discover how AI agents evolve from task executors to adaptive, self-improving systems through Agentic Lifecycle Management, driving agility and innovation.
The Cloud Reset: DevOps Brings Workloads Back to Private Clouds
DevOps teams are leading a “cloud reset,” moving workloads from public to private clouds for greater control, security and cost predictability. As organizations mature beyond cloud-first strategies, hybrid and private cloud environments are becoming the foundation for smarter, more accountable DevOps operations.
How Software Engineers and Students Use AI to Move Faster than Ever (Without Breaking Things)
We’re living through the AI revolution — or more accurately, the age of augmented intelligence. From agentic AI tools transforming software development to AI-native education shaping the next generation, super{set} explores how developers, students, and businesses can harness AI to amplify human potential and innovation.
Establishing Visibility and Governance for Your Software Supply Chain
Asset visibility and cloud governance start with SBOMs, VEX, and provenance tracking. Learn how to secure your software supply chain.
Secure By Design, Secure by Default
“Shift left” alone won’t secure software. Real security must be embedded continuously across design, development, and production—not just moved earlier.
When Metrics Overwhelm: How SREs Help Engineers Reclaim Focus
Observability promised insight but delivered alert fatigue. Learn how SREs are redefining observability to empower developers and restore real engineering value.
Technical Debt: Make Developers Happier Now or Pay More Later
In a survey of over a thousand CIOs, CTOs, CISOs and other tech execs conducted by Protiviti, organizations spend an average of 30% of their total IT budgets on managing technical debt. Not only is it costly, but nearly 70% felt that technical debt highly impacted their ability to innovate. Technical debt happens to organizations […]
How to Eliminate DevOps Toil Using Automation Scripts
Engineering teams spend nearly 15 hours a week on repetitive DevOps toils that drain productivity. This guide explains how to identify high-impact automation opportunities, apply the 15-minute rule, and build sustainable script-based solutions that eliminate toil and free teams for innovation.
Coding Agent Teams: The Next Frontier in AI-Assisted Software Development
Developers are moving beyond single AI coding assistants to teams of specialized agents, boosting speed, scalability, and collaboration in software development.
Whose Ops is it Anyway? How IDPs, AI and Security are Evolving Developer Culture
It was only a few years ago that perhaps the biggest hurdle for DevOps advocates was convincing leadership that it was worth the investment. That conversation has since shifted. In most organisations today, the value of faster releases, tighter feedback loops, and closer collaboration between development and operations is obvious. The challenge is no longer […]
Developer Experience: Overcoming 6 AI-Induced Challenges
The use of artificial intelligence brings high hopes and expectations in the technological world, promising changes to the way businesses operate. A staggering 79% of companies are now or will be using AI within the next year, according to an August 2025 survey from OpenText and the Ponemon Institute. AI’s rise is especially prevalent in the software development sector, and in particular in the area of developer […]
Common IaC Security Issues and How to Fix Them
Learn the top five Infrastructure as Code (IaC) security vulnerabilities, their fixes, and best practices to prevent misconfigurations, drifts, and breaches.
How Can the Usage of AI Help Boost DevOps Pipelines
AI is revolutionizing DevOps by making CI/CD pipelines smarter, self-learning, and more efficient — enabling faster, secure, and automated software delivery.
Build vs. Buy: What it Really Takes to Harden Your Software Supply Chain
When it comes to securing the software supply chain, engineering teams often assume that the choice between building their own hardened images or buying a solution is straightforward…until they try to build the images themselves. As the programmer’s credo goes: “We do these things not because they are easy, but because we thought they’d be easy.” The decision […]
Why Automation Fails Without the Right QA Mindset
In the DevOps world, with its faster release cycles and continuous delivery, quality assurance (QA) cannot be sidelined until the end of the process. Companies that actively use automation achieve up to 60% faster release cycles compared to those relying solely on manual testing. However, automation alone is insufficient. Without the right QA mindset, moving faster can […]
NLP Tools for Intelligent Documentation and Developer Enablement
Natural language processing (NLP) is reshaping technical documentation and developer enablement. Organizations that select the right tools and integrate them effectively into existing environments streamline documentation workflows, reduce manual effort, and make technical knowledge more accessible to developers at all levels. Unlocking the highest value from NLP tools requires organizations to adapt models to their […]
How Model Context Protocol (MCP) is Fueling the Next Era of Developer Productivity
MCP standardizes how AI agents connect to tools and data, solving fragmentation in AI development with secure, reusable, and scalable integrations.
The DevSecOps Career Path: What No One Tells You About Getting Started
DevOps teams across organizations are suddenly finding themselves responsible for security with no roadmap. One day, teams are focused on deployment velocity and infrastructure automation, the next day, they’re expected to understand threat modeling, vulnerability management and compliance frameworks. This shift isn’t happening by choice — it’s happening because traditional security approaches can’t keep pace […]
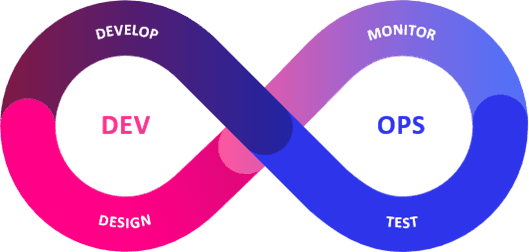
Is the Future of DevOps DaaS?
DevOps as a service (DaaS) is emerging as the next big shift in how organizations build, deploy and maintain their software pipelines. What started as do-it-yourself automation with Jenkins scripts and self-hosted Git servers has now become an increasingly complex ecosystem of tooling, governance and culture. The question now is whether companies really need to […]
From Legacy to GitOps: A Roadmap for Enterprise Modernization
Learn how enterprises can modernize legacy infrastructure with GitOps. A roadmap for automation, governance, and resilience at scale.
Why Automation Fails Without the Right QA Mindset
In the DevOps world, with its faster release cycles and continuous delivery, quality assurance (QA) cannot be sidelined until the end of the process. Companies that actively use automation achieve up to 60% faster release cycles compared to those relying solely on manual testing. However, automation alone is insufficient. Without the right QA mindset, moving […]
What Makes Vulnerability Scanning Effective in Fast-Moving DevSecOps Pipelines Today?
Traditional vulnerability scanning can’t keep pace with CI/CD. Learn how real-time, context-aware scanning reduces noise, speeds fixes, and enables secure DevSecOps at scale.