

OpenAI Hires 1,000 Low Wage Coders to Retrain Copilot ¦ Netflix Blocks Password Sharing
In this week’s #TheLongView: ChatGPT darling OpenAI wants people to write code in English, and the unintended consequences of blocking shared accounts.
Cisco AppDynamics Survey Surfaces DevSecOps Challenges
A survey of 1,150 large enterprise IT professionals from the AppDynamics unit of Cisco suggested application security progress is being made slowly and steadily as organizations continue to embrace DevSecOps best practices. The survey finds that while more than three-quarters of respondents (76%) believe that DevSecOps is essential for organizations to effectively protect against a […]
New Relic Bolsters Observability Platform
New Relic has updated its observability platform to include the ability to better detect and track errors in addition to monitoring vulnerabilities. At the same time, an instance of the New Relic observability platform that runs natively on the Microsoft Azure cloud platform is now also generally available. Manav Khurana, general manager for observability product […]
Software Supply Chain Security Debt is Increasing: Here’s How To Pay It Off
Last year, the world woke up to the software supply chain dilemma. We saw a spike in attacks as hackers sought to exploit known and unknown vulnerabilities within dependencies. There is also the chance of typosquatting, and malicious code commits to consider. Such supply chain attacks have increased by a shocking 742% over the past […]
Dynatrace Survey Surfaces State of DevOps in the Enterprise
A global survey of 1,300 CIOs and DevOps managers working for organizations with more than 1,000 employees published today finds more than three-quarters of respondents work for organizations (78%) that deploy software updates into production every 12 hours or less, with more than half (54%) say they do so at least once every two hours. […]
A DevSecOps Process for Node.js Projects
Node.js is an open source development platform for running JavaScript code on the server side. Node is useful for developing applications that require a persistent browser-server connection and is often used for real-time applications such as chat, social applications, or news feeds. DevSecOps is a way for development, security, and operations teams to work together […]
FAA Ground Stop due to Technical Debt? | Don’t Do DIY Crypto!
In this week’s #TheLongView: The FAA’s NOTAM database gets corrupted, and Threema shows why DIY encryption is bad.
AppSec in the Cloud: What DevOps Teams Should Know
Cloud application security refers to the measures and controls that are put in place to protect cloud-based applications and data from cyberthreats, unauthorized access and data breaches. These measures can include technical controls such as encryption, access controls and secure networks, as well as operational controls like policies and procedures for managing and securing data […]
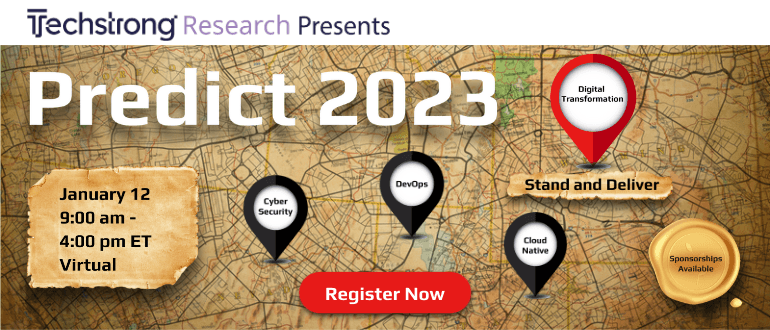
Predict 2023: Stand and Deliver
It’s that time of year again—the New Year’s ritual: Time to predict the big trends in your world for the new year. By now you have probably seen dozens of headlines, articles, videos and interviews telling you what big trends will shape the coming year. Here at Techstrong Group, our Predict virtual event is built […]
How DevOps Helps Banks Optimize Their Services
A world-renowned bank’s CEO was recently quoted as saying that while there are thousands of manual banks now, the future will see only a handful of digital banks. Along with the rest of the world’s critical business sectors, an overwhelming number of banks are also shifting to virtual platforms. This migration is being orchestrated by […]
Will DevSecOps Replace the Security Operations Center?
Traditionally, a security operations center (SOC) is a physical facility where an organization performs information security activities. The SOC team analyzes and monitors the organization’s security systems. A SOC aims to protect businesses from security breaches by identifying, analyzing and responding to cybersecurity threats. The SOC team consists of administrators, security analysts and security engineers. […]
Best of 2022: Agile/Scrum is a Failure – Here’s Why
In this week’s The Long View: Agile and Scrum are increasingly getting a bad reputation, being associated with the worst aspects of toxic workplace culture.
Best of 2022: Three Cloud Trends to Watch in 2022
As we close out 2022, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the latest in our series of the Best of 2022. Many developers and startups view cloud services as simply “compute”, “storage” and “networking.” The cloud has matured to the point where customers often don’t think […]

AWS Saves Ukraine’s Data | WPF ‘is not Dead’ (yet) | Devs Quit for Cash
In this week’s The Long View: Amazon S3 is keeping Ukraine’s data safe, we ask if Windows Presentation Foundation is dead, and developers tell us why they switch jobs.
Rezilion Updates Open Source MI-X Tool to Better Secure App Development
Rezilion has updated its open source MI-X vulnerability discovery tool to include mitigation and remediation recommendations. In addition, the tool can now produce machine-readable output in either a JSON or CSV format. Finally, the company added Windows support for Heartbleed and SpookySSL vulnerabilities in Windows environments. MI-X makes it possible to use a command line […]
How SASE Can Ease DevSecOps Adoption
DevSecOps is a software development methodology that merges development (Dev), security (Sec) and operations (Ops) into one team that integrates security throughout the entire software development life cycle (SDLC). The goal is to deliver high-quality applications quickly and securely. The traditional software development life cycle introduces security in the late phases of the SDLC. However, […]
EU Data Privacy: Try Again | SkyPilot: Choose Cheapest Cloud | WFH: Better Meetings
In this week’s The Long View: EU-U.S. Data Privacy Framework reemerges, Berkeley brings cloud selection box, and proof that remote work is good work.
Why Backups and Compliance Go Hand-in-Hand
It’s hard to run a business. Besides the numerous challenges you have to deal with daily, ensuring the security of your business and customer information is essential for operating smoothly. In order to mitigate information security risks that would affect companies and their users, a number of security regulations have been created, including a set […]
ActiveState Makes All Tiers of Curated Artifact Repository Service Free
ActiveState today announced it is making all tiers of its ActiveState Artifact Repository service available for free for a limited time. The move aims to enable organizations to better secure open source software components incorporated within applications. Loreli Cadapan, vice president of product for ActiveState, said the ActiveState Artifact Repository exposes a set of curated […]
Prioritizing Product Security With DevSecOps
Building software with strong security can no longer be an afterthought for organizations. The need for a reliable cybersecurity posture has proven vital amid the constant attacks we’re seeing across industries, all over the world. Product-specific security is top of mind for most companies, and a successful product security practice requires integrating with the ethos […]
Massive Number of Transitive Dependencies Traced to Open Source Code
An analysis of nearly 2,000 software packages published by Endor Labs found 95% of all application vulnerabilities can be traced back to a transitive dependency created when a developer used an open source component. The study, conducted by the Station 9 research arm of Endor Labs, a provider of a platform for identifying software dependencies, […]
Codenotary Extends Dynamic SBOM Reach to Serverless Computing Platforms
Codenotary has extended the reach of its platform for automatically generating software bills of materials (SBOMs) to serverless computing platforms running software constructed using functions. Codenotary CTO Dennis Zimmer said because serverless apps are dynamically created, it’s not possible to generate SBOMs using traditional approaches. The TrueSBOM platform makes it possible to create an SBOM […]
Dead Downtown: It’s YOUR Fault | Pentagon’s FOUR Cloud Vendors | Apple Adds MORE Price Flexibility
In this week’s The Long View: Home working is ripping the heart out of cities, the DoD’s bizarre cloud strategy, and Apple adds a $10,000 app price option.