

How the Cybersecurity EO Impacts DevOps Teams
Eric Greenwald, general counsel for Finite State, talks with Mike Vizard about how the executive order for securing software supply chains issued by president Biden will impact DevOps teams. The video is below, followed by a transcript of the conversation. Announcer: This is Digital Anarchist. Mike Vizard: Hey, guys. Thanks for the throw again. We’re […]
How to Automate PKI for DevOps With Open Source Tools
Historically, DevOps and security have been diametrically opposed practices. DevOps wants to move fast and break things, or so they say, but security policies tend to slow things down. However, it has become clear that this school of thought has evolved, as both practices have something to learn from the other. Organizations have embraced a […]
Unreliable Server Scare | Information Batteries | ARM IPO PDQ
In this week’s The Long View: We worry about chips failing randomly, we ponder a new way of thinking about workload shifting, and we grok Arm’s IPO.
Codenotary Launches Cloud Service to Generate SBOMs
Codenotary has launched a Codenotary Cloud platform that can automatically generate a software bill of materials (SBOM) and make it easier to discover what components have been included in an application. Moshe Bar, Codenotary CEO, said that capability can also play a key role in identifying which components in an application might contain, for example, […]
Why Developer-First is the Future of AppSec
DevOps culture and rapid cloud adoption mean developers are shipping code faster than ever and, in many cases, security teams struggle to keep up. To avoid relegating security to afterthought status, organizations must shift left and adopt a developer-first approach to application security (AppSec). Organizations that depend on software development need a solution that accomplishes […]
WhiteSource Tightens Code Scanning Tool Integration with Azure DevOps
WhiteSource has added the Microsoft Azure DevOps platform to the list of continuous integration/continuous delivery (CI/CD) platforms its open source vulnerability scanning tools natively supports. Susan St. Clair, director of product management for WhiteSource, said while developers are always encouraged to scan for vulnerabilities, it’s more effective if organizations implement scanning by default every time […]
App Store Antitrust Bill | GDPR vs. Google Fonts | Wordle Worth $1M+
In this week’s The Long View: The Open App Markets Act polls well among devs, Germany fines a website for using Google Fonts, and the NY Times buys Wordle for an unfeasible sum.
Continuous Security: The Next Evolution of CI/CD
Following a wave of high-profile cyberattacks and the White House’s release of the executive order on improving the nation’s cybersecurity, how to build a successful cybersecurity program has never been so hotly debated as it is now. From SolarWinds to the Colonial Pipeline attacks, these events demonstrate that defensive measures alone cannot mitigate cybersecurity risk, […]
Embedded Connectivity Solves the Right (and Left) Problem
In Steven Bellovin’s book, “Thinking Security: Stopping Next Year’s Hackers,” (2015) he wrote: “Companies are spending a great deal on security, but we read of massive computer-related attacks. Clearly, something is wrong. The root of the problem is two-fold: We’re protecting (and spending money on protecting) the wrong things, and we’re hurting productivity in the […]
Improving Software Security in 2022
The recent Log4j vulnerability showed just how quickly a security bug could disrupt not just an industry, but the entire world. Organizations, especially federal agencies, will always find themselves at some level of risk, but they can also do more to mitigate those challenges. In November 2021, the Biden administration issued a directive through the […]
4 Ways to Combat the DevOps and Security Workforce Shortage
Most people are painfully aware that security breaches have increased in recent years, while at the same time becoming much more sophisticated in their approach. Additionally, ever-expanding application environments and continuously evolving workloads have created more opportunities than ever for attackers. What’s not so apparent to those outside of the tech bubble: The world is […]
Embracing Security by Design in Development
The number of data breaches publicly reported in 2021 far exceeded the total for 2020, making 2021 a record year. With cyberattacks on the rise and bad actors and ransomware gangs demanding millions in ransom, cybersecurity has taken on new urgency. In addition to more sophisticated hacking techniques, the rapid pace of tech adoption during […]
2022 Will Be the Year of the Cyber ‘Shift Show’
As ransomware continues to plague organizations across industries, remote work continues and innovation brings with it new threat vectors for bad actors to exploit, 2022 is poised to be another messy year in cybersecurity. In July 2021 alone, organizations lost $45 million to ransomware. What’s more, ransomware costs are projected to reach $265 billion by […]
Infrastructure Access Management a Growing DevOps Priority
Organizations plan to address access management over the next 12 months, as the need to secure and streamline infrastructure-wide access controls serves as a prerequisite to other initiatives, like zero-trust. This was one of the key findings of a survey of 600 DevOps professionals conducted by Pollfish and sponsored by strongDM. The report also found […]
Survey Predicts Massive Migration to the Cloud
A global survey of 1,600 enterprise IT decision-makers found more than half are working for organizations that plan to eliminate the use of data centers over the next two years. The survey was conducted by Aryaka, a provider of a secure access service edge (SASE) platform, and found a quarter of the respondents have closed […]
EEEWW—Green iMessage Bubbles | ‘Great Resignation’ Redux | Faster Firefox 96
In this week’s The Long View: iMessage lock-in lessons, attrition-rate fixes, and more on Mozilla.
NPMs Sabotaged as OSS Sustainability Crisis Continues
A long-simmering debate over the sustainability of smaller open source projects moved beyond the theoretical when two widely used open source node packaged modules (npm) were deliberately sabotaged this week, allegedly by a primary contributor. Colors.js is an npm that has been downloaded more than 3.3 billion times, with more than 19,000 projects depending on […]
CIS Benchmarks: DevOps Guide to Hardening the Cloud
DevOps and cloud computing have become inseparable. But while the cloud started as primarily a dev/test environment — without stringent security and availability requirements — it has evolved into a mature platform for running production workloads. Moreover, devastating supply chain attacks like SolarWinds and Kaseya taught us all that development environments must also be secure. […]
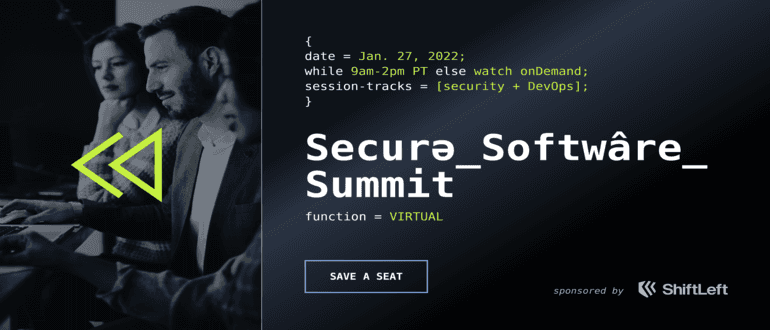
Secure Software Summit: Exploring Secure Coding Best Practices
In an era where software is dominating the world, the security and quality of code must remain a high priority. Delivering secure and reliable software at a rapid pace is crucial for most organizations today, but it’s not an easy task. What security best practices do organizations put in place to successfully produce secure software? How should DevOps teams […]
DevSecOps Will Cross the Chasm in 2022
We’ve been talking about DevSecOps and shift-left security for years. Although this approach probably didn’t “cross the chasm” in 2021, we did see some very telling milestones. Cybersecurity VC funding surged to record heights with a focus on DevOps and cloud security and the need for DevSecOps became glaringly evident with the Log4j vulnerability. On a […]
Best of 2021 – How to Revoke JSON Web Tokens (JWTs)
As we close out 2021, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the seventeenth in our series of the Best of 2021. One of the most common questions about JSON Web Tokens (JWTs): Once they’re issued, how can they be revoked? What Are JWTs? JSON Web Tokens […]
Best of 2021 – From Agile to DevOps to DevSecOps: The Next Evolution
As we close out 2021, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the ninth in our series of the Best of 2021. As the workforce shifts to remote locations, networks are becoming more diffuse as the edge gets farther away. At the same time, the number of […]
Best of 2021 – The Next Evolutions of DevOps
As we close out 2021, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the seventh in our series of the Best of 2021. As society continues to recover from the global COVID-19 pandemic and some semblance of normal starts to return, technology continues to move forward. The pandemic […]