

GitHub Breach Tied to Malicious VS Code Extension Exposes Thousands of Internal Repositories
GitHub says attackers accessed thousands of internal repositories after a company employee’s device was compromised through a malicious Visual Studio Code extension, though the company said it has removed the malicious extension, isolated the compromised endpoint, and launched an investigation. The company confirmed that approximately 3,800 internal repositories were affected. GitHub stated that investigators have […]
Widespread Mini Shai-Hulud Campaign Is a Matter of Trust
The latest series of attacks using the notorious Shai-Hulud worm puts into sharp focus the threats facing software developers and their CI/CD pipelines, an issue that has been raised in recent months as bad actors increasingly turn their attention to DevOps environments. That said, these most recent Shai-Hulud incidents attributed to the TeamPCP group also […]
AI-Generated Apps Without DevOps: A Security Disaster Waiting to Happen
A small internal tool was built over a weekend. An engineer used an AI coding assistant to generate most of the backend. A simple interface was added, a few API calls were wired together and within hours the app was live. The app worked. The app felt fast. The app looked like progress. No one […]
Cyber Threats to DevOps Platforms Rising Fast, GitProtect Report Finds
The number of incidents targeting DevOps platforms grew 21% in 2025, but the amount of downtime jumped almost 95%, the security firm said.
Critical Microsoft GitHub Flaw Highlights Dangers to CI/CD Pipelines: Tenable
A critical vulnerability in a popular Microsoft GitHub repository could allow a threat actor to easily exploit its CI/CD infrastructure to run arbitrary code in the repository and gain access to secrets, according to researchers with cybersecurity firm Tenable. In an advisory issued April 21, Rémy Marot, staff research engineer at Tenable, wrote that “by […]
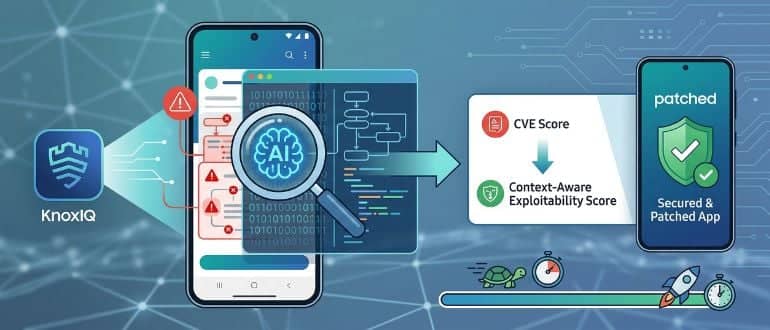
Appknox Adds AI Tool to Detect and Fix Vulnerabilities in Mobile Applications
Appknox today added an ability to apply artificial intelligence (AI) to assess vulnerabilities in the binaries used to construct a mobile application and recommend a fix that can be passed on to an AI coding tool to implement. Company CEO Harshit Agarwal said KnoxIQ provides an AI copilot to more accurately assess how exploitable a […]
LayerX: Anthropic’s Claude Code Can Easily Be Easily Weaponized
LayerX researchers were able to convince the popular AI coding tool to bypass its guardrails and execute malicious instructions.
Why Most DevSecOps Pipelines Fail at Runtime Security (not Build Time)
Runtime risk refers to security exposure caused by configuration, identity or infrastructure changes after deployment.
North Korean Hackers Suspected in Supply Chain Attack on Popular Axios Project
The threat actor targeted a highly popular open source project with more than 100 million weekly downloads, creating a large “blast radius.”
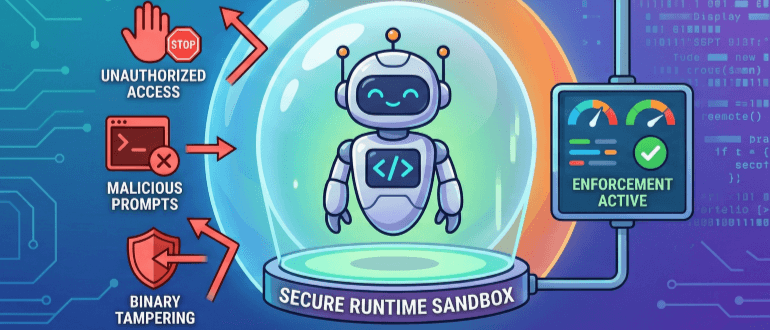
Sysdig Adds Runtime to Secure AI Coding Agents
Sysdig this week at the RSA Conference (RSAC) revealed it has created a runtime that makes it possible to securely deploy artificial intelligence (AI) coding tools. Jonas Rosland, director of the open source program for Sysdig, said the runtime makes it possible to monitor the activity of AI coding agents in real time, including potential […]
Sophisticated Supply Chain Attack Targeting Trivy Expands to Checkmarx, LiteLLM
The supply chain attack that compromised Aqua Security’s Trivy open source security vulnerability scanner and its associated GitHub Actions earlier this month continues to expand, with software development tools from Checkmarx and LiteLLM being the latest victims of the sophisticated campaign. The threat group behind it, TeamPCP, is using the attacks to create persistence and […]
N. Korean Famous Chollima Hackers Use Malicious npm Packages to Steal Data
A group of more than two dozen malicious npm packages used to steal secrets and credentials from software developers has all the hallmarks – from infrastructure to operations – of Famous Chollima, the North Korean nation-state actor linked to the ongoing high-profile Contagious Interview scam. Threat researchers with Socket and Kieran Miyamoto of the DPRK […]
Security Flaws in Anthropic’s Claude Code Risk Stolen Data, System Takeover
Three critical vulnerabilities found in Anthropic’s Claude Code agentic AI developer tool could be exploited simply by cloning and opening an untrusted project and lead to system takeover, stolen API keys, and credential theft, according to security researchers with Check Point. The security flaws, which Anthropic fixed last year and last month after the researchers […]
The Hidden Security Risks in Modern JavaScript Frameworks and How React Teams Can Reduce Them
React and modern JavaScript frameworks accelerate development—but hide serious security risks. Learn where vulnerabilities come from and how to reduce client-side attack surfaces.
Prompt Injection Isn’t Just a Chat Problem — It’s a DevOps Threat
Prompt injection is evolving into a serious DevOps threat, enabling AI agents to misuse tools, leak secrets and execute unauthorized actions unless governed with least privilege, sandboxing and human approval.
Survey Surfaces More Focus on Software Security Testing and API Security
A global survey of 828 enterprise IT professionals conducted by the Futurum Group finds well over a third of respondents expect their organization to increase spending on software security testing (39%) and application programming interface (API) security (36%) over the next 12 to 18 months. Overall, about 35% said they also plan to make some […]
‘PackageGate’ Vulnerabilities Can Let Attackers Bypass Shai-Hulud Defenses
In the wake of the massive Shai-Hulud supply chain attack that ripped through npm late last year and compromised more than 700 packages and exposed 25,000 repositories, developers in the JavaScript world embraced a two-part defense strategy. The widely adopted playbook called for disabling lifecycle scripts and using lockfiles. “It became the standard advice everywhere […]
Software Supply Chain Threats Are on the OWASP Top Ten—Yet Nothing Will Change Unless We Do
Software supply chain security is steadily moving to the forefront of cybersecurity conversations. In the past, it has been overshadowed by a focus on malware outbreaks, ransomware, endpoint protection, and application vulnerabilities. That changed this month, when OWASP elevated software supply chain failures to third place on its 2025 Top 10 list. The OWASP Top […]
N. Korea Contagious Interview Campaign Turns to VS Code to Deliver Backdoor
Jamf security researchers said state-sponsored espionage actors are using malicious VS Code projects to steal information.
Security Controls That Slow Teams Are Usually Poorly Designed
Discover strategies to enhance security controls in DevOps, emphasizing the shift from gates to guardrails and the importance of designing around real workflows.
DevSecOps In Digital Banking: Balancing Fast Releases With Regulatory Compliance
In the digital banking sector, fast releases of new features and security patches have become the norm. Unfortunately, many institutions lack the organization or the processes necessary to make the speed of necessary releases coincide with the need to follow strict regulatory guidelines. A failure to accurately test and ensure compliance can lead to critical […]
Cursor Allies with 1Password to Secure AI Coding Secrets
Cursor has partnered with 1Password to better protect secrets as applications are developed using an artificial intelligence (AI) coding tool. Nancy Wang, senior vice president and head of engineering for 1Password, said a Hooks Script provides application developers with a secure, just-in-time way to ensure only required secrets are made available to Cursor AI agents […]
Importance of Observability in the DevSecOps Pipeline: Enhancing Security, Compliance, and Collaboration
In today’s rapidly developing software world, security cannot be an afterthought. DevSecOps, the integration of security practices into every phase of DevOps, requires continuous monitoring and actionable insights to detect and mitigate threats effectively. Observability plays an essential role in this ecosystem by providing deep visibility into the security posture of the development process, enabling […]