

One Identity Allies With HashiCorp to Advance DevSecOps
One Identity, a provider of identity management software, has aligned with HashiCorp to make it easier for DevOps teams to implement best DevSecOps practices. Tyler Reese, a senior product manager for One Identity, said via a plugin for HashiCorp Vault developers can now securely manage, monitor, record and audit privileged and administrative access to their […]
Why You Can’t Have DevOps Without Test Automation
The rapid adoption of digital technologies by enterprises to stay nimble, competitive and quality-driven has given digital transformation wide currency. The process facilitates decision-making and allows organizations to innovate, accelerate the time to market and be responsive to customer needs. The world of today is for those enterprises that can quickly turn an idea into […]
Accurics Makes Infrastructure as Code More Secure
Fresh off raising $5 million in funding, Accurics today launched a platform that analyzes the code employed to manage infrastructure as code for vulnerabilities as well as indicators of drift to create a threat model for cloud application workloads and then, if necessary, automatically roll back cloud settings to their last known approved state. Accurics CEO […]
Continuous Security Through Developer Empowerment
Every organization is embracing DevOps to one degree or another. The business impact of shipping software quickly and adapting to market needs is so immense that it has become a requirement—you’re either heading toward DevOps or heading toward bankruptcy. Yet, while our need for speed has increased, so has our need for security—and combining both […]
Enterprise Inertia Slowing Down DevSecOps Integration
DevSecOps has become an increasingly popular topic as enterprises grapple with the continuing challenge of improving their cybersecurity infrastructure. As the first quarter of 2020 has come to a close, are we making significant progress in fully integrating the development, operations and security functions in the enterprise? The term “DevOps” was first used in 2009 […]
Top iOS Security Gotchas
Ensuring the security of user data within your app is critical to building trust in your business and contributing to the online safety of customers. Here’s a list of the top 10 essential security mechanisms that Apple offers to up the security posture of your iOS applications. Adopting these technologies and APIs within your products […]
ClickShare Vulnerabilities May Have Been Patched, But They Mask a Much Bigger Problem
I think we can all recall a time in recent memory where, in a meeting or at a conference, someone has had issues with presentation technology. It happens so often that there is almost an expectation of a clunky experience, at least initially. It stands as no surprise, then, that ClickShare’s seamless app was immediately […]
2020 DevSecOps Community Survey: Of 5,045 Developers, Guess How Many Are Happy?
We just released the seventh annual DevSecOps Community Survey. We captured the pulse of over 5,000 developers in 102 countries. What we learned about trends in DevSecOps will surprise you—especially the parts about how happiness influences company culture, software security and business competitiveness. When we tallied up the results we quickly saw some interesting correlations. […]
HashiCorp Strengthens Vault Secrets Management
HashiCorp has released an update to its HashiCorp Vault platform for managing secrets and encrypting data that now includes an internal storage option that eliminates the need to manage a separate storage backend. Version 1.4 of Vault also adds an OpenLDAP Secrets Engine, which automates the management of static entities within OpenLDAP directories, and the […]
Palo Alto Networks Advances DevSecOps in the Cloud
Palo Alto Networks has updated its Prisma Cloud to make it easier to embrace best DevSecOps processes while deploying workloads in the cloud. New capabilities include the ability to define and apply cybersecurity policies to continuous integration (CI) and continuous delivery (CD) workflows and scanning tools for discovering misconfigurations in cloud infrastructure templates, which is […]
Filling the Skills Gap for Effective DevSecOps
With the rise of DevSecOps comes a whole new need for training and upskilling. It isn’t a secret that the cybersecurity skills gap will only continue to grow. The security skills gap combined with the rise of DevSecOps has introduced hidden challenges organizations must address. The Rise of DevSecOps While DevOps accelerates agility and scalability […]
Six Steps Every Business Should Take to Protect Its Data
Data may or may not be the new oil but it is the growth engine of today’s digital age. Data about a company’s customers, products, services and sales is worth a lot to the company itself, of course, but also to its competitors, as well as to business-savvy hackers. This is why every business, regardless […]
Free Remote Endpoint Protection Solution From Qualys
Qualys today announced it is offering a completely free, 60-day version of its cloud-based remote endpoint protection solution. The product is fully featured, with nothing turned off in the free version. It’s also cloud-based, so there are no worries about hosting the solution. This comes at a perfect time, with so many workers working remotely. […]
42Crunch Extends API Security Alliance With Microsoft
42Crunch this week announced it has extended an existing alliance with Microsoft to now include support for Microsoft Azure Pipelines for its REST API Static Security Testing Tool. Previously, 42Crunch only provided support for the Microsoft Visual Studio integrated development environment (IDE). Dmitry Sotnikov, chief product and marketing officer for 42Crunch, said support for the […]
The DevOps Sweet Spot: Inserting Security at Pull Requests (Part 2)
In part one of this two-part series, I explored how organizations can more effectively automate security quality decisions and discard doing automation for automation’s sake. I shared why security scans need to be faster, more reliable and comprehensive. Only then can security be meaningfully automated into developer workflows without slowing them down. But, the other […]
Catch Emerging Security Risks Earlier by Leveraging Kubernetes Audit Logs
When a Kubernetes deployment suffers a security breach, it can be difficult for security teams to diagnose and identify the source of the intrusion and its impact. Each Kubernetes cluster may host multiple applications, and each application may be composed of dozens or even hundreds of interacting microservices deployed as pods. The complex and dynamic […]
The DevOps Sweet Spot: Inserting Security at Pull Requests (Part 1)
Today’s organizations are increasingly benefiting from the modernization of the software development lifecycle (SDLC), including the adoption of cloud, DevOps, Agile methodologies, containers and more. Thanks to this modernization, organizations are innovating and releasing updates faster than ever before. But these benefits aren’t without challenges. Application security arguably tops the list of challenges. Security has […]
Better Apps and Better Security When You Shift Left
Tens of thousands of people and hundreds of cybersecurity vendors descended on San Francisco at the end of April. While the RSA Conference was the primary draw, there are a number of peripheral events that go on throughout the week as well, such as the Cloud Security Alliance Summit, the CIO/CISO Interchange, BSides San Francisco […]
EP 2: DevSecOps and AppSec
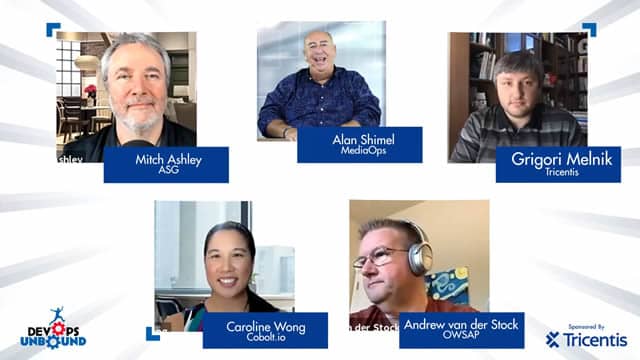
In this second episode of our DevOps Unbound streaming broadcast on TechStrong TV and DevOps.com’s sister site Digital Anarchist, Mitchell Ashley of ASG and Alan Shimel are joined by Caroline Wong, CSO at Cobalt.io; Andrew Van Der Stock, executive director at OWASP; and Dr. Grigori Melnik, CPO at Tricentis, to discuss DevSecOps and application security.
Tenable Allies With Datadog to Drive DevSecOps
Datadog and Tenable have teamed up to enable organizations to adopt best DevSecOps processes. Tenable CTO Renaud Deraison said his company is making the cybersecurity data it gathers via its Nessus vulnerability scanning software available to the monitoring and analytics service provided by Datadog. The goal is to make it easier for DevOps teams to […]
The DevSecOps Landscape is Maturing — We Want to Hear About Your Journey
The race to out-innovate one’s competition has led to high performing organizations chasing increased deployment velocities but often ignoring the quality of parts being used to manufacture their applications. It was 2003 when Bruce Schneier penned, “Today there are no real consequences for having bad security, or having low-quality software of any kind. Even worse, […]
Cybersecurity Fears May Drive Shift to Managed DevOps
Should organizations consider using a managed service for DevOps to keep their platforms up to date and secure? The recent disclosure of a vulnerability that would allow open source Jenkins continuous integration/continuous delivery (CI/CD) platforms to be employed to launch a distributed denial of service (DDoS) attack highlights how challenging it is to secure the […]
DevSecOps: A Renewed Commitment to Secure Delivery, Part 2
If done right, DevSecOps eliminates the cultural roadblocks that often prevent organizations from getting IT security proactively involved with development and operations. Barriers are the last thing any organization should contend with when comprehensive security is an absolute priority at a time when data breaches, intellectual property theft and other cybercrimes can almost immediately cripple […]