

Guess Who’s Coming to JFrog swampUP?
The annual DevOps gathering and JFrog user conference, swampUP 2019, is going to be here before we know it. It’s happening June 17-19 in San Francisco, providing easy access for everyone (it’s just 30 minutes away from SFO airport). What’s swampUP? For the thriving DevOps community, swampUP is the must-attend event where developers, engineers and […]
The Challenge of Securing a Dynamic, Cloud-Based DevOps Environment
The tech landscape has fundamentally changed over the last decade. The steady migration from local data centers to cloud computing combined with the advent of DevOps and the rise of containers have taken what was a more or less contained and relatively stable environment and transformed it into a dynamic, constantly shifting ecosystem. At the […]
CloudBees Acquires Electric Cloud to Advance Continuous Delivery
CloudBees announced it has acquired Electric Cloud as part of an effort to extend the reach of its DevOps portfolio further into the realm of continuous delivery and application release automation (ARA). Announced at the CloudBees Days event in San Francisco, the deal follows CloudBees’ acquisition of Codeship, a provider of a cloud-based continuous integration/continuous […]
DevOps and Security: Be Ready to Shield Your Application
All of us have heard of continuous improvement/continuous delivery (CI/CD). There are many benefits to implementing CI/CD, as it helps seamless integration from end to end for development and deployment processes. CI/CD helps in rapid improvement, shorter release cycles and more, but it also helps with the challenge of handling security effectively at DevOps speed. […]
5 Practical Ways to Deliver Secure Software That Could Actually Work
Almost every aspect of modern life is dependent on technology. As technology becomes even more advanced and pervasive, so, too, does the need for secure software. Today, even the tiniest breach at an organization could result in major loss of sensitive data. Therefore, it is crucial for both the reputation and proper functioning of the […]
Effective Cloud Security Requires a Cloud-Native Mindset
Thousands of developers and cloud security professionals will fill the Moscone Center in San Francisco next week for the sold-out Google Cloud Next ’19 conference. Three days of breakout sessions and keynotes will immerse attendees in deep technical content and opportunities for hands-on learning. It’s all designed to help organizations embrace the cloud. A key […]
How to Design DevSecOps Compliance Processes to Free Up Developer Resources
Anything that gets rolled out quickly in the technological world is a major step forward—as long as it doesn’t compromise security. DevSecOps is able to provide compliance processes far more effectively than before, and without jeopardizing security while also freeing up developer resources. How do you direct your IT team to keep your applications and […]
4 Steps to Introduce DevSecOps to Database Development
Although DevOps was implemented within application development, there is a growing awareness that including the database within DevOps processes is vital to success. We live in a data-driven world and many front-end applications use a database at the back end to collect, process and store customer and user data. The faster development of applications that […]
4 Steps to Improving Your Team’s Continuous Security
A recent npm survey revealed that 77 percent of developers were concerned about the quality and security of the open source libraries they use, while 52 percent said the tools currently available were inadequate. Given the trust issues in open source and the ongoing discovery of website and application vulnerabilities, security should be top of […]
API Security: A Key Part of the Bigger Plan
Standing as the “fuel” powering the customer-driven platform revolution, application programming interfaces (APIs) are the new “it thing” amongst operating systems. APIs are responsible for how apps communicate with each other and have become key components in many digital transformation strategies. Serving as a set of tools for building software application, they have empowered many […]
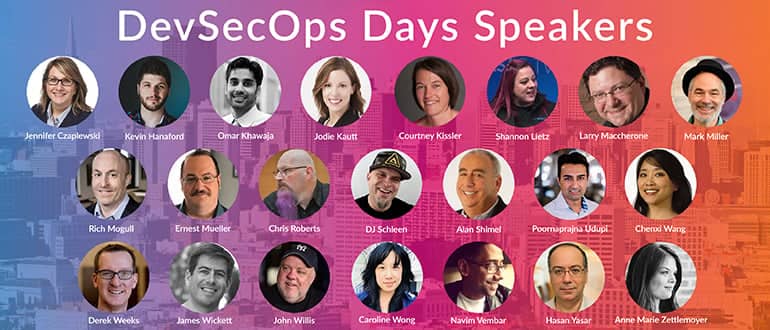
Announcing DevOps Connect: DevSecOps Days Virtual Summit
We just wrapped up our fifth annual DevSecOps Days @ RSA Conference 2019, featuring an exceptional lineup of speakers and a variety of informative sessions, providing an unparalleled experience for all. If you couldn’t make it to San Francisco for RSAC or missed any sessions, we’ll be hosting a virtual version of DevSecOps Days @ […]
DevSecOps: Fortanix Adds Open Source Rust SDK to Build Encrypted Apps
There’s a lot of focus these days on DevSecOps as part of an effort to fix what’s generally acknowledged as a broken cybersecurity paradigm. But instead of trying to ensure every potential vulnerability is addressed before an application is deployed, another idea is gaining momentum among the DevOps community: Build applications that are secure in […]
Survey Finds Mixed Progress on DevSecOps
A survey of 5,558 IT professionals published today by Sonatype in collaboration with CloudBees, Carnegie Mellon’s Software Engineering Institute, Signal Sciences, 9th Bit and Twistlock finds 27 percent of organizations have mature DevOps practices in place, while another 48 percent are still working on improving them. Despite the DevOps works that remains to be accomplished, […]
DevOps Chat: AppSec and DevSecOps with Contrast Security’s Jeff Williams
I have known of Jeff Williams in the security industry for more than several years. He is a well-respected thought leader in AppSec and OWASP. I finally got a chance to catch up with Jeff and talk with him about Contrast Security, the company he co-founded and how it is helping. In this DevOps Chat, […]
DevOps and Security: The Path to DevSecOps
A secure DevOps is highly beneficial for organizations. However, a secure DevOps environment shouldn’t be the end goal. When it comes to DevOps security, it’s important to integrate security right from scratch, secure the entire architecture, automate the security and use this technology to test the environment and the codes and respond to concerns immediately. […]
DevOps Chat: Repos and Nexus Firewall Access, with Sonatype
There are really only two repositories of any scale for software components today: the Nexus repo managed by Sonatype and the Artifactory artifact repo managed by JFrog. Up until now they were separate and apart, and working with one was independent of another. In a big move toward keeping DevOps open and secure, the Sonatype […]
Can DevSecOps Prevent a Zombie Apocalypse?
Making consistent progress within any DevSecOps initiative often can be an overwhelming undertaking. Developers tend to outnumber operations dramatically, with little to no security accountability. This leaves DevSecOps doomed to work with the same network security stack that was originally designed decades ago for on-premises environments. Still, the expectation is to support shrinking deployment cycles […]
Security Testing: Reducing Resistance to Change in an Agile and DevOps World
Software development has evolved, but security testing has not. That has to change In the bad, old days—which, sadly, many are still living in—security testing was tacked onto the end of the development process. Security testing hasn’t been a feature of software engineering for around 15 years now, since agile supplanted waterfall as the primary […]
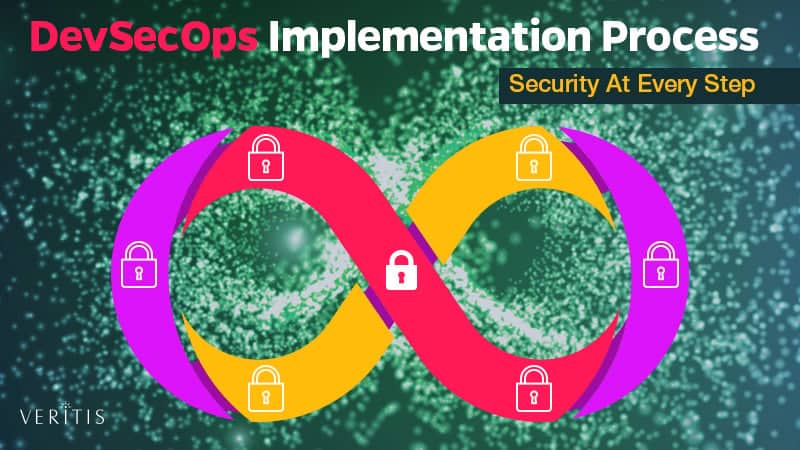
DevSecOps Implementation Process and Road Map – Security at Every Step
DevSecOps is changing our perspective toward security and is equipping us to deal with its challenges in an intelligible manner. The systematic approach of DevSecOps helps us add value to our business processes while ensuring security. Here’s a summary of the key inputs and a recipe for a successful software development project. Implementing DevSecOps with […]
Fail Fast: How Shifting Security Left Speeds Development
How DevSecOps can help organizations increase security, move faster and save money With developers under constant pressure to create more software in less time, the last thing you need is for your code to fail at the end of the development lifecycle. No developer wants to create inoperable or insecure code. We know that most […]
DevOps: Don’t Let Detection Be a Bottleneck for Security
AI and automation can help ensure DevOps security doesn’t impact performance The world revolves around software and internet-based applications—and speed is crucial. Users have very little patience for delays and will quickly jump to something else if performance lags. Organizations have embraced DevOps and containers in an effort to accelerate development and deployment of software […]
Study: CISOs Need to Take Charge of DevOps Security
A new report from CyberArk looks at the complexity that goes into securing emerging DevOps environments, and why CISOs need to take charge to protect them. As digital transformation is pushing more enterprises to adopt DevOps to address their needs for better software delivered faster and more frequently, a huge issue lingers over this strategic […]
Salt Security Unveils Platform to Secure APIs
Salt Security, fresh off raising an additional $10 million in funding, announced a platform that promises to advance the state of DevSecOps by making it possible to detect when application programming interfaces (APIs) are being probed by cybercriminals looking for weaknesses to exploit. Salt Security CEO Roey Eliyahu said the Salt Security API Protection Platform employs […]