

Best of 2021 – Torvalds’ Bug Warning is a Lesson for Linux Users
As we close out 2021, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the third in our series of the Best of 2021. Linux does, occasionally, raise security concerns. While many users see it as the most secure, robust and versatile operating system available — that’s this writer’s […]
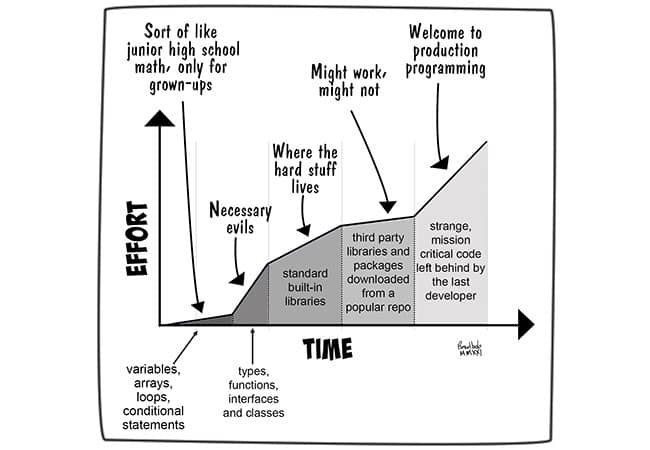
Best of 2021 – Programming Languages: Choose Wisely?
As we close out 2021, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the first in our series of the Best of 2021. We’ve got decades of experience in programming and language adoption under our belt at this point, and there are a few things we can say […]
U.S. Govt. CX EO | Mozilla Revenue | Log4j Latest
In this week’s The Long View: Improving U.S. government CX, how much money Mozilla makes, and the latest on the Log4j/Log4Shell débâcle.
Extending GitOps to the Enterprise
GitOps is a relatively new term, but it continues to gain momentum as more organizations embrace the paradigm. In DevOps, GitOps lands on the software engineering side of the development and operations continuum. Even though GitOps is more likely to be adopted by smaller organizations, larger enterprises can successfully implement GitOps with just a few […]
Reflections: A DevOps Christmas Carol
“Marley was dead, to begin with.” So begins my DevOps Christmas Carol. In this reflection, I am visited by the ghosts of DevOps past, present and future. I hope that, after hearing my story, you will have a better understanding of where DevOps is going based upon where it came from and where it is […]
AWS Outage Outrage | Rusty Linux | ARM Latest
In this week’s The Long View: Amazon Web Services falls on its face, Linux’s move to Rust takes the next step, and the FTC stabs another fatal wound in the horrible Arm/Nvidia deal.
AWS re:Invent Roundup: Private 5G | Graviton3 ARM Chips | DevOps Guru++
In this week’s The Long View: Three things that caught my eye from Amazon Web Services’ re:Invent conference. Private 5G, Graviton3 chips, and something called DevOps Guru for RDS (yes, really).
WTH? We Wanna WFH | DoD Dual-Sources JWCC | More Nvidia ARM Woes
In this week’s The Long View: Working from home is de rigueur, JEDI redux, and more about Nvidia/Arm.
DevOps Teams Struggling to Keep Secrets
A growing number of organizations are suffering security incidents related to exposed secrets in DevOps CI/CD pipelines, according to a recent ThycoticCentrify report. The study paints a troubling picture: Only 5% of survey respondents said most of their development teams use the same secrets management processes and tools. The incidents run the gamut, from secrets […]
Rethinking Programmer Education for Today’s Coders
The proliferation of low-code and no-code applications are changing the landscape for software. In the past decade, growth in these areas has empowered employees to generate solutions at the speed of a digital world, regardless of their technical background. This raises several questions: What kind of programmers do businesses really need? Should they still rely […]
Microsoft Expands Azure DevOps Portfolio
Microsoft has made available a bevy of updates to its DevOps portfolio that, collectively, are intended to increase its share of a wave of applications that will be rolled out across the extended enterprise. Additions to the Microsoft DevOps portfolio were announced at the Microsoft Ignite 2021 conference and include DevOps Workflow Generator, a free […]
GraphQL’s Greatest Strength is Also its Greatest Weakness
Michael Scott: Why don’t I tell you what my greatest weaknesses are? I work too hard, I care too much and sometimes I can be too invested in my job. David Wallace: Okay. And your strengths? Michael Scott: Well, my weaknesses are actually strengths. David Wallace: Oh. Yes. Very good. GraphQL is a new query […]
Couchbase Revamps DBaaS Based on Document Database
Couchbase Inc. has unfurled a revamped database-as-a-service (DBaaS) platform dubbed Couchbase Capella hosted on the Amazon Web Services (AWS) cloud. Scott Anderson, senior vice president for product management for Couchbase, said that as application development continues to evolve, it’s becoming apparent more organizations prefer to have providers of databases manage those platforms on their behalf. […]
Securing Your Software Development Pipelines
Earlier this year, it was announced that the attack on IT management software provider SolarWinds had been used to compromise other organizations, including parts of the United States government. There were several reasons for alarm because of this news, but one of the biggest was the revelation that attackers breached SolarWinds’ software development process and […]
Salt Security Adds Support for GraphQL APIs
Salt Security has extended its platform for securing application programming interfaces (APIs) to include support for APIs built using GraphQL. GraphQL is an open source data query and manipulation language for APIs that was originally developed by Facebook. It provides a more efficient approach to querying data than the REST APIs that are widely used […]
Sysdig Adds Cloud Access Controls to DevSecOps Platform
Sysdig announced today that it is adding a Cloud Infrastructure Entitlements Management (CIEM) capability to its Secure DevOps platform as part of an effort to better enforce least-privilege access within the context of a larger zero-trust approach to cybersecurity. Nick Fisher, vice president of product marketing for Sysdig, said this addition to the company’s core […]
Codenotary Uses Immutable Database to Verify Software Artifacts
Codenotary today unfurled a free notarization and verification service for open source artifacts and containers to enable IT organizations to track the provenance of the components that make up their applications. Dennis Zimmer, Codenotary CTO, said the Community Attestation Service is based on an immutable open source immudb database that cryptographically attaches an identity to […]
A Blueprint for Securing Software Development
Software development has changed dramatically in recent years, as technologies like DevOps, application containers, and cloud-native transform how software is built and distributed. Unfortunately, attackers have been paying close attention to these changes, and have retooled their attack strategies to take advantage of relatively weak security controls in software development and build environments. Attackers recognize […]
Why You Need a Value Stream Delivery Platform
While the pandemic was significantly challenging for businesses, it exposed the need to quickly adapt and change. Software products for internal or client use continue to provide an opportunity for a competitive edge in nearly any industry. Businesses will immerse themselves and compete in the digital economy by consistently producing better software products at an […]

Snyk Extends Tools Portfolio to Drive DevSecOps Adoption
During its online SnykCon 2021 conference this week, Snyk extended Snyk Code, a static application security testing (SAST) tool that already supports the Java, JavaScript and Python programming languages to include support for C#, Ruby, PHP and Go. At the same time, Snyk Open Source, a platform for remediating open source vulnerabilities, has been extended […]
Why an Embedded Analytics Maturity Framework is Essential
Contextual analytics, or embedding analytics directly into a business application’s transactional environment and core workflows, is the most sophisticated stage of business intelligence (BI) currently available to organizations today. It is one level ahead of the traditional integration of analytics, which is a standalone capability presented as a separate dashboard or reporting module. Today, there […]
Transform Mobile DevOps into Mobile DevSecOps
Mobile developers are mostly focused on adding new features and functionality to their apps. Security features—such as RASP protection, obfuscation, encryption, jailbreak/root prevention and MiTM prevention—are usually addressed at the end of the development cycle if they are addressed at all. Unfortunately, most apps ship with significant vulnerabilities. One internal app test showed that most […]