

Why Self-Healing Tests Need a Deployment Gate
When an end-to-end test fails after a front-end change, the repair often looks routine. A class name changed. A button moved. A selector that used to be unique now matches two elements. A self-healing system inspects the page, proposes a new locator, reruns the test, and gets a green result. That green result is useful, […]
Cloudsmith Extends Policies and Controls to Secure Application Binaries
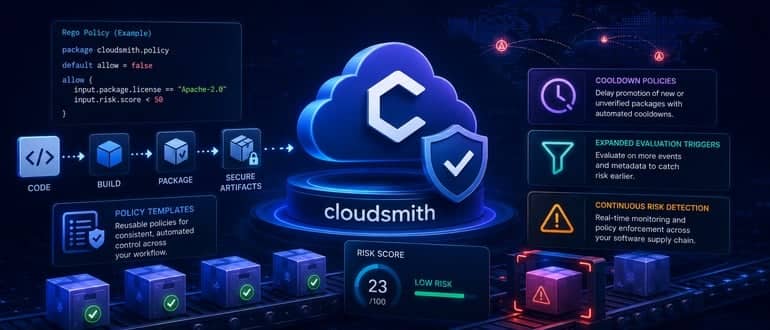
Cloudsmith this week revealed it has expanded the policy management and continuous risk detection capabilities it makes available within its software artifact management platform to now include policy templates, cooldown policies, and expanded evaluation triggers. Alison Sickelka, vice president of product for Cloudsmith, said these additions to the platform will make it simpler to prevent […]
Microsoft’s GitHub Hit by Major Outage as AI-Driven Demand Strains Infrastructure
GitHub, the Microsoft Corp.-owned code hosting platform serving more than 180 million developers, is still reeling from a widespread outage on Monday that severely disrupted software development pipelines globally. The hours-long incident was the latest in a relentless series of reliability failures for a service struggling to keep pace with an unprecedented surge in artificial […]
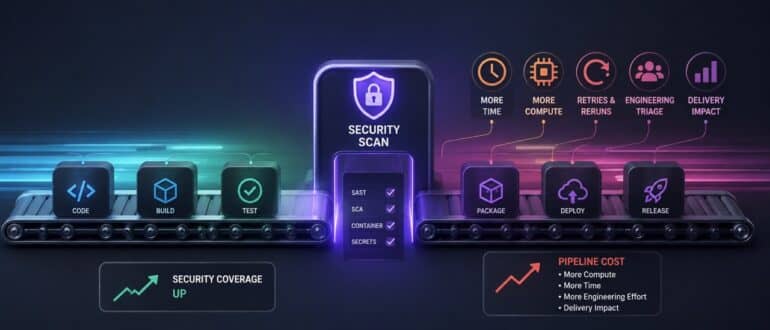
Is Your New DevSecOps Tooling Reducing Work Or Just Adding to It?
Security belongs in the software delivery pipeline. The harder question is where, how often and at what cost. Many pipeline teams eventually add security scanning to CI/CD, and relatively few go back afterward to measure what it actually cost the delivery process. Security coverage went up. Something else changed too, and it is rarely measured […]
Dynatrace Acquires Arize as AI Agents Deepen the Observability Challenge
Dynatrace announced Thursday it has agreed to acquire AI observability company Arize in a $915 million cash and stock transaction. Rick McConnell, CEO of Dynatrace, said the company expects demand for AI observability will keep growing as more AI systems move into production. He said acquiring Arize would speed up Dynatrace’s roadmap, expand its developer […]
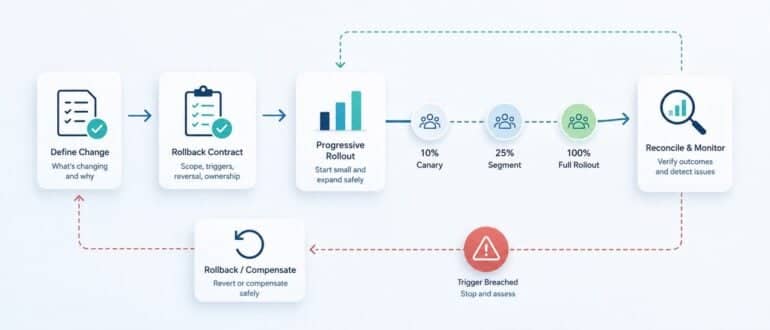
Treat Business Workflow Changes Like Deployments
Business automation often reaches production without the release discipline applied to application code. A routing rule changes, an approval threshold moves, or an integration starts writing to a new system. The edit may happen in a visual builder instead of a repository, but its blast radius is still real: orders can duplicate, customers can receive […]
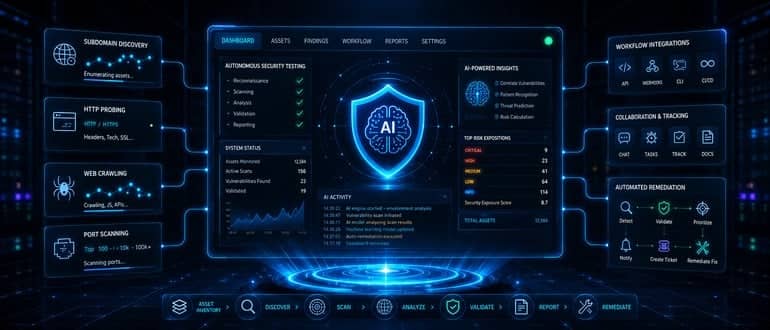
ProjectDiscovery Brings Open Source AI Testing to Vulnerability Discovery
ProjectDiscovery has made available an autonomous security testing platform that leverages an open source artificial intelligence (AI) testing framework to detect and validate vulnerabilities at a lower total cost. Company CEO Rishi Sharma said version 1.0 of the Neo platform is also available via a cloud service that makes it possible for DevSecOps teams to […]
Reflex’s Newly Open-Sourced XY Library Offers Faster Python Charting
A newly open-sourced Python charting library, called XY, from Reflex offers an advantage few other charting tools provide: massive scalability. The library rethinks how to render a set of points on the computer screen, and opens new possibilities for using charts in daily workflows. Most Python charting libraries today, such as Plotly, Bokeh, or Matplotlib, […]
What You Cannot See Will Break Your LLM App: A Practitioner Guide to Production Observability
Traditional application observability was built around a simple mental model: Your code runs, metrics come out and when something breaks, the logs tell you why. Large language models (LLMs) break that model in ways that are not obvious until you have shipped one and watched it misbehave in production. An LLM-powered application can be up, […]
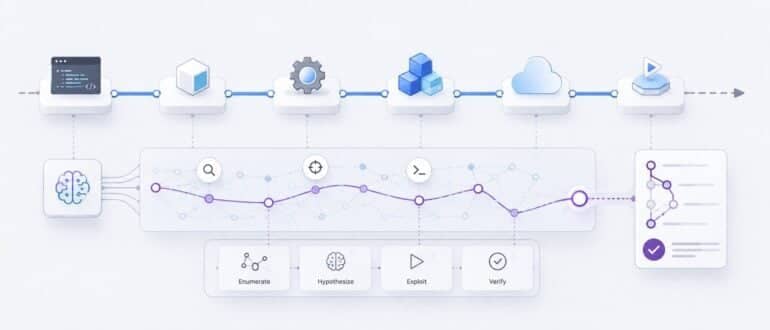
Why CI/CD Security Testing Is Going Autonomous (and Why It Should Stay Local)
Continuous integration and delivery changed the tempo of software. Teams merge dozens of times a day, infrastructure is redefined on every commit, and a new build can reach production in minutes. Security testing never caught up with that tempo. It still lives in two modes that both fight the pipeline instead of moving with it. […]
LiteLLM Attack Affected 2,500 Companies, 434,000 CI/CD Pipelines: CloudSEK
The massive supply-chain attack that compromised LiteLLM in the spring affected more than 2,500 companies and exposed about 434,000 CI/CD pipelines, with victims ranging from top-tier IT and AI companies to cybersecurity firms, SaaS, and enterprises. It rolled up a lot of victims, but also was a high-profile example of the growing trend of threat […]
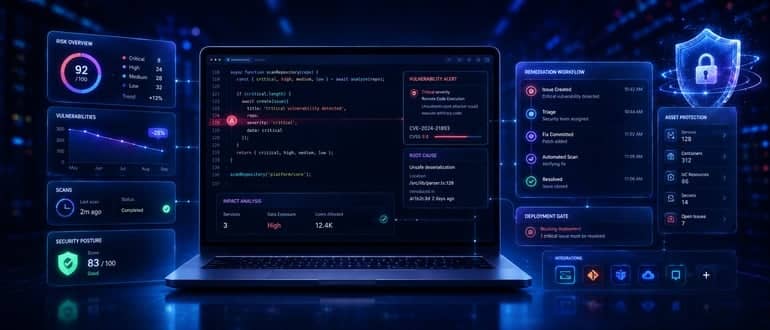
HackerOne Extends Platform Reach to Remediate Source Code Vulnerabilities
HackerOne has added a remediation capability to its H1 Platform that reduces the amount of time required to remediate validated vulnerabilities and other weaknesses affecting specific lines of source code. Nidhi Aggarwal, chief product officer for HackerOne, said H1 Remediation combines artificial intelligence (AI) and crowdsourced research to identify the root cause of issues that […]
Why Reliability Guardrails Are Needed in Every AI Coding Pipeline
We’re in the middle of a reliability reckoning. Thanks to AI, companies are shipping code much faster than before. But if there’s anything to learn from the surge in high-profile outages over the last couple of years, it’s that with more code comes more reliability risks. And when those risks do lead to an outage, […]
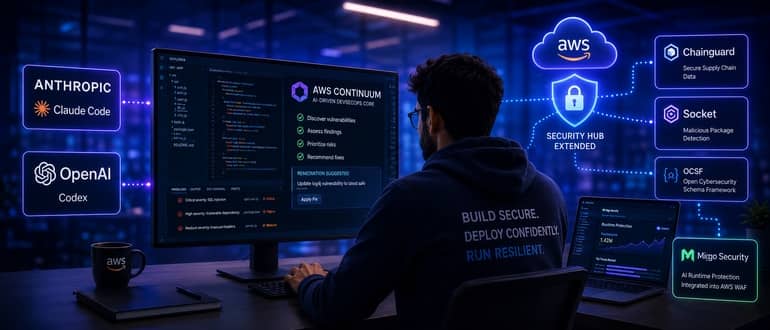
AWS Extends DevSecOps Reach to AI Coding Tools from Anthropic and OpenAI
Amazon Web Services (AWS) this week at the Black Hat USA conference revealed it is working with both Anthropic and OpenAI to integrate their respective coding tools with a service it has developed that makes available artificial intelligence (AI) agents to help application developers write more secure code. Launched earlier this year, the AWS Continuum […]
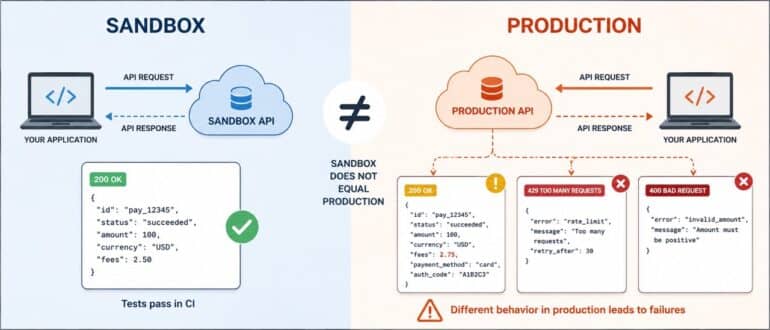
Sandbox Testing for API-Heavy Systems: What Changes When You Don’t Own the Dependency
Sandbox testing works well when your team controls both sides of the integration. You define the service, you define the mock, you know exactly what the sandbox should return. That setup holds up fine for internal microservices and first-party APIs. It starts to break down when you don’t own the dependency. Payment processors, identity providers, […]
RapidFort Extends Open Source Software Security Reach to Runtime Environments
RapidFort today at the Black Hat USA conference announced it has extended its ability to secure open source software to the runtimes that DevOps teams deploy in production environments. Michael Wood, chief marketing officer for RapidFort, said the RapidFort Runtime platform makes it possible to now monitor open source software deployed within a container image […]
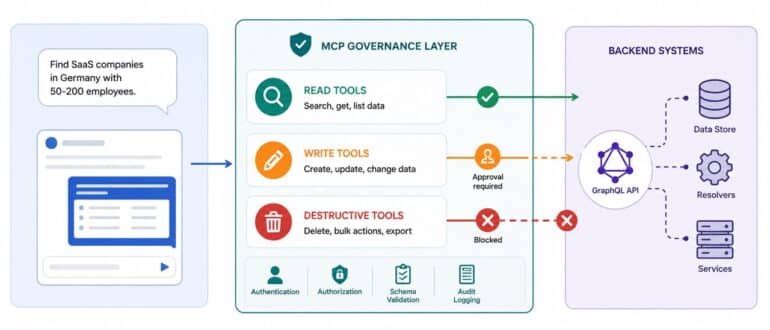
From API Integration to Agent Governance: What Backend Teams Need to Know About MCP
Many MCP projects begin with an existing API and a simple request: expose one backend capability to an LLM client. The quickest route is to wrap an endpoint as a tool and connect it to Claude or another MCP host. Users can then ask for data in natural language instead of navigating a fixed interface. […]
Fast-Moving Shai-Hulud Attack Infects npm Packages with 2 Billion Monthly Downloads
Researchers at Aikido Security and Endor Labs are tracking a fast-spreading supply-chain attack that is compromising a wide range of npm software packages that combined have more than 2 billion installs a month and is stealing a wide range of secrets and other information. According to Ilyas Makari, malware researcher with Aikido, the bad actor […]
N. Korea Group Behind Multiple Open Source Supply-Chain Attacks: Amazon
Amazon’s recent report attributing a series of compromises of open source software libraries to a North Korea-backed threat group encapsulates many of the expanding cyber risks increasingly facing developers, from the growing use of generative AI by bad actors and targeting of code repositories to financially focused attacks by nation-state hackers and the abuse of […]
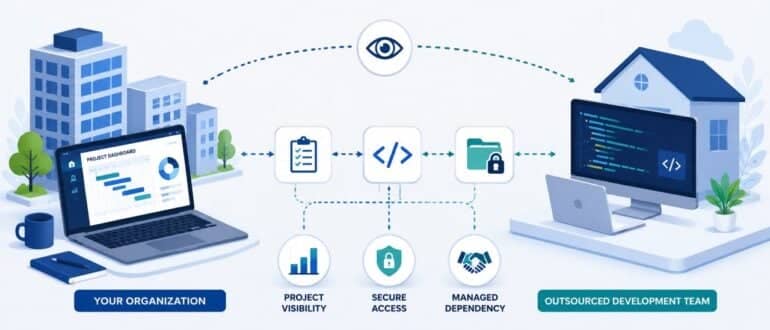
Common Risks of Outsourcing Software Development, and How to Tackle Them
Both SMBs and large enterprises often choose software development outsourcing over developing software in-house. It is no surprise, as partnering with external developers enables companies to bridge IT talent gaps that cannot be filled internally, avoid time-consuming recruiting and training processes, and eliminate expenses associated with salaries and benefits, eventually accelerating software delivery and reducing […]
GitHub Brings Stacked Pull Requests Out of the Shadows
GitHub introduces native stacked pull requests, helping development teams break large changes into smaller, dependency-ordered PRs that are faster and easier to review.
OpenAI Open Sources Codex Security CLI for the Merge Path
OpenAI has released its Codex Security command-line interface and software development kit as open source software under the Apache 2.0 license, providing a new way to bring its AI security scanner into development workflows. The CLI can scan repositories, review staged and unstaged changes before a commit, compare findings across scans and export results for […]
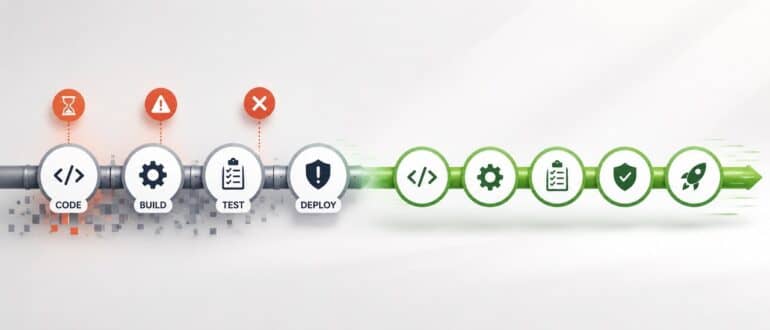
These are 10 CI/CD Pipeline Mistakes That Slow Down Engineering Teams
Continuous software delivery in the digital age has come to depend on CI/CD pipelines. They enable engineering teams to rapidly develop, test, and deploy code while keeping it highly usable and consistent across environments. CI/CD pipelines, however, can themselves become a source of friction as systems start at a small scale and become more complex. […]