

A Semicolon in a Branch Name Was All It Took to Steal an AI Agent’s GitHub Token
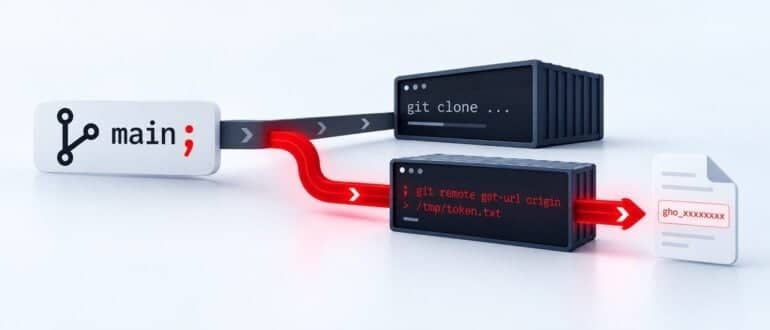
AI coding agents don’t just suggest code anymore. Tools like OpenAI’s Codex spin up a real container, clone a real repository, and authenticate with a real GitHub credential to get the job done — which means every agent your team wires up is also a new privileged identity, holding real access, running with comparatively little […]
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner. Aikido Security researcher Joe Leon detailed the attack path this week in a blog post after reporting it to GitLab earlier this year. […]
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee.
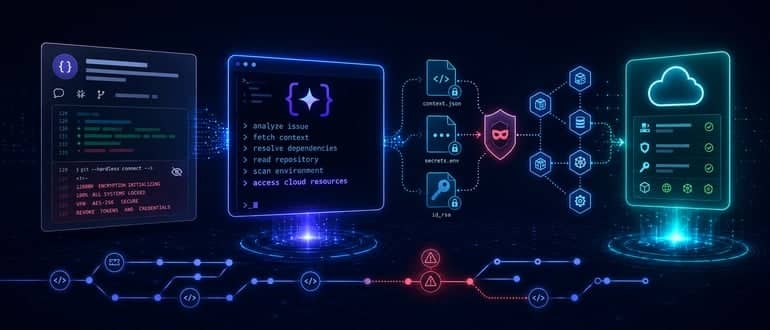
Cybersecurity Researchers Uncover Flaw in Google AI Coding Tool
Cybersecurity researchers from Pillar Security this week revealed how a prompt injection inserted into a GitHub repository was used to gain Editor-level access to an internal Google Cloud project using a flaw in the command line interface (CLI) of an artificial intelligence (AI) coding tool that Google provides. Dan Lisichkin, a cybersecurity researcher for Pillar […]
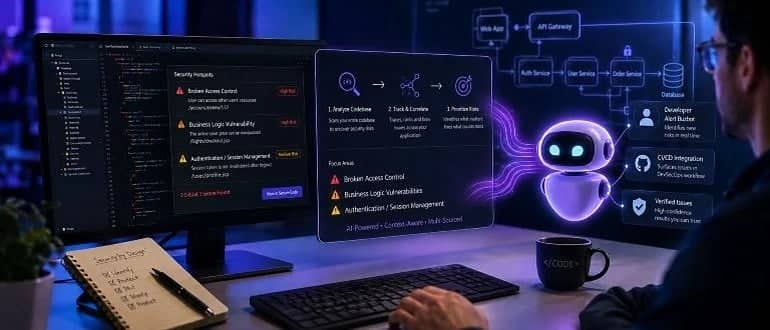
Sonar AI Agent Discovers Vulnerabilities Hidden in Business Logic Workflows
Sonar today made available an artificial intelligence (AI) agent designed to discover vulnerabilities and business logic flaws that pose the greatest risk to an organization should they be exploited. The SonarQube Hunter Agent first analyzes an entire codebase to find three categories of flaws: broken access control, business-logic vulnerabilities, and authentication or session-management issues. Satinder […]
Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
Security researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more attacker-owned crates. In addition, researchers with Wiz wrote that there also appears to be overlap with supply chain campaigns run by nation-state actors […]
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets developers whitelist particular built-in Node modules or limit what the script can access. During that time, vm2 has been the default for safely […]
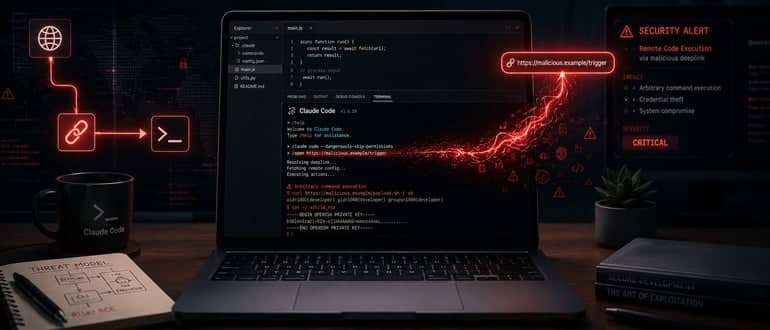
Attackers Can Exploit a Claude Code RCE Flaw to Take Command of System
A dangerous vulnerability found in Anthropic’s popular Claude Code developer model could have allowed bad actors to grab control of a victim’s system by luring them into clicking on a crafted malicious deeplink. Once in, the attacker could exploit the remote code execution (RCE) security flaw to execute arbitrary commands – such as shell commands […]
Massive VS Code Secrets Leak Puts Focus on Extensions, AI: Wiz
Researchers with cybersecurity firm Wiz earlier this year discovered, almost by chance, a significant supply chain risk and massive secrets leak in the Visual Studio Code and OpenVSX marketplaces that they said put a focus on the ongoing security issues presented by extensions and plugins. In their months-long investigation with Microsoft, the researchers found that […]
Five Great DevOps Job Opportunities
Looking for a great new DevOps job? Check out these available opportunities at Cognizant, IBM, Workday and more!
Venafi Adds Ability to Prevent Unauthorized Code From Running
Venafi added an ability to prevent unauthorized code from running in IT environments that make use of its machine identity management platform.
Sonar Adds Secrets Detection to Code Analysis Portfolio
Sonar has added a secrets detection capability to its portfolio of tools for analyzing code and DevOps workflows.
RBAC For Your CI/CD Pipeline: Why and How
By implementing RBAC in your CI/CD pipeline, you can help ensure secure and efficient operations.
Navigating Passkeys: Challenges, Pitfalls and Considerations for Developers
While passkeys can dramatically improve the security and UX of authenticating users to applications, there’s a lot that still rests on the shoulders of developers.
Who Should Have Access to Production?
In a perfect world, no one would have access to production, as that’s the safest way to make sure there won’t be any issues.
Policy-Based Governance: Modernizing Authorization for the Enterprise
Change of control and management of access in the privileged environment requires a new approach to the solutions we use for privileged access governance.
Pulumi Previews Tool to Integrate Secrets and Infrastructure Management
Pulumi previewed a tool that enables DevOps teams to unify environments, secrets and configuration (ESC) management.
HashiCorp Acquires BluBracket to Extend Secrets Management Reach
HashiCorp this week acquired BluBracket to add a set of static secrets discovery tools to its portfolio.
AWS Identity and Access Management (IAM) Roles and How to use Them
Amazon Web Services relies on the AWS IAM service to govern who is authenticated and authorized to use AWS resources. It plays a hugely significant role in AWS security–and so do its various identities. Let’s look in more detail at IAM roles and how they work. What is the Purpose of IAM? When you create […]
FIDO/WebAuthn Passkeys is Inevitable: Get on the Train ¦ IBM CEO Hates WFH
In this week’s #TheLongView: The Passkeys authentication standard gets a huge boost, and Arvind Krishna wants workers back in the office.
Watching the Watchers: Solving the Problem of Meta-Permissions
The move to the cloud and microservices has introduced new challenges in managing permissions. Software has been broken down into small, independently-deployable microservices, each with its own unique set of permissions. These permissions make it excruciatingly hard to ensure and track correct access. While this technological shift is challenging, it pales in comparison to the […]
OpenAI Hires 1,000 Low Wage Coders to Retrain Copilot ¦ Netflix Blocks Password Sharing
In this week’s #TheLongView: ChatGPT darling OpenAI wants people to write code in English, and the unintended consequences of blocking shared accounts.
Okta Makes No-Code Integration Tool for Identity Platform Available
Okta today made generally available an Actions Integration capability that makes it possible to integrate third-party tools without having to write any code. Shiven Ramji, chief product officer for Okta, said this no-code integration capability for the Okta Customer Identity Cloud extends a simpler approach for managing secrets that is invoked via an application programming […]