

Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner. Aikido Security researcher Joe Leon detailed the attack path this week in a blog post after reporting it to GitLab earlier this year. […]
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee.
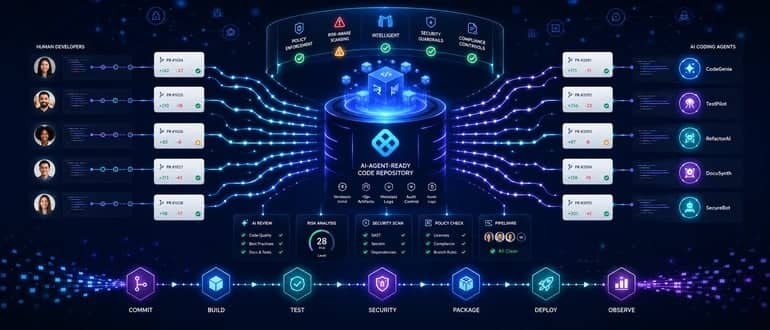
Flaw in DeepSeek Harness AI Coding Tool Let Agents Disable Their Sandbox
News of the now-fixed vulnerability comes amid growing concerns that AI vendors do not in have complete control of their autonomous agents.
JFrog Moves to Secure Agentic Engineering Workflows
JFrog today at its swampUP 2026 conference added a zero touch remediation capability that ensures the most secure version of a binary is provided even when application developers request a version that has known vulnerabilities. Additionally, JFrog is adding tools and capabilities to secure artificial intelligence (AI) agents that have been embedded within a DevOps […]
Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
Security researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more attacker-owned crates. In addition, researchers with Wiz wrote that there also appears to be overlap with supply chain campaigns run by nation-state actors […]
npm v12 Shuts Down a Popular Malware Trick — But the Threat Isn’t Going Away
For years, one of the easiest ways to sneak malware onto a developer’s machine has been to hide in plain sight. Install a package from npm, and any lifecycle script bundled with it runs automatically — no review, no approval, no second look. Attackers have known this for a long time, and they’ve used it […]
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets developers whitelist particular built-in Node modules or limit what the script can access. During that time, vm2 has been the default for safely […]
GitHub Sharpens CodeQL’s Eye on Actions Workflows and Modern JavaScript
GitHub Actions pipelines have become one of the quieter attack surfaces in software development. They pull in third-party actions, cache dependencies, and pass secrets between jobs, often without anyone reviewing the workflow file as closely as they’d review application code. That gap is exactly where cache-poisoning and output-clobbering attacks live, and it’s why GitHub keeps […]
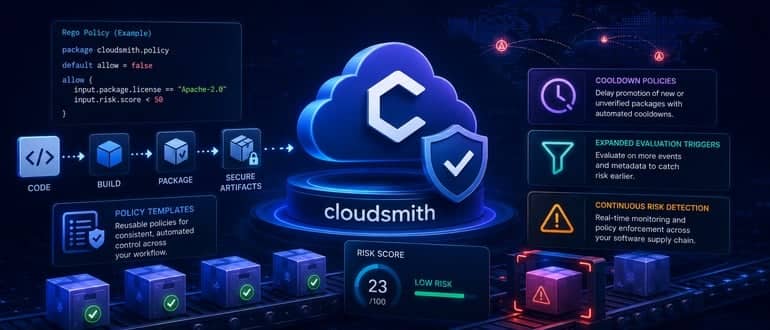
Cloudsmith Extends Policies and Controls to Secure Application Binaries
Cloudsmith this week revealed it has expanded the policy management and continuous risk detection capabilities it makes available within its software artifact management platform to now include policy templates, cooldown policies, and expanded evaluation triggers. Alison Sickelka, vice president of product for Cloudsmith, said these additions to the platform will make it simpler to prevent […]
GitHub Breach Tied to Malicious VS Code Extension Exposes Thousands of Internal Repositories
GitHub says attackers accessed thousands of internal repositories after a company employee’s device was compromised through a malicious Visual Studio Code extension, though the company said it has removed the malicious extension, isolated the compromised endpoint, and launched an investigation. The company confirmed that approximately 3,800 internal repositories were affected. GitHub stated that investigators have […]
Cyber Threats to DevOps Platforms Rising Fast, GitProtect Report Finds
The number of incidents targeting DevOps platforms grew 21% in 2025, but the amount of downtime jumped almost 95%, the security firm said.
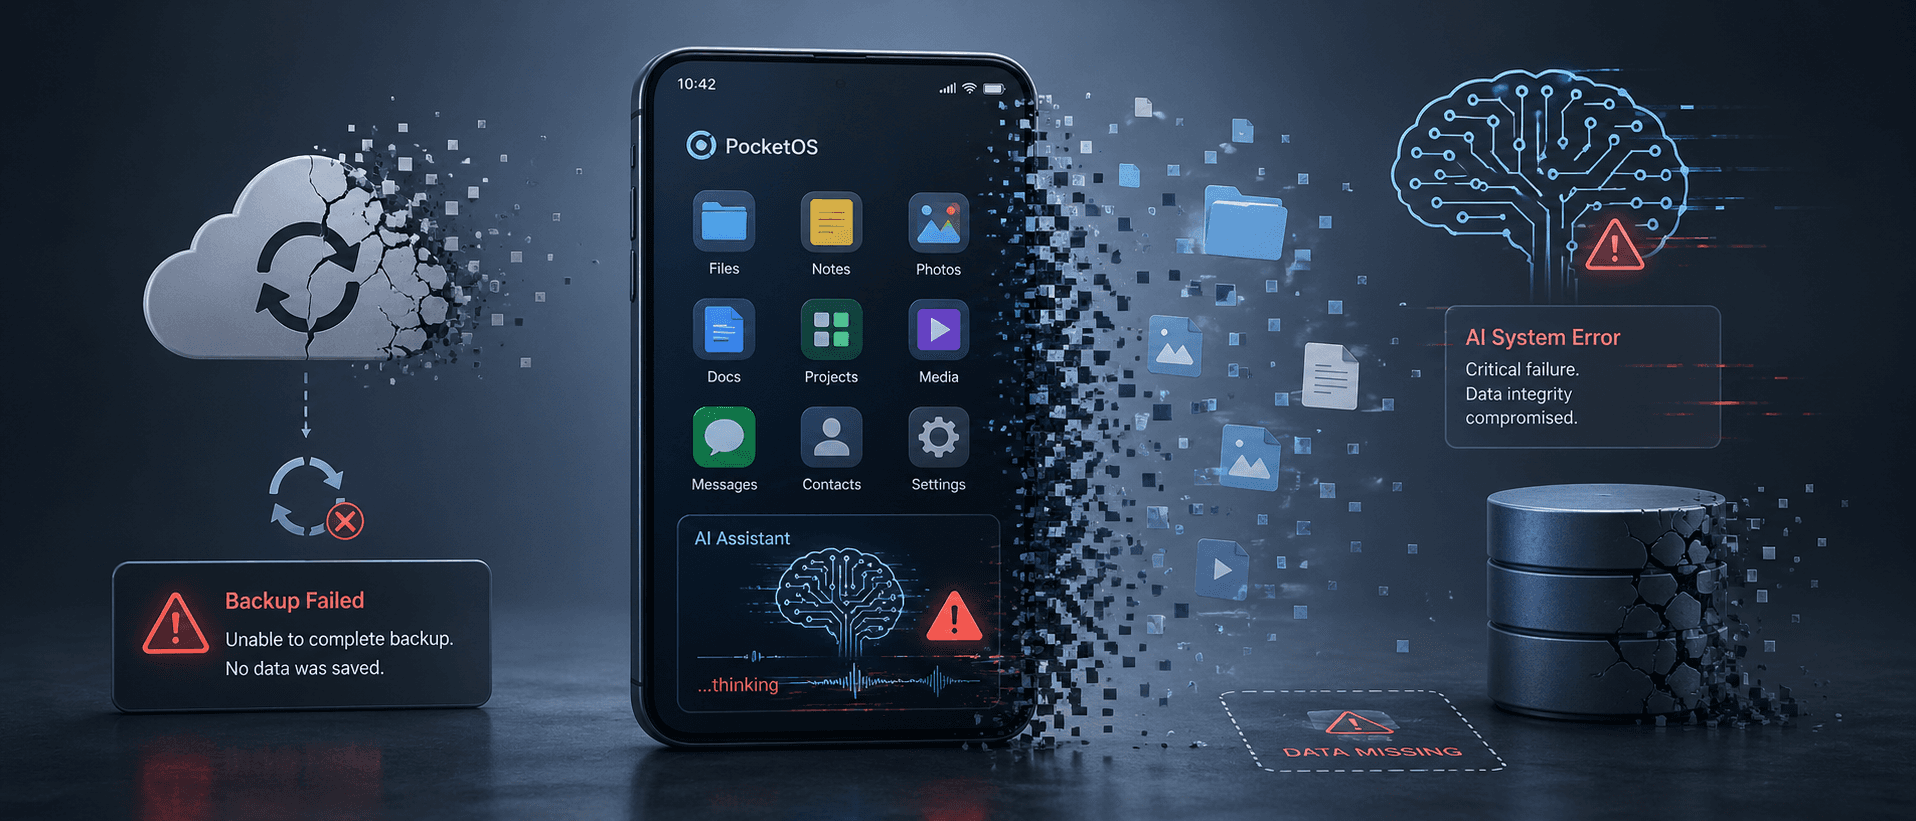
When AI Goes Really, Really Wrong: How PocketOS Lost All Its Data
You can’t make this crap up. You just wish you could. Jer Crane, founder of the small vertical software company, PocketOS, reported on X that the AI Cursor coding agent and a Railway backup misconfiguration combined to briefly wipe out the company’s car‑rental customer production data. Not some of the data. All of it. That’s […]
Sophisticated Supply Chain Attack Targeting Trivy Expands to Checkmarx, LiteLLM
The supply chain attack that compromised Aqua Security’s Trivy open source security vulnerability scanner and its associated GitHub Actions earlier this month continues to expand, with software development tools from Checkmarx and LiteLLM being the latest victims of the sophisticated campaign. The threat group behind it, TeamPCP, is using the attacks to create persistence and […]
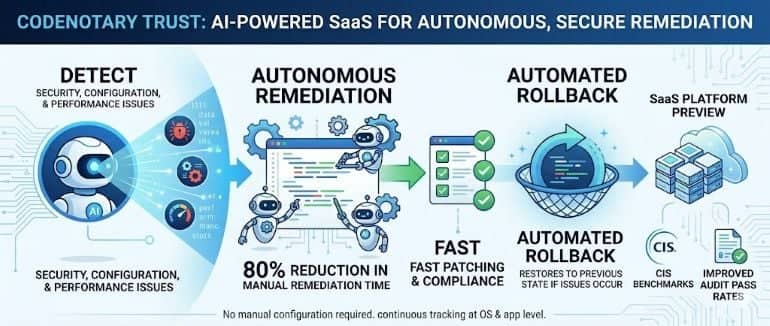
Codenotary Previews AI Platform to Autonomously Detect and Remediate IT Issues
Codenotary is previewing a software-as–a-service (SaaS) platform that enables artificial intelligence (AI) agents it has developed to autonomously detect, prioritize, and fix security, configuration, and performance issues. Company CEO Moshe Bar said the Codenotary Trust platform also enables continuous vulnerability tracking at both the Linux operating system and application level. Once an issue is detected, […]
N. Korean Famous Chollima Hackers Use Malicious npm Packages to Steal Data
A group of more than two dozen malicious npm packages used to steal secrets and credentials from software developers has all the hallmarks – from infrastructure to operations – of Famous Chollima, the North Korean nation-state actor linked to the ongoing high-profile Contagious Interview scam. Threat researchers with Socket and Kieran Miyamoto of the DPRK […]
‘PackageGate’ Vulnerabilities Can Let Attackers Bypass Shai-Hulud Defenses
In the wake of the massive Shai-Hulud supply chain attack that ripped through npm late last year and compromised more than 700 packages and exposed 25,000 repositories, developers in the JavaScript world embraced a two-part defense strategy. The widely adopted playbook called for disabling lifecycle scripts and using lockfiles. “It became the standard advice everywhere […]
Attackers Testing New Strain of Shai-Hulud on npm: Aikido
Threat actors behind the virulent Shai-Hulud worm that wreaked havoc in open npm repositories toward the end of 2025 apparently are trying out a new strain that comes with slight modifications. Security researchers with Aikido Security, who have been tracking Shai-Hulud for months, wrote in a report that was updated January 2 that there doesn’t […]
Crates.io Removes Malicious Rust Package Targeting Web3 Developers
A malicious Rust package that was found to be downloading payloads aimed at stealing cryptocurrency was removed from the crates.io Rust package registry, along with another package by the same author that appeared benign but was dependent on the first. The crates.io team removed both packages this week after security researchers with Socket alerted it […]
Typosquat Supply Chain Attack Targets Go Developers
A backdoor that impersonates a widely used database module in the popular Go programming language can give hackers control of infected systems, according to a senior threat intelligence analyst with developer-focused platform provider Socket. The malicious package, which the threat actor first published in November 2021 and remains in the Go Module Proxy, typosquats the […]
CISA Pushes Steps to Better Secure Software and Product Designs
The country’s top cybersecurity agency is urging developers to take steps to ensure the software they’re building and the products they roll out are secure and protect end users. The Cybersecurity and Infrastructure Security Agency (CISA) this week rolled out a series of recommendations that it wants businesses and critical infrastructure organizations to adopt to […]
White House to Spend $11 Million to Study Open Source Software Use
Hardening the security around open source software has been a key part of the White House’s larger cybersecurity efforts since President Biden released his executive order for improving the United States’ security posture in May 2021, only months after taking office. Now the Biden Administration and the Department of Homeland Security (DHS) are putting $11 […]
Does More Money Improve Open Source Security?
It sounds simple: If you pay developers more money they’ll improve the quality and security of their code. The evidence isn’t so clear.
OpenSSF warns of Open Source Social Engineering Threats
Linux dodged a bullet. If the XZ exploit had gone undiscovered for only a few more weeks, millions of Linux systems would have been compromised with a backdoor. We were lucky. But can we stay lucky? The Open Source Security Foundation (OpenSF) and the OpenJS Foundation revealed that a similar hackling attempt had targeted several […]