

How Much Is That AI Subscription in the Window?
An analysis of the escalating AI subscription wars between Anthropic and OpenAI, highlighting the “Single Prompt Sinkhole” phenomenon where power users exhaust $100/month limits in hours and the industry’s shift toward observability to justify opaque, agentic-heavy pricing models.
LayerX: Anthropic’s Claude Code Can Easily Be Easily Weaponized
LayerX researchers were able to convince the popular AI coding tool to bypass its guardrails and execute malicious instructions.
Bad Actor Drops 36 Malicious Packages in npm, Targets Guardarian Users
The npm code repository is again being used by a bad actor to launch a supply chain attack that includes three dozen malicious packages that appear as Strapi CMS plugins but deliver a range of threats. Strapi is a popular open source headless Node.js content management system developers use to build, manage, and expose content […]
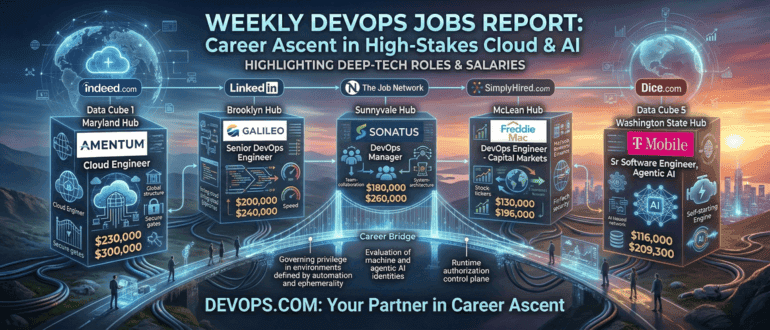
Five Great DevOps Job Opportunities
Explore this week’s top DevOps and Platform Engineering roles. From $300k Cloud Engineering in Maryland to cutting-edge Agentic AI positions at T-Mobile.
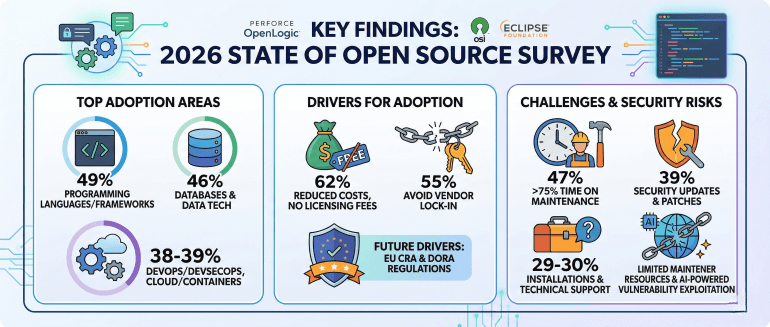
Survey Surfaces Increased Reliance on Open Source Software to Build Apps
Open source adoption is surging, with 49% of IT teams increasing usage. However, 47% of staff spend 75% of their time on maintenance. Explore the impact of AI threats and EU regulations like CRA and DORA.
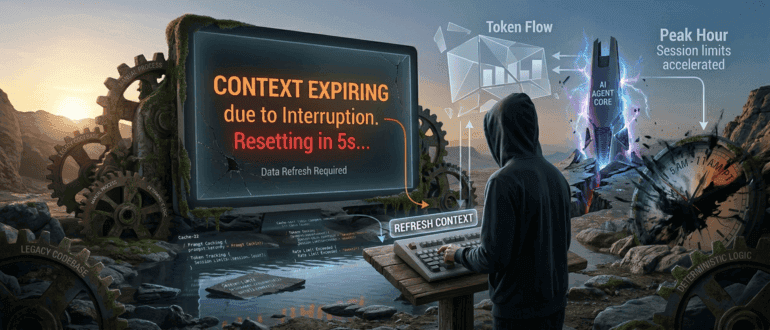
Developers Using Anthropic Claude Code Hit by Token Drain Crisis
Anthropic’s Claude Code users report Max tier quotas exhausting in under 20 minutes. Explore the “Cache-22” of prompt caching, session limits, and why AI coding “opacity” is stalling developer workflows.
North Korean Hackers Suspected in Supply Chain Attack on Popular Axios Project
The threat actor targeted a highly popular open source project with more than 100 million weekly downloads, creating a large “blast radius.”
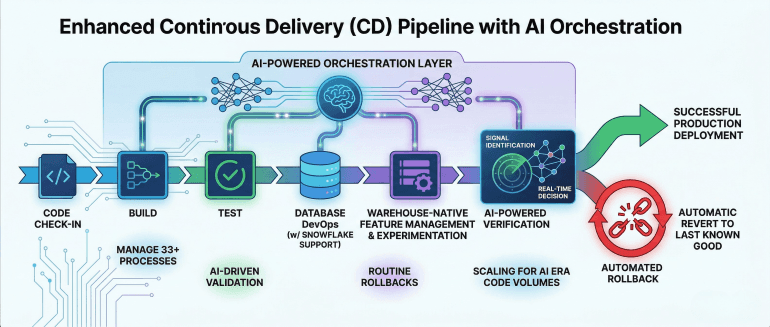
Harness Extends CD Platform to Address AI Coding Challenges
Harness expands its CD platform to tackle the “AI code explosion” with automated rollbacks, snowflake support, and warehouse-native feature management.
OpenTelemetry Gets Kotlin Multiplatform API & SDK
OpenTelemetry expands its observability reach with a native Kotlin Multiplatform API and SDK. Contributed by Embrace, this update enables vendor-neutral telemetry across JVM, iOS, and web, offering idiomatic Kotlin support and optimized performance for mobile and client-side applications.
Tekton Kubernetes-Native CI/CD Project Reaches CNCF Incubation
The CNCF TOC has voted to accept Tekton as an incubating project. As a Kubernetes-native framework for CI/CD, Tekton enables developers to build, test, and deploy across clouds by treating pipelines as standard K8s resources. Originally part of Knative, it now offers a modular ecosystem including Triggers and Chains for supply chain security, integrating deeply with Argo CD and Sigstore.
Five Great DevOps Job Opportunities
Explore this week’s top DevOps career opportunities featuring roles at SAP, Maximus, Inc., and Bellota Labs. Salaries range from $115k to $337k for senior and lead positions.
Sophisticated Supply Chain Attack Targeting Trivy Expands to Checkmarx, LiteLLM
The supply chain attack that compromised Aqua Security’s Trivy open source security vulnerability scanner and its associated GitHub Actions earlier this month continues to expand, with software development tools from Checkmarx and LiteLLM being the latest victims of the sophisticated campaign. The threat group behind it, TeamPCP, is using the attacks to create persistence and […]
Five Great DevOps Job Opportunities
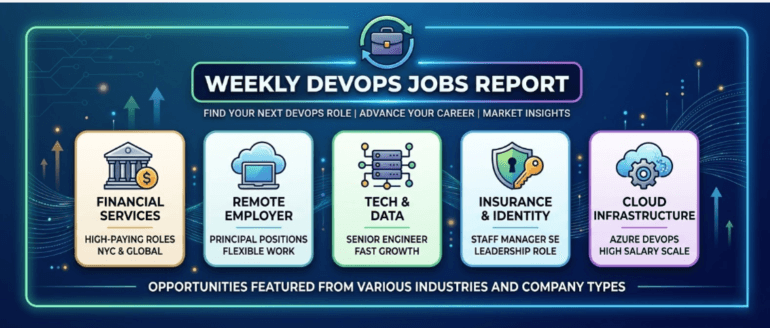
Explore the latest DevOps.com weekly jobs report. Highlighting premier opportunities at Bank of America, Microsoft, and GEICO, with salary insights up to $300,000 for senior engineering and platform leadership roles.
Two Malicious npm Packages Aim to Steal Credentials and Other Secrets
Bad actors took over a npm maintainer account and have published two malicious packages designed to steal credentials, API keys, and other secrets from the computers of victims who download them from the repository. Analysts with Sonatype’s Security Research Team wrote in a report that the two packages – sbx-mask and touch-adv – likely are […]
OpenAI Bolsters AI Coding with Acquisition of Python Toolmaker Astral
OpenAI announced Thursday that it has reached an agreement to acquire Astral, the startup behind some of Python community’s most popular open-source developer tools. The acquisition marks further escalation in the rapidly evolving artificial intelligence (AI)-assisted development market, which has led to a coding war between OpenAI and its primary rivals, including Anthropic and the […]
Java 26 Arrives With AI Integration and a New Ecosystem Portfolio — What It Means for DevOps Teams
Overview of Java 26 emphasizing performance, concurrency, security, HTTP/3, and the new Java Verified Portfolio—positioning the JVM as a supported infrastructure layer for enterprise AI workloads and easing DevOps modernization of large Java estates.
When Code Becomes Cheap, Engineering Becomes Governance
AI agents can now generate in minutes what once took teams weeks, but the real shift is not faster coding. It is the collapse of code scarcity. As software production becomes industrialized, the job of engineers is moving from writing lines to governing systems, managing risk and deciding what should exist in the first place.
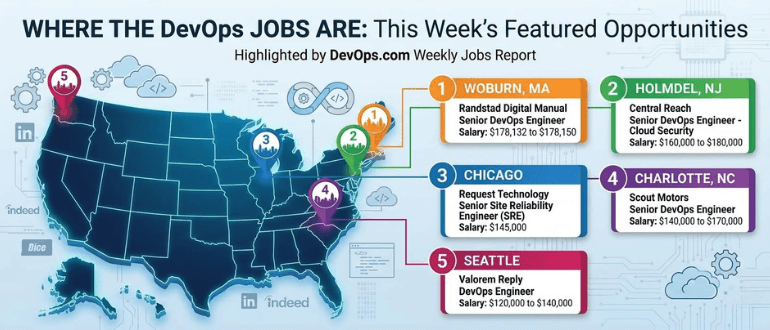
Five Great DevOps Job Opportunities
Weekly DevOps jobs roundup, this week highlighting top roles in Massachusetts, New Jersey, Chicago, Charlotte and Seattle, with pay ranges and hiring trends to help DevOps pros advance careers.
Sorry, Charlie, StarKist Wants AI With Good Taste
A surprising AI experiment showed that feeding a model sloppy code didn’t just produce bad programming, it produced bad behavior. The result points to something philosophers and DevOps engineers have long understood: Character, culture and incentives shape systems far more than rules alone.
The Observability Bill is Coming Due – and AI Wrote Most of It
Observability has always had a data quality problem. AI coding agents just made it catastrophically worse. Shimmy sits down with the co-founders of Sawmills to dig into why unmanaged telemetry is the unglamorous DevOps crisis that is quietly killing budgets — and what an agentic telemetry management platform actually does about it.
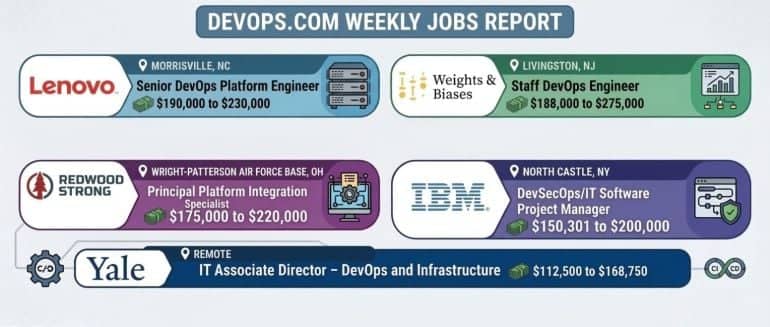
Five Great DevOps Job Opportunities
Latest DevOps Jobs report highlights opportunities at Lenovo, IBM, Yale and Weights & Measures. Find out more here.
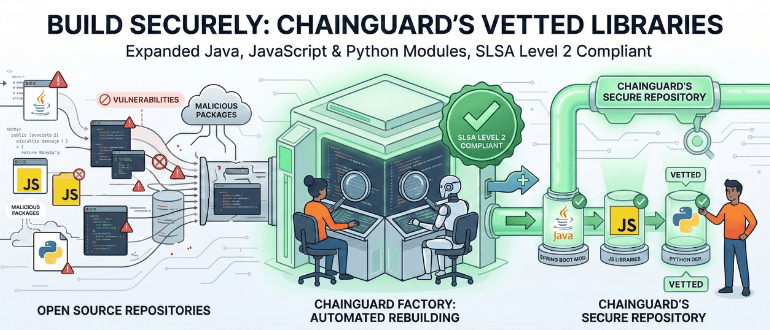
Chainguard Expands Repository to Add More Secure Open Source Libraries
Learn how Chainguard is strengthening software supply chains by expanding its secure repository of Java, JavaScript, and Python libraries, enabling DevOps teams to access components compliant with SLSA framework standards.
N. Korean Famous Chollima Hackers Use Malicious npm Packages to Steal Data
A group of more than two dozen malicious npm packages used to steal secrets and credentials from software developers has all the hallmarks – from infrastructure to operations – of Famous Chollima, the North Korean nation-state actor linked to the ongoing high-profile Contagious Interview scam. Threat researchers with Socket and Kieran Miyamoto of the DPRK […]