

Modernization Is Not Migration
Modernization worked only if the platform became easier to change, easier to understand and safer to run under pressure. That is not a philosophical position — it is a measurable one.
Why CI-Based Security is Too Late for Modern Node.js Projects
Most Node.js teams rely on CI pipelines to tell them whether their dependencies are secure. By the time that feedback arrives, however, the most important decisions have already been made.
These are 10 CI/CD Pipeline Mistakes That Slow Down Engineering Teams
Continuous software delivery in the digital age depends on CI/CD pipelines, which enable engineering teams to rapidly develop, test, and deploy code while maintaining high usability and consistency across environments.
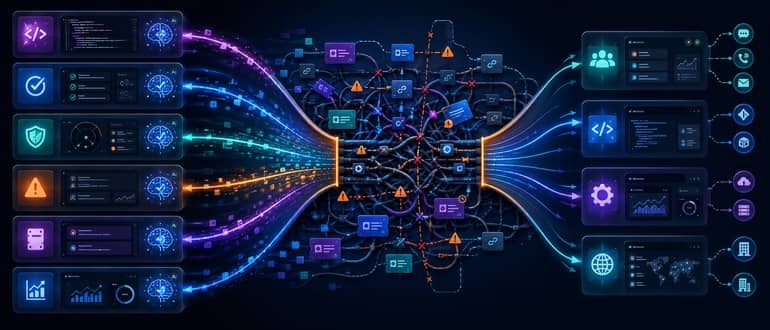
The Bottleneck Isn’t Coding Anymore. It’s Verification
The teams that come out ahead in the next two years won’t be the ones that adopted agents fastest. They’ll be the ones that invested in verification capacity with the same seriousness they invest in production capacity: Tests, policies, audit logs, rollout controls.
Mastering the Blast Radius, Deployment Without Fear- Progressive Delivery in Modern DevOps
‘Progressive delivery’ is the modern evolution of continuous delivery, designed to reduce the blast radius of new features and decouple ‘deployment’ (moving code to production) from ‘release’ (exposing features to users).
Shift-Left Performance Testing in CI/CD: A Practical LoadRunner Framework
CI/CD pipelines speed up software delivery, but performance testing is often delayed, resulting in late feedback and costly fixes. Many teams run tests earlier but fail to enforce performance as a deployment gate.
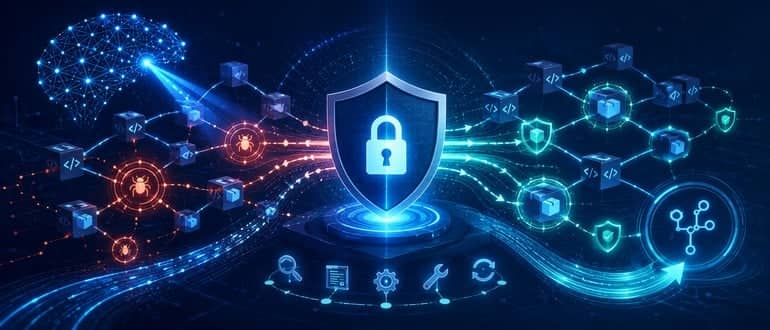
Akrites: The Latest Attempt to Protect Open-Source From AI Attacks Has Arrived
Akrites, a new Linux Foundation initiative backed by many of the world’s largest tech and financial firms, is the industry’s latest attempt to get ahead of AI‑accelerated software supply chain risks by hardening critical open source projects before attackers can exploit them. On June 25, the Linux Foundation unveiled Akrites, a coordinated industry program designed […]
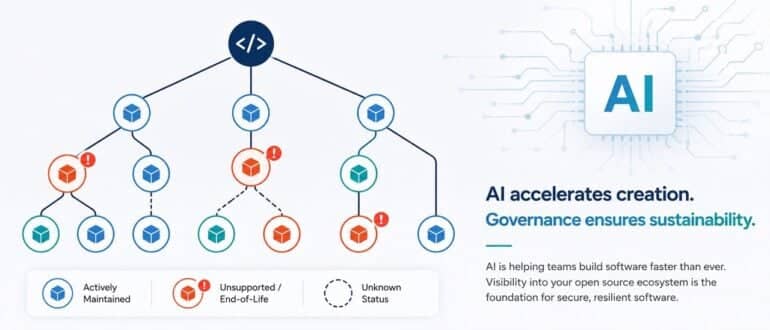
AI Is Exposing a Growing Blind Spot in Open Source Security
With AI, teams across organizations are now building internal applications faster than ever, often pulling in open source libraries and frameworks without much thought about long-term support, lifecycle management, or security ownership. An unintended consequence of this is that unsupported open source software (OSS) is quietly spreading across environments faster than security and engineering teams […]
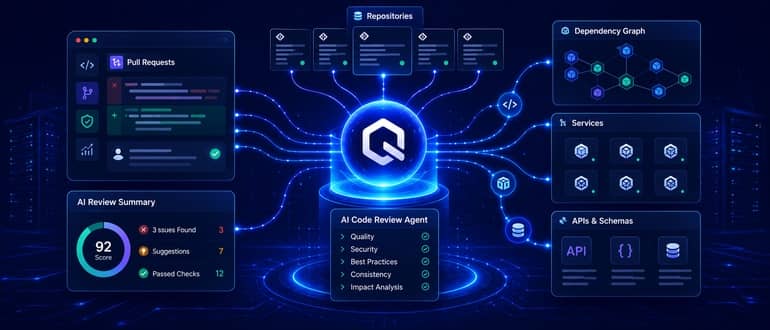
Qodo Extends Reach and Scope of AI Code Review Platform
Qodo this week extended its platform for managing code quality and governance to enable an artificial intelligence (AI) agent to review code spanning multiple repositories. Additionally, version 2.8 of the Qodo platform adds a custom rules miner that discovers coding patterns from existing codebase behavior and pull request (PR) history that are then used to […]
HeroDevs Allies with Commonhaus Foundation to Support Open Source Software
HeroDevs this week revealed it has joined the Commonhaus Foundation as the founding member of the Open Source Sustainability Initiative (OSSI) after establishing partnerships with the open source Hibernate, Jackson, and Quarkus communities to provide commercial support for older versions of these frameworks. OSSI is a framework administered by the Commonhaus Foundation through which governance […]
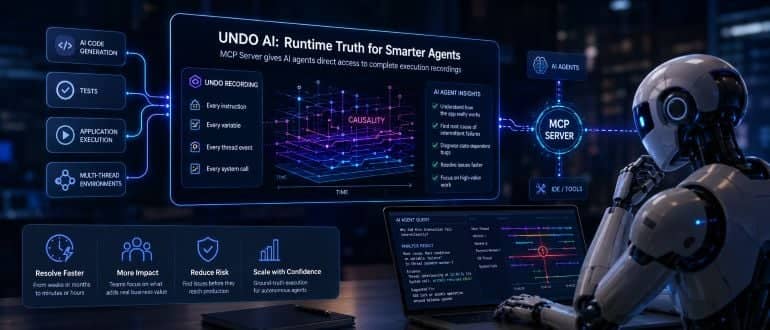
Undo Enables AI Agents to Diagnose Root Cause of Application Issues
Undo today revealed that its platform for recording interactions within applications can now be accessed by artificial intelligence (AI) agents via a Model Context Protocol (MCP) server. Company CEO Greg Law said this Undo AI capability makes it simpler for any agent to discover the root cause of any issue that otherwise would have required […]
Microsoft Brings the Azure SDK for Rust to General Availability
Microsoft has moved the Azure SDK for Rust out of beta and into general availability, giving Rust developers a stable, production-ready way to connect to core Azure services. The release covers Core, Identity, Key Vault (Secrets, Keys, and Certificates), and Storage (Blobs and Queues), built around the same design patterns already used in the .NET, Java, JavaScript, Python, Go, and C++ SDKs.
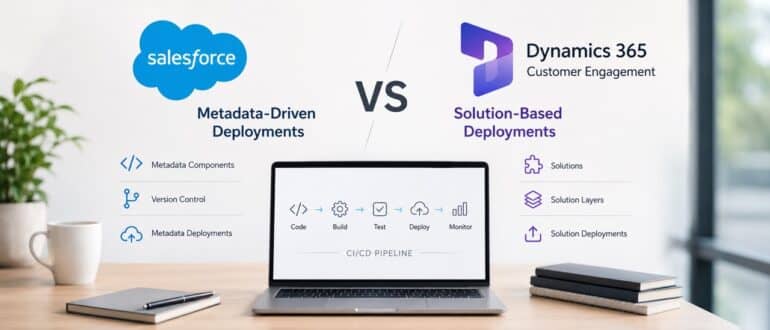
Salesforce vs Dynamics 365 CE DevOps: A Practical Comparison for Enterprise Teams
Most organizations running CRM platforms eventually face the same challenge: how to deploy changes safely, consistently, and quickly. While Salesforce and Dynamics 365 Customer Engagement (CE) support modern DevOps practices, they approach application lifecycle management differently. Understanding these differences can help teams design more effective deployment pipelines and avoid common release issues. As these platforms […]
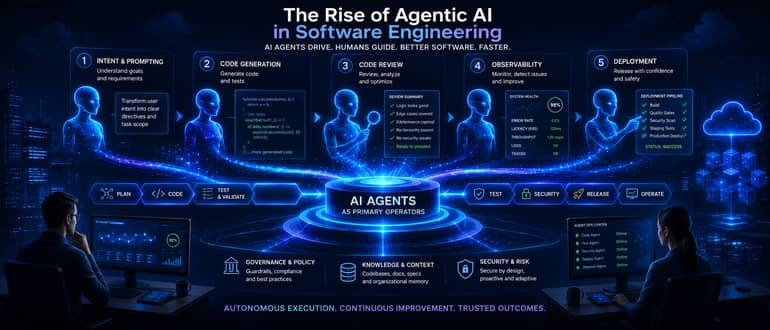
Newly Appointed CloudBees CEO Charts Agentic AI Engineering Course
The newly appointed CEO of CloudBees, Mo Plassnig, says that as the agentic artificial intelligence (AI) era dawns, the time has come to reinvent software engineering in a way that moves beyond human-centric tooling. Plassnig, who earlier this month succeeded Anuj Kapur, joins CloudBees from Immuta, a provider of a data security and governance platform, […]
CData Gives Developers Free Access to the Data Layer That IT Already Trusts
CData launches Connect AI Developer Edition, a free Python SDK, and CLI to give developers governed enterprise data access across Salesforce, Snowflake, and hundreds of other systems.
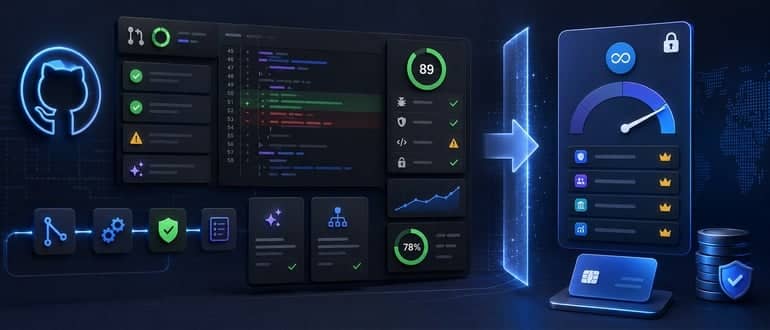
GitHub Code Quality Moves to General Availability, Bringing New Costs and Capabilities
GitHub is closing the book on the free preview period for one of its most widely adopted recent features. More than 10,000 enterprises used the GitHub Code Quality public preview to detect maintainability and reliability issues, enforce quality gates, and track code coverage. Starting July 20, 2026, that free ride ends. Code Quality becomes a […]
Homebrew to Packages: No ID, No Service
Homebrew, the unofficial but default package manager for many Apple Mac users, now has safeguards to prevent supply-chain attacks. The approach mimics how GitHub just fortified npm against attacks by establishing a set of trusted repositories to download from. “The Homebrew team is aware of the supply-side security issues with other package managers. We’ve taken […]
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
Why Every DevOps Engineer is Suddenly Learning MCP
Before they were everywhere, developers spent ages stitching systems together, one by one. APIs changed everything. MCP wants to do the same for AI.
The New Convergence: How Value Stream Mapping is Rewiring Product, Platform and DevOps for 2026 and Beyond
Value Stream Mapping (VSM) has re-emerged as the connective tissue that unifies product management, operations and architecture.
NVIDIA Research Bets on Code, Not Tool Calls, to Fix AI Spatial Reasoning
NVIDIA’s SpatialClaw uses code, not tool calls, to boost AI spatial reasoning by 11.2 points across 20 benchmarks and six model sizes.
Anthropic Brings Live, Shareable Artifacts to Claude Code
Anthropic adds live, shareable Artifacts to Claude Code, allowing teams to view AI coding sessions as real-time, interactive pages.
You Cannot Fake Flow: What Organizations Get Wrong About Value Delivery
Most organizations that have invested heavily in Agile and DevOps share a puzzling experience. Deployment frequency is up. Teams are busy. Dashboards are green. And yet value still queues. Strategy still takes months to reach the customer. Feedback still arrives too late to change anything important. Flow coach Marnus Marx has a name for this […]