

Five Great DevOps Job Opportunities
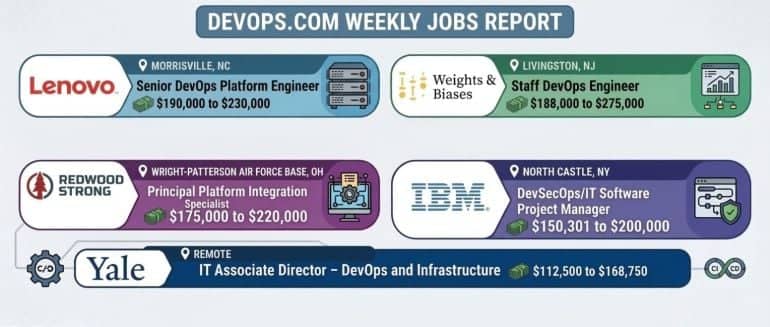
Latest DevOps Jobs report highlights opportunities at Lenovo, IBM, Yale and Weights & Measures. Find out more here.
On-Call Rotation Best Practices: Reducing Burnout and Improving Response
Practical SRE on‑call guide covering rotation models, alert hygiene, runbooks, metrics, compensation, shadowing, and automation to cut pager load and prevent engineer burnout.
Can QA Reignite its Purpose in the Agentic Code Generation Era?
AI-generated code is accelerating development but it exposes a deeper issue. Why deterministic infrastructure is becoming the foundation of agentic QA.
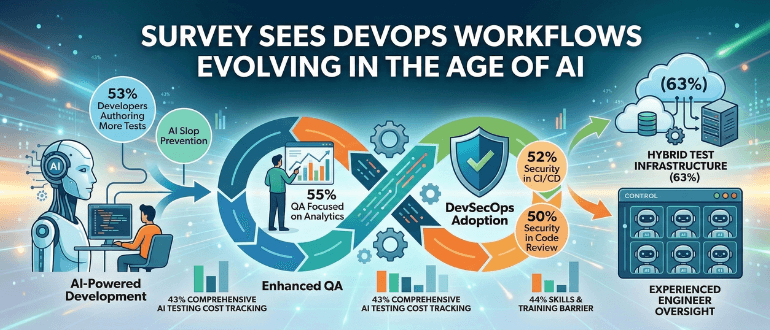
Survey Sees DevOps Workflows Evolving in the Age of AI
A global survey of 820 IT decision makers and DevOps practitioners finds that half of respondents (53%) report that developers in the age of artificial intelligence (AI) are now authoring more tests directly. Conducted by Perforce, that shift also appears to be enabling a similar percentage of organizations (55%) to provide quality assurance (QA) teams […]
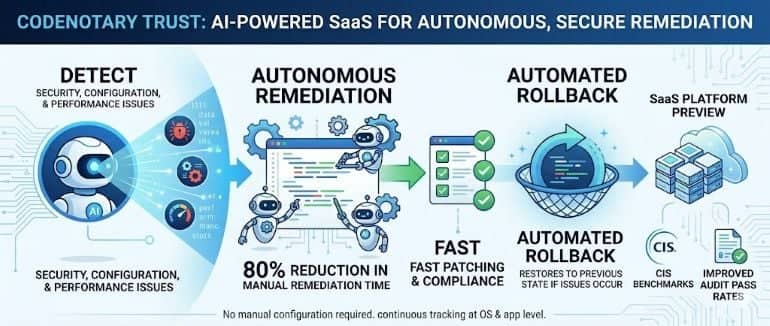
Codenotary Previews AI Platform to Autonomously Detect and Remediate IT Issues
Codenotary is previewing a software-as–a-service (SaaS) platform that enables artificial intelligence (AI) agents it has developed to autonomously detect, prioritize, and fix security, configuration, and performance issues. Company CEO Moshe Bar said the Codenotary Trust platform also enables continuous vulnerability tracking at both the Linux operating system and application level. Once an issue is detected, […]
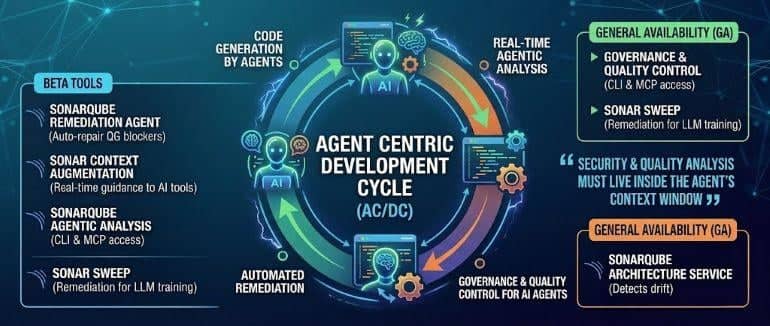
Sonar Unfurls Framework for Managing DevOps Workflows in the Age of AI
Sonar this week launched an Agent Centric Development Cycle (AC/DC) framework that promises to modernize continuous integration (CI) in the age of artificial intelligence (AI) coding. Announced at an online Sonar Summit, the AC/DC framework incorporates multiple tools and platforms the company has developed to better secure software supply chains, including now in beta Sonar […]
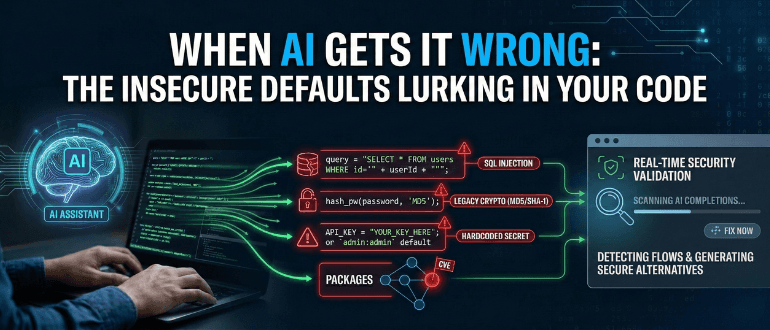
When AI Gets It Wrong: The Insecure Defaults Lurking in Your Code
The arrival of generative AI in the software development lifecycle (SDLC) is arguably the biggest shift in coding in decades. For development teams, tools like GitHub, Copilot, and other AI assistants act as a massive force multiplier, automating boilerplate, suggesting complex logic, and significantly accelerating time-to-commit. But as organizations rush to equip their teams, a […]
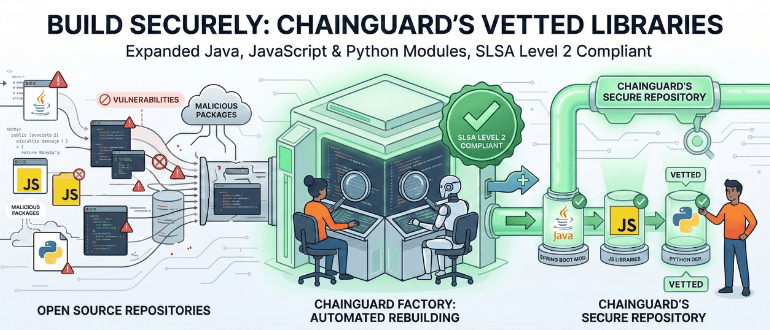
Chainguard Expands Repository to Add More Secure Open Source Libraries
Learn how Chainguard is strengthening software supply chains by expanding its secure repository of Java, JavaScript, and Python libraries, enabling DevOps teams to access components compliant with SLSA framework standards.
Unlocking Observability by Design With Inferred Schemas
Observability systems generate massive telemetry, but schema drift creates friction. Learn how inferred schemas and OpenTelemetry Weaver restore structure.
N. Korean Famous Chollima Hackers Use Malicious npm Packages to Steal Data
A group of more than two dozen malicious npm packages used to steal secrets and credentials from software developers has all the hallmarks – from infrastructure to operations – of Famous Chollima, the North Korean nation-state actor linked to the ongoing high-profile Contagious Interview scam. Threat researchers with Socket and Kieran Miyamoto of the DPRK […]
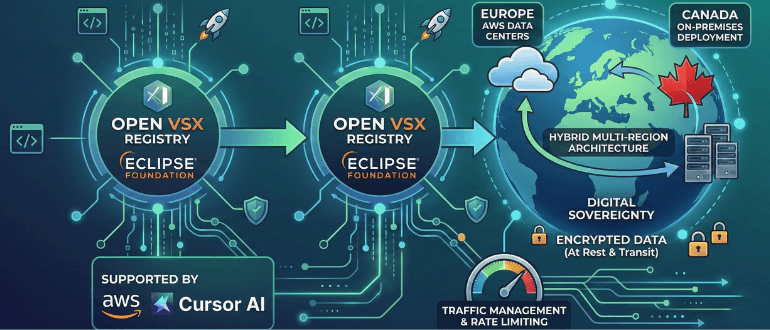
Eclipse Foundation Extends Scope and Reach of Open VSX Registry
The Eclipse Foundation launches a new framework for the Open VSX Registry, enhancing security features and transitioning to a hybrid architecture. With support from AI tool provider Cursor, this initiative aims to promote safer software supply chains.
Context Engineering is the Key to Unlocking AI Agents in DevOps
Explore how context engineering is essential for transforming AI agents from experimental prototypes to reliable production tools in DevOps. Understand its impact on automation workflows, accuracy, and scalability.
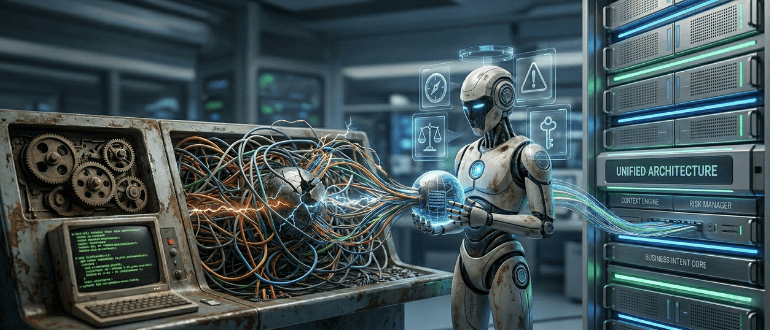
Why the Next Wave of Infrastructure Automation Requires a Different Kind of Intelligence
Every decade or so, something fundamental shifts in how we think about infrastructure. Not an upgrade, a rethinking. Virtualization changed what infrastructure was. The cloud changed where it lived. Infrastructure as Code changed how it was defined. Each of those shifts felt incremental from the inside and transformative in hindsight. We’re at one of those […]
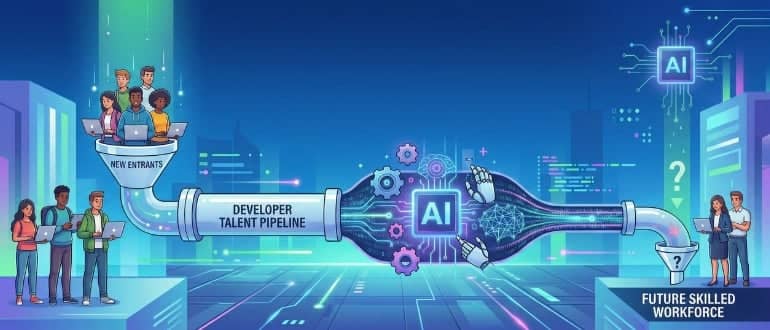
Microsoft Executives Warn AI Could Limit the Developer Talent Pipeline
Generative AI is transforming software development at remarkable speed. But in a new paper written by two Microsoft executives, Azure CTO Mark Russinovich and Scott Hanselman, VP of the developer community, argue that the AI technology also risks eroding the profession’s training pipeline. In their paper, Redefining the Software Engineering Profession for AI, published in […]
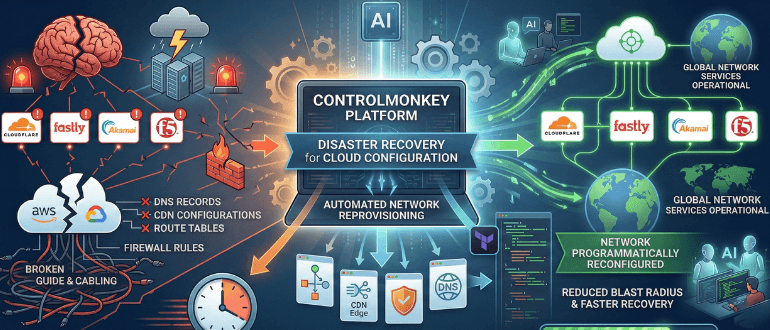
ControlMonkey Extends IaC Automation Reach to Restore Network Services
ControlMonkey has extended its platform for automating infrastructure-as-code (IaC) to add an ability to reprovision network services following a disruption in service. Company CEO Aharon Twizer said this extension to the Cloud Configuration Disaster Recovery platform, which the company launched last year, makes it possible to use Terraform code to programmatically reconfigure networking services among others […]
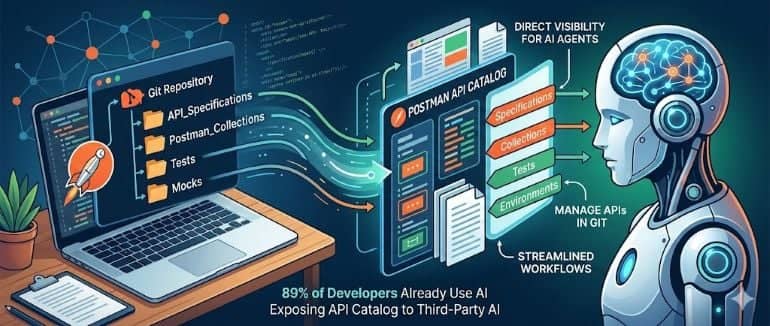
Postman Adds Ability to Invoke API Code From Within Git Workflows
Discover how Postman’s new feature allows software engineering teams to manage API specifications, collections, and environments directly from Git repositories, simplifying workflows for AI agents in the development process.
Google ADK Opens the Door to AI Agents That Work Inside Your DevOps Toolchain
Google ADK adds integrations for GitHub, GitLab, Jira, MongoDB, and seven observability tools. AI agents can now work inside your DevOps toolchain.
Five Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
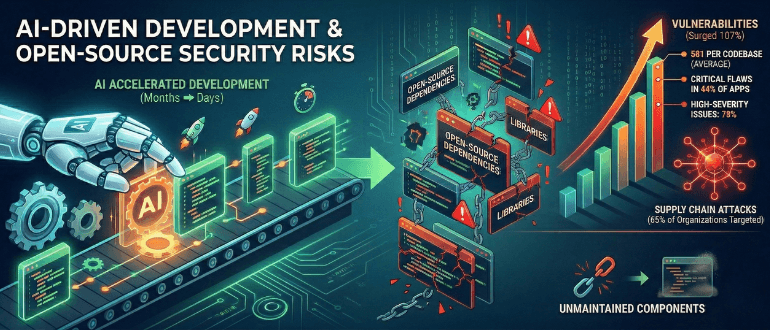
AI-Fueled Development Pushes Open-Source Risk to Extremes: Report
Artificial intelligence has shortened the timeline for software development from months to days. But according to new research, that acceleration is creating significant risks for security and compliance issues. Black Duck’s 2026 Open Source Security and Risk Analysis (OSSRA), based on audits of 947 commercial codebases spanning 17 industries, shows that vulnerabilities inside enterprise applications […]
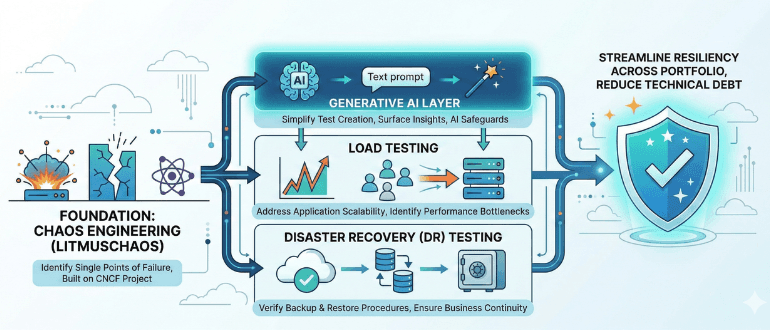
Harness Readies Resilience Testing Platform to Make Applications More Robust
Harness today revealed that it will make available a set of open source tools for testing the resiliency of applications that are based on a chaos engineering platform the company gained with the acquisition of LitmusChaos. The Harness Resilience Testing platform extends the scope of the tests provided to include application load and disaster recovery […]
I Learned Traffic Optimization Before I Learned Cloud Computing. It Turns Out the Lessons Were the Same.
I wanted to be a race car driver before I knew what a data center was. I started in traffic, not in the cloud. This was not a childhood dream driven by glamour. It was more practical than that. I grew up in India, and I was always late for school. Not entirely my fault. […]
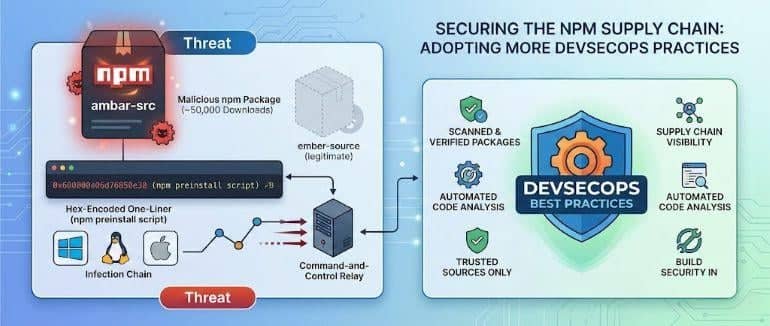
Malicious NPM Package Gets Downloaded 50K Times Before Discovery
A malicious package downloaded approximately 50,000 times from a node package manager (npm) is providing an object lesson for adopting more DevSecOps best practices. Security researchers from Tenable discovered a “ambar-src” package that was first published Feb. 13 and then updated again before being discovered. It is aimed at developers building JavaScript applications on Windows, […]
Security Flaws in Anthropic’s Claude Code Risk Stolen Data, System Takeover
Three critical vulnerabilities found in Anthropic’s Claude Code agentic AI developer tool could be exploited simply by cloning and opening an untrusted project and lead to system takeover, stolen API keys, and credential theft, according to security researchers with Check Point. The security flaws, which Anthropic fixed last year and last month after the researchers […]