

Open Source Code Just as Secure as Proprietary Software—If You Manage It Right, Says CISA
Open source can be just as safe as proprietary software, though government agencies (and private enterprises) should take additional measures to secure it properly, according to a new guide published by the U.S. Cybersecurity and Infrastructure Security Agency (CISA). The report, “Open Source Software: Security Principles and Practices,” provides with guidance to help agencies comply […]
Why Log Monitoring Is the Missing Link in Most Incident Response Workflows
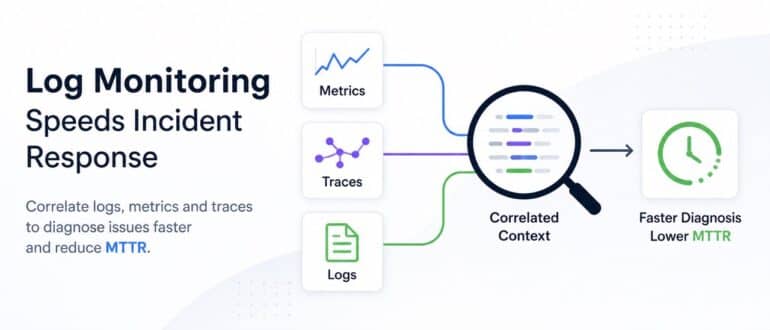
Modern engineering teams have invested heavily in observability. Dashboards are populated, alerts are configured, on-call rotations are set. Yet when production incidents occur, the average time to resolution hasn’t dropped nearly as fast as the tooling has improved. The reason, in many cases, comes down to one overlooked gap: logs aren’t being used the way […]
CISA’s 2026 SBOM Guidance Adds Hash Requirements and AI Coverage
CISA’s updated 2026 SBOM minimum elements expand software transparency requirements to AI, SaaS and open source while adding hashes, licenses and stronger validation.
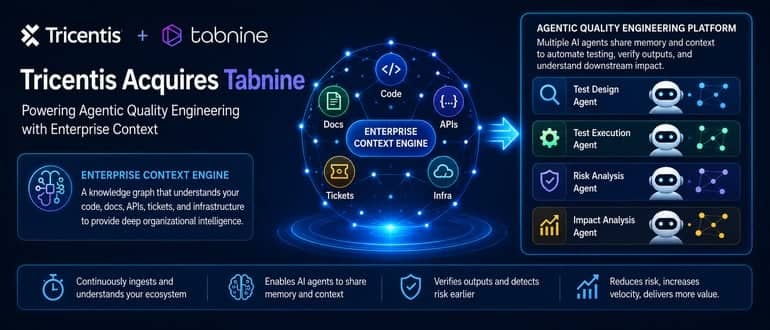
Tricentis Acquires Tabnine to Gain Knowledge Graph for AI Testing Agents
Tricentis today revealed it is acquiring Tabnine to gain access to a knowledge graph that will be used to provide context to AI agents that have been trained to automate a range of testing tasks. Once the acquisition is complete, Tricentis plans to integrate the knowledge graph developed by Tabnine, dubbed the Enterprise Context Engine, […]
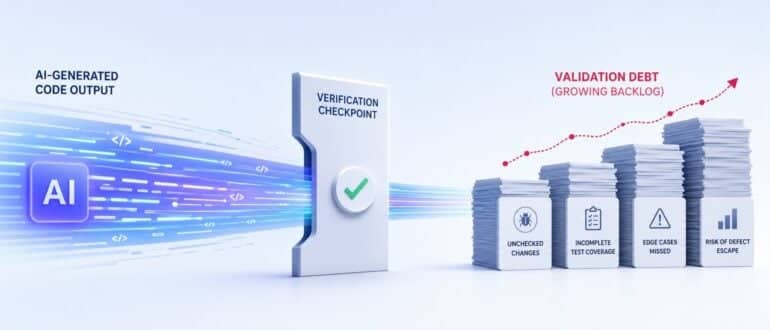
Validation Debt That Your Dashboards Are Not Showing
The gap between how fast AI writes code and how reliably teams verify it is quietly becoming a balance-sheet risk. Enterprise leaders are learning to measure it before it forces repayment. Every engineering organization that adopted AI coding assistants over the past two years has quietly taken on a liability that never appears on the […]
The Surprisingly High Cost of ‘Free’ Search Solutions
Not long ago, some business leaders seemed to view enterprise search as a “nice-to-have.” Or, at the very least, they considered it more of a supporting utility than a strategic, business-critical platform. Organizations use enterprise search tools to help employees locate internal documents and enable support teams to surface relevant information. And, of course, retailers […]
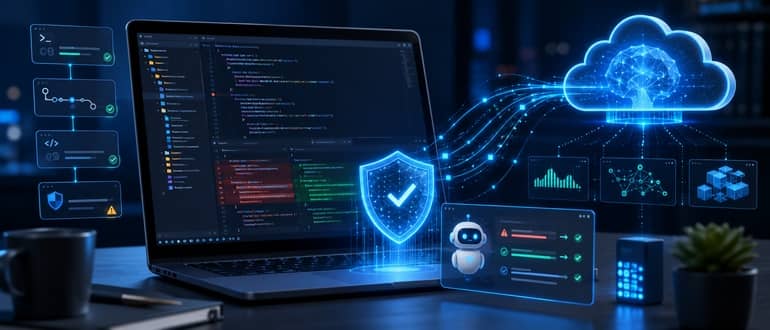
OpenAI Open Sources Codex Security CLI for the Merge Path
OpenAI has released its Codex Security command-line interface and software development kit as open source software under the Apache 2.0 license, providing a new way to bring its AI security scanner into development workflows. The CLI can scan repositories, review staged and unstaged changes before a commit, compare findings across scans and export results for […]
DevOps Is Drowning in Updates—and Engineering Is Paying the Price
DevOps used to be a manageable rhythm: several core tools, a handful of respected blogs, and a few incident write-ups that made everyone slightly uncomfortable in a useful way. Now it feels like a firehose aimed directly at the on-call rotation. DevOps teams now have more information than they can reasonably track. Critical updates are […]
The Anatomy of a $900,000 Validation Bill
A 50-developer team shipping at an agentic pace will spend roughly $900,000 this year on AI and developer tooling costs. Most of the engineering leaders I’ve talked to saw the compute costs coming. What they didn’t anticipate was where the rest of the bill was hiding. The culprit is a timing problem. Frontier models price […]
The Innovation Puzzle 2.0: Connecting Vision and Value
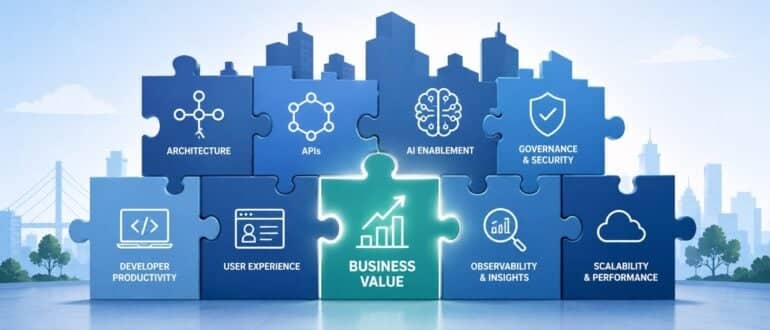
The tech landscape constantly evolves, making it tempting to chase every new trend. Ironically, in today’s business world, the word “innovation” has become almost synonymous with technology adoption. Yet after years of leading digital transformations, I’ve learned that sustainable innovation isn’t about having the latest technology—it’s about solving business problems and delivering measurable impact. In […]
Investments in DevOps Tools and Platforms Start to Accelerate in AI Era
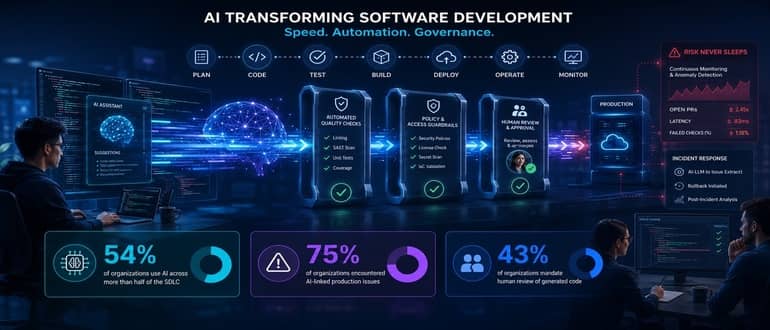
A global survey of 839 IT decision-makers conducted by the Futurum Group finds 54% now work for organizations that use AI across more than half of their software development lifecycle (SDLC), with 40% reporting AI already generates the majority of production code merged in the last 90 days. Within the next three years, a total […]
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
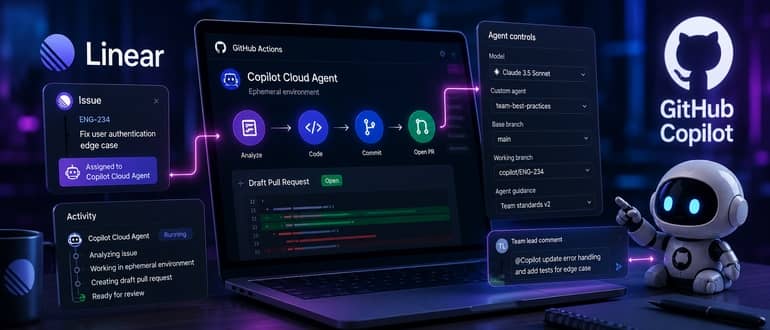
GitHub Gives Teams More Control Over Copilot’s Cloud Agent in Linear
GitHub’s Copilot cloud agent integration with Linear is now generally available, adding model, branch and team-level controls for delegated coding work.
GitHub and PyPI Bet On Time to Slow Down Software Supply Chain Attacks
GitHub and PyPI are using time as a security control, delaying dependency updates and locking older releases against new file uploads.
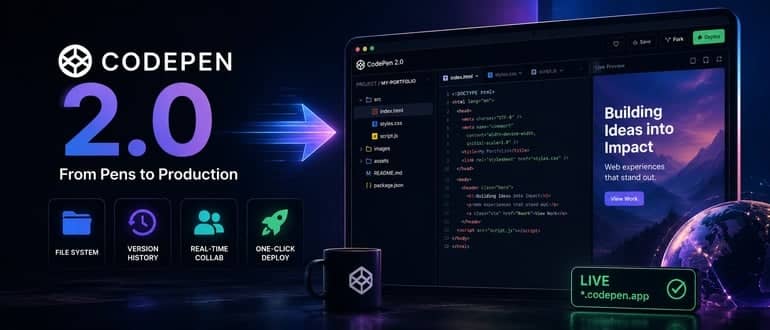
CodePen 2.0 Turns a Design Playground Into a Real Deployment Tool
CodePen 2.0 transforms the front-end playground into a file-based development platform with collaboration, version history and one-click deployment.
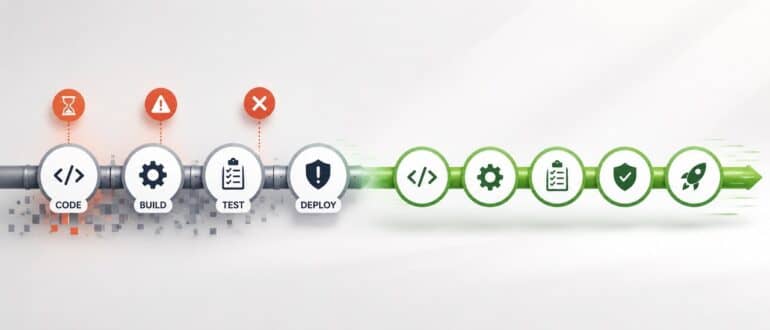
These are 10 CI/CD Pipeline Mistakes That Slow Down Engineering Teams
Continuous software delivery in the digital age has come to depend on CI/CD pipelines. They enable engineering teams to rapidly develop, test, and deploy code while keeping it highly usable and consistent across environments. CI/CD pipelines, however, can themselves become a source of friction as systems start at a small scale and become more complex. […]
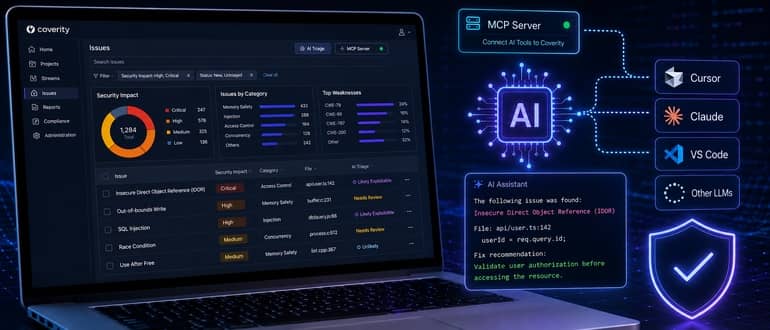
Black Duck Extends Scope and Reach of Code Scanning Tool
Black Duck has updated its Coverity static analysis code scanning tool to provide deeper integrations with artificial intelligence (AI) tools along with updates to its user interface that make it simpler to prioritize issues in a way that makes it easier to adhere to multiple compliance mandates. A Model Context Protocol (MCP) server added to […]
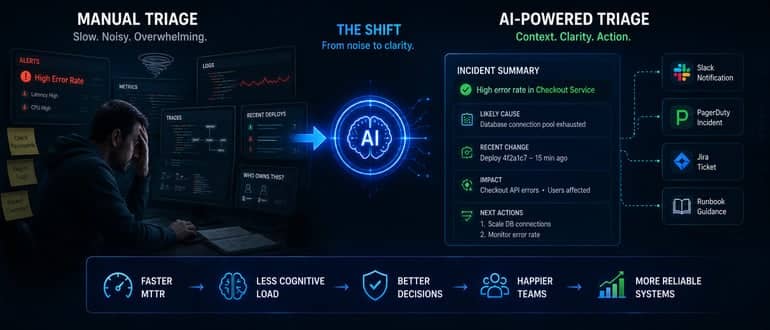
The End of Manual Triage
Why SRE teams are replacing manual incident triage with AI-assisted correlation, stronger observability and controlled agentic workflows.
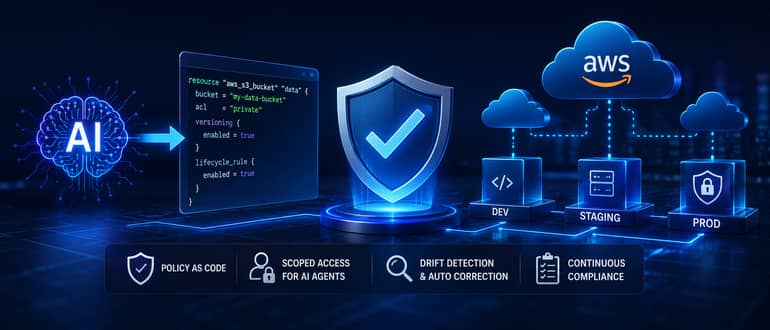
AI Agents Are Writing Your Infrastructure Code. Is Anyone Governing It?
AI agents now generate infrastructure code at scale, but security pass rates are stuck at 55%. Here’s how teams can close the governance gap.
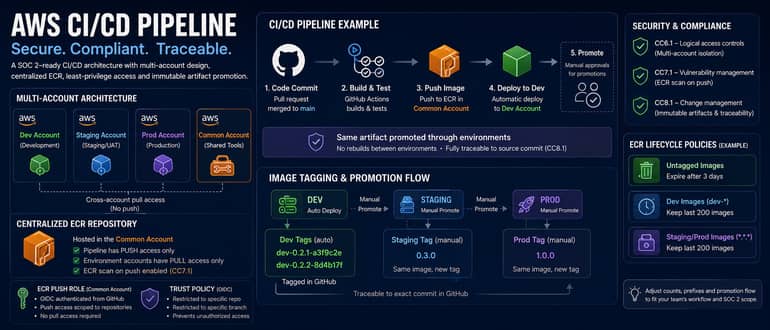
Building SOC 2 Compliant CI/CD Pipelines on AWS with GitHub Actions
How to design a secure, traceable AWS CI/CD pipeline using separate accounts, centralized ECR, OIDC and immutable image promotion for SOC 2.
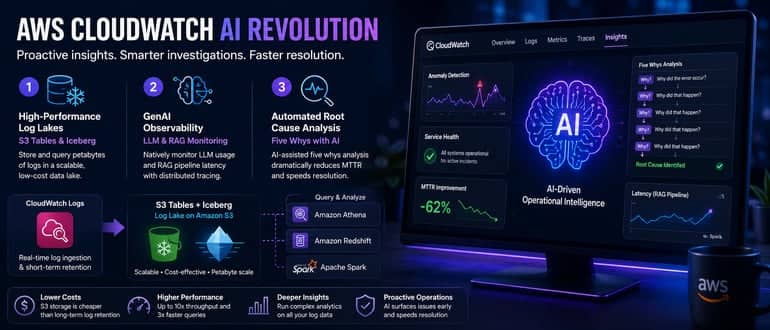
From Reactive Monitoring to AI-Driven Operational Intelligence
Traditional monitoring often meant chasing alerts and toggling between dashboards after an issue had already impacted users. AWS CloudWatch — long the backbone of metrics, logs and traces on AWS — is evolving past that reactive paradigm. The latest CloudWatch capabilities infuse AI-driven operational intelligence into observability, helping engineers surface issues before they escalate and […]
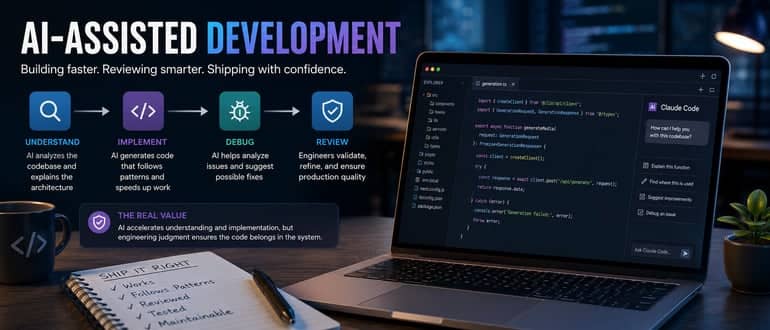
AI-Assisted Development Under Deadline: What It Takes to Ship Production Code on an Unfamiliar Stack
How Claude Code accelerated development on an unfamiliar stack while proving that production-ready AI-generated code still requires human judgment.
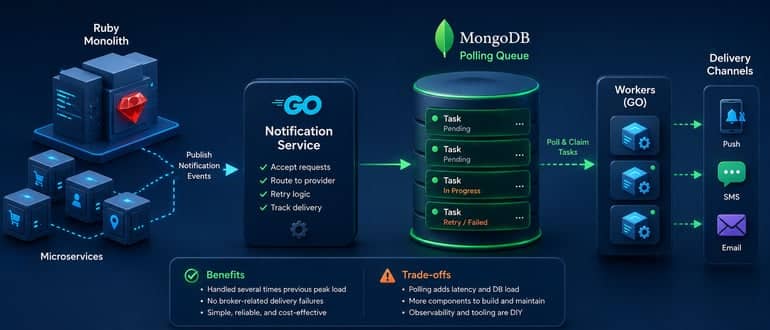
When the Message Broker Becomes the Bottleneck: Scaling Push and SMS With MongoDB Polling
A back-end team extracted notification delivery from a large Ruby monolith into a centralized Go service, only to discover that their shared RabbitMQ cluster could not reliably support the new workload. Here’s how they solved the problem using MongoDB as a polling queue and the trade-offs that came with it. The Scaling Problem Inside the […]