

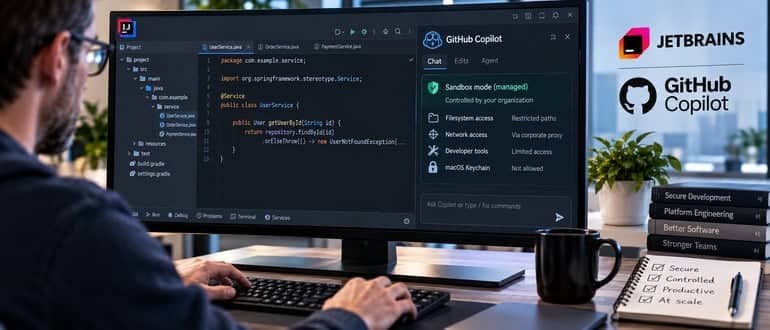
GitHub Puts Guardrails on Copilot’s Sandbox Inside JetBrains IDEs
JetBrains IDEs are where a lot of enterprise backend work happens — Java, Kotlin, Spring, big monorepos with a lot to break. So when an AI coding agent starts running shell commands inside that environment, the question isn’t whether it’s useful. It’s what happens if it touches the wrong file, the wrong network path, or […]
Rust’s First Debugging Survey Shows Most Developers Skip the Debugger Entirely
Most Rust developers don’t use a debugger. That’s the headline finding from the Rust compiler team’s first dedicated debugging survey, and it’s worth sitting with for a second. Rust has spent years building a reputation as the language that catches your mistakes before you ship them. The compiler is famously strict. The type system is […]
AI Has Turned Verification Into the New DevOps Bottleneck
The next DevOps challenge is not generating more software. It is proving, quickly and repeatedly, that a growing volume of machine-generated change is fit to ship.
GitHub Quietly Fixes One of Dependabot’s Oldest Headaches
GitHub Dependabot can now authenticate to GitHub-hosted package registries without personal access tokens, reducing credential management and supply chain security risk.
EU-Funded CodeSupply Offers Grants for Open Source Software Supply Chain R&D
Software supply chain, security and compliance tools all depend on accurate information about the packages they analyze, but that data is often fragmented across multiple sources and can be difficult to access or use consistently. A new European Union-funded initiative called CodeSupply, coordinated by the NLnet Foundation, is making €400,000 in grants available for open […]
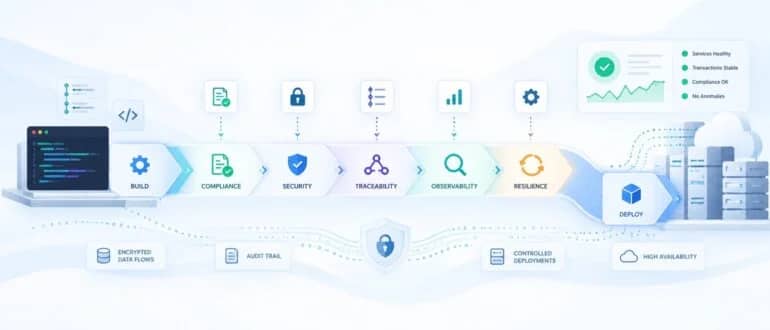
DevOps in Financial Services: Moving Fast Without Losing Control
DevOps is often associated with speed: shorter release cycles, greater automation, faster feedback and increased developer autonomy. In financial services, however, speed is only one part of the equation. A platform supporting banking, payments or other regulated financial workloads also has to account for security, traceability, resilience, access control and operational risk. A deployment that […]
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
Apica Adds AI Agents and MCP Server to Platform for Managing Telemetry Data
Apica today added an artificial intelligence (AI) agent and Model Context Protocol (MCP) server to version 3.0 of its Ascent platform for managing telemetry data pipelines. Andi Mann, chief product and technology officer for Apica, said the AI agent, dubbed Venn, makes it possible for IT teams to use natural language rather than having to […]
GitHub’s New Copilot Feature Takes the Guesswork Out of Picking AI Models
GitHub’s Project HydraFusion brings multi-model orchestration to Copilot, automatically routing coding tasks across AI models to balance quality, cost and complexity.
Your DevOps Pipeline Is Already a Sustainability Program
During my doctoral research on modern engineering practices and operational efficiency, one pattern kept surfacing that I did not expect to find. The engineering teams making the most measurable progress on sustainability were not the ones that had appointed green committees. They were the ones running tight DevOps discipline: right-sized fleets, lean pipelines, tuned alerting, […]
Observability’s Gaslighting Problem: “Send Less Data” Isn’t a Strategy
A familiar pattern is emerging in observability conversations. As telemetry volumes grow and costs rise, the default recommendation is often to collect less data: Sample more, retain less, index selectively, filter earlier, and reduce cardinality until the economics become manageable. Some of this is reasonable. No system benefits from unlimited accumulation without curation. But when […]
Observability 2.0: Why DevOps Teams Are Moving From Monitoring to Intelligent System Understanding
For a long time, monitoring just meant staring at dashboards and waiting for something to flash red. Engineers tracked things like CPU usage, memory, response times, error rates, and uptime. If a number crossed a certain line, you’d get an alert. Then, someone dived in to figure out what was wrong. That basic approach isn’t […]
From the Horse’s Mouth: Anthropic Says AI Has Changed the SDLC
Anthropic’s AI-native SDLC playbook argues that faster coding is shifting the bottleneck to planning, testing, governance, deployment and operations.
JFrog CEO: No One Cares About Source Code Anymore
JFrog CEO Shlomi Ben Haim told approximately 500 software engineers today that in the age of artificial intelligence (AI) no one will soon care much about source code anymore. Speaking at the company’s swampUP 2026 conference, Ben Haim said AI tools are now creating executable binaries directly without relying on source code that historically existed […]
GitOps in 2026: Why Pull Requests Are Taking Over Cloud Operations
For years, cloud infrastructure changes were mostly a mystery. An engineer would log into a dashboard, tweak a setting, run a few scripts, and that was it. Nobody worried until something broke. Suddenly, everyone wanted answers. Who changed this? Was it tested? Can we fix it? How did production end up out of sync with […]
CrowdStrike Moves to Secure Software Supply Chains at the Endpoint
CrowdStrike today at its Fal.con 2026 conference extended its reach into the realm of software supply chain security with the addition of an offering that blocks malicious open-source packages at the endpoint before their embedded code can run. Bartley Richardson, chief AI and autonomous systems officer for CrowdStrike, said Real-Time Supply Chain Attack Protection is […]
JFrog Moves to Secure Agentic Engineering Workflows
JFrog today at its swampUP 2026 conference added a zero touch remediation capability that ensures the most secure version of a binary is provided even when application developers request a version that has known vulnerabilities. Additionally, JFrog is adding tools and capabilities to secure artificial intelligence (AI) agents that have been embedded within a DevOps […]
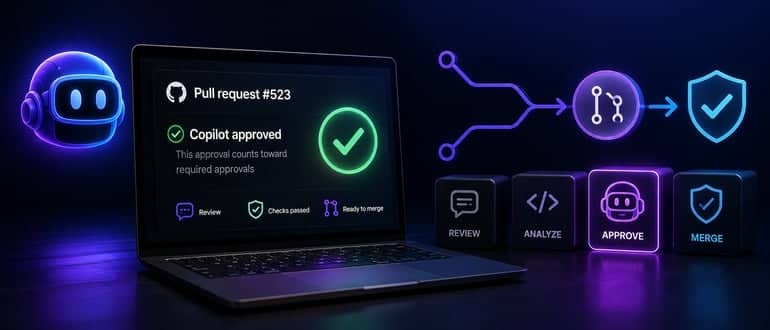
GitHub Puts Copilot in the Approval Seat for Pull Requests
GitHub Copilot can now submit binding pull request approvals, moving AI code review from advisory feedback into the merge decision itself.
Informing Stakeholders Isn’t the Same as Aligning Them
The first sign of trouble was a screenshot. We’d just switched on the A/B test via our feature management platform. Within the hour, a senior stakeholder landed in the variant feature flag, opened the app on their own phone, and sent us an image of it. The message, more or less: “Why is there a […]
Debian’s AI Vote Bets on Accountability Instead of a Ban
Debian’s new AI contribution policy avoids bans and mandatory disclosure, instead making developers responsible for reviewing AI-generated work and protecting sensitive data.
From Operator to Agent Manager: The Real Shift in Network Engineering
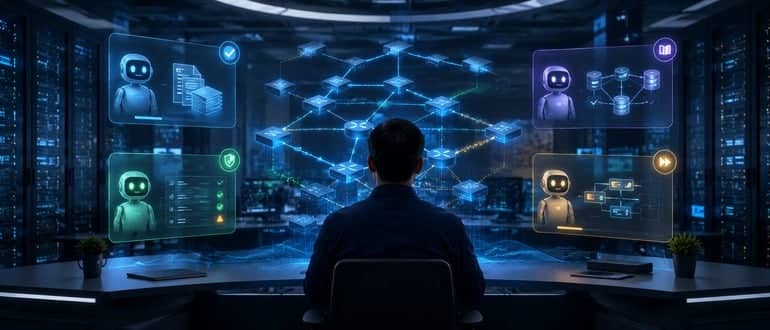
I’ve been saying for ten years that network automation was three years away from being the only way to do things. Every year I moved the goalposts, because the data never caught up to the rhetoric. After a decade of scripts, YAML, Ansible, Terraform, and every NetDevOps framework we could throw at the problem, roughly […]
Ten Great DevOps Job Opportunities
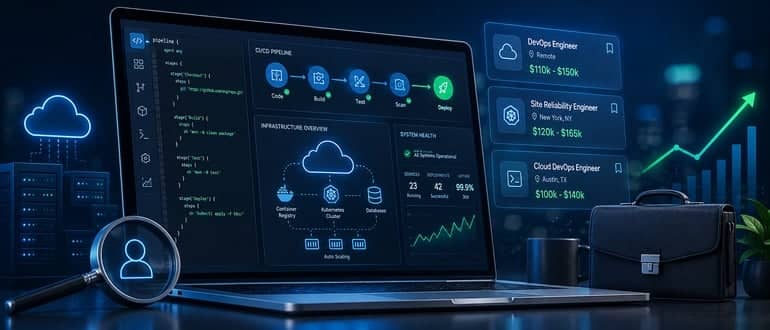
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
Broadcom Launches Trusted Artifact Service for Spring Framework
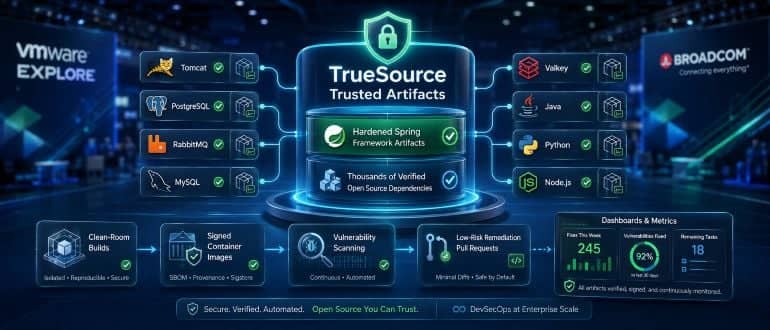
Broadcom launches TrueSource Trusted Artifacts to provide hardened Spring dependencies, secure open source packages and automated vulnerability remediation.