

When AI Coding Agents Become Malware Delivery Systems
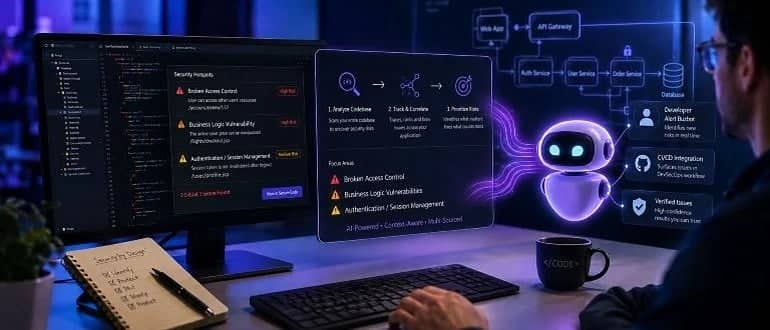
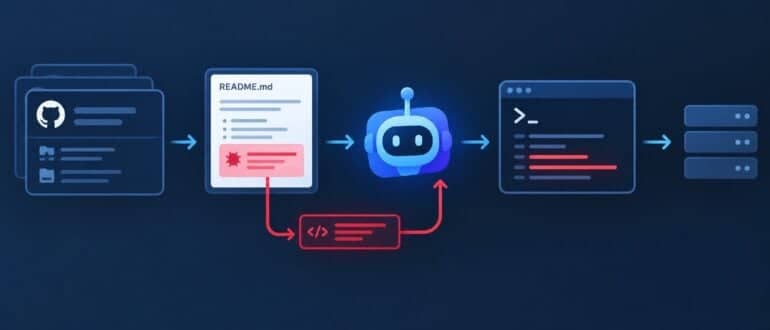
AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools. An agent can search GitHub, read project documentation, and run commands without the developer having to work through every step manually. That convenience is creating another security concern for […]
Harness Unfurls Source Code Repository Alternative to GitHub
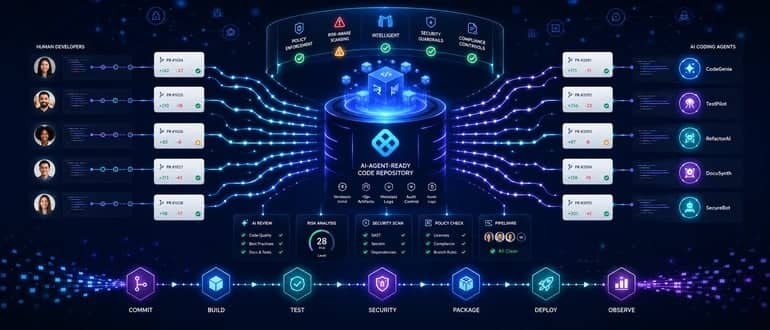
Harness today launched a code repository service that is specifically designed for DevOps teams that are relying on artificial intelligence (AI) agents to generate code. Martin Reynolds, Field CTO for Harness, said the Agent-Ready Harness Code Repository and AI Code Review service provides an alternative to existing GitHub source code repositories that were not designed […]
How to Build a Durable Change-Control Gate for AI Agents
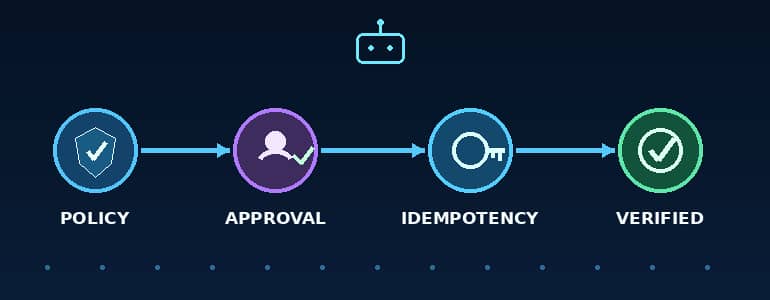
AI agents that trigger real-world changes need more than confidence scores. A durable change-control gate should recheck policy, require approval for consequential actions, enforce idempotency and verify the result before retrying.
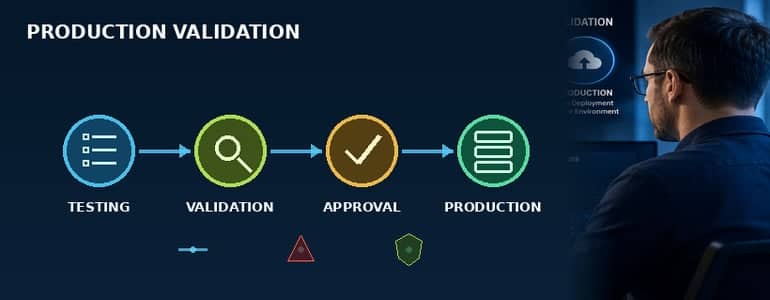
Production Validation: The Missing Layer in Enterprise Releases
Production validation adds a critical business-control layer between testing and deployment, combining data checks, exception review, approvals, reconciliation and operational readiness before a release reaches production.
Tricentis Preps Wave of Additional AI Testing Capabilities
Tricentis is providing early access to multiple artificial intelligence (AI) capabilities that it is gearing up to roll out later this year via a Tricentis Transform initiative, including an autonomous AI agent, dubbed Aida, that explores web and Windows desktop applications to surface defects, weaknesses and other potential gaps without requiring DevSecOps teams to create […]
The Missing Runtime for Long-Running AI Agents
Enterprise AI agents need more than stronger models. They need durable execution environments that can coordinate multi-step workflows, survive failures, pause for human review and resume reliably after disconnects or delays. AI Agents Have Moved Beyond Chat Demos AI agents work beautifully in demos. A user asks a question, a large language model generates a […]
Automated Diagnosis Isn’t Automated Understanding: What Postmortems Teach Us About Building Trustworthy Incident AI
AI incident tools can reduce alert noise, but real root-cause diagnosis requires causal reasoning, live dependency context, uncertainty handling and strong postmortem data.
AI Can Generate Your Infrastructure. Can Your CI/CD Pipeline Trust It?
AI-generated infrastructure code is exposing a growing security gap, pushing platform teams to add stronger automated gates, provenance tracking and human review before Terraform, Kubernetes and CI/CD changes reach production.
Your AI Coding Budget Is Becoming a Variable Cloud Bill
AI coding assistants are becoming a variable, usage-based engineering cost, forcing platform and DevOps teams to apply FinOps practices to models, credits, utilization and multi-vendor spend.
Is Java Enterprise Ready for AI? Absolutely
AI is transforming software engineering. For enterprise Java developers, the key question is whether Java and Jakarta EE are prepared to integrate AI into enterprise applications. The answer is yes. Java and Jakarta EE already support integration of Large Language Models (LLMs) and AI capabilities through existing APIs, libraries, and frameworks. Developers can continue using […]
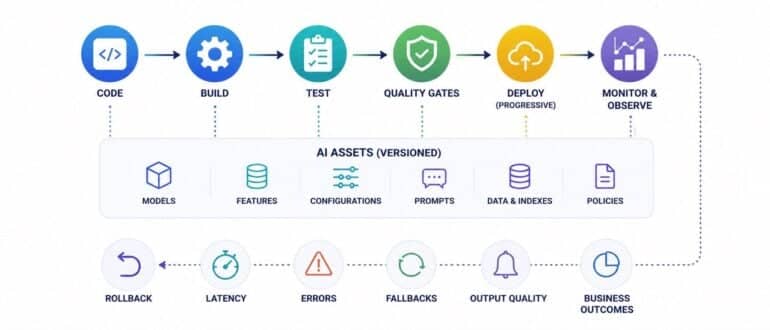
CI/CD for AI-Enabled Applications: Why Traditional Deployment Pipelines Need to Evolve
Traditional CI/CD pipelines are optimized around a familiar assumption: source code changes, automated tests validate the change, a build artifact is produced, and the application is promoted through environments. AI-enabled applications complicate that model because production behavior can change even when application code does not. A new model version, feature transformation, prompt configuration, retrieval index […]
The Blind Spot Between Back‐End Metrics and User Experience
Engineering teams often face a frustrating scenario when application performance monitoring (APM) shows perfect Apdex scores and negligible error rates, yet user retention drops due to poor front‐end performance. The solution requires bridging the gap between healthy back‐end metrics and the actual experience delivered in the browser. Teams that have built back‐end observability without instrumenting […]
Why DNS, DHCP, and IPAM Can No Longer Live in Separate Silos
Ask a network engineer where their DNS records live, and the answer is rarely straightforward. Some zones reside on Windows DNS servers, others are hosted in cloud-managed services, while DHCP scopes are spread across regional data centers, branch offices, and virtual networks. Meanwhile, IP address visibility is frequently fragmented across different management platforms, making routine […]
The AI Agent Race Is On. But Are We Watching the Right Race?
Claude Code, OpenAI Codex, GitHub Copilot, Cursor and a growing field of challengers are competing to define the future of software development. A new Techstrong special report examines who is ahead, how the race should be measured and what enterprises need to consider before placing their bets. Which AI coding agent is winning? It sounds […]
Report Shines Spotlight on 91 Vulnerabilities Fixed in Latest Update to Spring Framework
Sonatype says 91 Spring vulnerabilities affecting more than 209,000 software components highlight how AI is accelerating vulnerability discovery and creating a new patching challenge for DevSecOps teams.
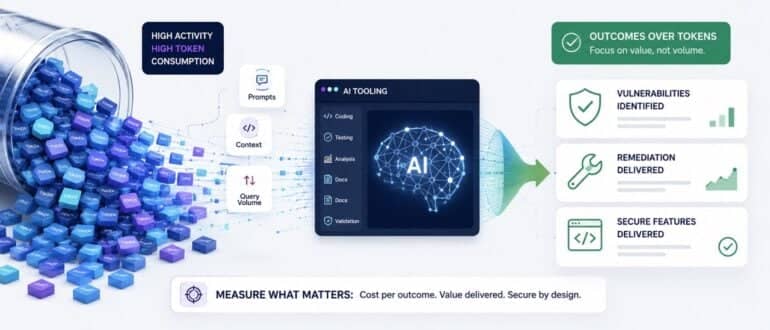
Why “Tokenmaxxing” Was Always the Wrong Way for Developers to Measure AI Productivity
The term “tokenmaxxing” left the developer lexicon just as quickly as it arrived, and like most viral technology concepts, it means different things depending on who’s using it. In practice, the term is being applied in two ways: maximizing total token consumption as a proxy for AI adoption and effort, or optimizing output per token […]
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
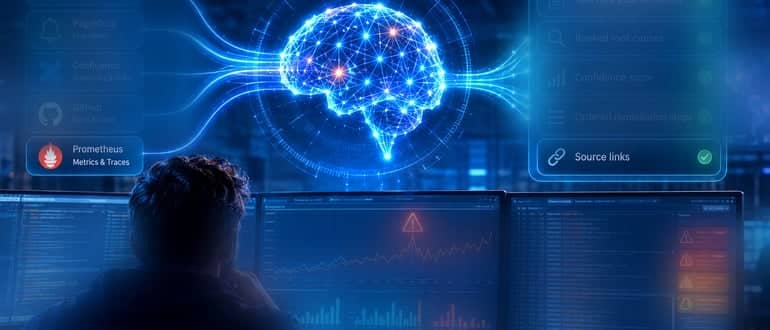
Beyond Log Search: What We Learned Building a RAG-Based Incident Diagnosis System
A RAG-based AIOps framework can cut incident diagnosis time by grounding LLM reasoning in real runbooks, tickets and postmortems, improving root-cause accuracy while giving SREs source-backed answers they can trust
Scalable Jenkins Management: Empowering Enterprises With Centralized Control for 150+ Instances
A centralized Jenkins control plane can reduce fleet sprawl, automate upgrades and backups, improve observability, and give application teams safe self-service across large multi-cloud CI/CD estates.
Preparing Infrastructure for the Next Phase of Agentic AI
Agentic AI is changing government infrastructure requirements, pushing agencies to rethink workflows, observability, data movement and resource prioritization before investing in new hardware.
Transforming Mainframe Recovery
Moving beyond disaster recovery, organizations can ensure business-critical mainframe environments. Over decades, the mainframe has earned a reputation for being synonymous with reliability. Many enterprise organizations continue to rely on the mainframe precisely because of the redundancy, automatic recovery, and availability that leads to “nine nines” reliability or 31.56 milliseconds of unplanned annual downtime per […]
Dash0 Acquires Polar Signals for Continuous Profiling and GPU Visibility
Observability startup Dash0 announced this week that it acquired Berlin-based continuous profiling specialist Polar Signals. The deal adds continuous profiling to SignalStore, Dash0’s OpenTelemetry-native data platform. Continuous profiling has been part of the developer toolbox for years and provides teams with an ongoing view of where running applications spend CPU time, allocate memory and consume […]
Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
Security researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more attacker-owned crates. In addition, researchers with Wiz wrote that there also appears to be overlap with supply chain campaigns run by nation-state actors […]