

Anthropic Adds a Coordinator to Claude Projects for Running AI Work in Parallel
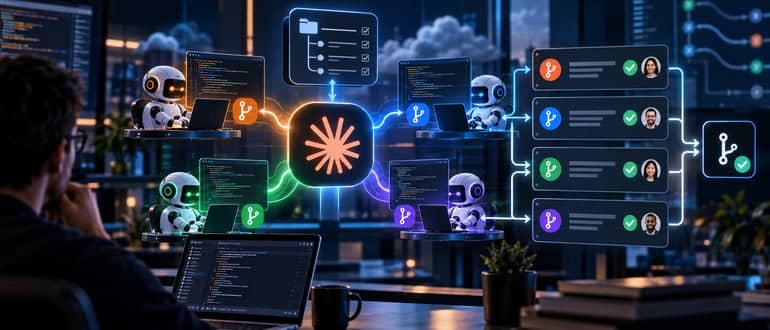
Anthropic’s redesigned Claude Projects coordinates parallel Claude Code sessions, delegates work across branches and brings the results back through familiar pull-request review workflows.
GitHub’s August Outages Show Growth Is Outpacing Infrastructure
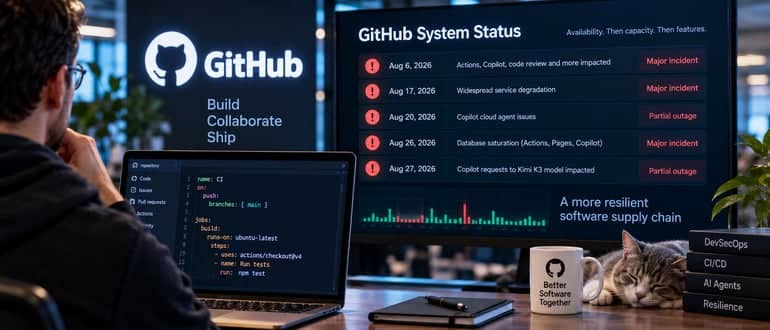
GitHub’s August 2026 report details five outages tied to Actions and Copilot growth outpacing infrastructure. Here’s what platform teams should know.
Flaw in DeepSeek Harness AI Coding Tool Let Agents Disable Their Sandbox
News of the now-fixed vulnerability comes amid growing concerns that AI vendors do not in have complete control of their autonomous agents.
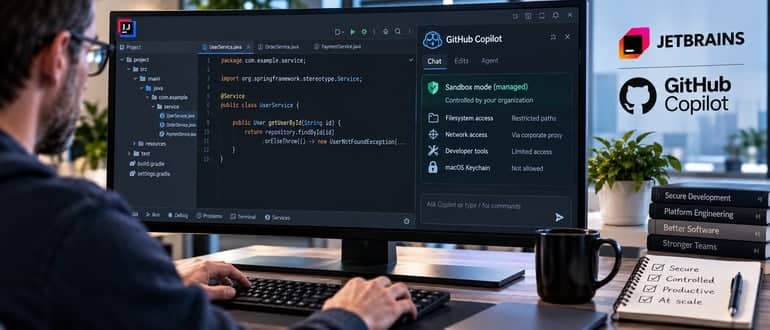
GitHub Puts Guardrails on Copilot’s Sandbox Inside JetBrains IDEs
JetBrains IDEs are where a lot of enterprise backend work happens — Java, Kotlin, Spring, big monorepos with a lot to break. So when an AI coding agent starts running shell commands inside that environment, the question isn’t whether it’s useful. It’s what happens if it touches the wrong file, the wrong network path, or […]
From the Horse’s Mouth: Anthropic Says AI Has Changed the SDLC
Anthropic’s AI-native SDLC playbook argues that faster coding is shifting the bottleneck to planning, testing, governance, deployment and operations.
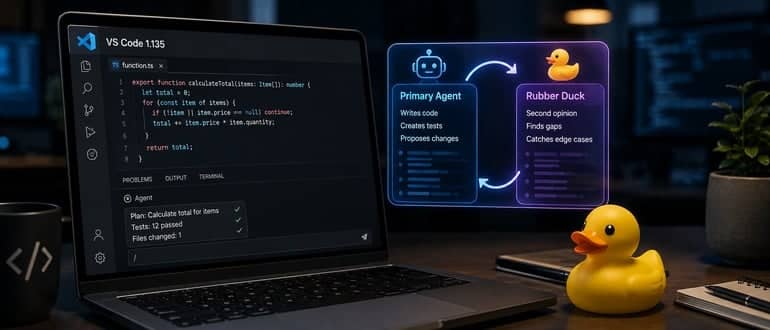
VS Code 1.135 Gives AI Coding Agents a Second Opinion
VS Code 1.135 adds Rubber Duck AI review, persistent agent sessions, Agent Host infrastructure and clearer token usage as Microsoft builds a more agentic IDE.
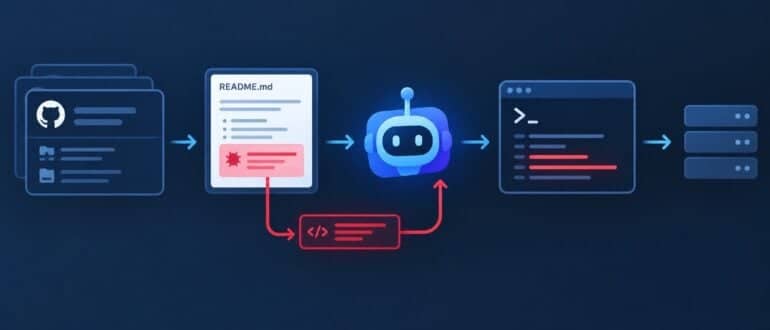
When AI Coding Agents Become Malware Delivery Systems
AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools. An agent can search GitHub, read project documentation, and run commands without the developer having to work through every step manually. That convenience is creating another security concern for […]
Claude Code’s Temporary Usage Boost Expires Tonight. Here’s What Actually Changes
Anthropic’s temporary 50% increase to Claude Code weekly usage limits expires August 19, reducing available capacity for developers and DevOps teams without lowering subscription prices.
The Agent Proposes, the Pipeline Disposes: Controls for AI-Authored Change
When agents write code and open pull requests faster than humans can read them, ‘the diff looked fine’ stops being a control. The durable controls live outside the agent’s reasoning loop.
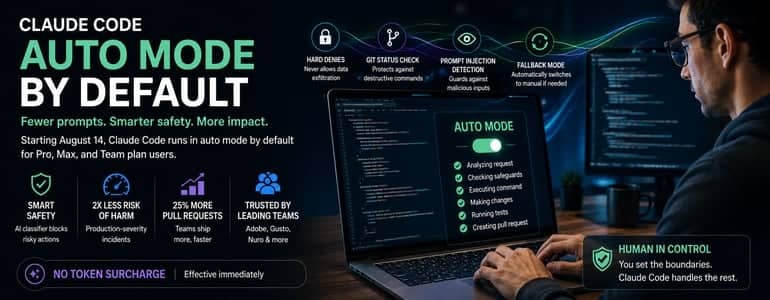
Anthropic Makes Claude Code’s Auto Mode the Default, Betting Automation Beats Manual Review
Anthropic is making Claude Code’s auto mode the default for Pro, Max and Team users, replacing constant permission prompts with classifier-based guardrails designed to catch risky actions without slowing developers down.
GitHub Brings Stacked Pull Requests Out of the Shadows
GitHub introduces native stacked pull requests, helping development teams break large changes into smaller, dependency-ordered PRs that are faster and easier to review.
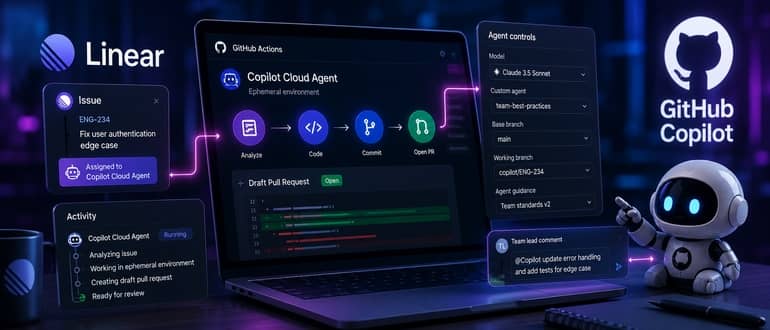
GitHub Gives Teams More Control Over Copilot’s Cloud Agent in Linear
GitHub’s Copilot cloud agent integration with Linear is now generally available, adding model, branch and team-level controls for delegated coding work.
FakeGit Targets AI Coding Agents with Malicious GitHub Repos
Threat actors continue to find new ways to incorporate AI into schemes aimed at luring developers into downloading malware from fake repositories. The latest example involves almost 7,600 malicious GitHub repositories that are being used to distribute a loader and an information-stealer. The FakeGit campaign is nothing new, with Oleg Zaytsev, lead security researcher with […]
Security Risks from AI Coding Agents Expand Beyond the Sandbox: Pillar
AI coding assistants have become an essential part of developers’ work, automating many of the repetitive tasks – think boilerplate coding and scaffolding – that in the past ate up a lot of their time. More jobs can now get done faster. That said, such agents also represent a significant security risk, making developers – […]
Signed, Attested, and Malicious: The Software Supply Chain Has a Deepfake Problem
A developer pulls a package from a reliable repo. It is signed, has provenance, and has been scanned. And then…it contains malware. That is no longer hypothetical. When the Miasma worm tore through the @redhat-cloud-services npm namespace in June, its malicious releases carried real SLSA provenance, because they were built in Red Hat’s own GitHub […]
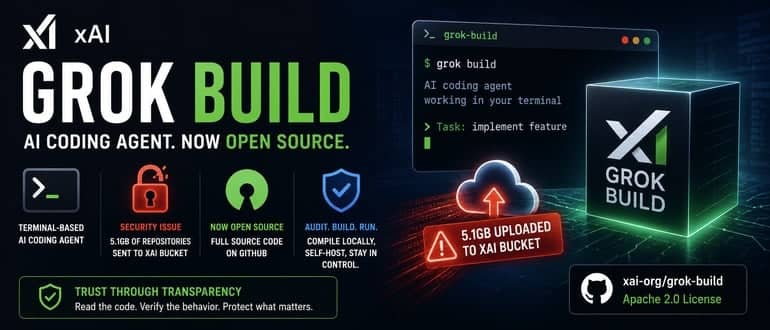
xAI Open-Sources Grok Build Coding Agent After Cloud Upload Exposes SSH Keys, Repos
xAI has published the full source code for Grok Build, its terminal-based AI coding agent, on GitHub under an Apache 2.0 license. The release lands three days after a security researcher showed the tool quietly shipping entire developer repositories — SSH keys and password databases included — to a Google Cloud bucket xAI controls. The […]
‘HalluSquatting’ Compromises AI Coding Agents to Install Malware, Create Botnets
Hallucinations have been an ongoing problem since OpenAI first introduced its ChatGPT chatbot in November 2022, highlighting generative AI’s tendency to generate plausible but false or misleading information and its inability to just say “I don’t know.” They can lead to embarrassing or uncomfortable moments. However, security researchers in Israel have found that the large […]
GhostApproval Flaw Featuring Decades-Old Feature Found in Six AI Coding Tools
A security flaw found in six popular AI coding agents can let attackers abuse a decades-old feature in Unix to trick an AI agent into giving them control of a developer’s system. Researchers with Google-owned Wiz said the vulnerability, dubbed “GhostApproval,” relies on symbolic links – or symlinks – a file system feature that has […]
Novee Uncovers Cordyceps: The Latest Threat to CI/CD Pipelines
A newly discovered supply chain security flaw is once again putting a spotlight on inherent weaknesses in CI/CD pipelines and the growing interest among cyberthreat actors to exploit them. Security researchers with Novee, an AI penetration testing platform provider, wrote about Cordyceps, an exploitable pattern in the open source supply chain that can allow attackers […]
Mozilla Shows the Danger of Indirect Prompt Injections in AI Coding Agents
A clean GitHub repository that contains no malicious code can launch an attack and fully compromise a developer’s systems by using indirect prompt injections to trick AI-powered coding agents like Anthropic’s Claude Code into taking steps that hand control to attackers and expose a wide range of secrets. In a proof-of-concept (PoC) attack, Mozilla 0DIN […]
AI Coding Costs Could Exceed Developer Salaries, Gartner Warns
Enterprises rapidly adopting AI coding assistants may eventually face an unexpected financial reality: the AI tools could cost more than the developers using them. According to new research from Gartner, spending on AI coding agents is on track to surpass the average software developer’s salary by 2028, driven by the rapid growth of LLM token […]
Tenet’s ‘Agentjacking’ Attack Turns Sentry Errors Into Code Execution
AI coding agents can create a new code execution risk when they treat externally influenced error data as trusted guidance and have access to command line tools, according to new research from Tenet Security. The security company demonstrated an indirect prompt injection technique it calls “Agentjacking” in a recent report. In its proof of concept, […]
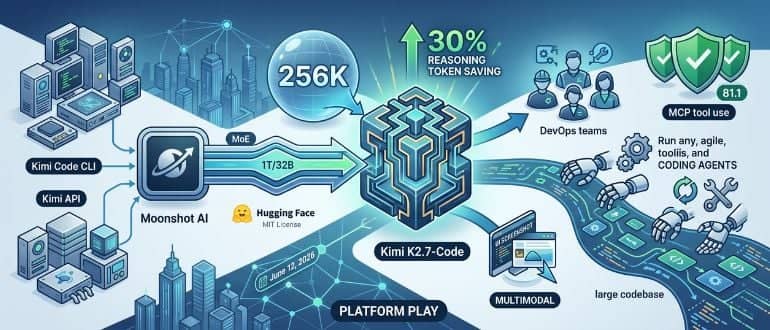
Moonshot AI’s Kimi K2.7-Code Targets Token Efficiency in Agentic Coding
Moonshot AI’s Kimi K2.7-Code offers 30% lower token usage and a 21.8% coding benchmark gain — here’s what DevOps teams need to know about the open-source release.