

AI Moved the Bottleneck From Writing Code to Understanding and Trusting It
AI coding boosts velocity, but without stronger review, governance and codebase visibility, teams risk higher costs, security gaps and production failures. TL;DR
Why You Need AI Agent Security Validation in Software Testing
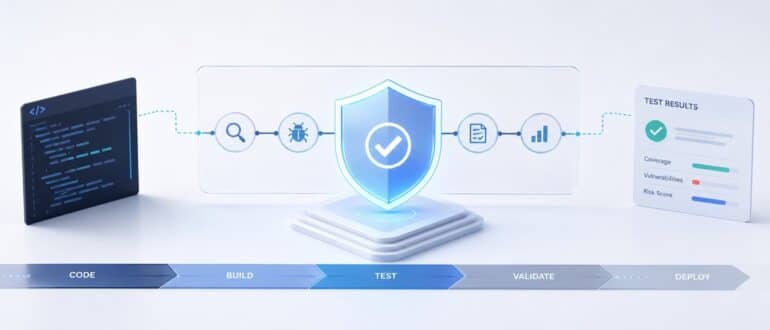
Engineering teams have been racing for the last two years to deploy AI agents that can find bugs faster than any QA team ever could. Autonomous testing agents can crawl through codebases, identify vulnerabilities, and generate test coverage reports while developers finally get to take a breath. The irony is that while development teams enjoy […]
AI Is Exposing a Growing Blind Spot in Open Source Security
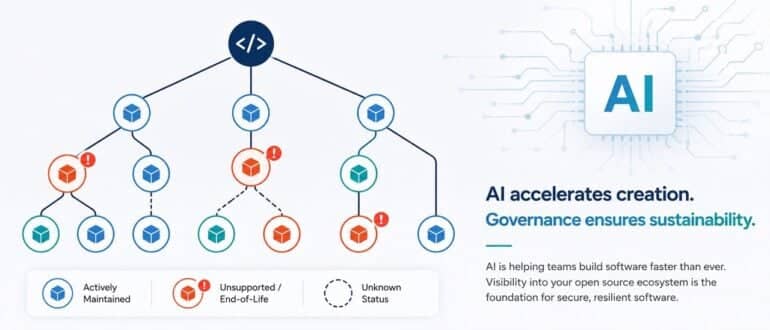
With AI, teams across organizations are now building internal applications faster than ever, often pulling in open source libraries and frameworks without much thought about long-term support, lifecycle management, or security ownership. An unintended consequence of this is that unsupported open source software (OSS) is quietly spreading across environments faster than security and engineering teams […]
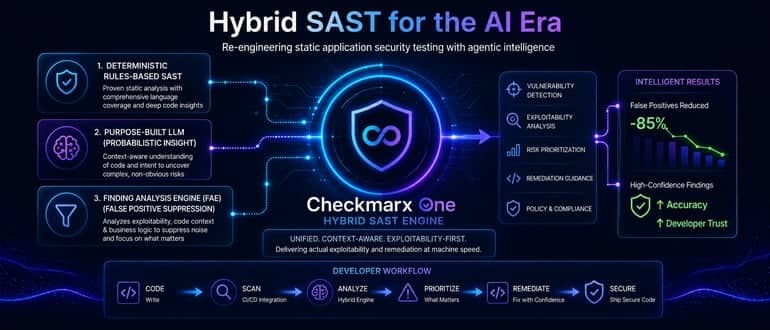
Checkmarx Adds Hybrid SAST Engine to Improve AppSec in AI Era
Checkmarx this week revealed it has re-engineered the core engines embedded within its static application security testing (SAST) tools for the agentic artificial intelligence (AI) era. At the core of that effort is a next-generation SAST hybrid scanning engine that combines three distinct capabilities within the Checkmarx One platform. An existing deterministic rules-based foundation is […]
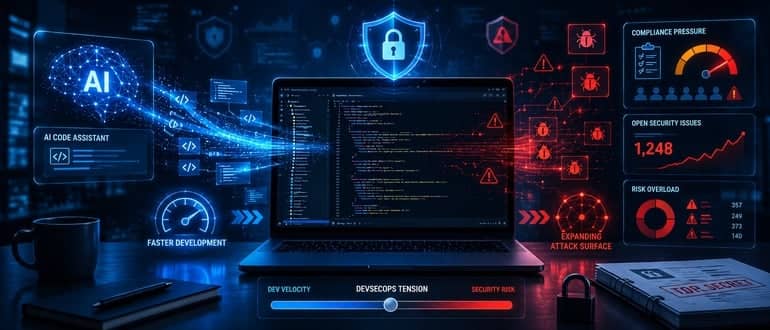
Survey Surfaces Depth of DevSecOps Crisis in the Age of AI
A global survey of 2,350 developers, CISOs and application security managers published this week finds that while nearly all respondents (96%) work for organizations that have embedded or connected artificial intelligence (AI) code and tools into some aspect of their application development workflows, nearly half of all code (49%) running in production environments was AI-generated […]
Agentic DevSecOps: AI Security Co-Pilots for Your CI/CD Pipeline
The emergence of AI has brought endless possibilities and innovative opportunities in today’s ever-changing, fast-paced technology landscape. AI is helping development teams produce software significantly faster than ever before. AI-enabled DevSecOps tools can automatically scan code, infrastructure and other configurations for security issues throughout development, accelerating the overall process. The introduction of agentic AI into the software […]
AI-Generated Apps Without DevOps: A Security Disaster Waiting to Happen
A small internal tool was built over a weekend. An engineer used an AI coding assistant to generate most of the backend. A simple interface was added, a few API calls were wired together and within hours the app was live. The app worked. The app felt fast. The app looked like progress. No one […]
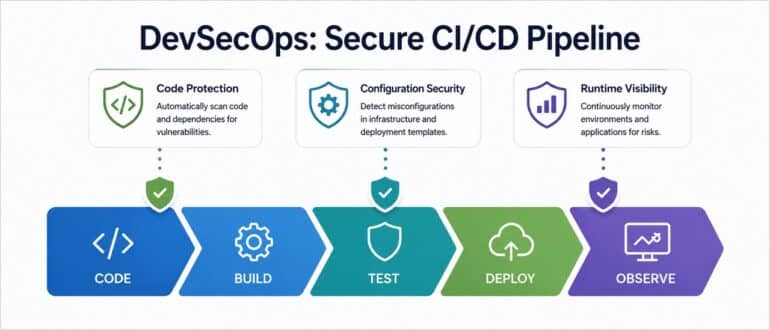
Beyond the Build: Integrating Security into CI/CD Pipelines
In today’s fast-paced software development landscape, Continuous Integration and Continuous Deployment (CI/CD) pipelines are essential for delivering applications efficiently. However, the speed and automation they offer can inadvertently introduce security vulnerabilities if not properly managed. Integrating security into CI/CD pipelines, often referred to as DevSecOps, is no longer optional; it’s a necessity. The Importance of […]
Agentic AI for Defense: How Checkmarx Turns Security into a Coding Partner
“AI-powered” has become the default label for every security tool on the market. But there’s a meaningful difference between a tool that uses AI to generate alerts after the fact and one that actively participates in development, preventing vulnerabilities as code is written. That difference is what separates reactive AI from agentic AI. And it […]
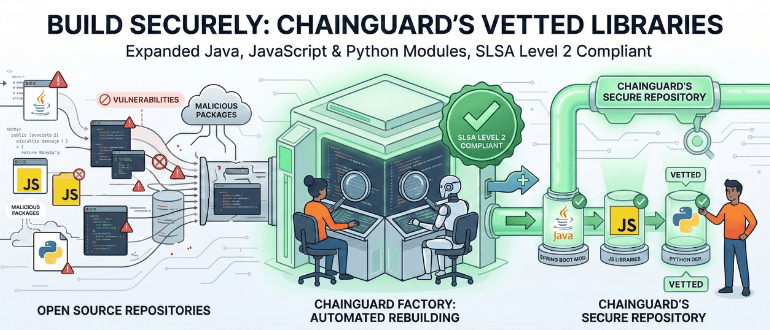
Chainguard Expands Repository to Add More Secure Open Source Libraries
Learn how Chainguard is strengthening software supply chains by expanding its secure repository of Java, JavaScript, and Python libraries, enabling DevOps teams to access components compliant with SLSA framework standards.

Tool Fragmentation is Breaking Delivery Context — Here’s What Teams are Learning
Explore the emerging crisis in application delivery caused by tool fragmentation in modern software development. This article discusses the need for semantic interoperability, context preservation, and a shift from linear pipelines to graph-based architectures to enhance efficiency and reduce cognitive load for developers
Secrets Management Failures in CI/CD Pipelines
Explore the critical role of secrets management in CI/CD pipelines and its impact on cybersecurity. This article highlights the risks of credential exposure, the importance of implementing strong security practices, and how organizations can ensure robust defenses against breaches and supply chain attacks.

Rein Security Emerges to Analyze Reachability of Application Vulnerabilities
Rein Security has emerged from stealth to launch an application security platform capable of determining the reach of a vulnerability based on which libraries and application programming interfaces are actually running in a production environment. Fresh off raising $8 million in seed funding. Rein Security CEO Matan Bar Efrat said DevSecOps teams can now gain […]

Apiiro Guardian Agent Prevents AI Models From Generating Insecure Code
Apiiro launches Guardian Agent, an AI security agent that rewrites prompts in real time to prevent insecure code from ever being generated, reducing vulnerabilities without slowing developers.
60% of Code Is AI-Generated—Are We in Trouble?
Jonathan Rende, chief product officer at Checkmarx, tackle’s one of the most urgent questions in AppSec right now: what happens when AI starts writing the majority of your software? With estimates that as much as 60% of code is being generated by AI in some environments—and that AI-authored code is already finding its way into […]
Survey Sees Wider Adoption of AI Coding Tools Creating More DevOps Challenges
Survey reveals 72% of developers use AI coding tools daily, generating 42% of code with AI. Trust issues persist, with 96% doubting AI code correctness.
Surprise! Everybody Uses AI Tools for Software Development, Few Do So Securely
AI is generating code faster than teams can secure it, widening software supply chain risk and exposing major gaps in AppSec and governance.
Checkmarx Acquisition of Tromzo Accelerates Plan to Apply AI to Application Security
Checkmarx accelerates its AI-driven DevSecOps strategy after acquiring Tromzo, integrating AI agents to automate application security across the software development lifecycle.
How to Escape the Talent Valley
Across the tech industry a disconcerting trend is emerging, job losses at the hand of a seemingly more efficient and cost-effective employee, artificial intelligence (AI). Software developers in particular have felt the full force of automation’s iron fist, with layoffs widespread. Since May, Microsoft alone has let go of approximately 15,000 employees, with software engineers […]
Endor Labs Adds AI SAST Tool to Discover Vulnerabilities in Code
Endor Labs launches an agentic AI-powered SAST tool that drastically reduces false positives, identifies deeper code flaws and helps DevSecOps teams secure AI-generated code across 40+ languages.
JFrog Adds Ability to Track Usage of AI Coding Tools
JFrog introduces AI-Generated Code Detection and Shadow AI Detection tools to identify AI-created code, track model usage, and enhance DevSecOps governance across software supply chains.

Establishing Visibility and Governance for Your Software Supply Chain
Asset visibility and cloud governance start with SBOMs, VEX, and provenance tracking. Learn how to secure your software supply chain.
What Makes Vulnerability Scanning Effective in Fast-Moving DevSecOps Pipelines Today?
Traditional vulnerability scanning can’t keep pace with CI/CD. Learn how real-time, context-aware scanning reduces noise, speeds fixes, and enables secure DevSecOps at scale.