


Datadog Unfurls Application Security Service
Datadog, Inc. today made generally available an Application Security Monitoring (ASM) service that is based on the same agent software that many DevOps teams already use to monitor applications. Pierre Betouin, vice president of product for the cloud security platform at Datadog, said ASM is designed to make it simpler for DevOps teams to add […]
Understanding SaaS Security for DevOps
As Software-as-a-service (SaaS) and DevOps adoption grew, new teams were formed to address emerging security challenges. Traditional solutions weren’t built to detect the new vulnerabilities in the cloud and created excessive noise for an already stressed pool of resources. The combination of emerging zero-day vulnerabilities and an avalanche of false-positives ends up increasing security […]
WhiteSource Offers Free Spring4Shell Vulnerability Tool
WhiteSource has launched a free command-line interface (CLI) tool that detects vulnerable open source Spring4Shell vulnerabilities (CVE-2022-22965) that are impacting Java applications built using the Spring development framework. Susan St. Clair, director of product management for WhiteSource, said the WhiteSource Spring4Shell Detect tool is similar to the tool the company made available earlier this year […]

3 Must-Haves When Implementing DevSecOps
The term DevSecOps is already more than a dozen years old. DevOps—the practice of combining software development with IT operations to deploy applications faster—was first coined in 2008 and refined in a historic conference presentation in 2009. DevSecOps—the concept of baking in security at every stage of Agile development, rather than tackling it at the […]
Secure Software Summit Series: Focus on Preventative Readiness
The connected world economy and the COVID-19 pandemic forced companies to accelerate digital transformation. Sophisticated cybercriminals have seized this forced acceleration to lay the groundwork for cyberwarfare. In reaction to recent attacks ranging from the SolarWinds breach to the recent Log4Shell exploits, many companies have quickly isolated and patched their systems. However, these reactive fixes […]

Linux Foundation Lists Top Open Source Libraries
The Linux Foundation today published a report that provides access to eight lists of the top 500 open source libraries being used by organizations as part of an ongoing effort to help better secure software supply chains. The Census II of Free and Open Source Software—Application Libraries report is based on usage data from providers […]
How to Build an Effective API Security Strategy
Application Programming Interfaces (APIs) enable organizations to grow their businesses and drive innovation. APIs allow applications to easily transfer data to external third-party developers, business partners and internal departments. Since APIs have access to valuable and sensitive data, they have increasingly become a target for cyberattacks. At the API Security Summit, taking place on March […]
How to Seamlessly Transition to DevSecOps
In the last few months, the cybersecurity world has been taken by storm following the discovery of the Log4Shell vulnerability. The zero-day had the potential to put much of the connected world at risk and left security teams scrambling to quickly apply security patches to software just before Christmas 2021. As a result of the […]
Why Developer-First is the Future of AppSec
DevOps culture and rapid cloud adoption mean developers are shipping code faster than ever and, in many cases, security teams struggle to keep up. To avoid relegating security to afterthought status, organizations must shift left and adopt a developer-first approach to application security (AppSec). Organizations that depend on software development need a solution that accomplishes […]
Best of 2021 – From Agile to DevOps to DevSecOps: The Next Evolution
As we close out 2021, we at DevOps.com wanted to highlight the most popular articles of the year. Following is the ninth in our series of the Best of 2021. As the workforce shifts to remote locations, networks are becoming more diffuse as the edge gets farther away. At the same time, the number of […]
Bridging the AppSec and DevOps Disconnect
Research estimates that cybercrime is going to cost the world $10.5 trillion annually by 2025, so it is no surprise that cybersecurity has become a top priority for business leaders. Today, security teams are striving to harden their systems against cyberattacks and improve their resilience through more employee security training, incident response programs and the […]
Mastering the Shared Responsibility Model
It’s no secret that cloud-native application development is growing exponentially, with Agile development, IaaS and PaaS from providers like Amazon, Microsoft and Google, enabling innovation at a pace that is challenging for security to keep up with. A global pandemic and the resulting remote work mandates have only accelerated this movement. And with this change […]

Data Theorem Adds Runtime Protection Enabled by Observability
Data Theorem, Inc. this week added an Active Protection offering to its portfolio of application security services that makes it possible for DevOps teams to embed observability and runtime defenses in their applications via a software development kit (SDK). The Data Theorem cloud services are based on Trustkit, an open source framework the company created […]
Oxeye Platform Helps Fix Code Vulnerabilities
Fresh from raising $5.3 million in seed funding, Oxeye emerged this week from stealth to launch a namesake application security testing platform that, in addition to pinpointing issues in code, also provides advice to best remediate the issues it found. The Oxeye platform requires developers to download an observer tool that scans code for vulnerabilities. […]
Secure Coding Adventure Park Virtual Summit: Wilder, Faster and More Visionary Than Ever
DevSecOps helps secure code from the start of production, rather than patching and debugging it at a later stage. It brings development, operations and security teams together so they can release secure software faster. At Secure Coding Adventure Park Virtual Summit, taking place on September 29, industry-leading AppSec and DevSecOps practitioners, analysts and visionaries will […]
AppSec Marketing in the Age of DevSecOps
A while back, I had a conversation with a friend I went to school with (currently a senior member of the engineering team at a large retail chain) who was tasked with the job of identifying potential application security partners (he addressed vendors as partners, which I personally liked) to collaborate with on various areas […]
No More Hot Potato: How Collaboration is Key in Application Security
Technology is accelerating at an unprecedented rate and companies with little digital footprint or experience in application security are struggling to keep up. With more and more breaches and vulnerabilities being detected in applications, people are shifting blame like it’s a game of hot potato. But it doesn’t have to be that way. With Shifting […]
How to Analyze Your Code for Security Vulnerabilities
Shifting Left 2.0 is a two-day virtual conference taking place from 9 a.m. to 2 p.m. PDT on June 22nd-23rd that dives deep into application security in the modern tech space. Security experts share insights on topics ranging from how to measure AppSec success to what role AppSec plays in digital transformation. Software developers, security […]
What Runtime Application Self-Protection (RASP) Doesn’t Solve
RASP, or Runtime Application Self-Protection, is a modern security technology that protects web applications from attacks during runtime. The technology is an important complement to defense systems that focus on the perimeter, but RASPs also have weaknesses that can introduce their own vulnerabilities. What are RASP’s strengths and weaknesses in protecting against modern security threats? […]
Security Risks With No-Code/Low-Code Tools
As the popularity of no-code and low-code tools grows, so, too, do security concerns The demand for new applications is growing at a rapid rate. Many individuals and business units will not tolerate delays. As a result, citizen developers are stepping in, some of whom may be sanctioned by the company while essentially operating as […]
Web Application Security is not API Security
Do you follow the same procedures to secure a web application as you do an API? Is there a difference between the two? We’ve spoken about API security quite a bit in the past few months because we believe that there are critical differences between API security and traditional web application security. A lack of […]

Modern AppSec and Supply Chain Attacks – Three Challenges
The recent news about the SolarWinds breach has focused on the difficulty and challenges a supply chain attack presents. In the case of what Microsoft is calling “solorigate,” the attackers modified a dll deep inside a trusted application, which was then deployed into over 18,000 enterprises and government organizations, where it would then create a live back […]
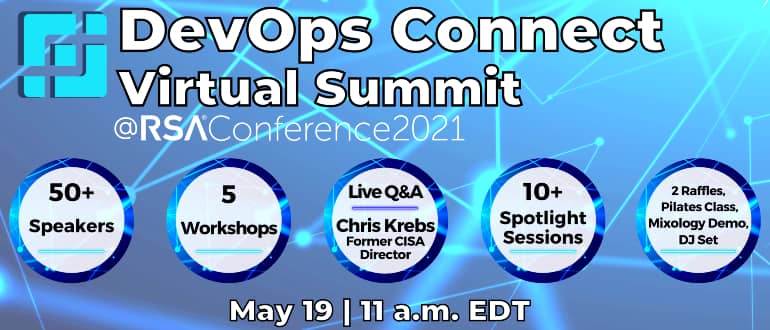
DevOps Connect at RSAC 2021: Insightful Talks, Live Q&A, Workshops, Pilates and More
We are excited to announce the return of DevOps Connect: DevSecOps Virtual Summit on May 19, as part of the RSA Conference 2021. This year, internationally recognized speakers will take a deep dive into “Securing the Cloud Native World.” DevOps Connect is a full-day event, featuring four different content tracks, with more than 50 speakers, […]