

VMware Aims to Advance Application Security
Most of the tasks associated with maintaining IT security assume that IT security professionals should discover and neutralize all potential threats to an application. At the VMworld 2017 conference this week, VMware is seeking to turn that notion of IT security on its head by focusing the efforts of IT security professionals on the known […]
Survey: Inviting Security into DevOps Promotes Effective Agility
Two of the biggest trends in business technology are seemingly at loggerheads with one another. Many companies are under severe pressure to digitally enable their businesses. At the same time, the need for hardened application security has never been more critical than it is now. You can deliver apps quickly and you can deliver apps […]
Study: Half of Enterprises Have Achieved DevSecOps
The inclusion of IT security into DevOps processes, also known as DevSecOps, appears to be occurring at an accelerated rate. A new survey of 300 enterprise IT organizations published this week by DigCert, a provider of identity management and encryption software, finds that almost half (49 percent) of the respondents says they have completed DevSecOps, […]
What Every Front-End Developer Needs to Know
One of the hardest things about being a front-end developer is the fact that everybody has very different expectations of what it means to be one. This, along with a technology stack that changes at the speed of light, makes interviewing for a front-end position tricky. To help you out, and to give you an […]
It’s All About the Tools: Lifecycle Security and Testing
In the past, whenever a new application or a new version of an application was bought to market, users often were abused as beta testers for security and usability. This was largely because of a lack of opportunity to test a large codebase effectively and efficiently. Similarly, the subsequent patches and new applications versions were […]
The 2016 State of Software Supply Chain Report is Here
Our State of the Software Supply Chain Report has just been released. Over the past year, we’ve amassed a great deal of data with respect to the staggering volume and variety of open source components flowing through software supply chains into development environments. This year, we assessed behaviors across 3,000 organizations and performed deep analysis […]
Rugged DevOps: Less Capture the Flag, More Teamwork
At the recent DEVNEXUS conference in Atlanta, I caught up with Chris Corriere to talk about his experiences in the realm of Rugged DevOps. Chris is a DevOps Engineer at AutoTrader and a contributor here at devopsy.kinsta.cloud. During our conversation, we discussed automation, culture and collaboration, and which thought leaders he is following. Chris also shared insights on […]
Case Study: Pearson Weaves ThreadFix into AppSec, Part 2
In part one, we discussed how education content publisher Pearson applied ThreadFix to its AppSec request workflow needs. Here’s the rest of the story. The ThreadFix Implementation Senior software security engineer Matt Tesauro added ThreadFix to Pearson’s workflow in the following steps: Using FPM, Tesauro created a Debian Linux package internally to deploy the ThreadFix […]
Case Study: Pearson Weaves ThreadFix into AppSec, Part 1
Pearson is a publisher of education industry content to meet the needs of teachers and students from kindergarten/early learning through higher education and continuing education (for professionals). The company uses a mix of software, from legacy third-party software and “classic ASP apps that are on life support to auto-scaling systems on Amazon,” says Matt Tesauro, […]
Minimum Viable App Doesn’t Mean Minimum Security
It’s estimated that the total market for mobile apps will hit $143 billion this year. A big portion of that budget will be enterprise mobile app development. By next year 25 percent of enterprise IT budgets will be aimed at their mobile app efforts. Yet, despite these efforts, most enterprises are still falling behind in […]
How DevOps Helps Improve Application Security
The DevOps trend is gathering pace, evolving from a niche to a mainstream strategy. Organizations are overcoming the barriers to successful implementation and finding real benefits in terms of speed and efficiency. But there are lingering issues to solve with regard to security. As companies look to push more changes to production more quickly, risks […]
Why do you need to implement a DevOpsSec team?
Just 20 years ago, organizations relied on a single wall of defense to secure their applications and networks. Fast forward to 2015 and that large fence is no longer adequate. With the proliferation of mobile, cloud and SaaS technology adding to the complexity of ever-advancing systems and networks, it becomes much more important that teams […]
Getting Rugged DevOps Right
Two Perspectives Jack, an accomplished application security pro, tells me, “The developers won’t talk to us. It’s like we speak a different language. They are releasing new builds so fast, how could they check each one for security vulnerabilities? We can’t move as fast as they do.” Then in the next moment, Diane, a DevOps […]
DevOpsSec: Survival is Not Mandatory
Deming, the patron saint of DevOps once advised, “It is not necessary to change. Survival is not mandatory.” To survive, application development teams are constantly pressured to deliver software even faster. But fast is not enough. The best organizations realize that security, quality and integrity at velocity are mandatory for survival. Hence, DevOpsSec My aim […]
DevOpsSec: 1 in 16 Chances
The quantitative research summarized below, covering over 7,000 repositories across nearly 100 countries, highlights some of the challenges with quality at modern development velocities, especially important for DevOpsSec practices. By leveraging automation in your repository manager, you can improve application quality and reduce unplanned work while lowering exposure to risk. While this practice supports DevOpsSec initiatives, at […]
The Software BOM Squad
In my previous post, “When Good Code Goes Bad“, I shared new research showing the average large development organization consumes over 15,000 known vulnerable and defective components annually. While we can’t stop software from going bad, there are practices from traditional manufacturers that we can use to improve our ability to recall and fix the “bad” […]
When Good Code Goes Bad
Milk spoils. Iron rusts. And in software, good code goes bad. Yet the difference is, with the first two, you know the change has occurred. With software, those changes are not always obvious. Your 5,100 Binaries Went Bad There is no way to prevent software from “going bad”. As with all products, bugs and defects,are […]
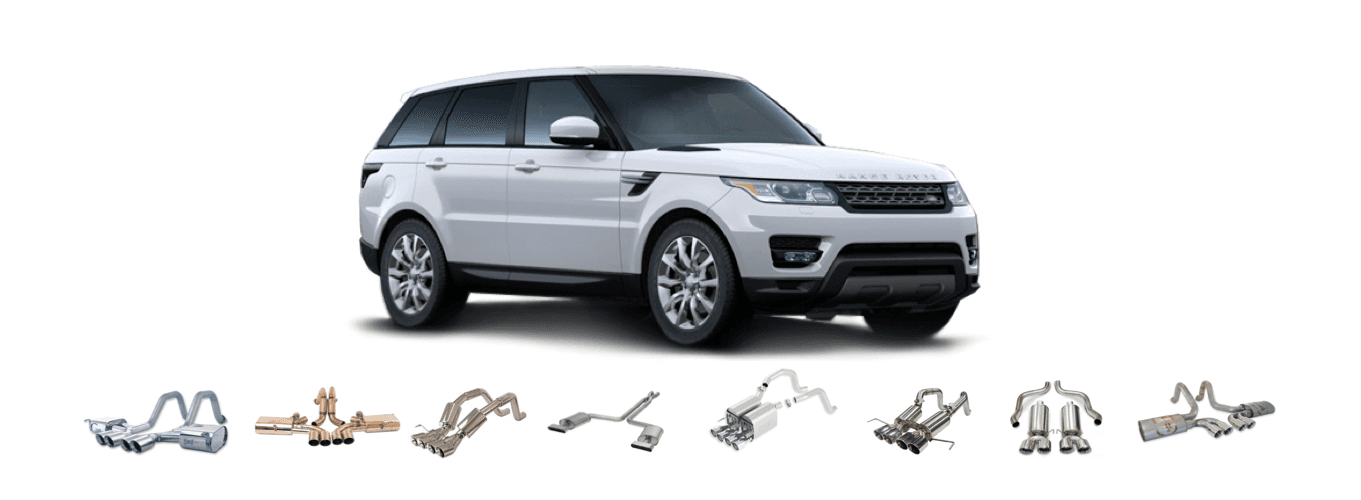
The Cost to DevOps: 27 Mufflers
Imagine Imagine that you are designing the 2016 Range Rover line of sport utility vehicles. Like all gas powered vehicles, each one needs an exhaust muffler. Range Rover likely has narrowed in on a preferred provider of mufflers. But imagine what would happen if the designers and factory line workers could pick from any one […]
The Myth of DevOps as a Catalyst to improve Security?
Few topics within DevOps discussions elicit more controversy than the relationship between DevOps and information security. Do DevOps practices help to improve security, or do most organizations simply automate and bring their existing bad internal processes along into DevOps? With this topic in mind, I recently had an engaging conversion with Adam Muntner on this […]
Managing Open source software components
Building any software need lots of efforts including resources, time, money, etc. It is really a great pleasure when it goes live or gets released. In parallel, there is always a chance that bugs may put the release in a difficult condition even after multiple rounds of testing. Teams can fix bugs related to software features […]
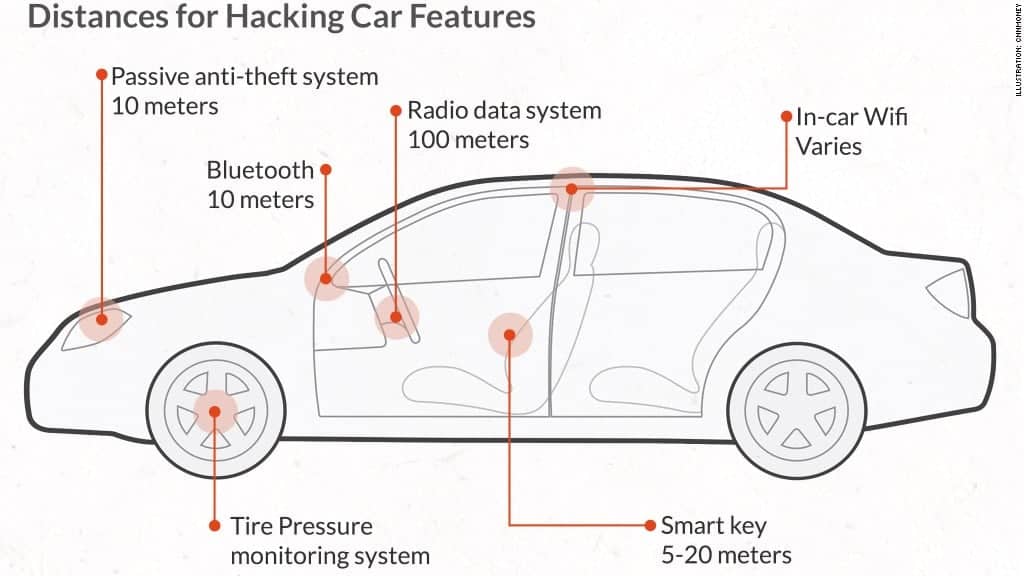
Chevy and DevOps: What the Wi-Fi?
In DevOps: Rapid Feedback, Rapid Repair I’m sure you have seen it too. Chevy cars now come with wi-fi. How cool. I want that (and so would my kids). I can only imagine the possibilities. But, this is not all about my needs. Chevy and every other vehicle maker wants this too. And not for the reasons […]