

Survey: Widespread Inability to Remediate App Vulnerabilities
A survey found only 20% of IT and security professionals are confident in their ability to detect a vulnerability before an app is released.
Backslash ASPM Platform Prioritizes DevSecOps Efforts
Backslash announced general availability of an ASPM platform that identifies and prioritizes vulnerabilities based on ease of exploitation.
Steady On. We Still Have a Job to Do
AI-generated change is not significantly different than the last couple decades where change has become IT’s constant companion.
Snyk Survey: AI Generating More Vulnerabilities in Code
A Snyk survey finds the use of artificial intelligence (AI) to write code is creating a software security paradox.
New Relic Adds App Security Testing Tool to Observability Platform
New Relic made available a public preview of an application security testing tool that will be integrated into its observability platform.
Mobb Launches Community Edition of Automated Remediation Tool
Mobb today made available a free community edition of a namesake tool that creates fixes to open source vulnerabilities. The fixes are based on the results of code scanning by a static application security testing (SAST) tool. Fresh from raising $5.4 million in seed funding, Mobb CEO Eitan Worcel said the company developed a tool […]
Cisco AppDynamics Survey Surfaces DevSecOps Challenges
A survey of 1,150 large enterprise IT professionals from the AppDynamics unit of Cisco suggested application security progress is being made slowly and steadily as organizations continue to embrace DevSecOps best practices. The survey finds that while more than three-quarters of respondents (76%) believe that DevSecOps is essential for organizations to effectively protect against a […]
AppSec in the Cloud: What DevOps Teams Should Know
Cloud application security refers to the measures and controls that are put in place to protect cloud-based applications and data from cyberthreats, unauthorized access and data breaches. These measures can include technical controls such as encryption, access controls and secure networks, as well as operational controls like policies and procedures for managing and securing data […]
2023 Application Security Budgets on the Rise
A survey of 500 DevSecOps professionals in the U.S. found nearly three-quarters (73%) of organizations plan to increase investment in application security in 2023. The survey, conducted by Wakefield Research on behalf of Invicti, a provider of dynamic application security testing (DAST) tools, also found 97% of DevSecOps teams said they ignored a real vulnerability […]
The Scariest Things About SCA
It is a time of ghouls, mischievous spirits and David S. Pumpkins. In the spirit of Halloween, here are the top five scariest limitations of software composition analysis (SCA) tools that are enough to send shivers down your spine. Read on … if you dare! 1. SCA Scans Only Your Application Code SCA’s scope is […]
Choosing the Right API Solution
There are more choices than ever when it comes to APIs–and that’s a good thing. But it also means you’ll need a strategic plan for choosing the right API solution. Two questions I’ve found can help guide that decision: What problem are you trying to solve right now? What functionality will you need in the […]
Putting the Security Into DevSecOps
The non-Newtonian fluid that’s composed of cornstarch and water has been around a long time, but Dr. Seuss’ 1949 book was the impetus for what it’s often called today – Oobleck, from “Bartholomew and the Oobleck.” When not under pressure, Oobleck is a thin liquid; when pressure is applied, its resistance increases to the point […]
Empathy for the API Developer
Security teams have always been perceived as an impediment to delivery by software teams who feel that security imposes arbitrary and unreasonable policies and use poorly-integrated tools that are beset with high false-positive rates. With the advent of DevOps, security has been seen as an increasing obstacle to rapid deployment cycles. Security teams believe developers […]
When DevOps-as-a-Service (DaaS) Meets Security
One of the most recent IT methodologies to be offered as a service is DevOps, a cultural and practical approach that brings development and operations teams together under one umbrella of work. DevOps-as-a-Service (DaaS) ensures that everything related to the selection, management and maintenance of DevOps tools and infrastructure, including all policies and procedures, are […]
Why Developer-First is the Future of AppSec
DevOps culture and rapid cloud adoption mean developers are shipping code faster than ever and, in many cases, security teams struggle to keep up. To avoid relegating security to afterthought status, organizations must shift left and adopt a developer-first approach to application security (AppSec). Organizations that depend on software development need a solution that accomplishes […]
Bridging the AppSec and DevOps Disconnect
Research estimates that cybercrime is going to cost the world $10.5 trillion annually by 2025, so it is no surprise that cybersecurity has become a top priority for business leaders. Today, security teams are striving to harden their systems against cyberattacks and improve their resilience through more employee security training, incident response programs and the […]
Mastering the Shared Responsibility Model
It’s no secret that cloud-native application development is growing exponentially, with Agile development, IaaS and PaaS from providers like Amazon, Microsoft and Google, enabling innovation at a pace that is challenging for security to keep up with. A global pandemic and the resulting remote work mandates have only accelerated this movement. And with this change […]
Data Theorem Adds Runtime Protection Enabled by Observability
Data Theorem, Inc. this week added an Active Protection offering to its portfolio of application security services that makes it possible for DevOps teams to embed observability and runtime defenses in their applications via a software development kit (SDK). The Data Theorem cloud services are based on Trustkit, an open source framework the company created […]
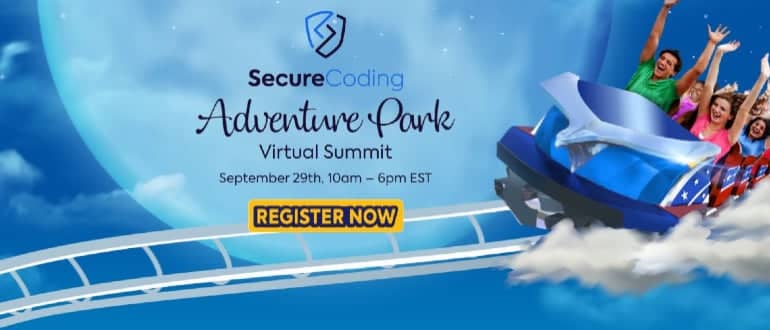
Secure Coding Adventure Park Virtual Summit: Wilder, Faster and More Visionary Than Ever
DevSecOps helps secure code from the start of production, rather than patching and debugging it at a later stage. It brings development, operations and security teams together so they can release secure software faster. At Secure Coding Adventure Park Virtual Summit, taking place on September 29, industry-leading AppSec and DevSecOps practitioners, analysts and visionaries will […]
AppSec Marketing in the Age of DevSecOps
A while back, I had a conversation with a friend I went to school with (currently a senior member of the engineering team at a large retail chain) who was tasked with the job of identifying potential application security partners (he addressed vendors as partners, which I personally liked) to collaborate with on various areas […]
No More Hot Potato: How Collaboration is Key in Application Security
Technology is accelerating at an unprecedented rate and companies with little digital footprint or experience in application security are struggling to keep up. With more and more breaches and vulnerabilities being detected in applications, people are shifting blame like it’s a game of hot potato. But it doesn’t have to be that way. With Shifting […]
How to Analyze Your Code for Security Vulnerabilities
Shifting Left 2.0 is a two-day virtual conference taking place from 9 a.m. to 2 p.m. PDT on June 22nd-23rd that dives deep into application security in the modern tech space. Security experts share insights on topics ranging from how to measure AppSec success to what role AppSec plays in digital transformation. Software developers, security […]
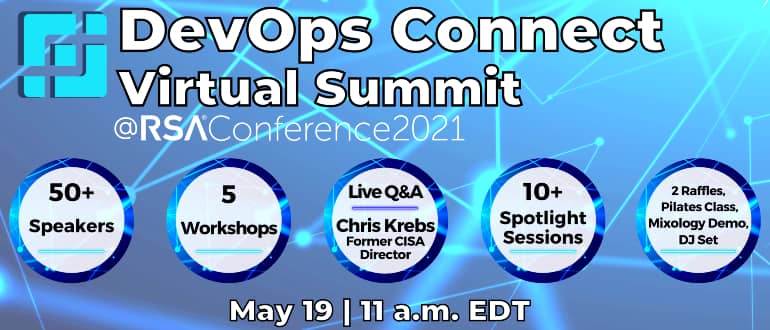
DevOps Connect at RSAC 2021: Insightful Talks, Live Q&A, Workshops, Pilates and More
We are excited to announce the return of DevOps Connect: DevSecOps Virtual Summit on May 19, as part of the RSA Conference 2021. This year, internationally recognized speakers will take a deep dive into “Securing the Cloud Native World.” DevOps Connect is a full-day event, featuring four different content tracks, with more than 50 speakers, […]