

GitHub Copilot Pulls Drawstring On Tighter Developer Usage Limits
New limits for GitHub Copilot come as no surprise. To roll out over the next few weeks, at the time of writing, two usage limit restrictions will come into place.
CloudBees Delivers on AI Promise to Improve Application Testing
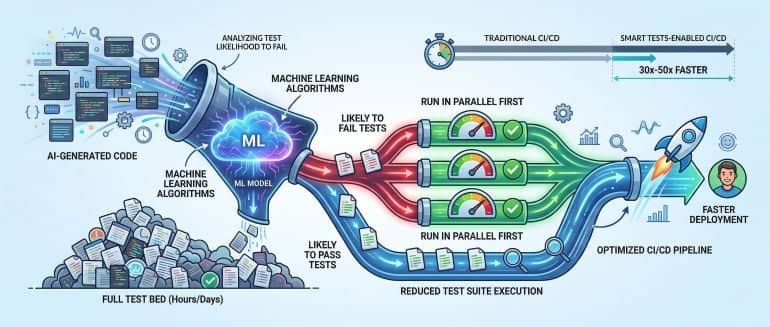
CloudBees has made generally available an add-on for continuous integration/continuous deployment (CI/CD) platforms that uses artificial intelligence (AI) to determine which tests should be run first based on the likelihood there will be a failure. Shawn Ahmed, chief product officer at CloudBees, said CloudBees Smart Tests eliminates the need to run an entire testbed. Instead, […]
Why Most DevSecOps Pipelines Fail at Runtime Security (not Build Time)
Runtime risk refers to security exposure caused by configuration, identity or infrastructure changes after deployment.
VibeCode Meets DevOps: Accelerating Low-Code Innovation
AI-assisted low-code tools like VibeCode speed app development, but DevOps teams must ensure security, quality and CI/CD integration.
If it Isn’t Code, it’s Just Advice
In the world of AI coding, success hinges on code-native solutions that integrate and verify changes directly in the codebase. Many AI tools fail by relying on external dashboards, lacking the reproducibility and testability that code provides. To truly harness AI, solutions must automate and validate changes within the existing code ecosystem, ensuring reliability and efficiency.
North Korean Hackers Suspected in Supply Chain Attack on Popular Axios Project
The threat actor targeted a highly popular open source project with more than 100 million weekly downloads, creating a large “blast radius.”
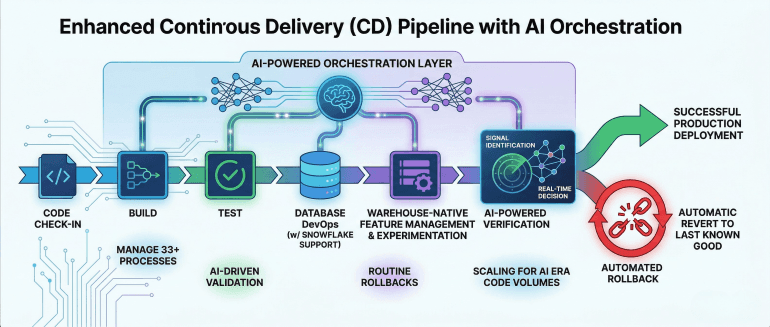
Harness Extends CD Platform to Address AI Coding Challenges
Harness expands its CD platform to tackle the “AI code explosion” with automated rollbacks, snowflake support, and warehouse-native feature management.

The Trust Tax Framework: Measuring Developer Confidence in CI/CD Systems
Is your re-run rate over 30%? Discover the “Trust Tax” killing your DevOps ROI. Learn to manage flaky tests through automatic quarantine, contextual reporting, and cultural shifts.
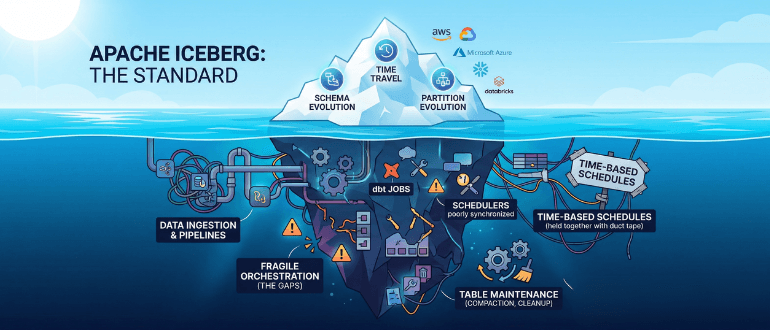
Iceberg Won the Format War — Now Comes the Hard Part
Apache Iceberg has effectively won the open table format conversation. AWS, Google Cloud, Microsoft, Snowflake, Databricks — every major platform has thrown its weight behind it. If you work in data engineering or platform operations, the question is no longer whether Iceberg is the right foundation. It’s what it actually takes to run it day […]
OpenTelemetry Gets Kotlin Multiplatform API & SDK
OpenTelemetry expands its observability reach with a native Kotlin Multiplatform API and SDK. Contributed by Embrace, this update enables vendor-neutral telemetry across JVM, iOS, and web, offering idiomatic Kotlin support and optimized performance for mobile and client-side applications.
Tekton Kubernetes-Native CI/CD Project Reaches CNCF Incubation
The CNCF TOC has voted to accept Tekton as an incubating project. As a Kubernetes-native framework for CI/CD, Tekton enables developers to build, test, and deploy across clouds by treating pipelines as standard K8s resources. Originally part of Knative, it now offers a modular ecosystem including Triggers and Chains for supply chain security, integrating deeply with Argo CD and Sigstore.
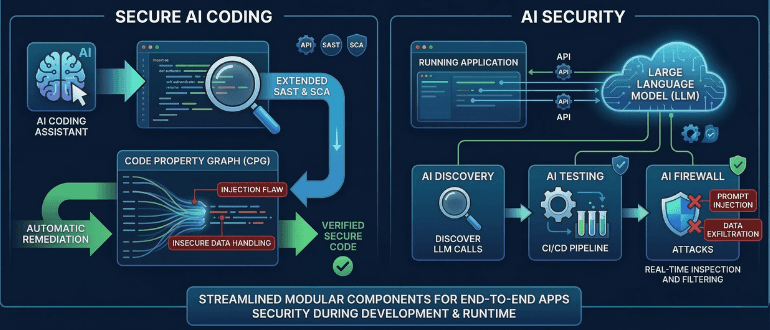
Harness Extends AI Security Reach Across Entire DevOps Workflow
Harness today added an ability to automatically secure code as it is being written by an artificial intelligence (AI) coding tool in addition to adding a module to its DevOps platform that discovers, tests, and protects AI components within applications. Secure AI Coding is an extension of the static application security testing (SAST) and software […]
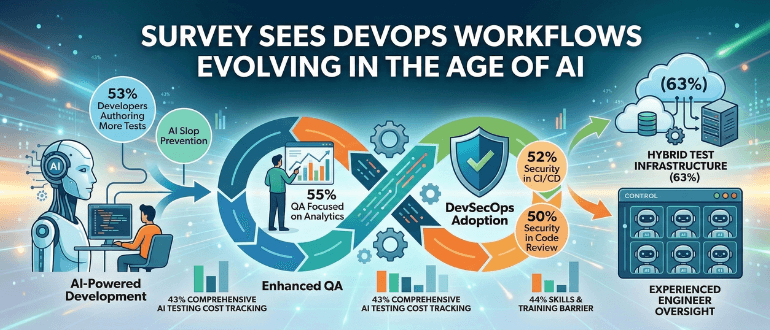
Survey Sees DevOps Workflows Evolving in the Age of AI
A global survey of 820 IT decision makers and DevOps practitioners finds that half of respondents (53%) report that developers in the age of artificial intelligence (AI) are now authoring more tests directly. Conducted by Perforce, that shift also appears to be enabling a similar percentage of organizations (55%) to provide quality assurance (QA) teams […]
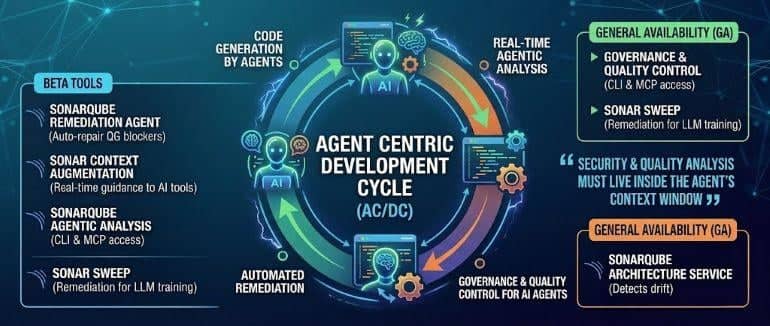
Sonar Unfurls Framework for Managing DevOps Workflows in the Age of AI
Sonar this week launched an Agent Centric Development Cycle (AC/DC) framework that promises to modernize continuous integration (CI) in the age of artificial intelligence (AI) coding. Announced at an online Sonar Summit, the AC/DC framework incorporates multiple tools and platforms the company has developed to better secure software supply chains, including now in beta Sonar […]
Google ADK Opens the Door to AI Agents That Work Inside Your DevOps Toolchain
Google ADK adds integrations for GitHub, GitLab, Jira, MongoDB, and seven observability tools. AI agents can now work inside your DevOps toolchain.

How OPA Changed Our Go-No-Go Forever
Learn how Open Policy Agent (OPA) transformed go/no-go releases from subjective meetings into automated, auditable, policy-driven decisions embedded directly in the CI/CD pipeline.
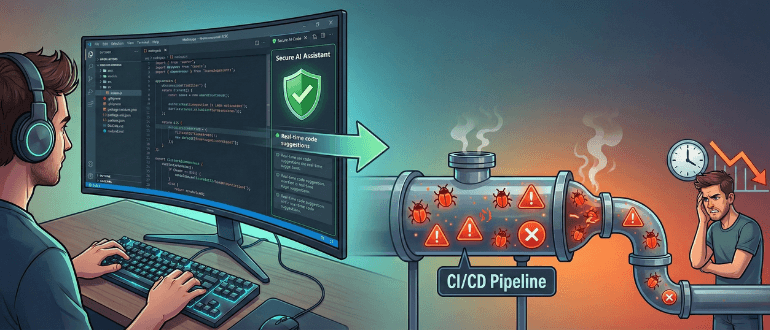
The AI Productivity Paradox: How Developer Throughput Can Stall
Software engineering leaders have invested heavily in generative AI coding assistants for over two years—and for good reason. For many teams, the productivity gains appear significant. I hear the same story in conversations with leadership at dozens of enterprises: thanks to AI, developers complete tasks faster, write more code, and spend less time on boilerplate […]
Test Automation Strategy for Growing Software Teams
Build a scalable test automation strategy that improves release speed, reduces defects, and supports growing software teams.
SRE vs. DevOps is a False Choice: Here’s the Unified Model That Works
DevOps and site reliability engineering (SRE) are complementary strategies that enhance both speed and reliability in software development. While DevOps focuses on collaboration and automation to break down silos between development and operations, SRE emphasizes engineering reliability through metrics and accountability. By integrating both approaches, organizations can foster high-quality software delivery that meets reliability standards, streamline incident response, and utilize data-driven decision-making to maintain system performance.

Bot-Driven Development: Redefining DevOps Workflow
Explore the future of DevOps with bot-driven development (BotDD) that integrates AI-powered tools. Learn how intelligent agents enhance automation, testing, and project management, transforming the software lifecycle.
Anthropic Adds Automated Security Reviews to Claude Code
Anthropic pulls security into the inner dev loop with new Claude Code tools that scan for vulnerabilities in the terminal and on every pull request—before insecure code ever ships.
DevSecOps In Digital Banking: Balancing Fast Releases With Regulatory Compliance
In the digital banking sector, fast releases of new features and security patches have become the norm. Unfortunately, many institutions lack the organization or the processes necessary to make the speed of necessary releases coincide with the need to follow strict regulatory guidelines. A failure to accurately test and ensure compliance can lead to critical […]
Importance of Observability in the DevSecOps Pipeline: Enhancing Security, Compliance, and Collaboration
In today’s rapidly developing software world, security cannot be an afterthought. DevSecOps, the integration of security practices into every phase of DevOps, requires continuous monitoring and actionable insights to detect and mitigate threats effectively. Observability plays an essential role in this ecosystem by providing deep visibility into the security posture of the development process, enabling […]