

Report: High Risks to Software Supply Chains are Commonplace
A nine-month analysis of more than 100 million alerts, tens of thousands of code repositories, and 140,000 real-world applications finds 95% of organizations have at least one high, critical, or apocalyptic risk within their software supply chain.
Succeeding at DevSecOps Requires a Rubric for SDLC Governance
Now is the time to engage your SDLC stakeholders and begin the journey of securing your development pipelines — the future of your organization’s security depends on it.
Backslash Security Adds Simulation and Generative AI Tools to DevSecOps Platform
Backslash Security today added an ability to simulate upgrades to a higher version of an application to its application security platform for scanning code and creating software bills of materials (SBOMs).
Secure Code Warrior Unveils Agent to Manage Commit Permissions
Secure Code Warrior (SCW) today added an agent to its portfolio of application security that assesses the security competency of developers as they commit code to a repository.
Implementing Threat Modeling in a DevOps Workflow
Integrating threat modeling into the DevOps workflow is essential to identify and mitigate potential security threats.

Report Surfaces Thousands of Potential Vulnerabilities in GitHub Workflows
An analysis of 2.5 million GitHub Actions workflow files belonging to 553,000 organizations and personal users surfaces thousands of potential vulnerabilities.

Survey Surfaces Lots of Software Supply Chain Insecurity
A global survey of 900 application security professionals finds nearly two-thirds work for organizations that have had their software supply chains compromised in the past two years.
Open-Source Software Community Riled by Yet Another CVE
Another maintainer of an open-source software project has decided to no longer actively update IP address parsing utilities used widely by JavaScript developers.

Aqua Security Shines Spotlight on Secrets Management Blindspots
A report published by Aqua Security finds that as many as 18% of secrets inadvertently exposed are not being discovered.
Ensuring Application Security from Design to Operation with DevSecOps
Safe development is critical for any company that creates software, whether for its own use or for others. DevSecOps principles focus on automating information security processes and introducing security measures early in software development. DevSecOps is extremely important these days as, according to recent surveys, more than 99% of tech professionals report that, on average, […]
Datadog Extends Scope and Reach of Observability Platform
Datadog at its DASH 2024 conference added a bevy of tools and capabilities to streamline DevSecOps workflows, including integration with open-source OpenTelemetry agent software developed under the auspices of the Cloud Native Computing Foundation (CNCF) and the Datadog On-Call tool to optimize incident management workflows in a way that maintains context with observability data already collected.

Why Business Risk Observability is Becoming Critical for Modern Applications
Full visibility into hybrid infrastructures is crucial for supporting the secure development and deployment of modern applications.
Decoding DevSecOps: Striking the Right Balance
DevSecOps has promise and pitfalls, and we need a path forward to achieve a balance between speed and security.
From Concept to Reality: How ASPM Brings DevSecOps to Life
Building on the foundation laid by DevSecOps, ASPM represents a leap forward in operationalizing these principles within the CI/CD process.

Survey Surfaces Extent of Web Application Security Crisis
A survey of 349 U.S. and UK cybersecurity professionals finds that while 60% work for organizations that update web applications at least once a week nearly three-quarters (75%) test their web applications monthly or less often.
Digital.ai Extends Scope and Reach of DevSecOps Platform
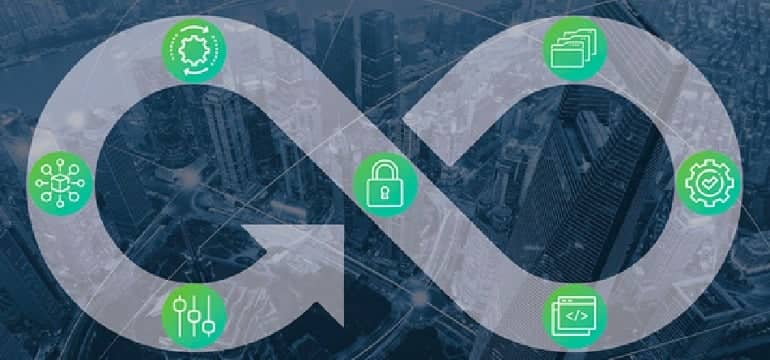
The Erawan Release of a DevSecOps platform provides a set of new and enhanced capabilities to help automate applications security along with integration with Backstage, an open-source internal developer platform originally developed by Spotify that is now being advanced under the auspices of the Cloud Native Computing Foundation (CNCF).
AWS Previews Generative AI Tool for CloudTrail Activity Logs
AWS today previewed a GenAI tool for its AWS CloudTrail data lake and is focusing most of its cybersecurity efforts on a new generation of cloud infrastructure that is inherently more secure.

Backslash Security Extends Reach of Application Security Platform
Making the Backslash application security platform even more secure with news of added support as well as a revamped, simpler user interface.
An Overview of Continuous Security Testing Processes for DevSecOps
Just getting started with DevSecOps and need a primer for the tools and processes to employ? This should help.
A Gentle Introduction to Continuous Monitoring and Optimization
The main objective of continuous monitoring is to help companies identify problems early enough for a DevOps team to address them before bad things happen.
Defining DevSecOps for IoT
By embedding security practices at every stage of the IoT development lifecycle, from design through deployment, organizations can significantly enhance the security and integrity of their IoT ecosystems.
Unlocking DevOps Mastery: A Comprehensive Guide to Success
DevOps is about breaking down silos, fostering collaboration, and promoting a culture of shared ownership and accountability. But at its core, DevOps is as much about culture as it is about technology.
The Role of DevOps in Orchestrating Enterprise-Wide Cloud Security
By implementing DevSecOps practices, organizations can proactively address security concerns early in development, reducing vulnerabilities.