


DevSecOps: Rethinking and Reengineering Cloud Security
Organizations are embracing the cloud to modernize legacy applications, create more resilient business infrastructures and to support remote work. In fact, Deloitte’s “TMT Predictions 2021: Cloud Migration Trends and Forecast” report suggests that, spurred by this growth, cloud revenues will likely continue to remain above 30% through 2025. While cloud migration is predisposed to embrace […]
How To Address DevSecOps Skills Shortages
“If it’s scarce, it drives the price up,” said McAfee director of systems engineering Sahba Idelkhani. And DevSecOps talent is scarce, and expensive. Restrictions on international travel are having an effect on immigration in some countries, notably Australia. But there’s practically nothing employers can do about that. But some aspects of the supposed skills shortage […]
42Crunch API Security Platform Now Available On-Premises
42Crunch has announced that the scanning tools it provides to enable DevOps teams to secure application programming interfaces (APIs) can now be deployed in on-premises IT deployments. Previously only available as a cloud service, the 42Crunch API Security Platform has also been updated to provide expanded support for the OpenAPI specification for REST interfaces defined […]
Red Hat Survey Reveals More Confidence in Open Source
A recent Red Hat survey revealed how DevOps teams increasingly depend on open source to support their shift to cloud-native environments and digital transformations, and to maintain security in these highly distributed environments. Based on a survey of 1,250 IT professionals, Red Hat maintains that the survey respondents — from organizations that were Red Hat […]

Sysdig Adds CSPM Module to DevSecOps Platform
Sysdig today announced it added a cloud security posture management (CSPM) module to its Sysdig Secure DevOps Platform for monitoring application performance and security to enable IT teams to continuously detect threats. Pawan Shankar, director of product marketing for Sysdig, said this CSPM capability is based on an open source Cloud Custodian tool that enables […]
Solvo Automatically Crafts Cloud Security Policies
Solvo today announced general availability of a namesake tool that automatically creates a least-privilege policy and applies it to application workloads deployed in the cloud. Previously available only as a private beta, Solvo will also continually analyze a workload after it’s been deployed to enable IT teams to adjust security policies as additional updates to […]

Data Theorem Extends Scope of App Analyzer Portfolio
Data Theorem, Inc. today added to its portfolio a Cloud Secure analyzer that promises to provide full stack visibility into applications through the client, network and cloud layers of a distributed computing environment. Doug Dooley, Data Theorem COO, said Cloud Secure extends an existing Analyzer Engine offering that is currently widely employed to identify vulnerabilities […]
How to Mitigate Low-Code Security Risks
Gartner predicts that by the end of 2025, over 65% of development projects will use low-code builders. The field of low-code continues to expand. But what security implications does low-code introduce? Low-code refers to tools that enable application construction using visual programming models. Adopting drag-and-drop components instead of traditional code, no-code and low-code platforms enables […]

Managing Business Risk in a DevOps Context
We hear a lot in the industry about the importance of automation in DevOps to enable speed. However, there is another element that is often missing in the discussion – risk, compliance and security. Traditionally we have a zero-sum approach, where we need to either go fast or be safe and secure. It’s one or […]
Copado Acquires New Context to Drive DevSecOps Adoption
Copado, a provider of a DevOps platform for building applications deployed on the Salesforce cloud platform, announced today it has acquired New Context as part of an effort to expand the scope of its portfolio into the realm of DevSecOps best practices. Andrew Leigh, chief marketing officer for Copado, said the acquisition brings Copado tools […]
Without These 3 Things, You Don’t Have DevSecOps
DevSecOps adds security to the DevOps software development and releasing paradigm. Everyone thinks this is a great idea, except actual Dev and Ops practitioners, for whom security can be a thankless, stressful time sink. Without the right approach and tools, an organization can run a DevSecOps process that actually contributes little to security. Security simply […]
GitGuardian Reports Careless Handling of Application Secrets
A new report, the 2021 State of Secrets Sprawl on GitHub, published today by GitGuardian, a provider of a tool for monitoring usage of application secrets, suggests developers are not especially good at keeping those secrets safe. Based on an analysis of every single commit made to GitHub, the report finds there has been a […]

GrammaTech Allies with GitLab to Advance DevSecOps
GrammaTech announced today it has partnered with GitLab to integrate its GrammaTech CodeSonar static application security testing (SAST) tools with the GitLab Ultimate DevSecOps platform. Vince Arneja, chief product officer at GrammaTech, said integration with continuous integration/continuous delivery (CI/CD) platforms such as GitLab is critical because it enables security scans to run automatically any time […]
Cybersecurity 2021: Are You Really Prepared for a Cyberattack?
As the majority of businesses are increasingly moving to the online world, employees keep working remotely and more cyberattacks keep happening all over the globe, there is no doubt that embracing DevSecOps should be the new normal for every company. Organizations need to be able to adopt DevSecOps practices and adapt to new and evolving […]
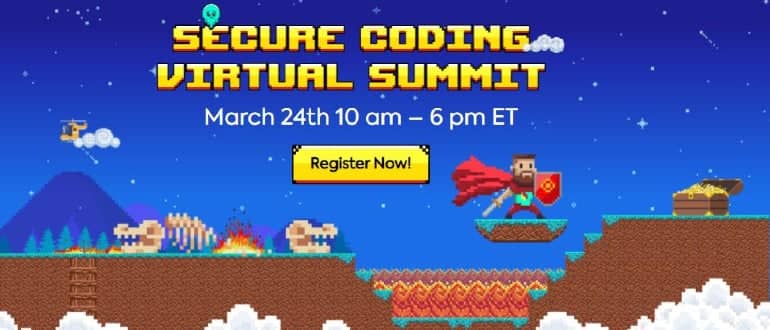
Game On: Secure Coding Virtual Summit 2021
Agile organizations are looking for ways to win at security without slowing down their release cycles. That’s where DevSecOps comes in. The days of a hands-off security approach for developers are over. Organizations implementing DevSecOps to integrate security into their DevOps framework are able to release secure software faster. Developers test code for potential security […]
GitLab Releases Updates to CI/CD Platform
GitLab this week made available a 13.9 update that adds more than 60 new features and updated capabilities to its namesake open source continuous integration/continuous delivery (CI/CD) platform. Brian Glanz, a product marketing manager for GitLab, said chief among those capabilities is a Security Alert Dashboard that enables DevOps teams to triage high-priority alerts more […]
Application Security and Continuous Observability with DeepFactor
Today’s modern applications are becoming increasingly complex and released more frequently than ever before, therefore increasing security, privacy and compliance risks. How do you identify the security and compliance risks hidden in your application before you deploy it to production? Continuous observability enables DevSecOps teams to observe millions of application telemetry events and find runtime […]
Protecting Data from Insider Threats
“Insider threat” can be defined as the threat an employee or a contractor will use their authorized access to, wittingly or unwittingly, do harm to an organization’s security. Certainly, as organizations become data-driven, embrace data democratization and release new applications at breakneck speed, the probability of an insider threat is rising sharply. A common example […]
DevSecOps Trends to Know For 2021
For DevSecOps leaders, 2021 will be the year of the open source supply chain attack. It’s already starting, in fact. On January 7, security researchers at Sonatype identified three malicious Java components in the Maven Central repository. The components had identical names to reputable components. Then on January 20, the same research team found three […]
DevSecOps May Be Key to Prevent Data Leaks
Data leakage has become something of a norm in the digital realm, despite the fact that cybersecurity budgets are growing and more engineers are assigned to these very issues. Nowhere does this seem more true than in the realm of health care, where breaches that expose sensitive patient data are, sadly, a fairly common occurrence. […]
DevSecOps Implementation: Patch Management
Patch management has been a thorn in IT’s side for decades. While it is undeniably necessary for security and stability purposes, the staggering array of patches that are available make managing them effectively nearly a full-time job – or a job better left to users. Few IT professionals want to be the “patch person,” and […]
ZeroNorth Adds Analytics App to Advance DevSecOps
ZeroNorth today added an Advanced AppSec Risk Analytics module to its platform for orchestrating DevSecOps processes. John Worrall, ZeroNorth CEO, said the analytics tool pulls vulnerability data generated by a variety of security tools to provide both DevOps and cybersecurity professionals with a single source of truth for assessing security within an application environment. The […]
Survey Shows DevSecOps Progress in Larger Organizations
A survey of 250 U.S. and UK large enterprises with more $1 billion in revenue conducted by Security Compass, a provider of a platform for automating security tasks as application are developed, finds three-quarters (75%) have implemented DevSecOps processes on current application development projects. Rohit Sethi, CEO, Security Compass, said the State of DevSecOps Report […]