

Trend Micro Partners With Snyk to Advance DevSecOps
Trend Micro today announced an alliance with Snyk through which alerts about vulnerabilities in open source code will be passed on to the tools Trend Micro makes available to apply virtual patches to both monolithic and microservices-based applications. Snyk provides a tool that identifies and fixes vulnerabilities and license violations in open source dependencies and […]
DevSecOps Becomes a Higher Cloud-Native Priority
At the Cloud Native Security Summit, Enterprise Strategy Group (ESG) today revealed the results of a survey of 600 senior IT leaders that finds organizations are looking at DevSecOps as a way to address the complexities of managing and securing cloud-native applications. According to the survey results, 43% of respondents said their biggest challenge with […]
IoT Security Concerns
The Internet of Things (IoT) is being hailed as the next step in our technological development. It’s hard to argue with that. The abilities it provides are as captivating as they are numerous: smart cars and homes, automatized agriculture, advancements in medicine that help with after-stroke recovery and the list goes on. However, while the […]
GitLab Outlines Scope of DevOps Ambitions
At the GitLab Commit event in New York today, GitLab launched an ambitious effort to extend the scope of its DevOps platform to provide a view into the software development life cycle for not just developers but also designers, product managers and business leaders. Fresh off raising an additional $268 million in funding, GitLab now […]
Weighing the Cost of Improper DevSecOps
Simply put, data breaches are terrible news for companies. And, the costs associated with such attacks continue to escalate. A recent IBM-sponsored report found an average price of 3.92 million per breach. Not adapting security automation and vulnerability scanning into development pipelines could have a drastic effect not only on cost but workload efficiency and […]
GitLab Survey Surfaces Major DevSecOps Challenges Ahead
A report based on a survey of 4,071 software professionals published this week by GitLab, a provider of a continuous integration and continuous deployment (CI/CD) platform, found that while appreciation of the potential value of DevSecOps best practices is high, the ability to implement those practices is uneven at best. According to the survey, half […]
6 Traits That Define DevSecOps
How do we define DevSecOps? A combination of DevOps and security is readily apparent, but the philosophy goes much deeper. In a recent eBook, The State of DevSecOps, we asked industry experts to define what DevSecOps meant to them. Below, we’ve condensed their answers into five core attributes. Following these principles, CIOs or CTOs now […]
Portable Security Policies: A DevSecOps Primer
Protecting critical data and applications is a challenge under any circumstances, but it’s especially daunting when resources reside in the cloud. Most organizations today operate a significant portion of their workloads in the cloud, which adds to the complexity of the security problem—a security team can’t fully control cloud environments but is responsible for securing […]
Shift Left Without Fear: The Role of Security in Enabling DevOps
It’s the age of DevOps, and we all want to shift left, which refers to the idea of performing processes earlier in the CI/CD cycle. That includes security checks and audits. By starting security operations earlier in the delivery pipeline, it becomes easier to find problems, and teams have more time to address them before […]
How to Design DevSecOps Compliance Processes to Free Up Developer Resources
Anything that gets rolled out quickly in the technological world is a major step forward—as long as it doesn’t compromise security. DevSecOps is able to provide compliance processes far more effectively than before, and without jeopardizing security while also freeing up developer resources. How do you direct your IT team to keep your applications and […]
7 Ways to Introduce DevOps in Your Work Culture
As many industries are going through a wave of digital transformation, a number of key technologies and principles are being deployed to business advantage. One such principle is DevOps. This collaborative principle is proving to be extremely helpful for businesses in their pursuit of customer satisfaction and beating their competition. The DevOps trend is growing, […]
DevOps Chat: AppSec and DevSecOps with Contrast Security’s Jeff Williams
I have known of Jeff Williams in the security industry for more than several years. He is a well-respected thought leader in AppSec and OWASP. I finally got a chance to catch up with Jeff and talk with him about Contrast Security, the company he co-founded and how it is helping. In this DevOps Chat, […]
DevOps Chat: Repos and Nexus Firewall Access, with Sonatype
There are really only two repositories of any scale for software components today: the Nexus repo managed by Sonatype and the Artifactory artifact repo managed by JFrog. Up until now they were separate and apart, and working with one was independent of another. In a big move toward keeping DevOps open and secure, the Sonatype […]
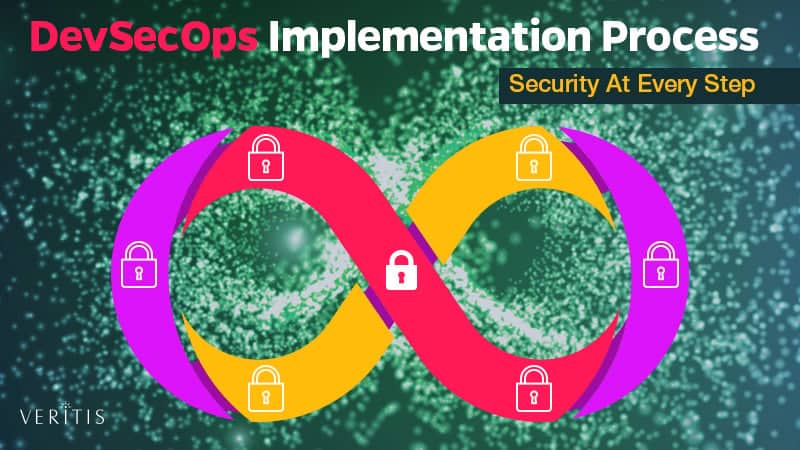
DevSecOps Implementation Process and Road Map – Security at Every Step
DevSecOps is changing our perspective toward security and is equipping us to deal with its challenges in an intelligible manner. The systematic approach of DevSecOps helps us add value to our business processes while ensuring security. Here’s a summary of the key inputs and a recipe for a successful software development project. Implementing DevSecOps with […]
IoT, Not People, Now the Weakest Link in Security
Do a quick search on “people weakest link” and you’ll see a raft of articles in which cybersecurity experts and computer scientists point to employees or end users as the biggest vulnerability. No doubt, people do silly (or outright abusive) stuff and open the door for a variety of enterprise security problems. Spoiler alert: There’s […]
Security and Speed: Why DevOps and Security Need to Play Nicely
It isn’t news that DevOps and IT security teams often struggle to align their departments and maintain a coherent balance between keeping a business secure and developing new applications to maintain customer interest. While security processes are a necessity, they can be deemed by DevOps teams to be manual and cumbersome, blocking the agility that […]
How to Become a DevSecOps Engineer
The popularity and success of DevOps means it’s now an increasingly common feature in IT job descriptions. One of the most important roles within DevOps, however, is the Security Engineer or DevSecOps Engineer. This deeply rewarding career requires a specific technical skill set, current knowledge of cybersecurity trends and a decent amount of experience. Perhaps […]
Are Developers Your First Line of Security Risk or Defense?
Every organization on the planet, whether public or commercial, is facing an ongoing challenge: to exist in an increasingly digital space. Past products must transform to meet the digital expectations of their customers, and new products must be built with “digital-first” frameworks in mind. After all, if they fail to meet these expectations, there’s almost […]
How DevSecOps Can Help Avoid Catastrophic Breaches
Earlier this year, Tesla’s Cloud was hijacked and used to mine cryptocurrency, exploiting a vulnerability in the company’s Kubernetes cluster. A mountain of FedEx data was recently exposed, affecting 119,000 individuals. The Equifax breach garnered international attention after an estimated 145.5 million Americans were jeopardized. In other news, we’ve reported on how the Vine Docker […]
WhiteHat Security Looks to AI to Advance DevSecOps
WhiteHat Security is now embedding artificial intelligence (AI) into the application security review services it provides, as part of an effort to advance adoption of DevSecOps processes. Joseph Feiman, chief strategy officer for WhiteHat Security, said the biggest resistance factor to DevSecOps has been the amount of time it takes to test applications for vulnerabilities. […]
DevSecOps: Embedding a Security Practice into your DevOps Approach
It’s a no-brainer that the element of security cannot be compromised even to the smallest of extents in today’s competitive, fast-paced, modern technology-driven IT infrastructure. However, to keep up with the rapid developments of other processes in this agile world, security is often given relatively less importance and in some cases, even left behind. As […]
451 Research Report Highlights Value of DevSecOps for the CI/CD Pipeline
One of the compelling benefits of DevOps for many organizations is speed. Between breaking down silos, streamlining processes and automating routine tasks, the process of developing and deploying software can be significantly faster. A new report from 451 Research and Synopsys, however, points out the value of incorporating DevSecOps in the equation, especially with continuous […]
Simplify DevSecOps with a Zero Trust Approach
There are major cyberattacks and data breaches weekly, if not daily. Each incident is unique in some way, but one element common to almost all successful attacks is trust. Whether it’s a disgruntled employee conducting an insider attack, an attacker infiltrating the network using stolen credentials or an exploit that leverages a third-party vendor or […]