

Murphy’s DevOps: 7 Habits of Rugged DevOps
Attendees of Rugged DevOps Connect at RSA packed Moscone West’s second floor Feb. 29 to immerse themselves in security. Among the presenters of the daylong event was Forrester analyst Amy DeMartine, who provided a tutorial on how security, developers and operations folks can work together better in the new DevOps world. Through a slide show, DeMartine […]
How DevOps Prevents DDoS Attacks
Distributed denial of service (DDoS) attacks are some of the most pervasive and difficult attacks to prevent. The attack uses many distributed endpoints and/or systems to flood a web domain, application or service with excessive service requests or application calls. There are limits to the amount of bandwidth or the number of service requests or […]
Murphy’s DevOps: Is Security Causing Things to Go Wrong?
“Rugged DevOps,” “DevSecOps”—am I missing any? About the only thing more abundant than the volume of terms emerging to describe different facets of how security supports DevOps are the number of vendors now claiming to provide products and services that “solve” related security problems. There have been some interesting offerings we’ve seen emerge at this […]
John Willis, Jez Humble & Josh Corman Headline DevOps Connect: Rugged DevOps at RSA
A week from today, February 29th, we gather in San Fransisco for DevOps Connect: Rugged DevOps @ RSA Conference at the Moscone Center. This is the 2nd year we are holding this conference and the line up is I think even stronger than last year! I am really happy and proud of the group that […]
Flash Mob Inflection: Rugged DevOps Revolution
Truthfully, I was never a huge fan of the HBO series “The Sopranos.” It’s not that it wasn’t entertaining; I just didn’t agree with the “best ever” label that so many espoused during the show’s halcyon days. This had something to do with living in Hoboken, N.J., at the time and feeling the show was […]
DevOps Connect: Rugged DevOps @ RSA Conference
Once again this year DevOps.com along with Sonatype, The Nexus Community, Gene Kim, Josh Corman and Mark Miller are producing DevOps Connect: Rugged DevOps @ RSA Conference. The full day event takes place at the Moscone Center on the Monday of RSA Week, February 29 (it only comes once every 4 years), 2016. After the […]
Rugged DevOps: Good, Bad & Ugly
The Good: DevOps has been a success for Dev. With higher expectations, better processes, more management focus and new tools like advanced PaaS and containers, developers are churning out more and more software faster than ever. Success! Or is it? The Bad: DevOps has been a success…for Dev. For Dev teams, this may result in […]
Making the Case for Secure, Defect-Tested Software Development
Creating a software security initiative in any organization is no easy feat. Often times, organizational culture or politics can provide development managers with a strong counterargument for implementing software security concepts. Unfortunately, building software without a consideration for security has become a less viable option given the increase in compliance pressures and widely publicized data […]
Getting Rugged DevOps Right
Two Perspectives Jack, an accomplished application security pro, tells me, “The developers won’t talk to us. It’s like we speak a different language. They are releasing new builds so fast, how could they check each one for security vulnerabilities? We can’t move as fast as they do.” Then in the next moment, Diane, a DevOps […]
DevOpsSec: Survival is Not Mandatory
Deming, the patron saint of DevOps once advised, “It is not necessary to change. Survival is not mandatory.” To survive, application development teams are constantly pressured to deliver software even faster. But fast is not enough. The best organizations realize that security, quality and integrity at velocity are mandatory for survival. Hence, DevOpsSec My aim […]
All Systems Fail*
Vince Lombardi once said, “It’s not whether you get knocked down, it’s whether you get up.” But in today’s world of high velocity development and release practices, it’s also about how fast you can get up. Today, we are seeing more news about sites from major online retailers and service providers like HP, Target, PayPal […]
DevOpsSec: 1 in 16 Chances
The quantitative research summarized below, covering over 7,000 repositories across nearly 100 countries, highlights some of the challenges with quality at modern development velocities, especially important for DevOpsSec practices. By leveraging automation in your repository manager, you can improve application quality and reduce unplanned work while lowering exposure to risk. While this practice supports DevOpsSec initiatives, at […]
The Software BOM Squad
In my previous post, “When Good Code Goes Bad“, I shared new research showing the average large development organization consumes over 15,000 known vulnerable and defective components annually. While we can’t stop software from going bad, there are practices from traditional manufacturers that we can use to improve our ability to recall and fix the “bad” […]
The Cost to DevOps: 27 Mufflers
Imagine Imagine that you are designing the 2016 Range Rover line of sport utility vehicles. Like all gas powered vehicles, each one needs an exhaust muffler. Range Rover likely has narrowed in on a preferred provider of mufflers. But imagine what would happen if the designers and factory line workers could pick from any one […]
Bring Your Own Exploit
Here’s a simple question: for each tool that your organization uses, have you (or someone else on your DevOps team) changed the default passwords? That should be a no-brainer, shouldn’t it? Of course you changed them! Or at least you changed them for the tools that looked like they would have default passwords. Well, OK, […]
Security at the Speed of Innovation
With the advent of the cloud and platform as a service (PaaS) offerings, developers are innovating faster than ever. But with this rapid pace comes risk. Companies quickly implement new apps to meet their business demands, but the increasing complexity of the infrastructure being used – both in the cloud, on premise, or a hybrid […]
Security Breaks DevOps – Here’s How to Fix It
The concepts of communication, collaboration, abstraction, automation and orchestration are cornerstones of the rapidly growing DevOps movement. At the same time reliance on virtualized infrastructure and Infrastructure-as-a-Service has exploded, making manual provisioning and management simply not feasible anymore; it takes too long and locks up too many resources. Modern DevOps methods and tools have emerged, […]
Rework is Choking Software
Rework is Hell “Software may be eating the world, but rework is choking software”, tweeted John Jeremiah (@j_jeremiah). To shed more light on what is choking software, new data was released last week in the 2015 State of the Software Supply Chain Report. In its discussion of application quality and integrity, the report revealed that the average […]
7,600 Open Source Projects Per Company (and how it impacts DevOps)
That Supplier is Better For You Since releasing the 2015 State of the Software Supply Chain Report, there has been a lot of great discussion across the industry on best practices for managing the complexity introduced by the volume and velocity of the components used across your software supply chain. Today I want to focus on […]
2015 State of the Software Supply Chain Report
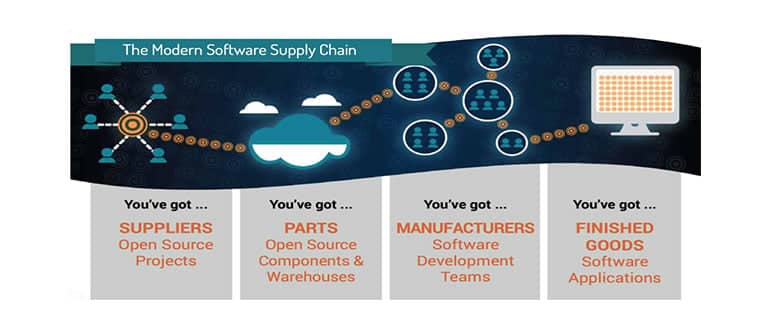
In April of this year, I embarked on a six-week journey diving deep into an analysis of the world’s software supply chains. I evaluated the practices of 106,000 organizations, the 100,000+ suppliers they relied on, and the billions of software components that fueled their agile, continuous delivery and DevOps practices. The facts I discovered and […]
The devOpsSec Dilemma: Effective Strategies for Social Networking
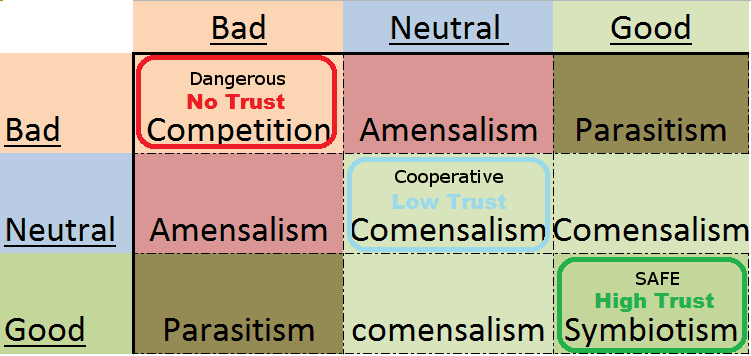
I was sad to hear of the passing of John Nash and his wife Alicia this weekend. May they rest in peace. As a game theorist I am familiar with his work and it just so happens that Nash Equilibriums have been in the center of what I’ve been working with lately. It’s an honor […]
DevOps Connect: Rugged DevOps @Infosecurity Europe
We have assembled another top flight list of speakers for our DevOps Connect event @Infosecurity Europe. While pre-registration is sold out, if you are one of the 15,000+ attendees of Infosecurity Europe, you can still come to DevOps Connect on a first come, first serve basis. Details and schedule are below: When: Thursday 4th June, […]
The #1 trick DevOps shops use to reduce vulnerabilities
A new report out this week highlights how important it is to find ways to fold in vulnerability assessment information into the software development lifecycle. Released by WhiteHat Security, the Website Statistics Report 2015 offers a smorgasboard of interesting data around web application security. Amid all of the statistics, though, DevOps shops should perhaps home […]