

How AI is Revamping DevSecOps Processes
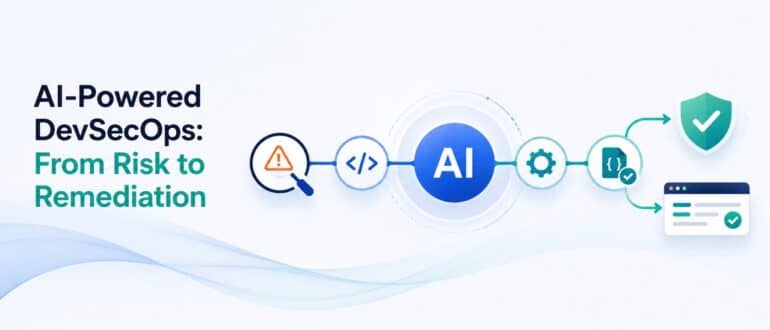
Artificial Intelligence is pushing DevSecOps into a new phase where security is no longer just about detecting vulnerabilities, but increasingly about resolving them automatically within the flow of software delivery. As many organizations are discovering, DevSecOps historically gave teams visibility into risk. AI is now turning that visibility into automated remediation. This evolution has taken […]
AI Is Exposing a Growing Blind Spot in Open Source Security
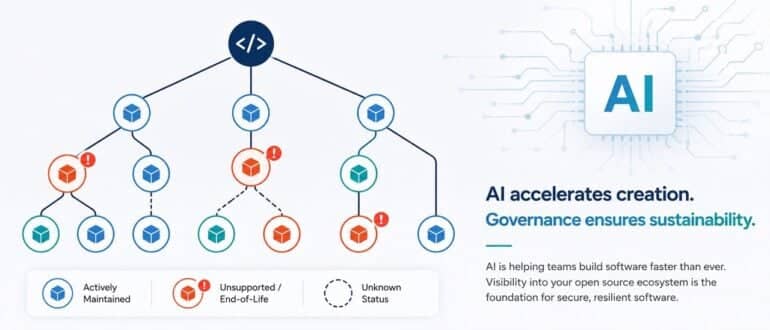
With AI, teams across organizations are now building internal applications faster than ever, often pulling in open source libraries and frameworks without much thought about long-term support, lifecycle management, or security ownership. An unintended consequence of this is that unsupported open source software (OSS) is quietly spreading across environments faster than security and engineering teams […]
Shift Left to the Developer’s Machine: Building Local Git Security Gates
Shift left to the developer’s machine. The principle is what matters: Stop secrets before they ship. The tooling is a means to that end.
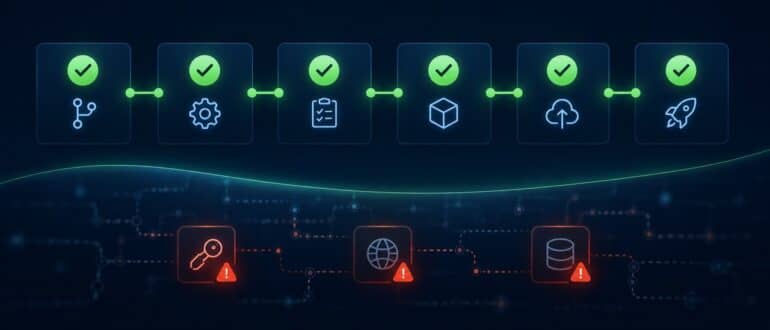
The Silent Risk of AI-Written DevOps Pipelines
These days, when a developer needs a CI/CD pipeline, they don’t always dive into GitHub Actions docs or spin up Jenkins from scratch. Instead, they pull up an AI assistant and type out something like: “Create a deployment pipeline for a containerized application.” Seconds later, the AI spits out a complete workflow. It looks polished. […]
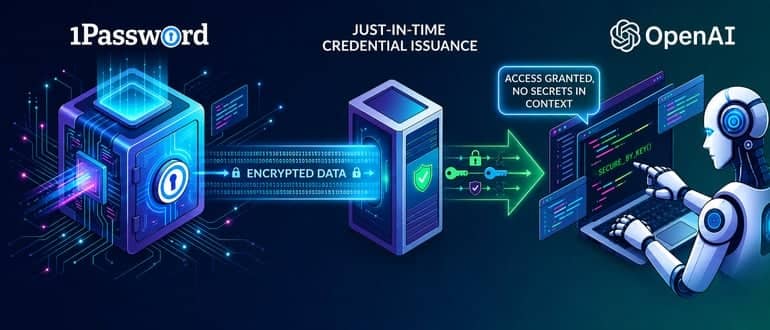
1Password Allies With OpenAI to Secure Codex AI Coding Tool
DevSecOps teams can now manage coding agents as a tenant rather than another vault where secrets might be stored, ensuring credentials are never exposed to an AI agent or LLM as plain text. The MCP server does not read or return secret values through the MCP channel, allowing Codex to create environments and invoke applications while the values themselves never leave the 1Password vault.
Open Source Contribution is About More Than Just Altruism
Passive consumption of open source software creates hidden costs, including $670,000 annually in internal workarounds; however, organizations that shift to upstream contribution report up to 5x returns through improved talent retention and faster development cycles.
AI-Generated Apps Without DevOps: A Security Disaster Waiting to Happen
A small internal tool was built over a weekend. An engineer used an AI coding assistant to generate most of the backend. A simple interface was added, a few API calls were wired together and within hours the app was live. The app worked. The app felt fast. The app looked like progress. No one […]
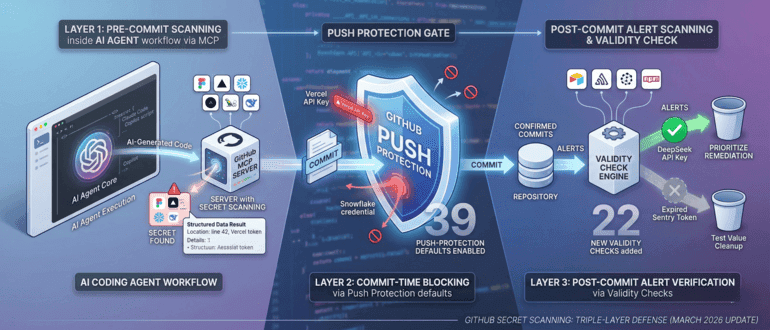
GitHub Adds 37 New Secret Detectors in March, Extends Scanning to AI Coding Agents
GitHub’s March 2026 updates introduce secret scanning for AI agents via MCP, 37 new detectors, and expanded push protection. Learn how to secure AI-generated code.
The Risk Profile of AI-Driven Development
Analysis arguing that AI-driven code generation accelerates dependency decisions and expands supply-chain risk, requiring shift-left governance, prompt-level controls, automated SBOM/AIBOM visibility, threat-modeling as engineering, and autonomous security to match autonomous development.
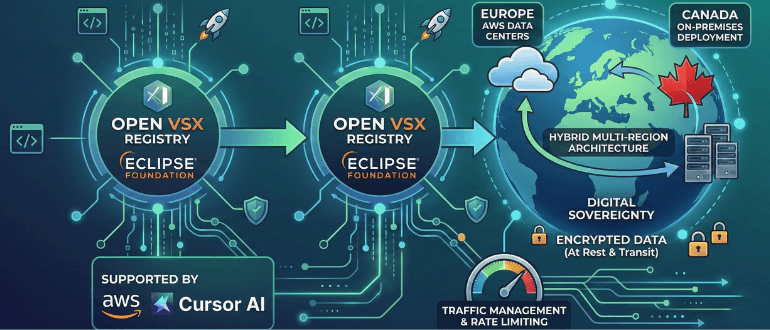
Eclipse Foundation Extends Scope and Reach of Open VSX Registry
The Eclipse Foundation launches a new framework for the Open VSX Registry, enhancing security features and transitioning to a hybrid architecture. With support from AI tool provider Cursor, this initiative aims to promote safer software supply chains.

AWS CodeBuild Webhook Misconfiguration Exposed Admin Access Risk
AWS fixed webhook filter misconfigurations in CodeBuild that could have allowed unauthorized repository access. No customer impact or malicious code found.
Codenotary’s Free SBOM Service Tackles the AI Software Supply Chain
Just because AI is writing your code doesn’t mean you can stop worrying about software bills of materials. While the quality of AI coding remains open to debate, there’s no question that everyone and their dog is using it. That means, if you’re serious about using AI in production, you must track its code in […]
Legit Security AI Tool Uses Threat Feed to Identify Risks to Software Supply Chain
Legit Security this week added a threat feed that DevSecOps teams can use to instantly determine if a newly discovered vulnerability impacts their software supply chain. Built using the Legit VibeGuard tool, the threat feed added to the company’s application security posture management (ASPM) platform also enables DevSecOps teams to take advantage of “vibecoding” techniques […]

Worms in the Supply Chain: Shai-Hulud and the Next DevOps Reckoning
DevOps was supposed to make software delivery faster, safer and more reliable. For the most part, it has. But every so often, something nasty crawls out of the shadows and reminds us how fragile the system really is. It wasn’t a zero-day in Kubernetes or a cloud misconfiguration that caught my eye. It was a […]
Securing the Software Supply Chain with Full Visibility and Compliance
At swampUP 2025 in Napa Valley, JFrog’s Yossi Shaul, senior vice president of DevOps, joined Alan to reflect on both his personal journey and JFrog’s evolving role in shaping modern software delivery. Shaul has been with JFrog since its early days, starting with the creation of Artifactory nearly 16 years ago — before “DevOps” was […]
Shai-Hulud Attacks Shake Software Supply Chain Security Confidence
Being the Dune groupie that I am, I couldn’t pass up the chance to comment on the “Shai-Hulud” NPM attacks. What a clever name for a worm attack. But as the saying goes, “the spice must flow,” so let’s have a look at what is going on here. The Backbone: What Is NPM (and Why […]
Outages and Security Threats in DevOps Tooling: Cracks in the Foundation
Alan warns that DevOps toolchains — from GitHub to Jira — are showing cracks, with outages and breaches threatening delivery resilience. He urges platform engineers to design for failure, harden security, and rethink vendor trust to prevent fragile foundations from collapsing.
Survey Surfaces Uneven Adoption of SBOMs to Secure Software
A survey of 100 security professionals finds nearly half (48%) of security professionals admit their organizations are falling behind on meeting software bill material (SBOM) requirements as specified by the U.S. Office of Management and Budget (OMB) Memo M-22-18, Executive Order 14028, and the European Union (EU) Cyber Resilience Act. Conducted during the recent RSAC […]
Checkmarx Surfaces Malicious Effort to Compromise Software Supply Chains
Checkmarx, this week, reported it has discovered malicious software packages that, in addition to injecting malware capable of bypassing endpoint security to exfiltrate data, also provide persistent remote access and control of desktops and servers.
Report: Commercial Software Just as Vulnerable as Open Source
An analysis published by ReversingLabs, a provider of tools for securing application development environments, suggests that commercial software used in software supply chains is just as vulnerable as open-source code.
Endor Labs Extends Microsoft SCA Alliance to GitHub
Endor Labs has allied with GitHub to integrate its software composition analysis (SCA) tools directly within DevOps workflows.
North Korea’s Lazarus Group Targets Developers, Supply Chain
North Korea’s notorious Lazarus Group is using an advanced malicious implant to target cryptocurrency wallets and spreading it via legitimate GitHub profile and possibly through npm packages. The ongoing campaign, dubbed Operation Marstech Mayhem, is the example of a threat group using open-source code repositories like GitHub, npm, and Python Package Index (PyPI) in software supply […]

Proactive Dependency Management: Reducing Risk and Improving Software Quality
Managing dependencies isn’t just best practice, it is an essential ongoing process. Implement these strategies in your projects to stay ahead of potential issues and ensure your software remains reliable, secure and up to date.