

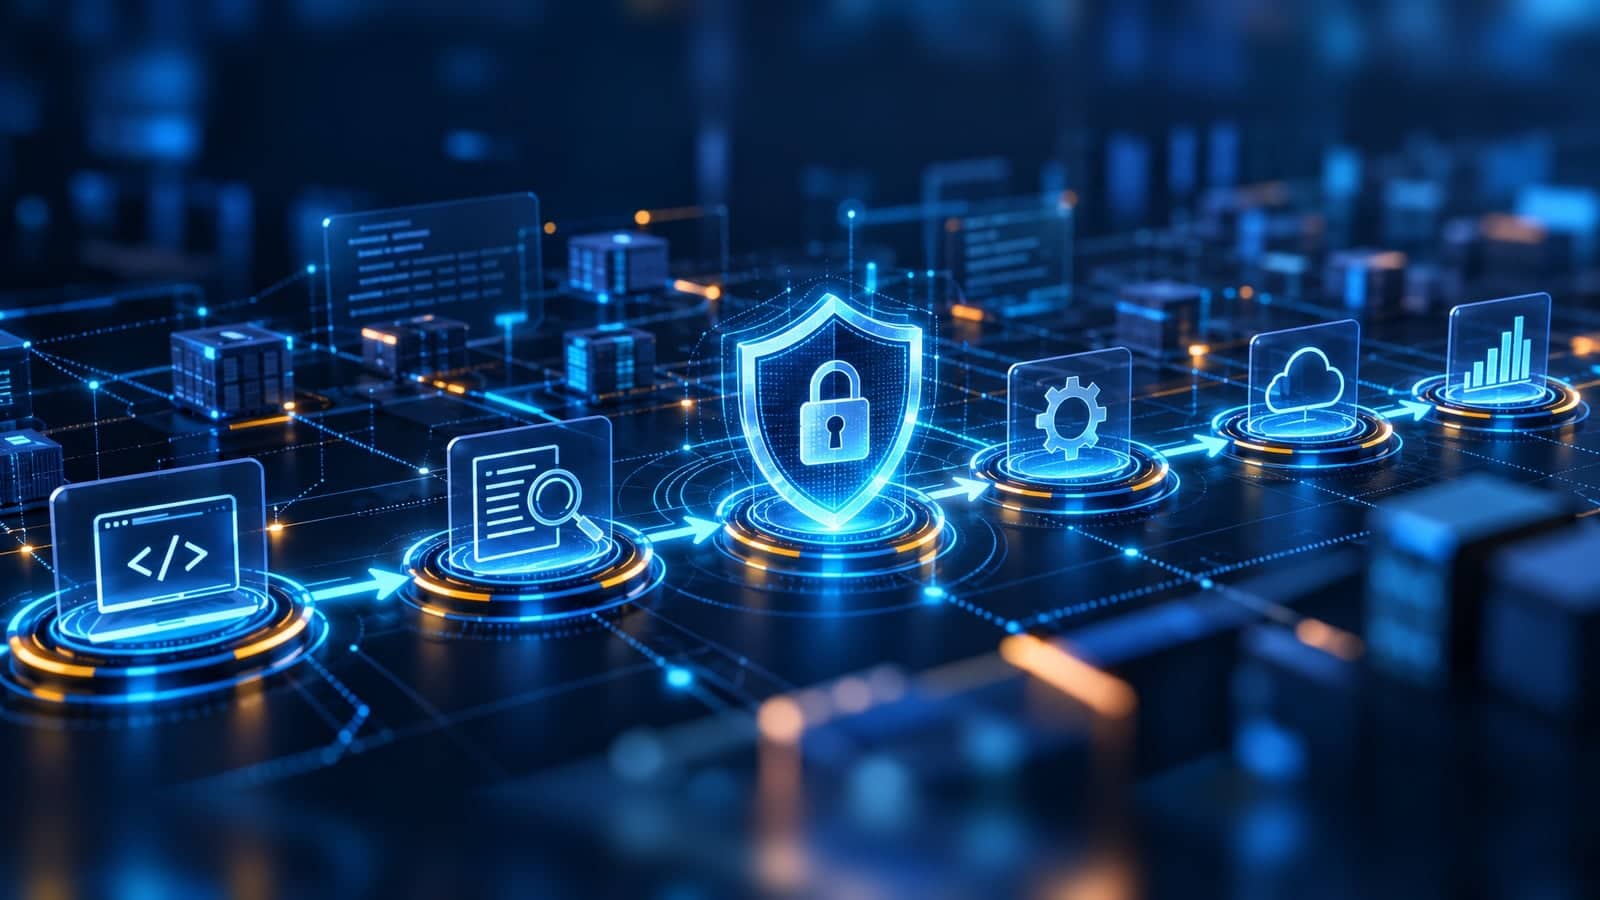
DevSecOps is part of the larger shift-left IT paradigm, which aims to identify and address vulnerabilities before they lead to security incidents.
NIST’s guidance on secure software development emphasizes integrating security throughout the development lifecycle, rather than treating it as a separate concern addressed late in development or after deployment.
By prioritizing a proactive approach to defense rather than reacting as events occur, teams can reduce the risk of development setbacks or post-deployment remediation tied to cybersecurity compromise.
But DevSecOps doesn’t just “happen.” Combining these three functions is a start. Ensuring they deliver on their protective potential means creating a multi-layered DevSecOps strategy that includes shared responsibility, automated testing, and continuous vulnerability management.
DevSecOps: Benefits and Challenges
The biggest benefit of DevSecOps is greater control over the software development and deployment process end-to-end. This is especially critical given the growing use of third-party and open-source components that save companies time and money but create possible vulnerability points for bad actors.
By ensuring security is part of every design and development decision, teams can identify and address issues earlier, while maintaining protections throughout testing, deployment and ongoing operations. Correcting identified problems is also easier the earlier they are caught. It’s relatively simple to remove and rewrite a line of code in a development build—it’s far more difficult in software that is fully deployed and integrated.
DevSecOps also comes with potential challenges. Some of the most common include:
- Skill and knowledge gaps: As a relatively new discipline, organizations may struggle to find and recruit skilled DevSecOps practitioners. Internal reskilling and upskilling can help address this issue. It’s also important to build a culture of shared responsibility that promotes security accountability across teams.
- Complex tool sprawl: According to research published in the Information and Software Technology (IST) journal, tool-related challenges were the most frequently reported DevSecOps issue. Tool sprawl is one common culprit; while more tools mean more data, they can also lead to complexity and confusion. Addressing this challenge means taking the time to thoroughly review potential tools before purchase and deployment. If they don’t address a measurable gap in current IT frameworks, they’re more likely to add complexity than value.
- Alert fatigue: With a focus on finding problems as quickly as possible, teams may face a growing volume of alerts, including false positives. To combat this issue, teams need to establish clear alert thresholds and leverage automated testing to address and resolve low-level issues without the need for human intervention.
The Role of Continuous Vulnerability Management in Proactive Security
Continuous vulnerability management helps address these challenges.
Four components play a critical role in effective vulnerability management:
- Risk Prioritization: Identifying and categorizing risk by short-term impact, long-term effect and overall likelihood lets teams ensure that continuous management efforts target critical issues.
- Ongoing Vulnerability Scanning: Given the rapidly changing nature of security threats and compromise pathways, fixed-interval scanning alone may leave important gaps. Instead, organizations should conduct regular, risk-based scans and continuously assess emerging vulnerabilities.
- Automated Remediation Workflows: When vulnerabilities are identified, DevSecOps teams should prioritize remediation based on the risks they pose. Automated and AI-driven workflows provide front-line defense against these issues. The caveat? They must be paired with human oversight to ensure accuracy.
- Continuous Monitoring: None of these steps happen in a vacuum. IT environments are constantly changing, which in turn requires continuous monitoring solutions that can collect, curate and correlate risk data for in-depth analysis.
Finding the Balance
DevSecOps integrates security earlier into software development, giving teams the ability to find and eliminate issues as early in development as possible.
As companies shift toward more proactive functions, however, it’s easy for everyday processes to fall farther down the list. Server maintenance, cloud coordination and resource management can take a backseat to more proactive efforts, setting the stage for long-term issues that go unnoticed until they impact day-to-day operations.
A partnership with a trusted IT services provider enables teams to focus on DevSecOps without losing sight of foundational infrastructure and network needs. For some organizations, this takes the form of 24/7 help desk support to solve critical issues. For others, it means fully managed IT support, including infrastructure design, installation and management.
When it comes to balancing DevSecOps and IT services, there’s no single path. To ensure they’re getting the service they need when they need it, companies should prioritize providers that seek to understand existing issues and create a tailored plan, rather than those that offer one-size-fits-all solutions that, in truth, really don’t fit anyone.
Making the Most of DevSecOps
DevSecOps strategies help organizations streamline software development and stay ahead of security issues.
Simply deploying DevSecOps, however, isn’t enough to guarantee success. Instead, teams need to create an environment of shared responsibility, deploy automated testing frameworks and implement continuous vulnerability management processes.
The result? Issues can be found and addressed before failures occur, not only after the fact.

Reporting and analysis on the technology, teams and operating models behind modern software delivery.