

Amazon Warns Engineers Against Tokenmaxxing as AI Costs Mount
Amazon has issued new guidelines for its software engineers that discourage excessive use of AI tools simply to boost productivity metrics, signaling a shift in how the company evaluates AI’s contribution to software development. The guidelines address tokenmaxxing, a practice in which employees use huge volumes of AI tokens to demonstrate their use of the […]
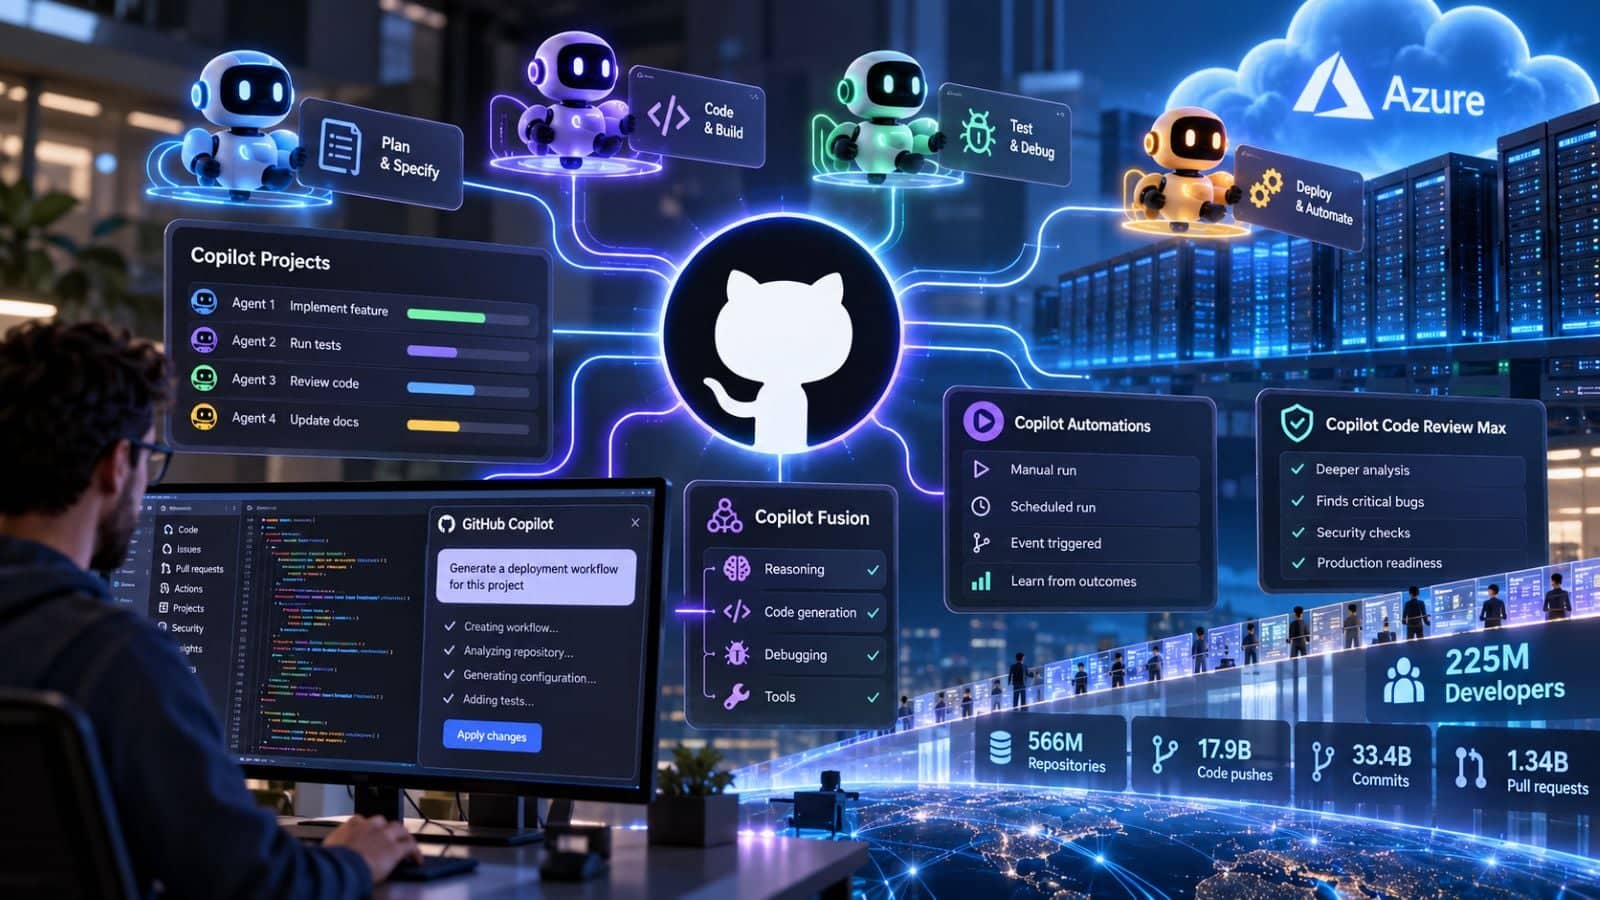
GitHub Adds Tools to Manage AI Coding Agents Running in Parallel at Scale
GitHub today made a bevy of updates that collectively promise to make it simpler for DevOps teams to build and maintain workflows using artificial intelligence (AI) agents. Announced at the GitHub Universe conference, Jay Parikh, executive vice president for CoreAI at Microsoft, also provided additional insights into the investments that Microsoft is making to ensure […]
How to Secure AI-Generated Code Across an Enterprise SDLC
Broken access control has topped the last two editions of OWASP Top 10, with OWASP finding some form of it in every application in its dataset. AI coding assistants are making this worse because correct access rules depend on business logic that rarely makes it into the prompt and is hard to test. For enterprises, […]
AWS Delivers AI Service to Discover Vulnerabilities and Generate Patches
Amazon Web Services (AWS) has made generally available a service through which it finds and validates code vulnerabilities and provides a patch that DevSecOps teams can then automatically apply or set up a pull request to implement. Dr. Neha Rungta, director of applied science at AWS, said the AWS Continuum service for code vulnerabilities is […]
Gheist Hackers Abuse GitHub Tokens to Steal Repository Secrets
The evolving Gheist campaign uses stolen GitHub tokens and malicious Actions workflows to extract repository secrets and cloud credentials. While GitHub protections have blocked observed attacks on public repositories, private environments remain exposed.
Claude Writes 180 Million Lines of Proofs to Verify 123 Open Source Libraries
Formal verification has long been the gold standard for software correctness. It has also been too expensive for almost everyone. New research from Anthropic suggests that’s changing. Anthropic’s Frontier Red Team, working with formal methods company Theorem, used Claude to prove security properties in the compiled code of 123 open-source libraries from Google’s OSS-Fuzz project. […]
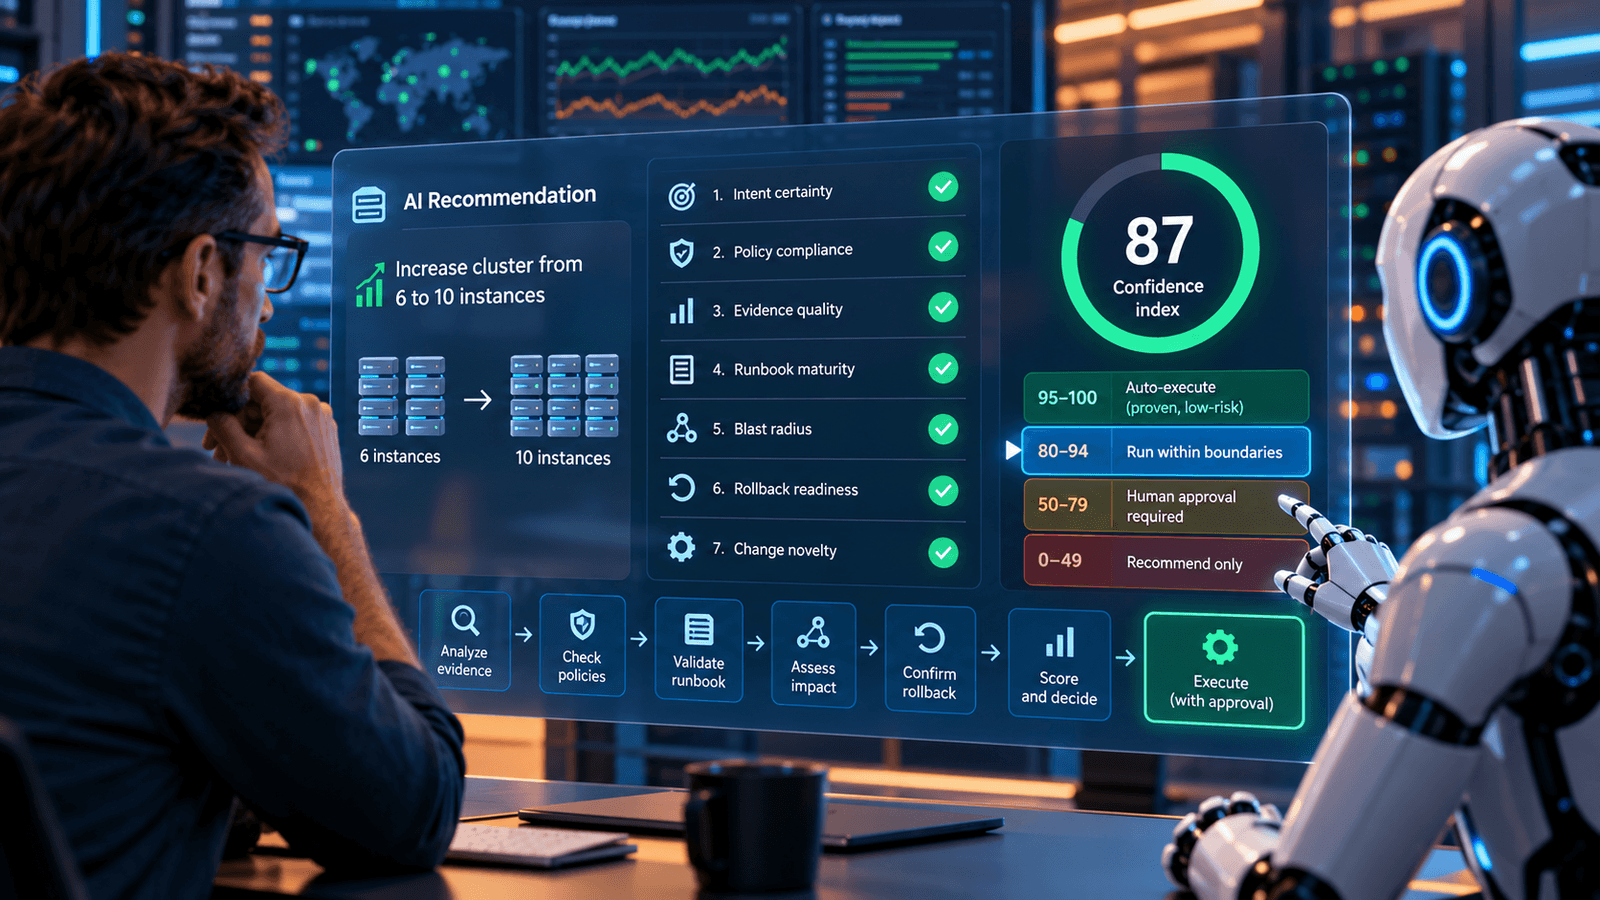
The Automation Confidence Gap: When Should AI Be Allowed to Change Production?
AI-generated infrastructure recommendations can look convincing, but production execution requires more than a plausible runbook. A seven-factor confidence index helps platform teams determine when AI should recommend, seek approval or execute changes within strictly enforced boundaries.
Hackers Inject Credential-Stealer, RAT Into LiteLLM
Attackers compromised a version of LiteLLM this week by injecting malicious code into all seven of its published Python wheels on PyPI, delivering a package that included an infostealer to exfiltrate credentials and secrets and a remote access trojan (RAT) that could let bad actors run arbitrary code on infected machines. The compromised version – […]
Linux Foundation: AI Speeds Development, but Low-Quality Code Strains Maintainers
A new Linux Foundation study finds that generative AI is delivering big productivity gains for open source software developers, but AI is also creating an influx of low-quality code submissions that need time-consuming human review. The research found that an estimated 25% of incoming pull requests, which are proposed changes to software projects, are considered […]
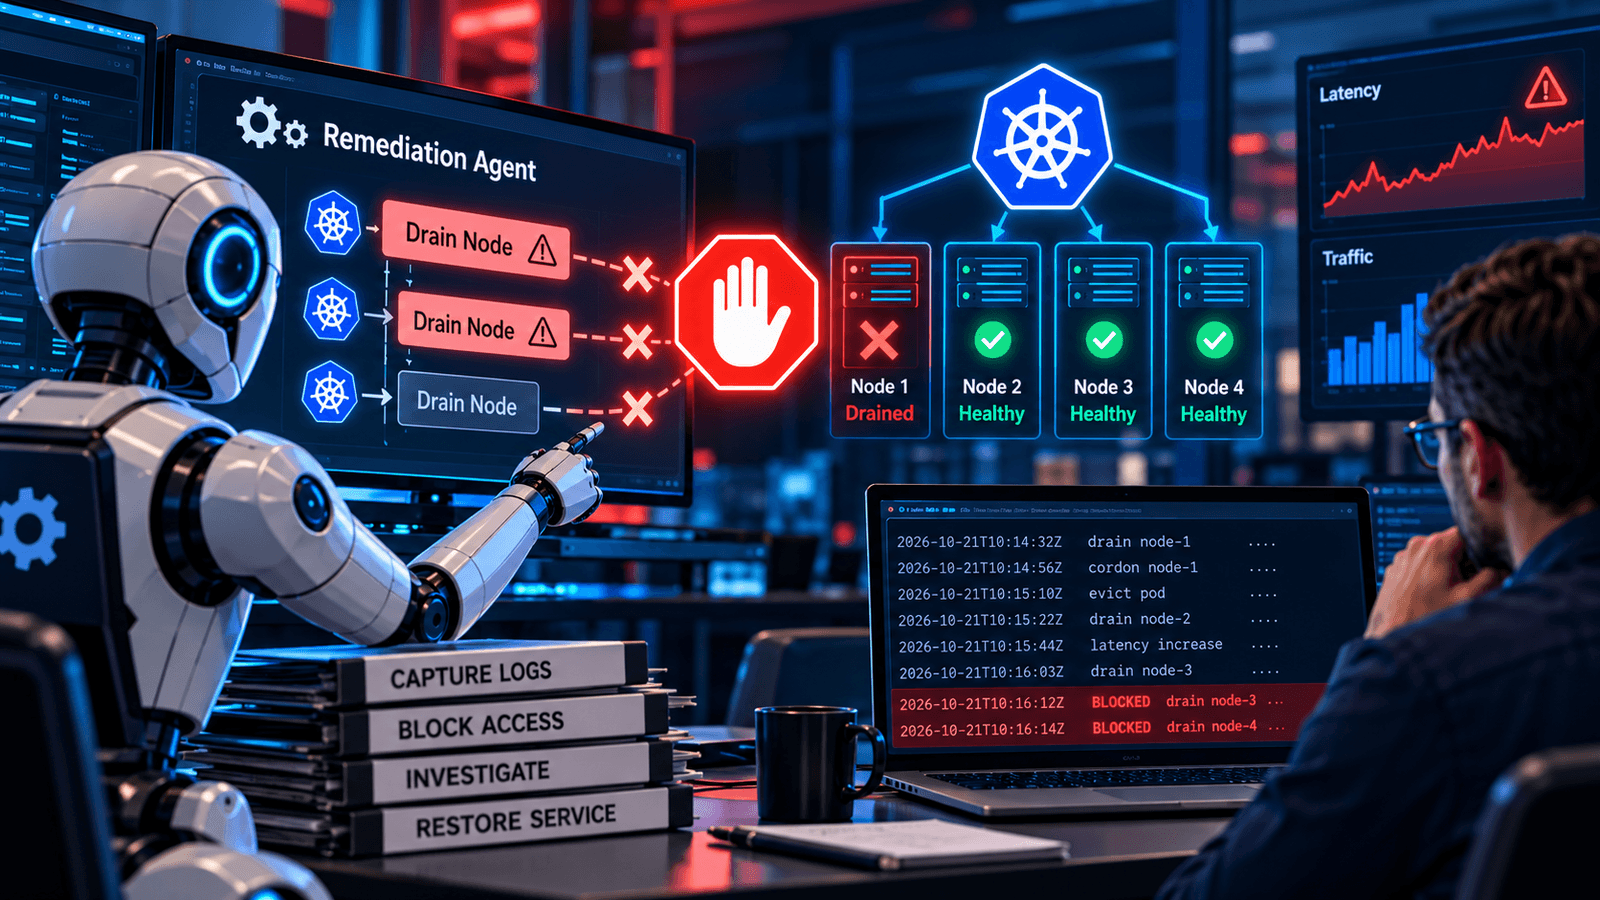
When the Agent is the Incident
When AI remediation agents make the wrong infrastructure decisions, automated fixes can quickly escalate into major incidents. This seven-step incident response playbook explains how to stop unsafe agent actions, block tool access, preserve forensic evidence and restore services without triggering further damage. A Kubernetes simulation demonstrates why stopping an agent worker alone is not enough.
Survey: AI Coding Tools Increase Open Source Software Dependencies
A survey of 307 enterprise technology leaders finds that as organizations rely more on artificial intelligence (AI) coding tools to build applications, they are simultaneously increasing the amount of open source software they are dependent on. Conducted by the market research firm Moving Horizon on behalf of ActiveState, a provider of a platform for accessing […]
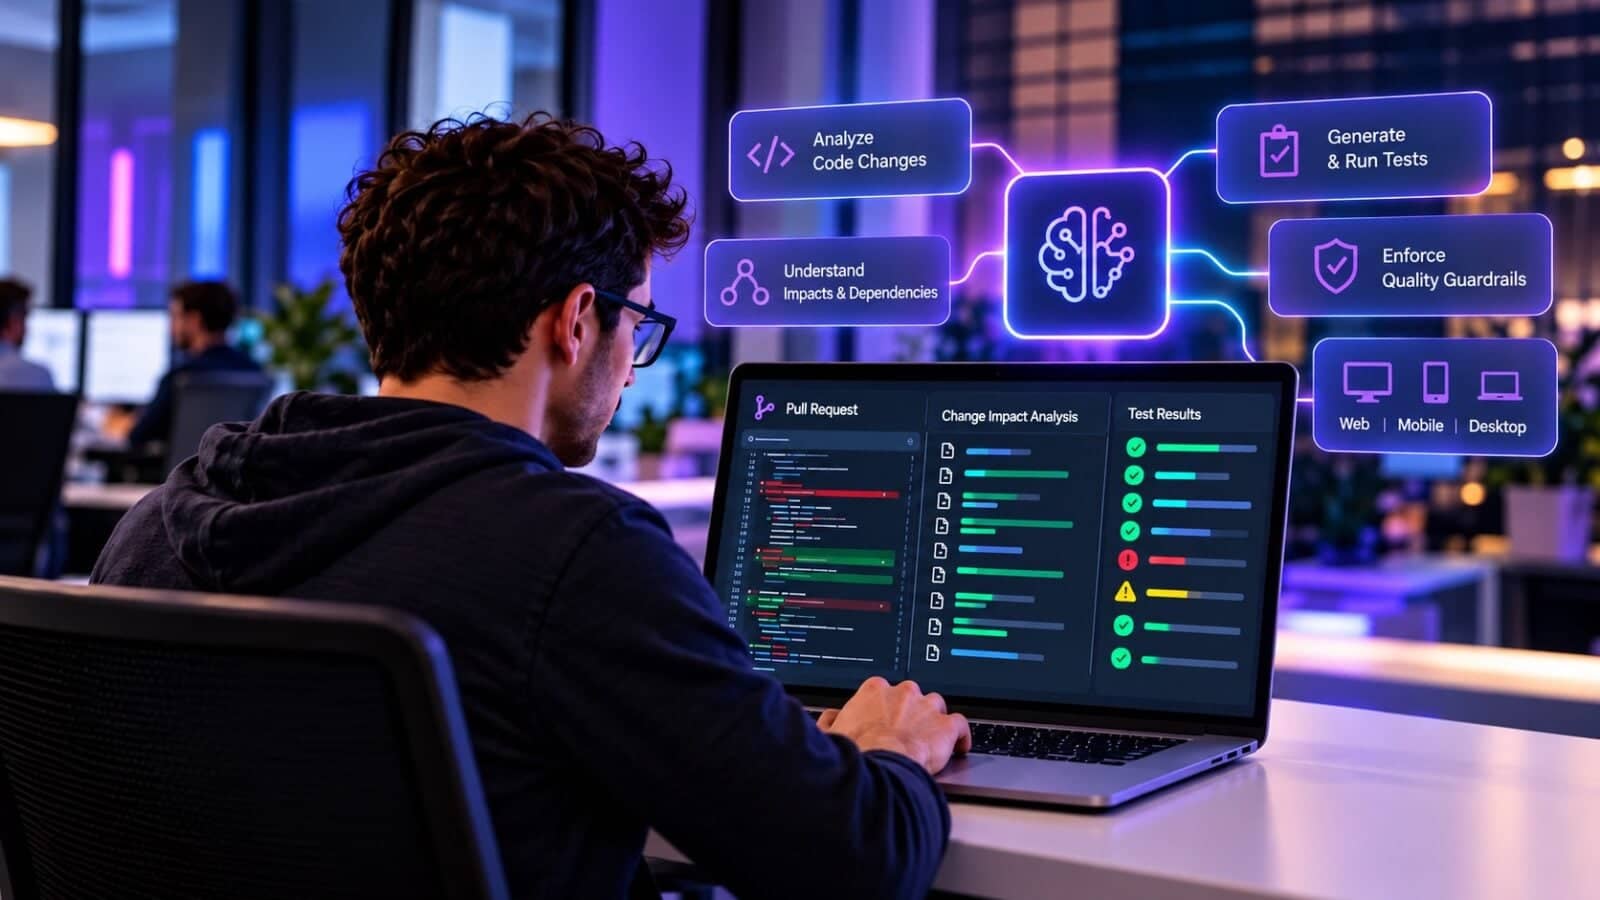
mabl Adds Harness to AI Testing Automation Platform
Mabl today extended its test automation platform with a harness that, in addition to enforcing guardrails and testing standards for artificial intelligence (AI) agents, enables application development teams to better understand the impact of code changes before a pull request (PR) is made. Announced at a mabl Experience event, the extensions to the test automation […]
Coding Agents Moved the Bottleneck From Writing to Reviewing PRs
AI coding agents are generating more pull requests than developers can review. Learn why review bottlenecks create quality debt and how DevOps teams can respond.
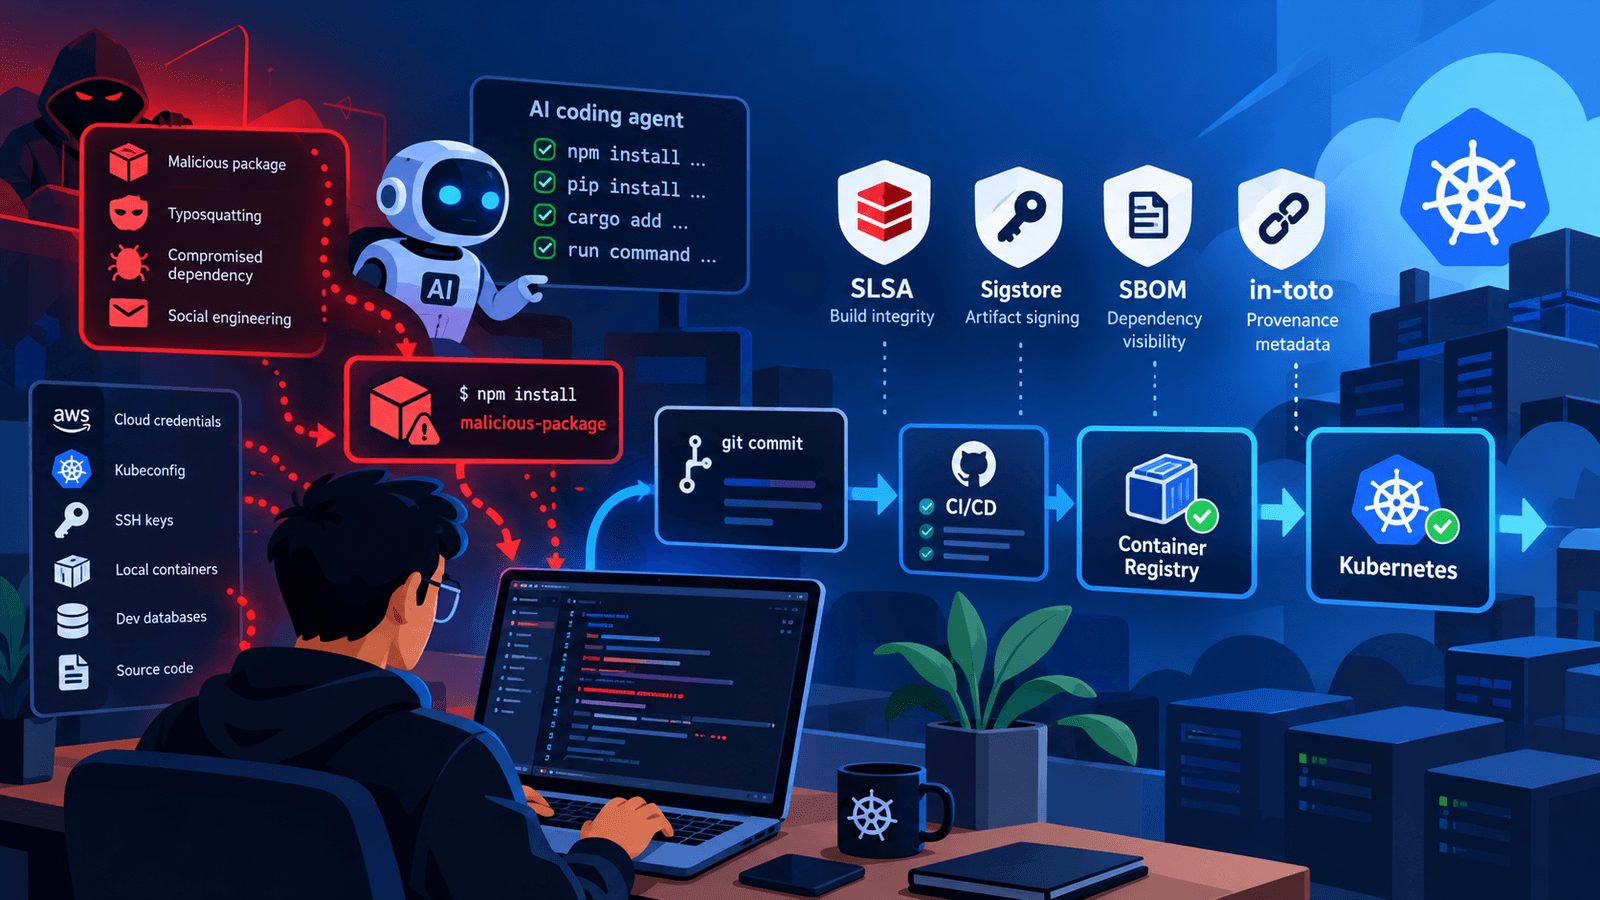
Beyond SLSA and Sigstore: Securing the Developer Origin in the Age of Agentic Coding
SLSA, Sigstore and SBOMs have strengthened software supply chain security, but attackers are increasingly targeting developer workstations before code reaches the CI/CD pipeline. With autonomous AI coding agents installing dependencies, executing commands and accessing sensitive credentials, endpoint security is becoming a critical cloud-native concern. Securing the software supply chain now requires protection from the developer’s IDE all the way to Kubernetes production workloads.
AI Agents Can Now Take Software Apart. DevOps Teams Need a Plan
AI-powered reverse engineering is making it easier to understand and rebuild software without source code. Tools such as REA and increasingly capable AI models create opportunities for legacy modernization while raising fresh concerns about intellectual property, application security and functional correctness.
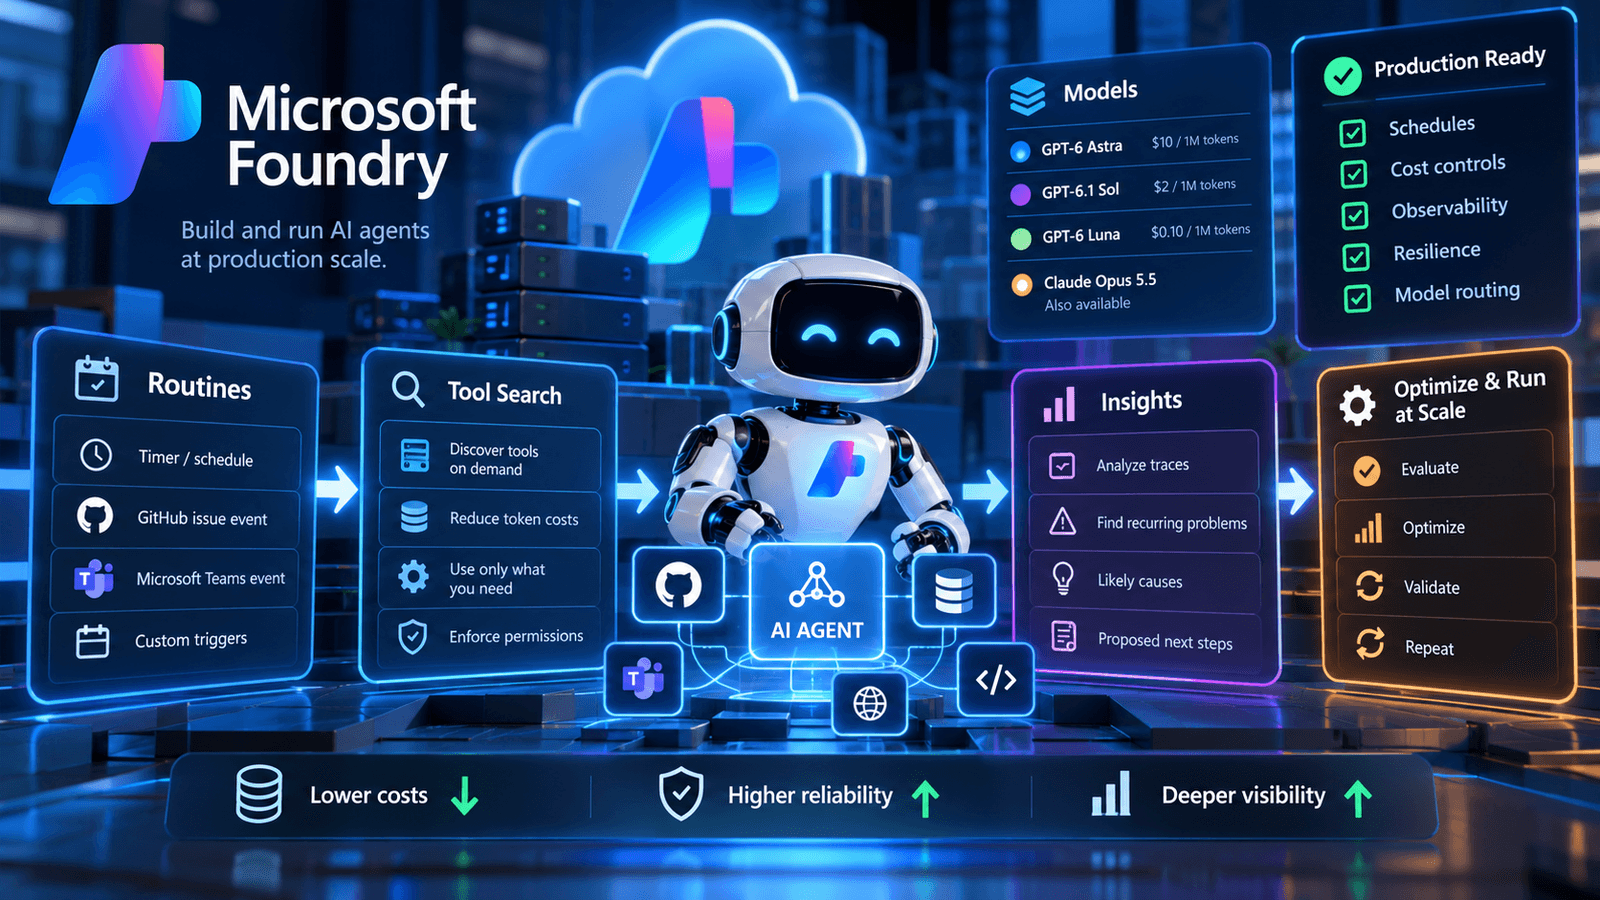
Microsoft Foundry Puts AI Agents on a Schedule and Under Watch
Microsoft’s September Foundry updates focus on making AI agents production-ready with automated routines, lower token costs, trace-based insights and improved resilience. For DevOps teams, the changes bring agent operations closer to familiar CI/CD and observability practices.
GitHub Brings AI Security Scanning to Pull Requests CodeQL Can’t Cover
GitHub’s AI Scan brings AI-powered vulnerability detection to pull requests involving languages, scripts and infrastructure files beyond CodeQL’s existing coverage. Paired with the general availability of agentic autofix, the release expands security automation across the development lifecycle. But advisory-only findings, coverage gaps and AI credit consumption mean DevOps teams still need clear review policies.

Cohere Plans to Acquire Aisle to Add AI-Powered Code Security
Enterprise AI platform provider Cohere announced it has signed a letter of intent to acquire Aisle, a cybersecurity startup whose AI agent platform discovers source-code vulnerabilities and generates proposed fixes. The proposed acquisition would also establish a dedicated cybersecurity business called Cohere Cyber. Aisle’s platform analyzes software for previously unknown vulnerabilities, validates potential findings, evaluates […]
Chainguard Debuts a Security-First Agent Platform
Open source security company Chainguard has released Workspaces, a service designed to provide a safe space for agents to do their thing without disrupting the security of existing operations. The market for platforms to host agents is large and growing daily, though Chainguard’s expertise in security solves a major problem with running agents, namely managing […]
OpenCode Breach Puts Spotlight on AI Distillation Threats
An attack using the technique on the open source coding agent’s Console hub exposed third party API keys from OpenAI, Anthropic, and Google
Blitzy Adds Chat-to-Prompt Interface to Agentic AI Engineering Platform
Blitzy this week added a chat interface to a platform that enables DevOps teams to employ artificial intelligence (AI) agents by expressing their intent in natural language. Dr. Neeraj Deshmukh, Field CTO for Blitzy, said the Chat to Prompt interface makes it possible for a software engineer to describe a desired outcome that is then […]
ScienceLogic Extends Observability Reach and Control Deeper into AI Agents
ScienceLogic has added additional tools and capabilities to its observability platform that provide deeper visibility and control over artificial intelligence (AI) agents that are being used to automate IT operations. The latest 2.7 update to the Skylar AI platform provides visibility into agent routing and tool selection via a catalog that uses traces to surface […]
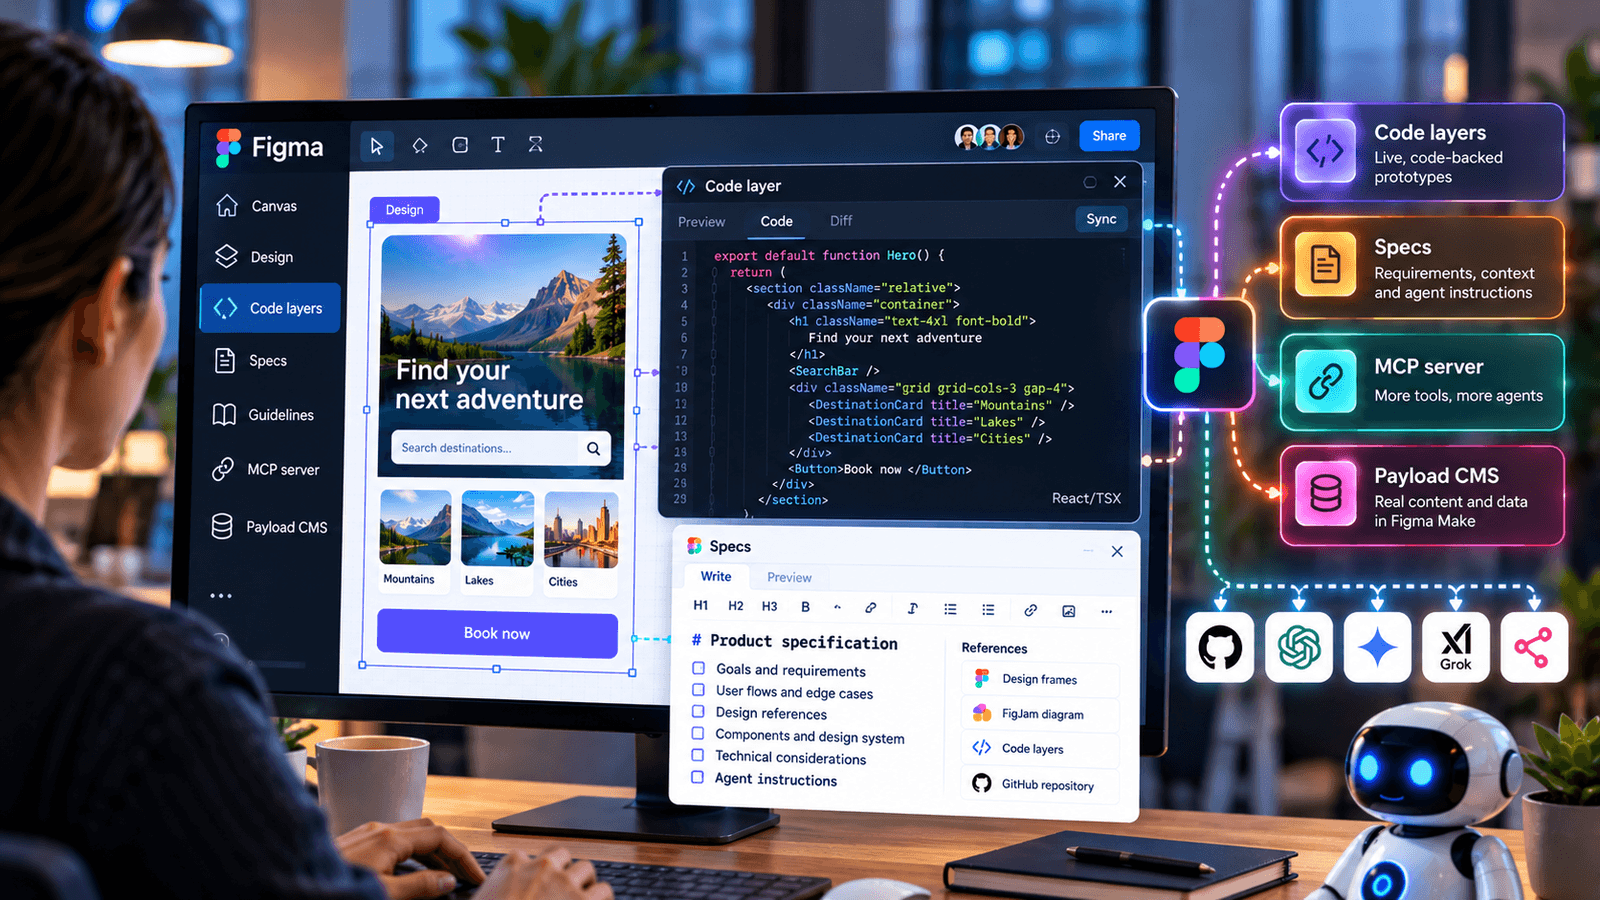
Figma Gives AI Agents a Spec Sheet and Developers a Shared Canvas
Figma introduces Specs, code layers and expanded MCP tools to connect AI agents, designers and developers while improving design-to-code workflows.