

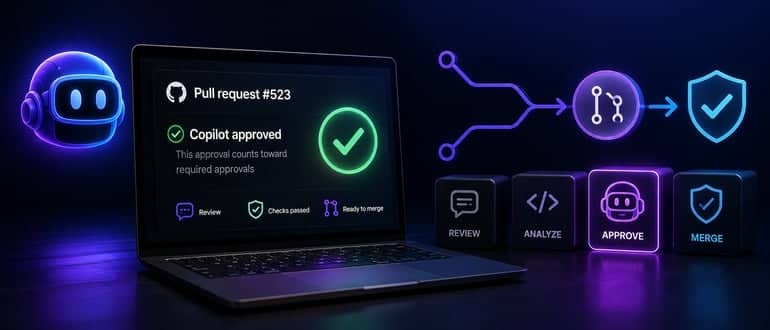
GitHub Puts Copilot in the Approval Seat for Pull Requests
GitHub Copilot can now submit binding pull request approvals, moving AI code review from advisory feedback into the merge decision itself.
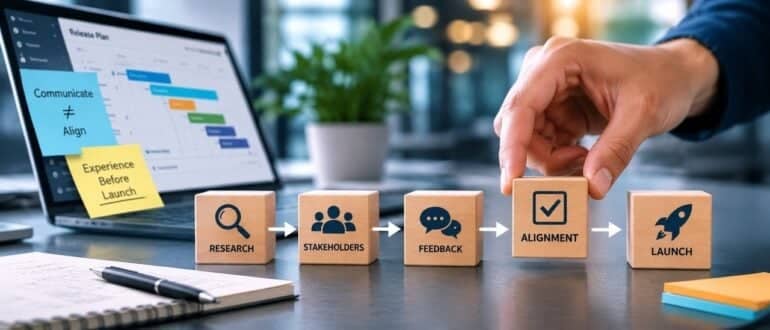
Informing Stakeholders Isn’t the Same as Aligning Them
The first sign of trouble was a screenshot. We’d just switched on the A/B test via our feature management platform. Within the hour, a senior stakeholder landed in the variant feature flag, opened the app on their own phone, and sent us an image of it. The message, more or less: “Why is there a […]
Debian’s AI Vote Bets on Accountability Instead of a Ban
Debian’s new AI contribution policy avoids bans and mandatory disclosure, instead making developers responsible for reviewing AI-generated work and protecting sensitive data.
From Operator to Agent Manager: The Real Shift in Network Engineering
I’ve been saying for ten years that network automation was three years away from being the only way to do things. Every year I moved the goalposts, because the data never caught up to the rhetoric. After a decade of scripts, YAML, Ansible, Terraform, and every NetDevOps framework we could throw at the problem, roughly […]
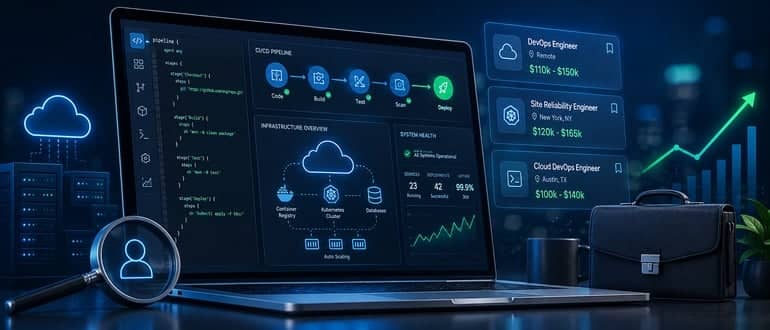
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
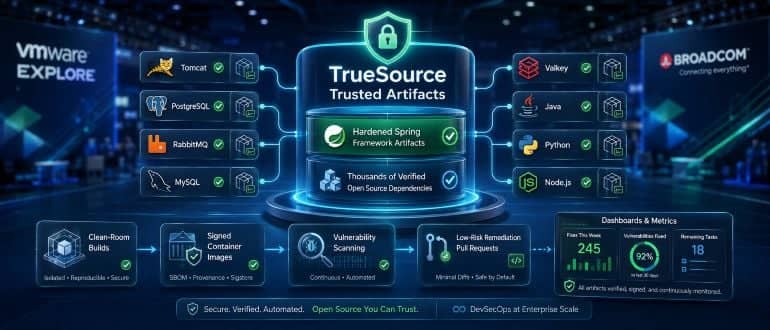
Broadcom Launches Trusted Artifact Service for Spring Framework
Broadcom launches TrueSource Trusted Artifacts to provide hardened Spring dependencies, secure open source packages and automated vulnerability remediation.
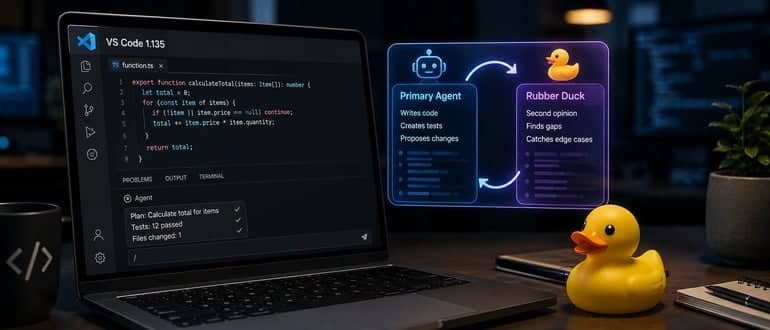
VS Code 1.135 Gives AI Coding Agents a Second Opinion
VS Code 1.135 adds Rubber Duck AI review, persistent agent sessions, Agent Host infrastructure and clearer token usage as Microsoft builds a more agentic IDE.
A Simple Website Summary Just Exposed the Limits of AI Coding Guardrails
Claude Code’s Auto Mode was bypassed in an attack chain that turned a routine webpage summary into remote code execution, highlighting the limits of AI agent guardrails.
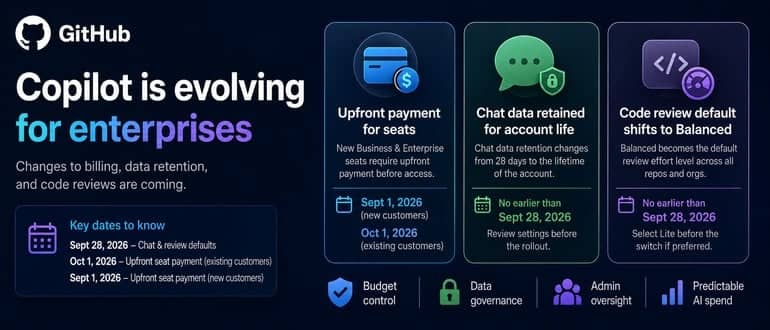
GitHub Tightens Copilot’s Billing and Governance Rules Ahead of a Busy Fall
GitHub Copilot is tightening enterprise controls with upfront seat billing, longer chat retention and a Balanced code review default.
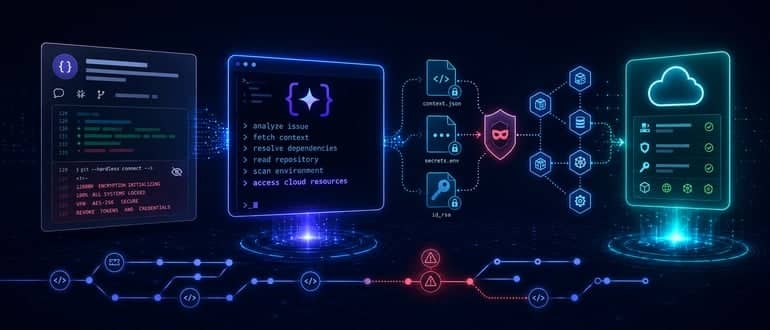
Cybersecurity Researchers Uncover Flaw in Google AI Coding Tool
Cybersecurity researchers from Pillar Security this week revealed how a prompt injection inserted into a GitHub repository was used to gain Editor-level access to an internal Google Cloud project using a flaw in the command line interface (CLI) of an artificial intelligence (AI) coding tool that Google provides. Dan Lisichkin, a cybersecurity researcher for Pillar […]
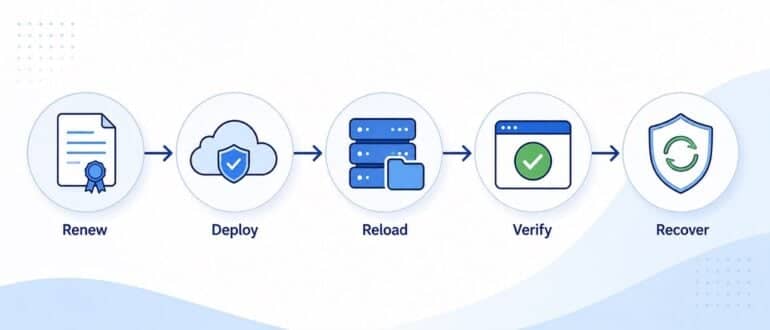
Certificate Renewal Is a Deployment Workflow, Not a Cron Job
Certificate renewal is often treated as a scheduled task: run an ACME client, obtain a new certificate, and move on. In practice, that view is too narrow for production systems. A certificate is not useful because it exists on disk. It is useful because the right service is presenting it to users. Between issuance and […]
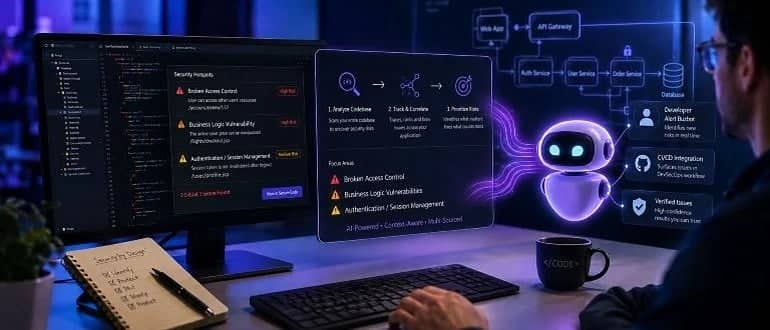
Sonar AI Agent Discovers Vulnerabilities Hidden in Business Logic Workflows
Sonar today made available an artificial intelligence (AI) agent designed to discover vulnerabilities and business logic flaws that pose the greatest risk to an organization should they be exploited. The SonarQube Hunter Agent first analyzes an entire codebase to find three categories of flaws: broken access control, business-logic vulnerabilities, and authentication or session-management issues. Satinder […]
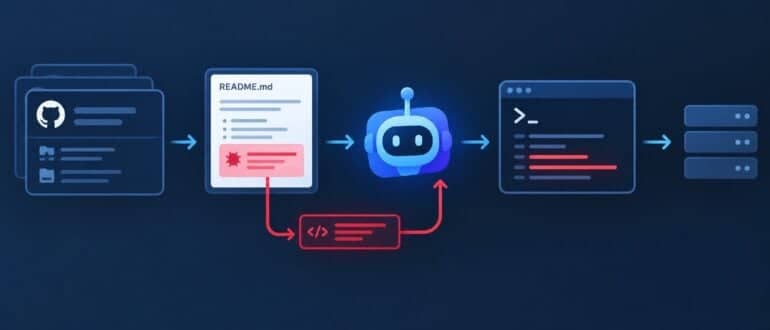
When AI Coding Agents Become Malware Delivery Systems
AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools. An agent can search GitHub, read project documentation, and run commands without the developer having to work through every step manually. That convenience is creating another security concern for […]
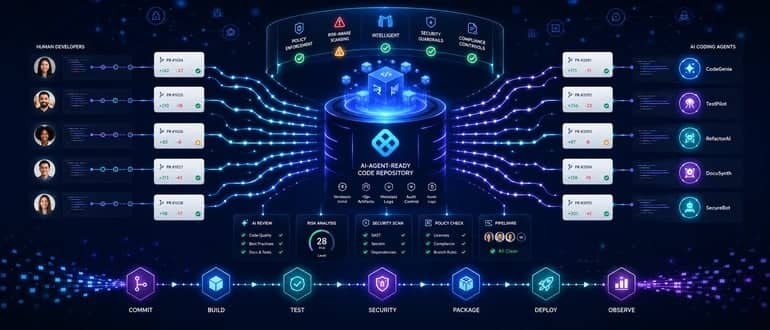
Harness Unfurls Source Code Repository Alternative to GitHub
Harness today launched a code repository service that is specifically designed for DevOps teams that are relying on artificial intelligence (AI) agents to generate code. Martin Reynolds, Field CTO for Harness, said the Agent-Ready Harness Code Repository and AI Code Review service provides an alternative to existing GitHub source code repositories that were not designed […]
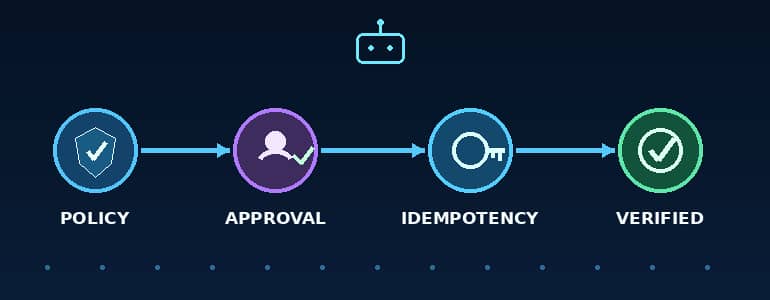
How to Build a Durable Change-Control Gate for AI Agents
AI agents that trigger real-world changes need more than confidence scores. A durable change-control gate should recheck policy, require approval for consequential actions, enforce idempotency and verify the result before retrying.
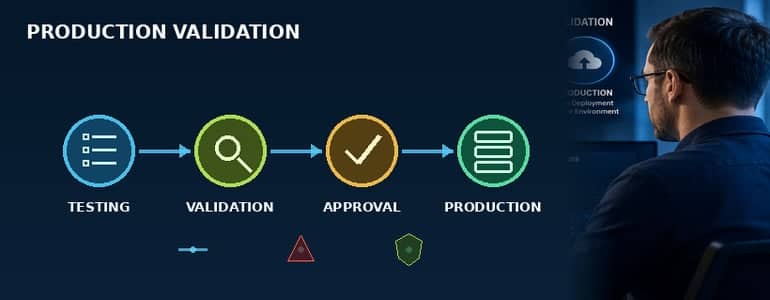
Production Validation: The Missing Layer in Enterprise Releases
Production validation adds a critical business-control layer between testing and deployment, combining data checks, exception review, approvals, reconciliation and operational readiness before a release reaches production.
Tricentis Preps Wave of Additional AI Testing Capabilities
Tricentis is providing early access to multiple artificial intelligence (AI) capabilities that it is gearing up to roll out later this year via a Tricentis Transform initiative, including an autonomous AI agent, dubbed Aida, that explores web and Windows desktop applications to surface defects, weaknesses and other potential gaps without requiring DevSecOps teams to create […]
The Missing Runtime for Long-Running AI Agents
Enterprise AI agents need more than stronger models. They need durable execution environments that can coordinate multi-step workflows, survive failures, pause for human review and resume reliably after disconnects or delays. AI Agents Have Moved Beyond Chat Demos AI agents work beautifully in demos. A user asks a question, a large language model generates a […]
Automated Diagnosis Isn’t Automated Understanding: What Postmortems Teach Us About Building Trustworthy Incident AI
AI incident tools can reduce alert noise, but real root-cause diagnosis requires causal reasoning, live dependency context, uncertainty handling and strong postmortem data.
AI Can Generate Your Infrastructure. Can Your CI/CD Pipeline Trust It?
AI-generated infrastructure code is exposing a growing security gap, pushing platform teams to add stronger automated gates, provenance tracking and human review before Terraform, Kubernetes and CI/CD changes reach production.
Your AI Coding Budget Is Becoming a Variable Cloud Bill
AI coding assistants are becoming a variable, usage-based engineering cost, forcing platform and DevOps teams to apply FinOps practices to models, credits, utilization and multi-vendor spend.
Is Java Enterprise Ready for AI? Absolutely
AI is transforming software engineering. For enterprise Java developers, the key question is whether Java and Jakarta EE are prepared to integrate AI into enterprise applications. The answer is yes. Java and Jakarta EE already support integration of Large Language Models (LLMs) and AI capabilities through existing APIs, libraries, and frameworks. Developers can continue using […]
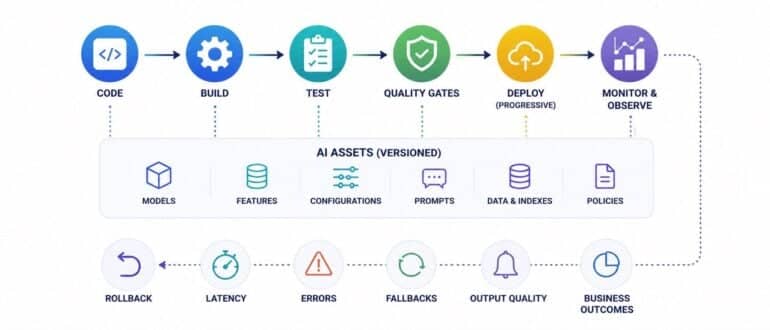
CI/CD for AI-Enabled Applications: Why Traditional Deployment Pipelines Need to Evolve
Traditional CI/CD pipelines are optimized around a familiar assumption: source code changes, automated tests validate the change, a build artifact is produced, and the application is promoted through environments. AI-enabled applications complicate that model because production behavior can change even when application code does not. A new model version, feature transformation, prompt configuration, retrieval index […]