

Report Shines Spotlight on 91 Vulnerabilities Fixed in Latest Update to Spring Framework
Sonatype says 91 Spring vulnerabilities affecting more than 209,000 software components highlight how AI is accelerating vulnerability discovery and creating a new patching challenge for DevSecOps teams.
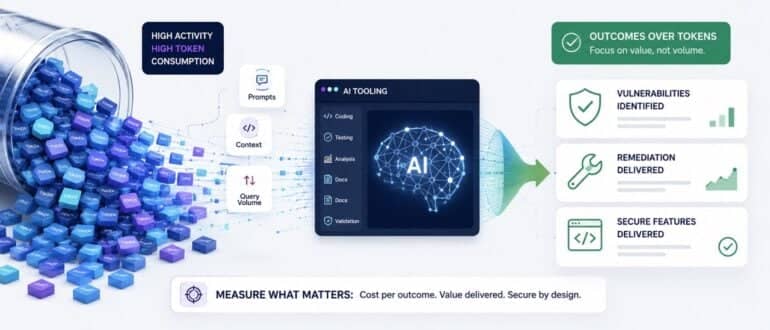
Why “Tokenmaxxing” Was Always the Wrong Way for Developers to Measure AI Productivity
The term “tokenmaxxing” left the developer lexicon just as quickly as it arrived, and like most viral technology concepts, it means different things depending on who’s using it. In practice, the term is being applied in two ways: maximizing total token consumption as a proxy for AI adoption and effort, or optimizing output per token […]
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
Beyond Log Search: What We Learned Building a RAG-Based Incident Diagnosis System
A RAG-based AIOps framework can cut incident diagnosis time by grounding LLM reasoning in real runbooks, tickets and postmortems, improving root-cause accuracy while giving SREs source-backed answers they can trust
Scalable Jenkins Management: Empowering Enterprises With Centralized Control for 150+ Instances
A centralized Jenkins control plane can reduce fleet sprawl, automate upgrades and backups, improve observability, and give application teams safe self-service across large multi-cloud CI/CD estates.
Preparing Infrastructure for the Next Phase of Agentic AI
Agentic AI is changing government infrastructure requirements, pushing agencies to rethink workflows, observability, data movement and resource prioritization before investing in new hardware.
Dash0 Acquires Polar Signals for Continuous Profiling and GPU Visibility
Observability startup Dash0 announced this week that it acquired Berlin-based continuous profiling specialist Polar Signals. The deal adds continuous profiling to SignalStore, Dash0’s OpenTelemetry-native data platform. Continuous profiling has been part of the developer toolbox for years and provides teams with an ongoing view of where running applications spend CPU time, allocate memory and consume […]
Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
Security researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more attacker-owned crates. In addition, researchers with Wiz wrote that there also appears to be overlap with supply chain campaigns run by nation-state actors […]
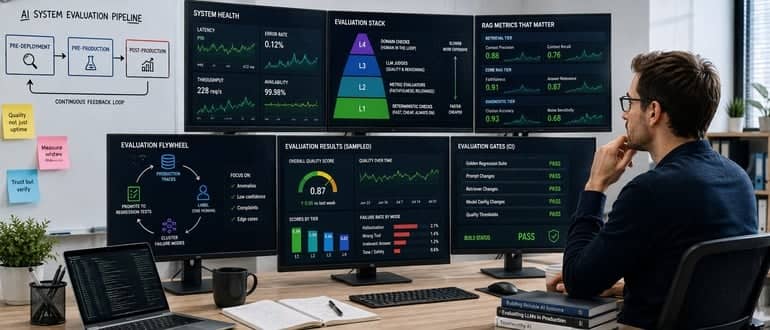
Production-Grade AI Eval Systems. What I Learned Putting LLMs on Call
Production-grade AI reliability requires more than uptime and latency. A layered eval system helps teams detect hallucinations, RAG failures and quality regressions before customers do.
Waterfall 2.0: Controlling LLM-Driven Software Development with Stage-Gated Discipline
Waterfall 2.0 reimagines classic stage-gated software development for the LLM era, combining fast AI generation with structured validation, cheap backtracking and a shared knowledge corpus.
Why API Test Generation Is a Judgment Problem, Not a Code Generation Problem
When we started using large language models for API test generation at KushoAI, the results were impressive on the surface. Tests appeared in seconds. Coverage breadth went up. The team was excited. Then we looked more carefully at what was being produced. On one endpoint, the model generated 26 tests where a senior QA engineer […]
Why Cryptographic Inventory Is the First Step Toward Quantum Readiness
Post-quantum readiness starts with visibility. DevOps teams need a continuous cryptographic inventory to map algorithms, keys, certificates, libraries, infrastructure and third-party dependencies before PQC migration begins.
npm v12 Shuts Down a Popular Malware Trick — But the Threat Isn’t Going Away
For years, one of the easiest ways to sneak malware onto a developer’s machine has been to hide in plain sight. Install a package from npm, and any lifecycle script bundled with it runs automatically — no review, no approval, no second look. Attackers have known this for a long time, and they’ve used it […]
AI Agents Are Writing Code Faster Than Anyone Can Review It. Tessl Is Betting On Standards To Close That Gap
Every team that has turned coding agents loose on real work has run into the same wall. The agents write fast. They write a lot. And somewhere between the tenth and twentieth pull request of the day, the humans responsible for reviewing that code start falling behind. That’s not a hypothetical. It’s the operating reality […]
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets developers whitelist particular built-in Node modules or limit what the script can access. During that time, vm2 has been the default for safely […]
GitHub Sharpens CodeQL’s Eye on Actions Workflows and Modern JavaScript
GitHub Actions pipelines have become one of the quieter attack surfaces in software development. They pull in third-party actions, cache dependencies, and pass secrets between jobs, often without anyone reviewing the workflow file as closely as they’d review application code. That gap is exactly where cache-poisoning and output-clobbering attacks live, and it’s why GitHub keeps […]
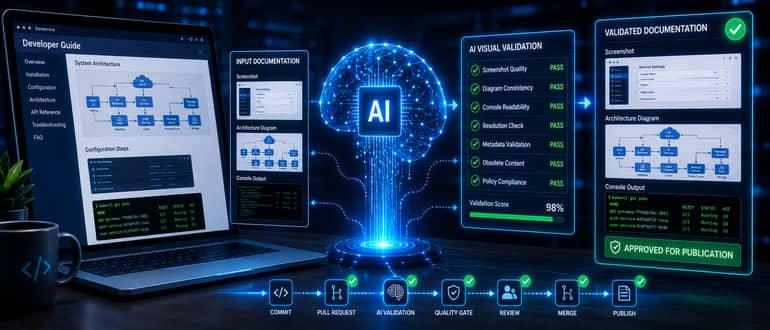
Elevating Technical Documentation: Using Predictive AI to Standardize Visual Knowledge Bases
Every release changes documentation alongside the code. Developers depend on that documentation during implementation, maintenance and troubleshooting. A diagram becomes misleading once services are renamed or integrations change without a corresponding documentation update. Keeping documentation updated becomes increasingly difficult as repositories, products and release cycles grow. Outdated or inconsistent images eventually find their way into […]
How to Avoid Repeating the “Automate Everything” Mistake Due to AI FOMO
The DevOps community has already experienced technological extremes. You might recall the time when automation was thought of as a panacea for all possible engineering issues, and the slogan “Automate Everything” was ringing out everywhere. Over time, the industry came to an important conclusion: Automation should not become the end goal. Along with faster software […]
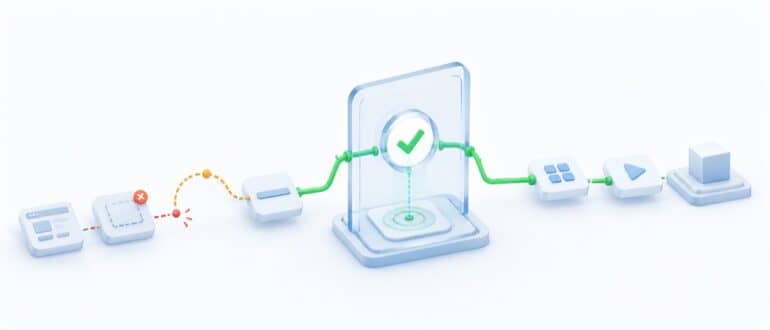
Why Self-Healing Tests Need a Deployment Gate
When an end-to-end test fails after a front-end change, the repair often looks routine. A class name changed. A button moved. A selector that used to be unique now matches two elements. A self-healing system inspects the page, proposes a new locator, reruns the test, and gets a green result. That green result is useful, […]
Cursor Launches Origin Code Hosting Platform as GitHub Rival
AI coding provider Cursor has launched Origin, a code hosting platform that puts source code and AI coding agents inside the Cursor development environment. The new coding platform expands the company into a market long dominated by GitHub. The rollout arrived as GitHub suffered a major outage lasting more than six hours, disrupting pull requests, […]
LangChain’s dcode Isn’t New. Its Governance Play for Sensitive Code Is
Enterprises are running into the same wall with AI coding agents: the tools that write code fastest are usually the ones IT trusts least with sensitive codebases. Legacy modernization projects — COBOL migrations, .NET upgrades, decade-old frameworks nobody wants to touch by hand — are exactly where agentic coding tools could help most, and exactly […]
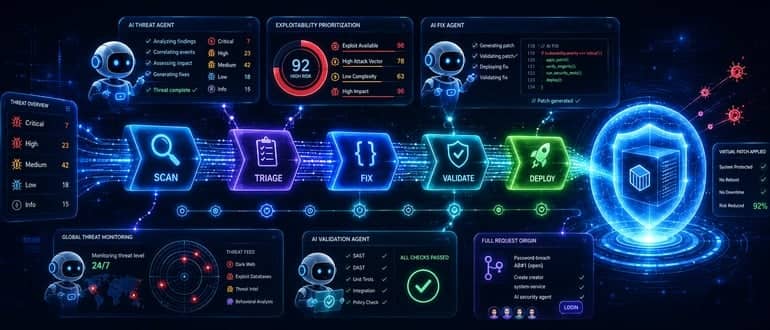
Harness Adds AI Agents to Automate DevSecOps Workflows at Machine Speed
Harness today added multiple artificial intelligence (AI) agents and a virtual patching capability to its portfolio to automate DevSecOps workflows at a time when the number of vulnerabilities being discovered in code continues to exponentially increase. The AI agents include one that has been added to the static application security testing (SAST) tool that Harness […]
Claude Code’s Temporary Usage Boost Expires Tonight. Here’s What Actually Changes
Anthropic’s temporary 50% increase to Claude Code weekly usage limits expires August 19, reducing available capacity for developers and DevOps teams without lowering subscription prices.