

Are LLMs Equally Good (or Bad) at Building Secure Software?
An SCW study finds a large variance in how frontier and budget LLMs perform across different frameworks, and explains the striking cost variance.
What the Microservices Era Can Teach Us About AI
AI agents are not just microservices with LLMs attached. Their long-running, non-deterministic workflows demand durable execution, per-step identity, governance and observability.
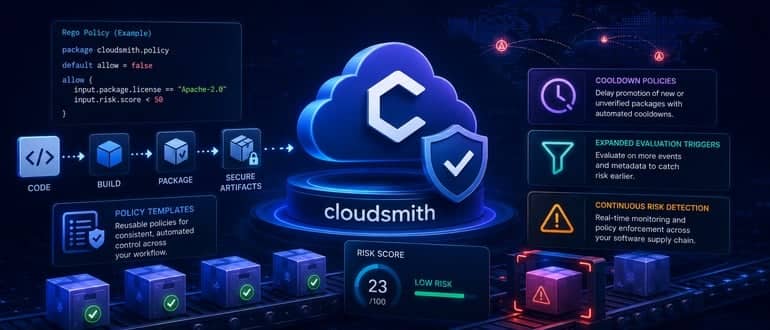
Cloudsmith Extends Policies and Controls to Secure Application Binaries
Cloudsmith this week revealed it has expanded the policy management and continuous risk detection capabilities it makes available within its software artifact management platform to now include policy templates, cooldown policies, and expanded evaluation triggers. Alison Sickelka, vice president of product for Cloudsmith, said these additions to the platform will make it simpler to prevent […]
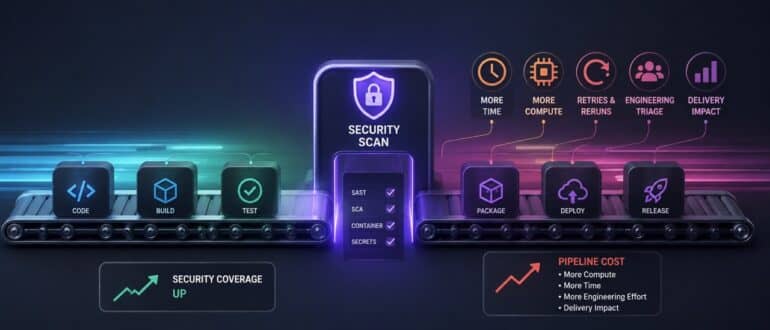
Is Your New DevSecOps Tooling Reducing Work Or Just Adding to It?
Security belongs in the software delivery pipeline. The harder question is where, how often and at what cost. Many pipeline teams eventually add security scanning to CI/CD, and relatively few go back afterward to measure what it actually cost the delivery process. Security coverage went up. Something else changed too, and it is rarely measured […]
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
Dynatrace Acquires Arize as AI Agents Deepen the Observability Challenge
Dynatrace announced Thursday it has agreed to acquire AI observability company Arize in a $915 million cash and stock transaction. Rick McConnell, CEO of Dynatrace, said the company expects demand for AI observability will keep growing as more AI systems move into production. He said acquiring Arize would speed up Dynatrace’s roadmap, expand its developer […]
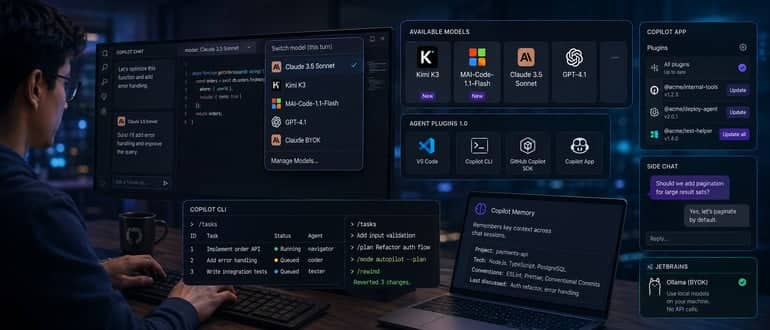
GitHub Copilot’s Latest Update Bets on Model Choice, Not Model Loyalty
GitHub’s latest Copilot updates add Kimi K3, MAI-Code-1.1-Flash, Agent Plugins 1.0, model switching, CLI improvements, and local Ollama support.
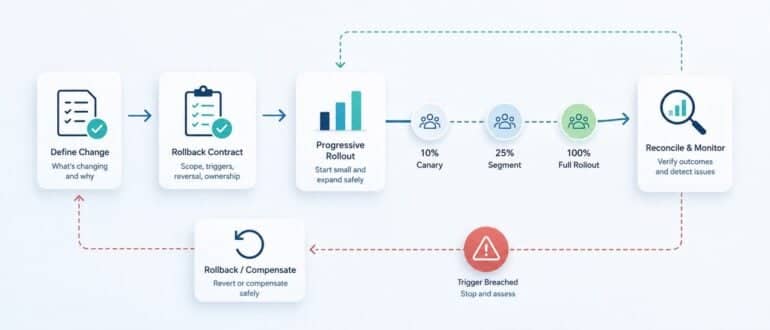
Treat Business Workflow Changes Like Deployments
Business automation often reaches production without the release discipline applied to application code. A routing rule changes, an approval threshold moves, or an integration starts writing to a new system. The edit may happen in a visual builder instead of a repository, but its blast radius is still real: orders can duplicate, customers can receive […]
Microsoft Decouples AI Agents From the VS Code Editor in Latest Release
Microsoft has shipped Visual Studio Code 1.133, and the headline change is architectural rather than cosmetic: AI agent sessions now run in a dedicated background process rather than within the editor’s extension host. The release, which rolled out August 12, moves agent execution into what Microsoft calls the Agent Host, a standalone process built on […]
Developer Resistance to AI Isn’t Fear – It is Identity
Developer resistance to AI is less about job loss than a deeper shift from hands-on coding to supervising, validating and orchestrating AI-generated work.
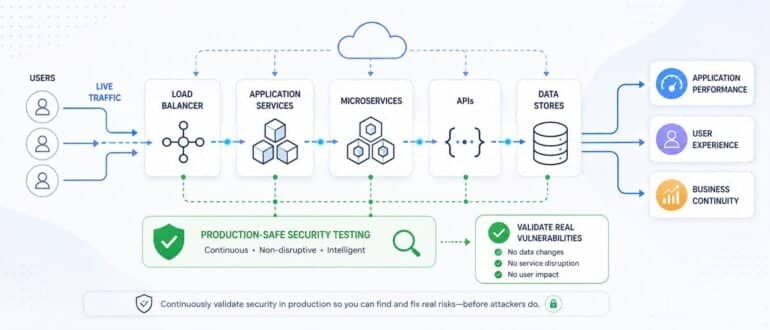
Production-Safe Testing: The Missing Piece in Most DevSecOps Strategies
Most DevSecOps teams invest heavily in security before deployment, yet attackers target the production environment where applications, APIs, and user behavior are constantly changing. If security validation stops before release, critical risks can remain hidden until they are exploited. The gap is more common than many organizations realize. A survey found that over 70% of […]
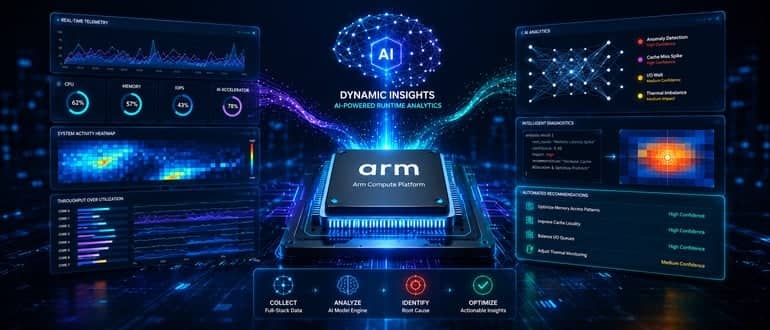
Arm Adds AI Tool to Optimize Workloads Using Runtime Data
Arm has made available a Dynamic Insights tool that leverages artificial intelligence (AI) models to generate recommendations for optimizing software running on its processors using actual data collected at runtime. Alex Spinelli, senior vice president for AI and developer platforms at Arm, said the Dynamic Insights tool provides both human developers and AI agents with […]
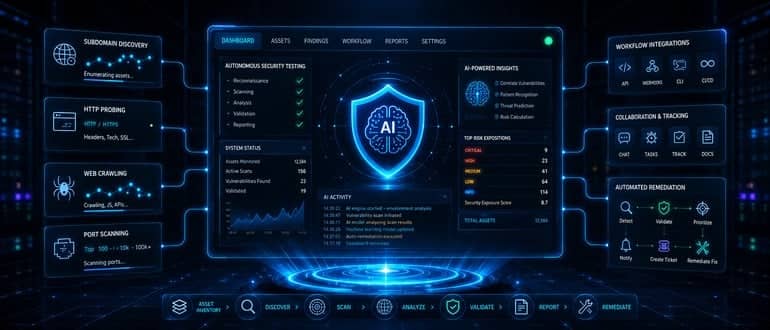
ProjectDiscovery Brings Open Source AI Testing to Vulnerability Discovery
ProjectDiscovery has made available an autonomous security testing platform that leverages an open source artificial intelligence (AI) testing framework to detect and validate vulnerabilities at a lower total cost. Company CEO Rishi Sharma said version 1.0 of the Neo platform is also available via a cloud service that makes it possible for DevSecOps teams to […]
Reflex’s Newly Open-Sourced XY Library Offers Faster Python Charting
A newly open-sourced Python charting library, called XY, from Reflex offers an advantage few other charting tools provide: massive scalability. The library rethinks how to render a set of points on the computer screen, and opens new possibilities for using charts in daily workflows. Most Python charting libraries today, such as Plotly, Bokeh, or Matplotlib, […]
Reducing MTTR: A Practical Guide to Correlating Incidents with AIOps
AI-driven incident correlation helps SRE and DevOps teams reduce alert noise, identify root causes faster and improve MTTR by connecting related metrics, logs and traces.
Developer’s Checklist: How to Build an FHE Application
A practical guide to building fully homomorphic encryption applications, covering architecture, noise budgets, polynomial approximations, parameter choices, SIMD packing, testing and performance optimization.
The Agent Proposes, the Pipeline Disposes: Controls for AI-Authored Change
When agents write code and open pull requests faster than humans can read them, ‘the diff looked fine’ stops being a control. The durable controls live outside the agent’s reasoning loop.
What You Cannot See Will Break Your LLM App: A Practitioner Guide to Production Observability
Traditional application observability was built around a simple mental model: Your code runs, metrics come out and when something breaks, the logs tell you why. Large language models (LLMs) break that model in ways that are not obvious until you have shipped one and watched it misbehave in production. An LLM-powered application can be up, […]
Software Deployment Strategies for Enterprise Teams: A Scenario-Based Guide to Choosing the Right Approach
Choosing the right software deployment strategy depends on the scenario. Get a practical decision framework for enterprise teams.
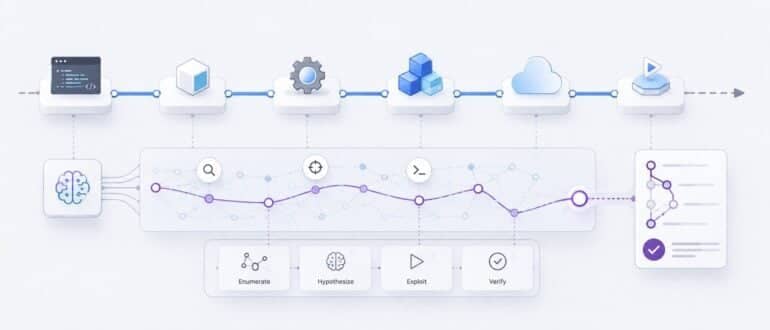
Why CI/CD Security Testing Is Going Autonomous (and Why It Should Stay Local)
Continuous integration and delivery changed the tempo of software. Teams merge dozens of times a day, infrastructure is redefined on every commit, and a new build can reach production in minutes. Security testing never caught up with that tempo. It still lives in two modes that both fight the pipeline instead of moving with it. […]
LiteLLM Attack Affected 2,500 Companies, 434,000 CI/CD Pipelines: CloudSEK
The massive supply-chain attack that compromised LiteLLM in the spring affected more than 2,500 companies and exposed about 434,000 CI/CD pipelines, with victims ranging from top-tier IT and AI companies to cybersecurity firms, SaaS, and enterprises. It rolled up a lot of victims, but also was a high-profile example of the growing trend of threat […]
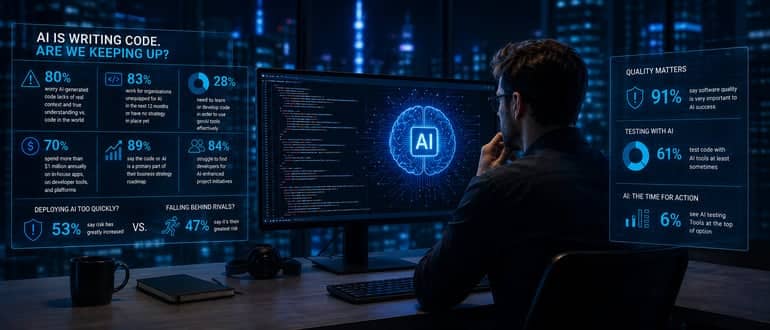
Survey Surfaces Rising Tide of Production Issues Traced Back to AI Code
A survey of 400 business and engineering executives finds 80% have traced a production incident, outage, or customer-impacting defect to code generated by artificial intelligence (AI) tools in the past 12 months. Conducted by Wakefield Research on behalf of Sauce Labs, a provider of an application testing platform, the survey finds 83% of respondents work […]
How Test Management Tools Give Engineering Teams the Visibility They Need to Ship With Confidence
Test management tools do more than track results. Learn how they give engineering teams the coverage visibility needed to ship with confidence.