

env zero Previews Control Plane for Agentic DevOps Workflows
env zero’s EZ Control introduces an agentic DevOps control plane that detects infrastructure drift, applies policy-driven remediation and keeps automated changes attributable, reversible and auditable.
Docker Introduces Open Sandbox Kit Spec for AI Agent Permissions
AI agents are getting good at probing the boundaries developers put around them. Their ability to improvise makes them hard to contain. “You ask for something in a very high-level, vague-at-best way. You walk away, and you come back to a remarkable pile of mostly working software. But you then realize that you gave a […]
Survey: Lack of Confidence in Software Supply Chain Security Runs High
A survey of 400 platform and security engineers in the U.S and United Kingdom (UK), finds nearly three quarters (73%) are either only moderately confident (58%) or not confident (15%) in the ability of their existing tools for managing software artifacts to prevent attacks against their organization’s software supply chain. Conducted by Cloudsmith, a provider […]
DHH Declares End of Hand-Writing Code at Rails World 2026
Controversial developer David Heinemeier Hansson (aka DHH) announced last week at Rails World 2026 that the end of handwritten code is upon us, calling it the modern era’s “Brownie” moment. The moment to which he referred was when Kodak released its Brownie camera that forever changed the trajectory of photography. In this case, the Brownie […]
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]
GitHub’s Security Autofix Agent Now Remembers What It Fixed
GitHub’s agentic autofix now uses Copilot Memory to reuse repository-specific security fix patterns, helping Copilot apply lessons from past vulnerabilities across future alerts, reviews and coding workflows.
Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner. Aikido Security researcher Joe Leon detailed the attack path this week in a blog post after reporting it to GitLab earlier this year. […]
Blitzy Makes Sandbox for Reverse Engineering Code Available at No Cost
Blitzy has made available a sandbox where DevOps teams can reverse-engineer up to one million lines of code, generate up to 25,000 lines of tested end-to-end code, and identify security vulnerabilities across a codebase at no cost. Dan Ochs, director of AI solutions consulting for Blitzy, said the provider’s Proactive Insights platform uses multiple artificial […]
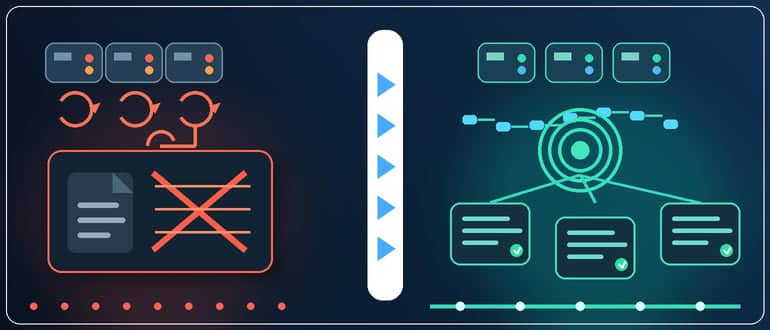
Dependency Mocking Approach That Gets More Accurate as Your Services Deploy More Often
Traffic-based dependency mocking turns frequent upstream deployments into opportunities to refresh mocks from real behavior and reduce integration test drift.
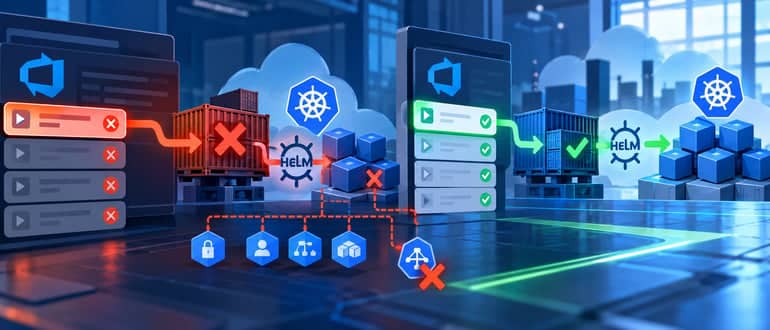
Why Old Azure DevOps Releases Survive a Pipeline Cutover
Old Azure DevOps Classic releases can retain retired deployment tasks, Helm names, image paths and variables long after a pipeline cutover, leaving stale redeploy paths active.
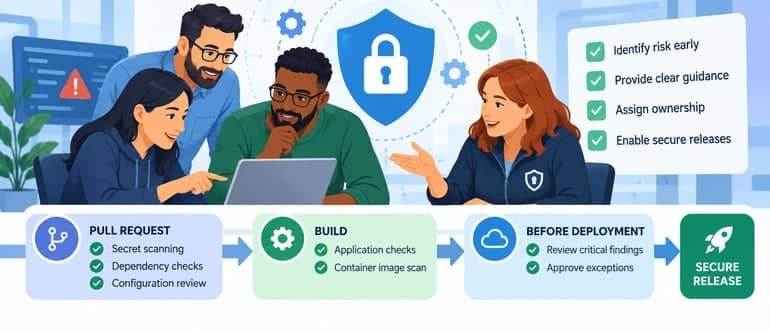
DevSecOps Teams as Partners in Secure Software Delivery
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable.
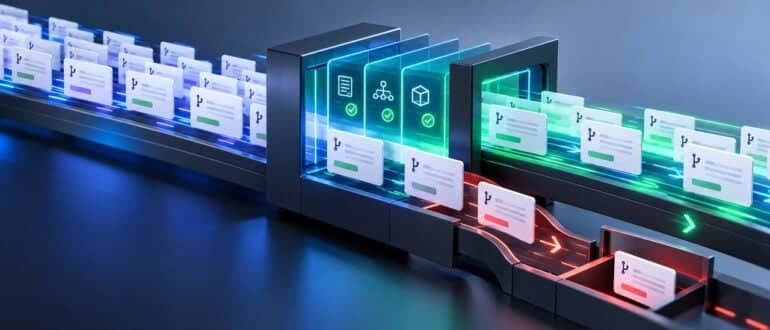
Why Plan Review Stopped Working
The control that held your infrastructure together was plan review, meaning a person reading a diff and deciding whether to approve it. Not the policy document and not the pipeline configuration. It worked because change arrived at human speed. That condition no longer holds. An agent opens 40 pull requests before lunch. Reviewers approve them […]
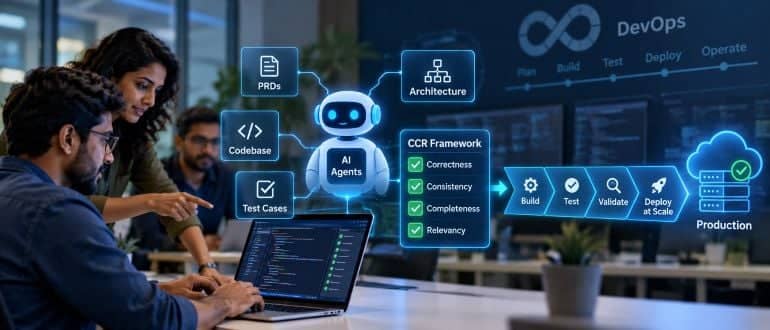
Talentica Software Unfurls Managed AI Service to Optimize Software Delivery
Talentica Software this week launched a managed software delivery service that leverages artificial intelligence (AI) to enable DevOps teams to deploy applications developed using AI coding tools at scale. Company CTO Manjusha Madabushi said the DevX AI Pods service makes use of a set of AI agents that Talentica has trained to provide the context […]
What I Learned Building Cloud-Portable Services Across Multiple Providers
Multi-cloud strategies often stumble over provider-specific behavior. A layered abstraction built on official SDKs can normalize differences while preserving access to valuable native capabilities.
The Observability Tax: When Monitoring Costs Exceed Downtime Costs
Observability costs can spiral when teams collect more telemetry than they actually use. A more mature approach prioritizes the data that directly improves incident detection, diagnosis and recovery.
GitHub Gives Enterprises a Full Count of Who Holds the Keys
GitHub Enterprise Cloud now lets organizations export a full inventory of credentials, helping security teams identify stale, overprivileged and forgotten access across users, apps and automation.
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee.
AWS Adds Harness to Open Source SDK for Building AI Agents
Amazon Web Services (AWS) this week revealed it has added a harness to the open source software development kit (SDK) it makes available for building artificial intelligence (AI) agents. First introduced last year, the Strands SDK makes it simpler for application developers to use AI models to build and deploy AI agents. The Strands harness […]
Cycode Extends DevSecOps Reach to Software Packages Developers Download
Cycode is adding workstation-level protection to stop developers and AI coding agents from downloading malicious or insufficiently vetted software packages.
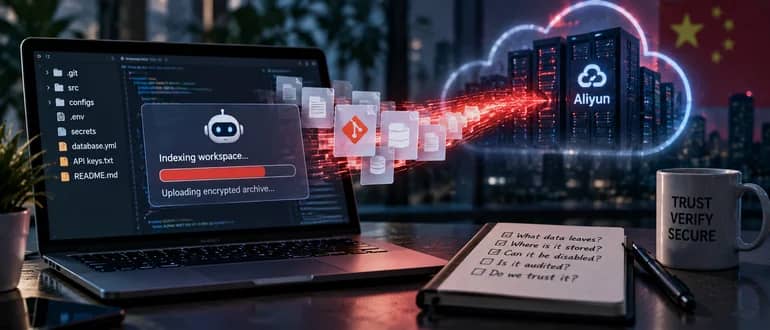
Your AI Coding Assistant Has the Keys to the Repo. Z.ai Just Showed Why That Matters
ZCode’s default-on indexing feature reportedly uploaded entire developer workspaces to cloud storage, highlighting why AI coding assistants should be treated as privileged software and closely monitored.
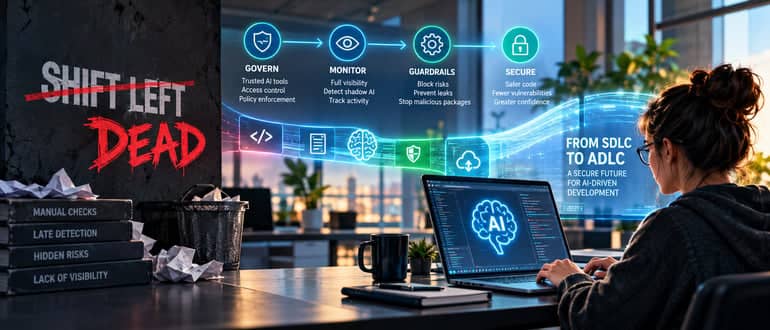
Why Shift Left is Dead
AI-driven development is exposing risks before code is written, forcing security teams to move beyond shift-left and govern agents, prompts, tools and data across the entire development lifecycle.
New npm Threat Bypasses Install Script Protections
A malicious npm package that has been downloaded millions of times comes with a new way of spreading the malware that makes it easier to bypass security protections, say researchers with security vendor Checkmarx. Rather than using more common preinstall or postinstall scripts, the bad actors instead created a malicious package – indexed-btree – that […]
Ten Great DevOps Job Opportunities
DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience. Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers. Of course, the pool of […]