

SBOMs 101: What You Need to Know
Recent security incidents have the industry buzzing about the lack of knowledge about code dependencies, attacks on the software supply chain, software bills of materials (SBOM), digital signatures, provenance, attestation and the like. The fact is, every time a new vulnerability appears a lot of time and effort is required to detect not just when, […]
To Prevent Supply Chain Attacks, Build Secure Code
More than a year after the massive SolarWinds cyberattack, targeted companies continue to feel its ramifications in both reputation and financial cost. Moreover, the global software supply chain remains vulnerable to severe attacks, whether from a hostile nation-state like Russia–now increasingly in the cybersecurity spotlight due to fears of retaliation due to U.S. sanctions–or from […]
Survey Warns of Looming Software Testing Crisis
A survey of CEOs and IT professionals involved in application testing finds a significant gap in terms of how acceptable it is to release software that has not been properly tested. The survey, conducted by the market research firm Censuswide on behalf of Leapwork, a test automation platform provider, polled 480 CEOs in the U.S. […]
The Future of Low-Code Development
Fear of automation (automation anxiety) has existed since the 16th century. It has been a major driver of negative attitudes toward technology and machines (also known as technophobia). With more sophisticated low-code and no-code development solutions on the horizon, even software developers face bouts of disquietude related to their job security. While low-code solutions have […]
Red Hat CEO: Out | Blind Users: Revolt | ARM: Google Joins Party
In this week’s The Long View: Matt Hicks is the new Red Hat CEO, visual accessibility is in focus, and Google Cloud rolls out ARM instances.
Scribe Security Unveils Pair of Tools to Secure Software Supply Chains
Scribe Security today unveiled a Scribe Integrity tool that scans software artifacts to make sure they comply with IT organizations’ security policies before they are integrated into an application. The Scribe Integrity tool authenticates open source and proprietary source code before it is uploaded into a build. It assumes that all artifacts are “guilty” until […]
A Full Pipeline: CI/CD for Network Automation and Orchestration
The intersection of CI/CD and network automation has grown substantially over the past few years. Network teams have seemingly reached the point in their automation and orchestration journey where it has become critical to implement a strategy to manage the testing, version control and deployment of both network changes and automation assets. While CI/CD has […]
Styra Unfurls Cloud Service for Implementing Compliance-as-Code
Styra, Inc. today launched an authorization service based on the Open Policy Agent (OPA) software that can be invoked via an application programming interface (API). Torin Sandall, vice president of open source for Styra, said the Styra Run cloud service will make it much simpler to embed enterprise-grade authorization capabilities within applications. Today, developers spend […]
How Automated Testing Closes the Development and Delivery Gap
For the past two years, companies have leaned into digital transformation projects to keep their digital offerings at pace with their in-person operations. Rather than become a stopgap, this digital approach became the new standard for the modern employee and customer experience. It also creates friction between a company’s development team and its user base. […]
CodeLogic Toolkit Increases Visibility Into App Dependencies
CodeLogic launched today a toolkit that enables developers to scan binaries, runtime application behavior and database connections and then leverage graph technology to identify connections and dependencies in real-time. Brian Pierce, CodeLogic CEO, said the goal is to make it simpler for developers to identify the relationship between application elements to increase overall productivity and […]
Rezilion Launches Vulnerability Prioritization Platform
Rezilion today announced general availability of a platform that enables DevOps teams to better prioritize remediation efforts by identifying which vulnerabilities both run in memory and actually impact a class or function that can be executed. Liran Tancman, Rezilion CEO, said the biggest DevSecOps challenge organizations face today is that the bulk of vulnerabilities that […]
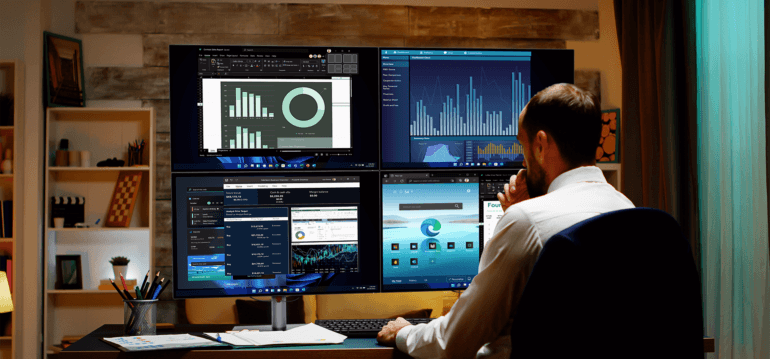
5 Best Practices for Software Development in the Hybrid Workplace
Over the years, software teams have gradually become more dispersed as technology advancements facilitated hybrid work and allowed teams to collaborate, create and innovate remotely. However, this trend accelerated and became more of a mainstream norm over the last two years during the COVID-19 pandemic, requiring newly dispersed teams to develop a more streamlined hybrid […]
Connections Matter: Gaining Visibility Into APIs
Digital transformation is at the center of modern enterprise. Yet, as cloud initiatives take shape and the complexity of connecting systems and applications multiplies, the need to tie everything together and automate processes grows. APIs, otherwise known as application programming interfaces, fuel this automation. These small pieces of code—which connect and interconnect clouds, containers, microservices […]
The Quest To Unify With GraphQL, The Modern Data API
There is an ongoing trend in enterprise software: Using GraphQL as an aggregation layer to unify access to underlying data sources and REST APIs. Some call this the supergraph, and others refer to it as a meta layer. The idea is that by providing a more consumable layer to a wide range of internal sources, […]
BMC Adds Support for DORA Metrics to Mainframe Tools Portfolio
BMC this week announced it has added support for DevOps Research and Assessment (DORA) metrics within its portfolio of DevOps tools for mainframe environments. John McKenny, senior vice president and general manager for intelligent Z optimization and transformation at BMC, said the latest edition of BMC Compuware zAdviser now includes a DORA KPI Dashboard that […]
Planview Outlines VSM Strategy After Acquiring Tasktop
Planview this week announced it completed its acquisition of Tasktop, a provider of a value stream management (VSM) platform that enables DevOps teams to align their efforts more closely with strategic business goals. Louise Allen, chief product officer for Planview, said the goal is to tighten integration between the Tasktop VSM platform and the project […]
Dev Job Phisher Steals $540M | Patch OpenSSL NOW | Systemd Dev Joins Microsoft
In this week’s The Long View: Spear-phishing causes $540 million loss, a high severity bug in OpenSSL might be “worse than Heartbleed,” and Lennart Poettering is now working for Microsoft.
5 Mean-Time Reliability Metrics To Follow
Most folks working in DevOps or SRE roles are familiar with metrics like mean-time-to-recovery (MTTR). Keeping track of the average time a team takes to respond to incidents is crucial to identifying bottlenecks in the support process. It’s also something executives like to show higher-ups when sharing a snapshot of overall platform performance. However, focusing […]
Applying Automation to DevOps
In the book, “Life and the Art of Engineering,” author Haresh Sippy said, “Automation is cost-cutting by tightening the corners, not cutting them.” Today, businesses and organizations are constantly on the lookout for ways to improve productivity while reducing inefficiencies across their operations. Automation has emerged as the natural answer as it addresses these issues while […]
Why Your DevSecOps Initiative Will Fail
When you’ve been in and around the security industry for long enough, you get used to the industry hype machine turning a cool innovation into, uh, meh. This hype cycle starts at the RSA conference each year, and folks like me look for new hot stuff on the show floor. For perhaps only the second […]
Survey Shows Increased Reliance on DORA Metrics
A new survey found just under a quarter (23%) of respondents are now tracking all four of the DevOps metrics defined by the DevOps Research and Assessment Team (DORA), with another 17% now tracking three. The State of Developer Experience survey polled 129 IT professionals that play a role in software development and was conducted by […]
TechStrongCon: Time to Build an Army of Citizen Developers
DevOps teams need to start drafting a strategy to support what will soon become an army of citizen developers. Speaking at the virtual TechStrongCon event, JP Morgenthal, global director for modern applications development at DXC Technology, told conference attendees that the time to build an army of citizen developers is now. Citizen developers are typically […]
Salesforce Adds RPA Bots to MuleSoft Integration Platform
Salesforce today announced that it is now using robotic process automation (RPA) to connect disparate data via a no-code tool developed by its MuleSoft unit. Shaun Clowes, chief product officer for MuleSoft, said bots created using an RPA-infused integration platform can now automate much of the effort previously required to integrate data residing in different […]