

Is Your AI Agent Secure? The DevOps Case for Adversarial QA Testing
Adversarial QA testing helps validate AI agents under real-world conditions, exposing risks like prompt injection and logic failures.
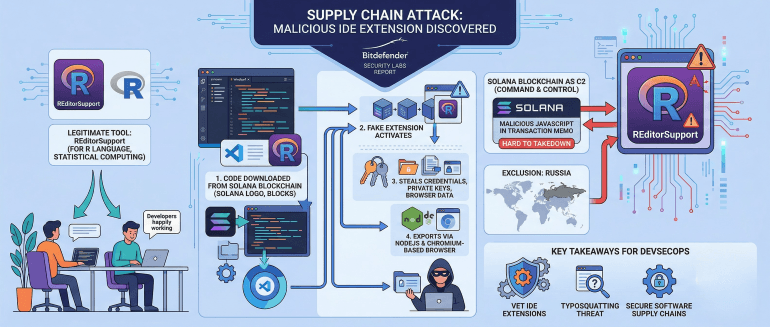
Latest Typosquatting Attack Targeting VS Code Tools Hits Windsurf IDE
Cybersecurity researchers from Bitdefender, a provider of an endpoint detection and response (EDR) platform, have discovered an extension to the Windsurf integrated development environment (IDE) that steals credentials and data after code is downloaded from the Solana blockchain platform. Silviu Stahie, a security analyst for Bitdefender, said the extension makes use of typosquatting tactics to […]
GitHub to Leverage User Code for AI Model Training, Allows Opt-Out
GitHub is preparing a significant change to how it trains the AI models behind its Copilot coding assistant. Beginning April 24, the Microsoft-owned platform will collect user interaction data by default to improve its AI systems, unless users actively disable the setting. The update applies to individuals using Copilot Free, Pro, and Pro+ tiers. Enterprise […]
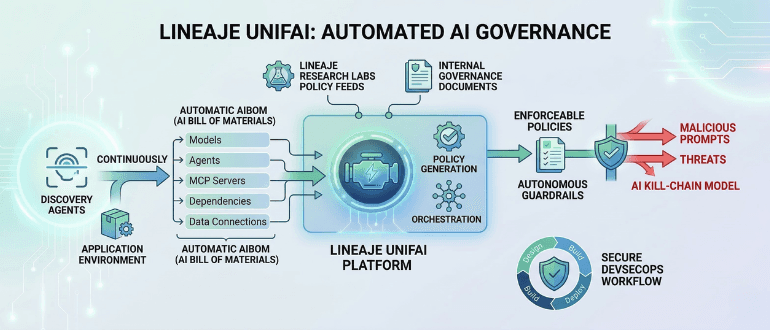
Lineaje Adds Ability to Automatically Apply Governance Policies to AI Components
Lineaje this week unfurled a platform that automatically discovers the artificial intelligence components of an application, defines security and governance policies, and then autonomously generates guardrails. At the core of the Lineaje UnifAI platform are a set of artificial intelligence (AI) capabilities that are integrated with an orchestration framework for applying governance policies that has […]
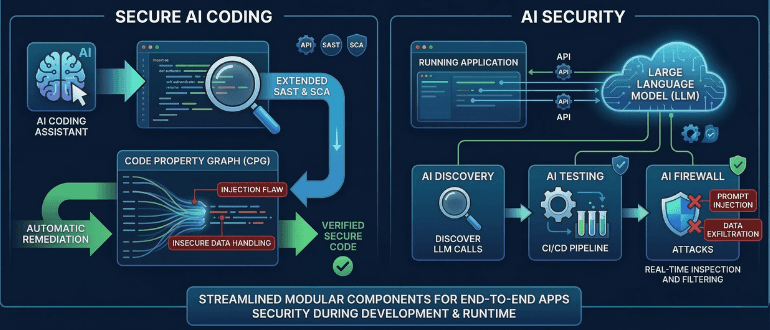
Harness Extends AI Security Reach Across Entire DevOps Workflow
Harness today added an ability to automatically secure code as it is being written by an artificial intelligence (AI) coding tool in addition to adding a module to its DevOps platform that discovers, tests, and protects AI components within applications. Secure AI Coding is an extension of the static application security testing (SAST) and software […]
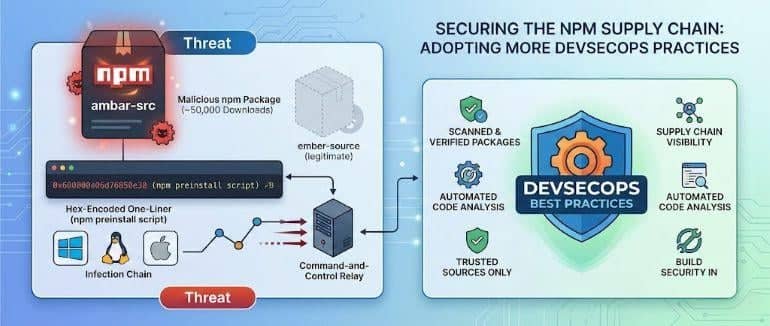
Malicious NPM Package Gets Downloaded 50K Times Before Discovery
A malicious package downloaded approximately 50,000 times from a node package manager (npm) is providing an object lesson for adopting more DevSecOps best practices. Security researchers from Tenable discovered a “ambar-src” package that was first published Feb. 13 and then updated again before being discovered. It is aimed at developers building JavaScript applications on Windows, […]
Checkmarx Extends Vulnerability Detection to AI Coding Tool from AWS
Checkmarx this week revealed it has added support for the Kiro artificial intelligence (AI) coding tool provided by Amazon Web Services (AWS) to its Checkmarx Developer Assist that leverages AI to surface vulnerabilities before code is committed. The Checkmarx IDE extension for Kiro is designed to be activated from within the Developer Assist tab that […]
Bridging the Dev–Security Gap With Smarter Authorization
Software teams have always lived with a built-in tension – developers push to ship fast, while security teams pump the brakes to assess risk. Now, with AI flooding the enterprise, that friction is spiking. One recent survey found a staggering 322% jump in privilege-escalation risks tied to AI-generated code. The root problem isn’t new – […]
Arcjet SDKs Make It Simpler for Developers to Include Security Functions
Arcjet this week made available a software development kit (SDK) that makes it simpler for JavaScript developers to embed capabilities such as bot detection, rate limiting, email validation, attack protection and data redaction directly within their applications. Company CEO David Mytton said the release of v1.0 of its Arcjet JavaScript SDK makes it possible for […]
CodeHunter API Integrates Deterministic AI Models into DevSecOps Workflows
CodeHunter, a provider of behavioral malware analysis and threat intelligence tools, today announced it is making available an application programming interface (API) to make it simpler to embed the capabilities it provides within a DevSecOps workflow. At its core, CodeHunter makes use of a set of deterministic AI models that it has developed to analyze […]
Rein Security Emerges to Analyze Reachability of Application Vulnerabilities
Rein Security has emerged from stealth to launch an application security platform capable of determining the reach of a vulnerability based on which libraries and application programming interfaces are actually running in a production environment. Fresh off raising $8 million in seed funding. Rein Security CEO Matan Bar Efrat said DevSecOps teams can now gain […]
Legit Security AI Tool Uses Threat Feed to Identify Risks to Software Supply Chain
Legit Security this week added a threat feed that DevSecOps teams can use to instantly determine if a newly discovered vulnerability impacts their software supply chain. Built using the Legit VibeGuard tool, the threat feed added to the company’s application security posture management (ASPM) platform also enables DevSecOps teams to take advantage of “vibecoding” techniques […]
Malicious VS Code Extensions Take Screenshots, Steal Info
Developers were the targets of two new malicious Microsoft Visual Studio Code (VS Code) extensions created by a threat actor that security researchers believe is experimenting with methods for delivering information-stealing malware to the victims’ systems. The malicious extensions come posing as a harmless “premium dark theme” and an AI-powered coding assistant, but both – […]
Second Coming of Shai-Hulud Cyberattack Ravages JavaScript Repositories
A major expansion of the self-propagating Shai-Hulud cyberattack aimed at popular node package managers (npms) used by JavaScript application developers is creating a major headache for DevSecOps teams around the globe. Based on what is being described as the “Second Coming” of Shai-Hulud, this version affects a much wider range of npms and is much […]
Patch Management is Essential for Securing DevOps
Zero-day exploits don’t wait for anyone and are one of the main reasons why the cybersecurity market will be worth a whopping $256 billion worldwide. In the current threat landscape, attackers weaponize vulnerabilities within hours of disclosure, and that puts DevOps teams in a precarious position. The ability to patch quickly and confidently can mean […]
Minimus Adds VEX Support to Managed Hardened Images Service
Minimus has extended its managed service for providing application developers with hardened images to include support for the Vulnerability Exploittability eXchange (VEX) format used to share data across multiple application security tools and platforms along with hardened Helm charts for securely deploying applications on Kubernetes clusters. Additionally, Minimus has added compliance dashboards and views, and […]
ControlMonkey Adds Dashboard to Manage IaC Risk
ControlMonkey today added a risk index dashboard to its automation platform for managing code created using infrastructure as code (IaC) tools based on open-source Terraform software.
Veracode Allies with Wiz to Bring More Context to DevSecOps Workflows
Veracode today revealed an alliance through which it will integrate its application security posture management (ASPM) platform with the cloud native application protection platform from Wiz.
GitLab Extends Scope and Reach of Core CI/CD Platform
GitLab Inc. has updated its core continuous integration/continuous delivery (CI/CD) platform to natively provide more artificial intelligence (AI) capabilities, along with built-in software artifact management capabilities and more robust security tools.
Minimus Unfurls Service for Accessing Secure Software Artifacts
Minimus today at the 2025 RSA Conference launched a managed service through which it ensures application development teams are provided access to a secure set of minimal container images and virtual machines. Company CTO John Morello said the Minimus service eliminates the possibility that developers might inadvertently download software artifacts that might be infested with […]
Harness Merges with Traceable to Provide Integrated DevSecOps Platform
Harness today announced that Traceable will be merged into the company to create a combined company that will further advance the adoption of best DevSecOps practices across the software development lifecycle (SDLC).
More Than 3,000 ‘Ghost’ Accounts Spreading Malware on GitHub
GitHub and similar open-source code and project repositories have become a common target of cybercriminals looking to lure developers into unknowingly downloading malicious scripts.
CrowdStrike Software Update Sparks Microsoft Outage, Global Chaos
Airlines, hospitals, banks and other businesses were disrupted when a faulty software update knocked Windows users of their systems.