

Lineaje Adds Module to Manage Open Source Software Security Lifecycle
This can help DevSecOps teams identify open source software projects that are not being well maintained.
Snyk Adds Second ASPM Tool to Portfolio
Today, Snyk made available an edition of its application security posture management (ASPM) tool for assessing application risks that provides more context into how code has been written and its role within the application environment. Manoj Nair, chief product officer for Snyk, said Snyk AppRisk Pro leverages artificial intelligence (AI) and machine learning to provide […]
OpenSSL Fiasco: What can DevOps Learn? | Elon Fires ‘50%’ of Twitter
In this week’s The Long View: The OpenSSL project has egg on its face, and half of Twitter’s staff are for the chop tomorrow.
Meta Income Down by Half | Will Apple Make it Worse? | Linux Secure Boot Fix
In this week’s The Long View: Meta’s latest results are very bad, Apple wants its cut of Facebook ads, and Lennart Poettering proposes improving Secure Boot for Linux.
Kill the Password: Google on Board | 4-Day Week Proves Worthy
In this week’s The Long View: Passkeys is getting another big-tech supporter, and the four-day workweek train picks up speed.
AWS re:Invent Roundup: Private 5G | Graviton3 ARM Chips | DevOps Guru++
In this week’s The Long View: Three things that caught my eye from Amazon Web Services’ re:Invent conference. Private 5G, Graviton3 chips, and something called DevOps Guru for RDS (yes, really).
Securing Your Software Development Pipelines
Earlier this year, it was announced that the attack on IT management software provider SolarWinds had been used to compromise other organizations, including parts of the United States government. There were several reasons for alarm because of this news, but one of the biggest was the revelation that attackers breached SolarWinds’ software development process and […]
DevOps Chat: Maximizing the Benefits of DevSecOps
When discussing security in DevOps, we often focus on the security tools instead of the DevSecOps process itself. In this DevOps Chat, ZeroNorth CEO John Worrall takes us to the root of “why” DevSecOps, focusing on the business benefit, gain and measurement of what we seek to accomplish through DevSecOps. John advocates we concentrate on […]
Solving Cloud-Native Challenges in the Rush to the Cloud
The shift to cloud-native environments away from traditional data center infrastructures continues unabated, but security and complexity challenges remain a struggle for DevOps teams. These were two of the main takeaways in a survey and analyst report published by the IT consultancy firm Flexera. The survey, based on the responses of 750 IT professionals, revealed […]
Unlocking Your DevOps Automation Mindset
In the new digital normal, where remote working has upended conventional software development cycles, the role of DevOps is central. Many enterprises have an accelerated digital agenda, but are often underinvested in rebooting DevOps for several reasons, including a lack of experience and insight into how it can help businesses recover from the new challenges […]
5 Principles for Securing DevOps
DevOps, a new model for software development, is transforming the way the world creates software. And despite its substantial organizational, cultural and technological requirements, this new way of organizing development and IT operations work is spreading rapidly. To read more about DevOps and how to secure it, download the PDF here: [su_button url=”https://devops.wpengine.com/wp-content/uploads/2020/08/Veracode_5-Principles-Securing-DevOps.pdf” target=”blank” background=”#ef2d3f”]Download […]
How-To Stop Copying and Pasting Flaws Using Open Source Code
In this video, learn how to prevent critical flaws in your copying and pasting methods using open source code through this video presentation from Brittany O’Shea, Senior Product Marketing Manager at Veracode. To watch the full video, download it here: [su_button url=”https://devops.wpengine.com/wp-content/uploads/2020/08/Veracode_How-To-Video_Open-Source-Code.mp4″ target=”blank” background=”#ef2d3f”]Download Now[/su_button] devopsy.kinsta.cloud
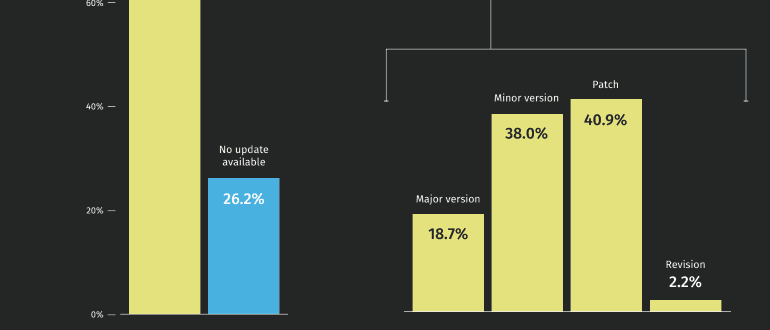
State of Software Security – Open Source Edition
For our State of Software Security: Open Source Edition report, we analyzed the security of the open source libraries found in 85,000 applications. Below are highlights of that analysis. To see these highlights, download the infographic below: [su_button url=”https://devops.wpengine.com/wp-content/uploads/2020/08/Veracode_State-of-Software-Security_Open-Source-Infographic.pdf” target=”blank” background=”#ef2d3f”]Download Now[/su_button] devopsy.kinsta.cloud
Understanding Modern Software Development: What Security Professionals Need to Know
There has been a noticeable shift from a monolithic architecture to services- or microservices-oriented architecture. Microservices architecture entails breaking applications into smaller, interconnected services instead of one large, monolithic application. The reason for the shift is likely due to the fact that microservices architecture is faster to develop and easier to maintain. Unlike monolithic applications […]
Creating Marketplace Efficiencies for the Healthcare Industries
With approximately 6 million patients that visit this digital healthcare company per month to schedule and book doctor appointments, they strive to adapt, innovate, and modernize the healthcare industry by providing a frictionless healthcare experience for healthcare practitioners and for the 21st century patient. The company started out by focusing on the first step in […]
At the Intersection of Finance and Security
Envestnet | Yodlee is a leading data aggregation and data analytics platform powering dynamic, cloudbased innovation for digital financial services. More than 1,000 companies, including 13 of the 20 largest U.S. banks and hundreds of Internet services companies, subscribe to the Envestnet | Yodlee platform to power personalized financial apps and services for millions of […]
Securing the Digital Commerce Ecosystem for Merchants, Customers, and Banks
Founded in 2006, GreenSky, Inc. is a leading financial technology company “Powering Commerce at the Point-of-Sale” for a growing ecosystem of merchants, consumers and banks. Their highly scalable, proprietary technology platform enables nearly 16,000 merchants to offer frictionless promotional payment options to consumers, driving increased sales volume and accelerated cash flow. Banks leverage GreenSky’s technology […]
Case Study – Travis Perkins plc by Checkmarx
With over 20 leading brands providing various online services for tens of thousands of consumers, Travis Perkins had the need for a strong AppSec solution in its arsenal to protect its applications. As the company shifted to an agile workflow, their development process became more fast-paced and it became evident that the company needed a […]
Modern Application Development on AWS
Modern application development using containers and serverless technologies can help your organization accelerate innovation. This paper includes information about important best practices and design patterns that you can use to build your modern application in the AWS Cloud. Read more here: [su_button url=”https://devopsy.kinsta.cloud/wp-content/uploads/2020/08/modern-application-development-on-aws.pdf” target=”blank” background=”#ef2d3f”]Download Now[/su_button] devopsy.kinsta.cloud
Serverless is great, but what about the security of my AWS Lambda functions and their dependencies?
Function as a Service (FaaS) platforms patch your operating system dependencies for you, but do nothing to secure your application dependencies, such as those pulled from npm, PyPI, Maven and the likes. These libraries are just as prevalent and just as vulnerable as operating system dependencies, and you—the application owner—are responsible for upgrading or patching […]
Putting the Sec in DevOps
Originally presented at TechStrongCon, watch the session presented by Checkmarx entitled “Putting the Sec in DevOps”. Below is the description for the presentation: Automation and DevOps have changed the way organizations deliver products. The shift towards DevOps made it pretty clear that companies are adopting this organizational model in order to facilitate a practice of […]
Time Inc Case Study by Checkmarx
Time Inc. is a mass media corporation that shares news and stories impacting global dialog across multiple media platforms for nearly a century. With some of the world’s biggest media brands under the umbrella of Time Inc., the company knew it had to completely secure their applications from continuous security threats. The task was to […]
Interactive Application Security Testing (CxIAST) from Checkmarx
In today’s competitive world, the name of the game is time-to-market. Organizations are under increasing pressure to continuously deliver new and improved software. To win the race, nothing can get in the way of rapid releases. This need for speed has often led organizations to leave security behind, making them a frequent target for attack. […]