

How AI is Revamping DevSecOps Processes
Artificial Intelligence is pushing DevSecOps into a new phase where security is no longer just about detecting vulnerabilities, but increasingly about resolving them automatically within the flow of software delivery. As many organizations are discovering, DevSecOps historically gave teams visibility into risk. AI is now turning that visibility into automated remediation. This evolution has taken […]
Why DevOps Is Critical for Modern Business Resilience
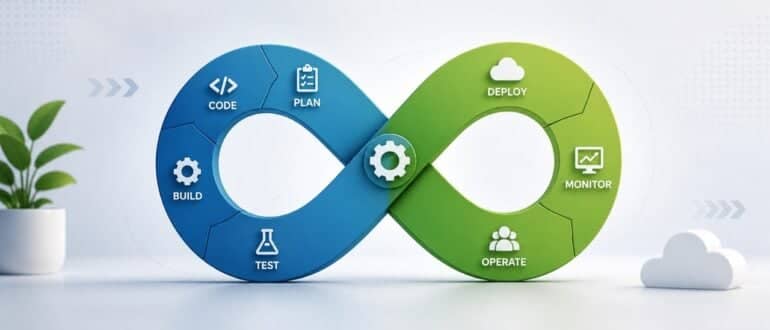
Today’s business world operates in a state of constant change. What the customer wants to buy changes quickly, new competitors appear overnight, and cyber threats are changing faster than ever. In this world, the concept of “resilience,” the ability to adapt, to overcome, and to continue to create value for the enterprise despite the changes, […]
How Open Source Dependency and Repo Attacks Compromise DevOps Pipelines and How to Stay Safe
Modern applications rely on open source components for up to 90% of their code, creating a vast attack surface dominated by inhemalicious supply chain injections. High-profile incidents like Log4j and the sabotage of colors.js highlight that traditional scanning often fails to detect sophisticated “protestware” or dependency confusion, necessitating 19 practical controls focused on strict intake governance, dependency pinning, and behavioral monitoring to secure the development lifecycle.
Claude Code Security Finds the Bugs That Static Analysis Can’t — and Wall Street Noticed
Claude Code Security scans code like a human researcher, not a rule engine. Anthropic found 500+ decade-old bugs — and cybersecurity stocks felt it.
White Paper: The Future of DevSecOps in a Fully Autonomous CI/CD Pipeline
Abstract The growing complexity of modern software development and the increasing speed at which organizations need to deliver software have led to the widespread adoption of DevOps practices, particularly continuous integration/continuous deployment (CI/CD) pipelines. These pipelines enable rapid development and deployment cycles; however, they also introduce significant security risks that must be addressed continuously. The […]
How Benchmarking Can Help Software Development Teams Achieve CISA’s “Secure by Design”
In April 2023, the Cybersecurity and Infrastructure Security Agency (CISA) launched its Secure by Design initiative, directing technology companies to ‘prioritize the security of customers as a core business requirement, rather than merely treating it as a technical feature’.
The Software Extinction Event That Wasn’t
The world may have just avoided a cybersecurity disaster, with potential impact of CrowdStrike x1000. Imagine if the world’s most pervasive programming language, used in the majority of organizations, services, websites and infrastructure today, was itself made to be malicious? Cybersecurity researchers from JFrog recently discovered a GitHub Personal Access Token in a public Docker […]
Sumo Logic Previews GenAI Tool to Improve DevSecOps Observability
Sumo Logic this week at the RSA Conference previewed a copilot that leverages generative artificial intelligence (AI) to make it simpler for IT and cybersecurity professionals of varying levels of experience to derive benefits from its observability platform via a user interface (UI) the company is in the process of revamping. In addition, Sumo Logic […]
Securing the DevOps Pipeline: Tools and Best Practices
Because of the critical nature of the DevOps pipeline, security is becoming a top priority. Here’s how to integrate DevSecOps.
5 Security Threats DevOps Teams Should Know
DevOps security (DevSecOps) is about breaking down silos and promoting open collaboration across teams.
Software Deployment Security: Risks and Best Practices
In an era where software is at the heart of every business, deploying applications securely and efficiently has never been more critical.
The Differences Between DevOps, DevSecOps and SRE
DevOps, DevSecOps and SRE are all quickly gaining traction within the tech world due to their effectiveness and promise of reliability for companies. Each framework provides various levels of safety and scalability—DevOps is agile, DevSecOps prioritizes security above all else and SRE focuses on performance optimization. Together, these are changing how software gets deployed from […]
Shift Left With DAST: Dynamic Testing in the CI/CD Pipeline
By focusing on application security like an attacker would, DAST can discover potential security threats that static testing methods might miss.
The Role of SBOMs in Software Supply Chain Security
The software supply chain has become increasingly complex and dynamic with the rise of cloud computing, open source software and third-party software components and APIs. Widespread damage can occur if third-party APIs, cloud services, SDKs and open source software have security flaws. As a result, software supply chain security has emerged as a critical concern […]
A DevOps Guide to the Language of DevSecOps
Security is increasingly important for DevOps due to the growing complexity of applications and the accelerated pace of development. As organizations adopt DevOps practices, they face new challenges in securing applications and infrastructure: Increased complexity and automated processes: With automation at the core of DevOps, processes and applications are more intricate. This can introduce vulnerabilities […]
Watching the Watchers: Solving the Problem of Meta-Permissions
The move to the cloud and microservices has introduced new challenges in managing permissions. Software has been broken down into small, independently-deployable microservices, each with its own unique set of permissions. These permissions make it excruciatingly hard to ensure and track correct access. While this technological shift is challenging, it pales in comparison to the […]
DevOps Done Right: How to Succeed in DevOps From Day One
Whether you are diving into DevOps for the first time or trying to do it right this time, DevOps Onramp provides all the information you need for a successful DevOps journey. Join us on May 4, 2023, to learn how to get started with DevOps—and how to do it right. You’ll learn: DevOps best practices, […]
A DevSecOps Process for Node.js Projects
Node.js is an open source development platform for running JavaScript code on the server side. Node is useful for developing applications that require a persistent browser-server connection and is often used for real-time applications such as chat, social applications, or news feeds. DevSecOps is a way for development, security, and operations teams to work together […]
5 Tips for Securing DevOps: What You Wish You Knew Sooner
Foundations and frameworks, concrete and steel—not exciting. But that’s the foundation and framing of pretty much every modern building. Everything else that is part of a building–flooring, wiring, lighting, room placement and so on—is made possible by the foundation and the framework. If you want DevOps to succeed in your organization, you have to start […]
Rust Momentum Intensifies | Elon Says No WFH
In this week’s The Long View: People won’t shut up about Rustlang, and Musk mandates Twitter teams return to the office.
Developer’s Guide to Fuzz Testing
Fuzz testing continues to grow in popularity among developers within the open source community. Google’s open source security (OSS) team recently reported finding more than 40,000 bugs in 650 open source projects through the use of fuzz testing. But if you have no clue what fuzz testing is (yet), don’t worry. You’ve come to the […]
How DevOps Helps With Secure Deployments
DevOps is an approach to software development that emphasizes communication and collaboration between teams. It’s best known for bringing together people who previously worked in separate areas like engineering or testing; this allows them all to learn from each other as they work on projects together. DevSecOps helps organizations monitor and discover security risks throughout […]
Putting the Security Into DevSecOps
The non-Newtonian fluid that’s composed of cornstarch and water has been around a long time, but Dr. Seuss’ 1949 book was the impetus for what it’s often called today – Oobleck, from “Bartholomew and the Oobleck.” When not under pressure, Oobleck is a thin liquid; when pressure is applied, its resistance increases to the point […]