

Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
Security researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more attacker-owned crates. In addition, researchers with Wiz wrote that there also appears to be overlap with supply chain campaigns run by nation-state actors […]
npm v12 Shuts Down a Popular Malware Trick — But the Threat Isn’t Going Away
For years, one of the easiest ways to sneak malware onto a developer’s machine has been to hide in plain sight. Install a package from npm, and any lifecycle script bundled with it runs automatically — no review, no approval, no second look. Attackers have known this for a long time, and they’ve used it […]
GitHub Sharpens CodeQL’s Eye on Actions Workflows and Modern JavaScript
GitHub Actions pipelines have become one of the quieter attack surfaces in software development. They pull in third-party actions, cache dependencies, and pass secrets between jobs, often without anyone reviewing the workflow file as closely as they’d review application code. That gap is exactly where cache-poisoning and output-clobbering attacks live, and it’s why GitHub keeps […]
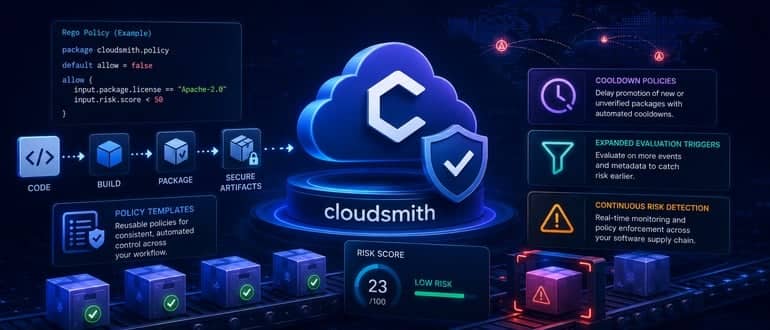
Cloudsmith Extends Policies and Controls to Secure Application Binaries
Cloudsmith this week revealed it has expanded the policy management and continuous risk detection capabilities it makes available within its software artifact management platform to now include policy templates, cooldown policies, and expanded evaluation triggers. Alison Sickelka, vice president of product for Cloudsmith, said these additions to the platform will make it simpler to prevent […]
Microsoft’s GitHub Hit by Major Outage as AI-Driven Demand Strains Infrastructure
GitHub, the Microsoft Corp.-owned code hosting platform serving more than 180 million developers, is still reeling from a widespread outage on Monday that severely disrupted software development pipelines globally. The hours-long incident was the latest in a relentless series of reliability failures for a service struggling to keep pace with an unprecedented surge in artificial […]
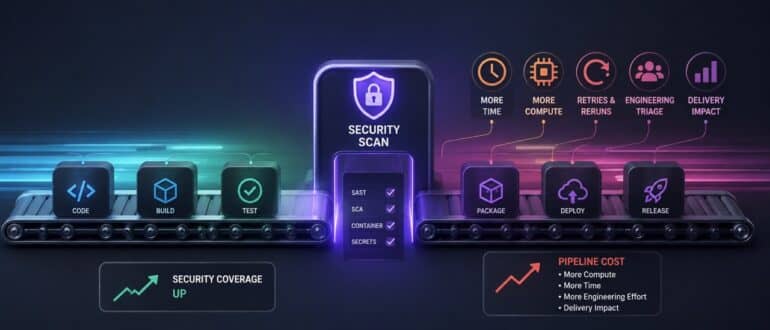
Is Your New DevSecOps Tooling Reducing Work Or Just Adding to It?
Security belongs in the software delivery pipeline. The harder question is where, how often and at what cost. Many pipeline teams eventually add security scanning to CI/CD, and relatively few go back afterward to measure what it actually cost the delivery process. Security coverage went up. Something else changed too, and it is rarely measured […]
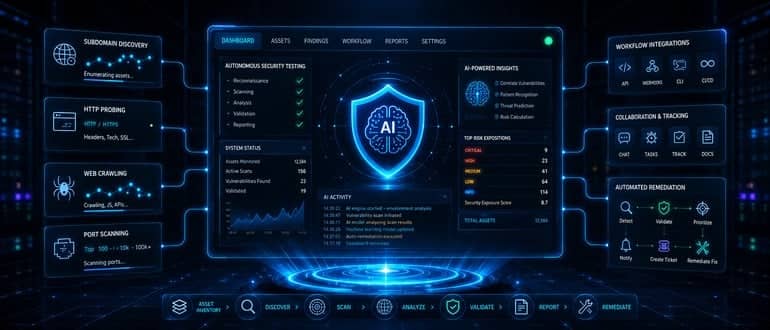
ProjectDiscovery Brings Open Source AI Testing to Vulnerability Discovery
ProjectDiscovery has made available an autonomous security testing platform that leverages an open source artificial intelligence (AI) testing framework to detect and validate vulnerabilities at a lower total cost. Company CEO Rishi Sharma said version 1.0 of the Neo platform is also available via a cloud service that makes it possible for DevSecOps teams to […]
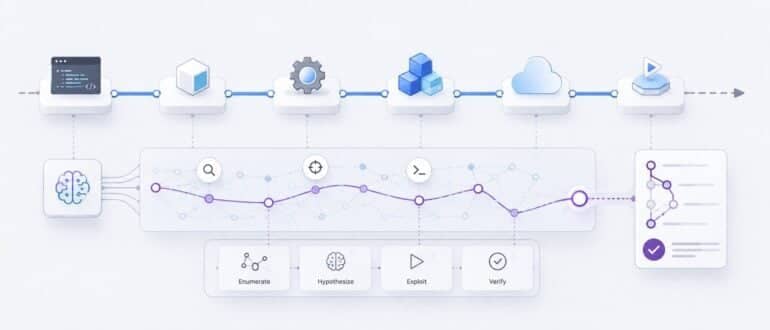
Why CI/CD Security Testing Is Going Autonomous (and Why It Should Stay Local)
Continuous integration and delivery changed the tempo of software. Teams merge dozens of times a day, infrastructure is redefined on every commit, and a new build can reach production in minutes. Security testing never caught up with that tempo. It still lives in two modes that both fight the pipeline instead of moving with it. […]
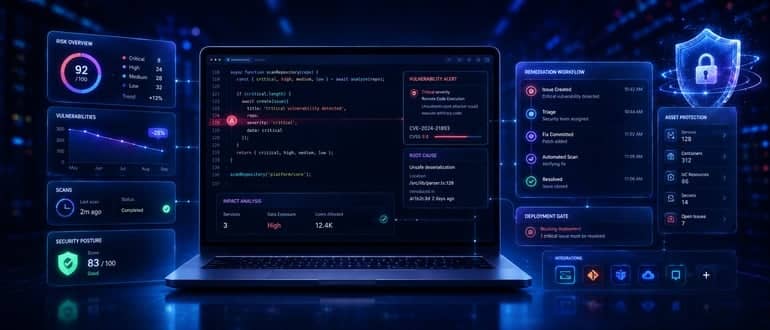
HackerOne Extends Platform Reach to Remediate Source Code Vulnerabilities
HackerOne has added a remediation capability to its H1 Platform that reduces the amount of time required to remediate validated vulnerabilities and other weaknesses affecting specific lines of source code. Nidhi Aggarwal, chief product officer for HackerOne, said H1 Remediation combines artificial intelligence (AI) and crowdsourced research to identify the root cause of issues that […]
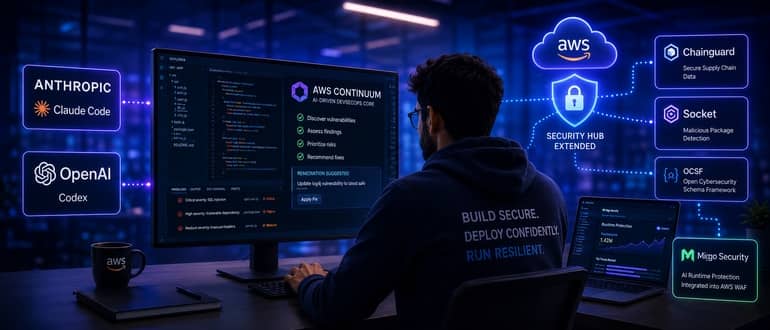
AWS Extends DevSecOps Reach to AI Coding Tools from Anthropic and OpenAI
Amazon Web Services (AWS) this week at the Black Hat USA conference revealed it is working with both Anthropic and OpenAI to integrate their respective coding tools with a service it has developed that makes available artificial intelligence (AI) agents to help application developers write more secure code. Launched earlier this year, the AWS Continuum […]
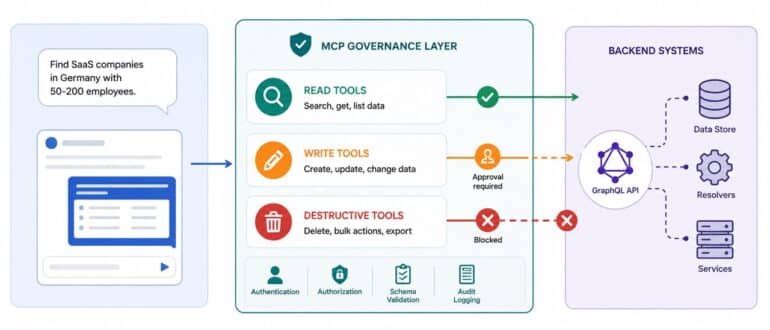
From API Integration to Agent Governance: What Backend Teams Need to Know About MCP
Many MCP projects begin with an existing API and a simple request: expose one backend capability to an LLM client. The quickest route is to wrap an endpoint as a tool and connect it to Claude or another MCP host. Users can then ask for data in natural language instead of navigating a fixed interface. […]
N. Korea Group Behind Multiple Open Source Supply-Chain Attacks: Amazon
Amazon’s recent report attributing a series of compromises of open source software libraries to a North Korea-backed threat group encapsulates many of the expanding cyber risks increasingly facing developers, from the growing use of generative AI by bad actors and targeting of code repositories to financially focused attacks by nation-state hackers and the abuse of […]
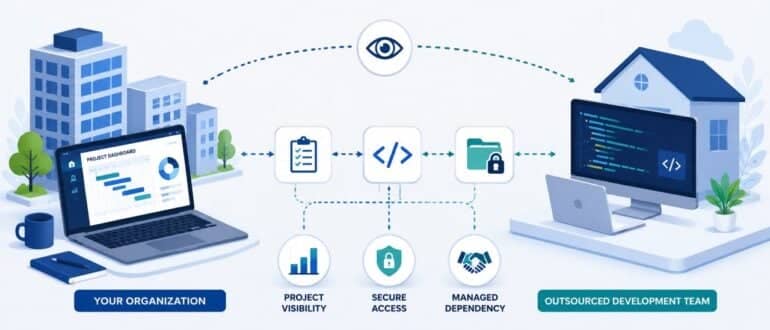
Common Risks of Outsourcing Software Development, and How to Tackle Them
Both SMBs and large enterprises often choose software development outsourcing over developing software in-house. It is no surprise, as partnering with external developers enables companies to bridge IT talent gaps that cannot be filled internally, avoid time-consuming recruiting and training processes, and eliminate expenses associated with salaries and benefits, eventually accelerating software delivery and reducing […]
OpenAI Open Sources Codex Security CLI for the Merge Path
OpenAI has released its Codex Security command-line interface and software development kit as open source software under the Apache 2.0 license, providing a new way to bring its AI security scanner into development workflows. The CLI can scan repositories, review staged and unstaged changes before a commit, compare findings across scans and export results for […]
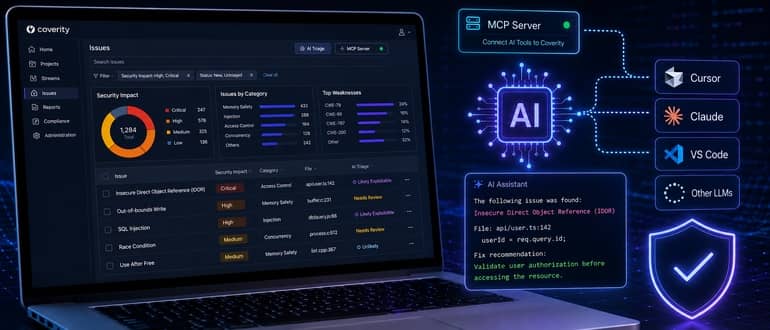
Black Duck Extends Scope and Reach of Code Scanning Tool
Black Duck has updated its Coverity static analysis code scanning tool to provide deeper integrations with artificial intelligence (AI) tools along with updates to its user interface that make it simpler to prioritize issues in a way that makes it easier to adhere to multiple compliance mandates. A Model Context Protocol (MCP) server added to […]
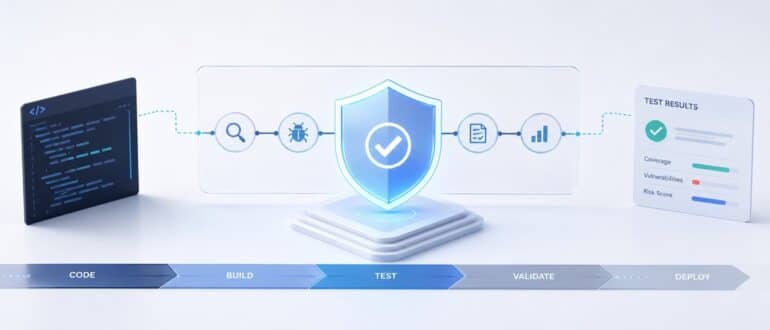
Why You Need AI Agent Security Validation in Software Testing
Engineering teams have been racing for the last two years to deploy AI agents that can find bugs faster than any QA team ever could. Autonomous testing agents can crawl through codebases, identify vulnerabilities, and generate test coverage reports while developers finally get to take a breath. The irony is that while development teams enjoy […]
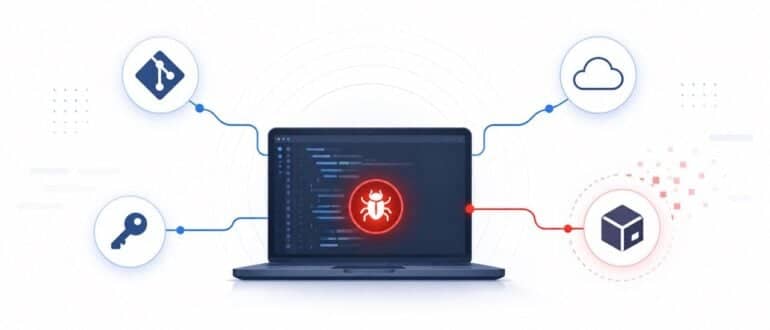
Why Developer Workstations Have Become a Critical Part of the Software Supply Chain
For years, software supply-chain security discussions focused on centralized infrastructure such as build servers, package registries, and CI/CD systems. Recent attacks suggest that this view is incomplete. The Megalodon campaign injected malicious GitHub Actions workflows into thousands of repositories, while a separate incident involving a malicious Visual Studio Code extension demonstrated how a single compromised […]
‘HalluSquatting’ Compromises AI Coding Agents to Install Malware, Create Botnets
Hallucinations have been an ongoing problem since OpenAI first introduced its ChatGPT chatbot in November 2022, highlighting generative AI’s tendency to generate plausible but false or misleading information and its inability to just say “I don’t know.” They can lead to embarrassing or uncomfortable moments. However, security researchers in Israel have found that the large […]
Enterprise Smart Contracts Have a Cryptography Problem. EY Just Built a Way Around It
The business case for smart contracts is building fast. Major financial institutions are using programmable, code-based agreements to underpin financial workflows, supply chain operations, and tokenization initiatives. Developers are being asked to prove the value. But there’s a problem most organizations don’t fully see until they’re already stuck: Privacy. Public blockchains are transparent by design. […]
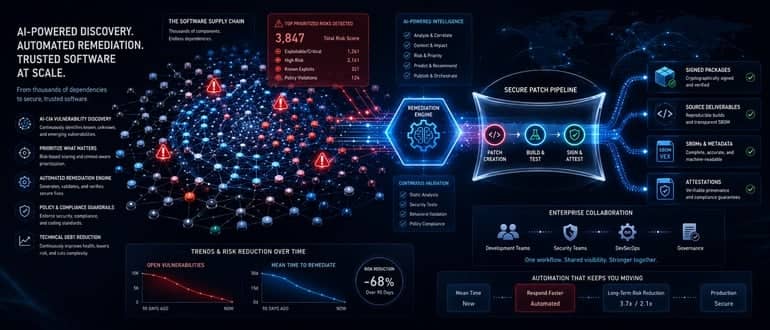
IBM and Red Hat Launch Lightwell Catalog to Automate Remediation
IBM and Red Hat this week revealed that Lightwell Network, a catalog of more than 6,500 application-layer dependencies that drives an automated vulnerability remediation service, is now generally available. At the same time, the Lightwell Clearinghouse Premier service, through which application development teams can both access validated patches and coordinate remediation efforts, is now available […]
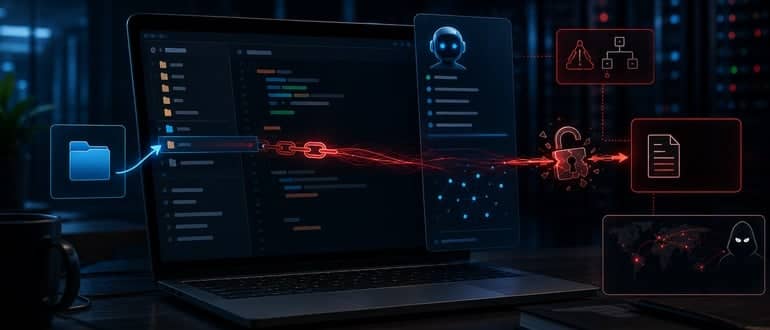
GhostApproval Flaw Featuring Decades-Old Feature Found in Six AI Coding Tools
A security flaw found in six popular AI coding agents can let attackers abuse a decades-old feature in Unix to trick an AI agent into giving them control of a developer’s system. Researchers with Google-owned Wiz said the vulnerability, dubbed “GhostApproval,” relies on symbolic links – or symlinks – a file system feature that has […]
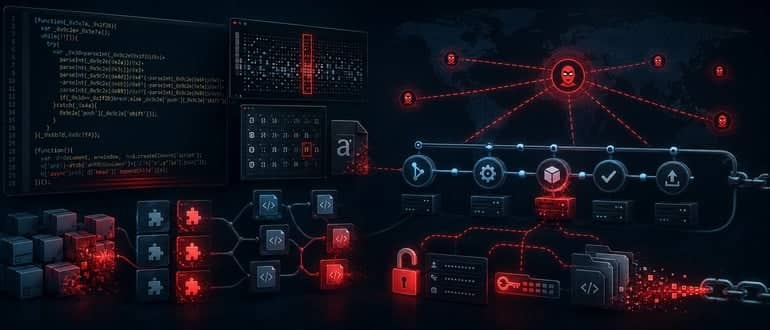
North Korea Expands the Reach of PolinRider Supply Chain Attack Campaign
The North Korean-sponsored threat groups behind the long-running fake interview scams targeting developers are expanding the PolinRider supply chain campaign that has escalated over the past several months. Reports from cybersecurity vendors Socket and Rescana found that two groups linked to the Democratic People’s Republic of Korea (DPRK) have published at least 108 malicious packages […]
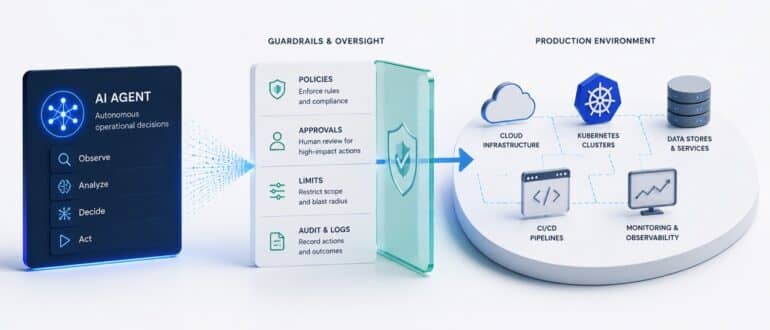
When AI Agents Get Production Access: The Next Big DevOps Risk
It wasn’t that long ago that AI assistants just watched from the sidelines. They could answer your questions, explain how things worked, sum up logs, and write deployment scripts. Handy, sure, but the real decisions? Still up to the engineers. That’s changing now. AI agents are stepping right into the heartbeat of operations. They can […]