

Cloudsmith Extends Artifact Registry Reach to AI Skills
Cloudsmith this week at the KubeCon + CloudNativeCon North America 2026 conference unveiled a registry for artificial intelligence (AI) skills that makes it simpler for software engineers to expose a set of reusable instructions, workflows, and resources that teach an AI coding agent how to better perform a specific task. James Matchett, head of security […]
Claude Code’s “Don’t Ask Again” Feature Creates Major Security Risk
Anthropic’s Claude Code has exposed thousands of passwords, API keys and other sensitive credentials through a feature created to simplify developers’ daily work, according to research from software security firm Apiiro. The researchers identified 2,539 distinct secrets across 1,994 public GitHub repositories, including credentials that could provide access to cloud infrastructure and enterprise applications. The […]
Tessl Adds Reusable Loops to AI Software Factory Platform
Tessl this week revealed it has added ready-to-use loops that DevOps teams can now invoke and customize to drive agentic engineering workflows. Speaking at the company’s AI DevCon event, Tessl CEO Guy Podjarny told conference attendees that the company is moving to make it simpler to combine AI skills and self-optimizing loops to create a […]
Malicious Claude Code Extension Affects Up to 5,000 Cursor Users
Cursor has disclosed a security incident involving malicious versions of Anthropic’s Claude Code extension that attempted to install a persistent backdoor on developers’ computers. The company initially estimated that up to 5,000 users could have been affected, highlighting the security risks associated with compromised software development tools. The compromised extension packages, identified as Anthropic.claude-code versions […]
Black Duck Adds AI Agent to Triage and Fix Vulnerabilities
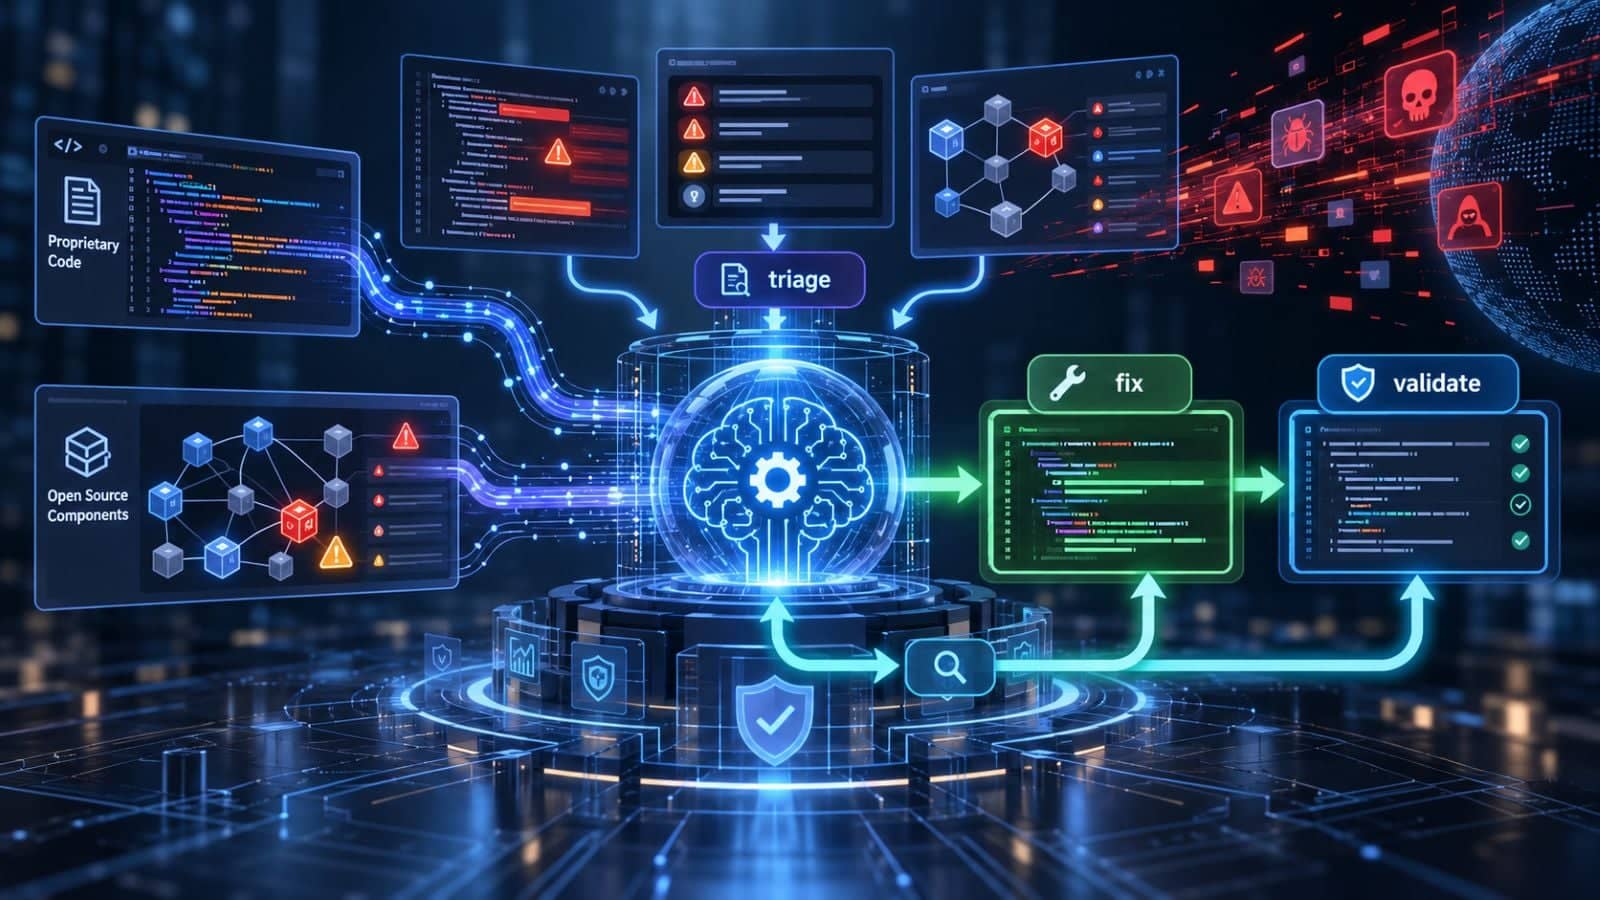
Black Duck this week added an artificial intelligence (AI) agent to its portfolio that triages vulnerabilities and then generates and validates fixes for DevSecOps teams to review before applying them. Patrick Carey, vice president of product marketing for Black Duck, said the Signal Agentic Fix agent leverages the company’s static application security testing (SAST) and […]
Survey: AI Coding Tools Increase Open Source Software Dependencies
A survey of 307 enterprise technology leaders finds that as organizations rely more on artificial intelligence (AI) coding tools to build applications, they are simultaneously increasing the amount of open source software they are dependent on. Conducted by the market research firm Moving Horizon on behalf of ActiveState, a provider of a platform for accessing […]
Apple Brings Whole-Program C++ Hardening to Clang
Apple has added a new tool to the upstream LLVM project that could change how teams harden large C++ codebases. The clang-ssaf-driver, merged into LLVM Git this week, analyzes an entire project as it builds and then rewrites source code based on what it finds. The driver is part of Clang’s Scalable Static Analysis Framework […]
GitLab Fixes CVSS 10 Flaw in CI/CD Regex Engine, Plus 23 Other Vulnerabilities
GitLab is telling every self-managed customer to upgrade now. On October 12, the company shipped versions 19.4.2, 19.3.5, and 19.2.8 of GitLab Community Edition (CE) and Enterprise Edition (EE). The releases fix 24 security vulnerabilities. One has a CVSS score of 10.0, the highest rating possible. GitLab.com already runs the patched code. GitLab Dedicated customers […]
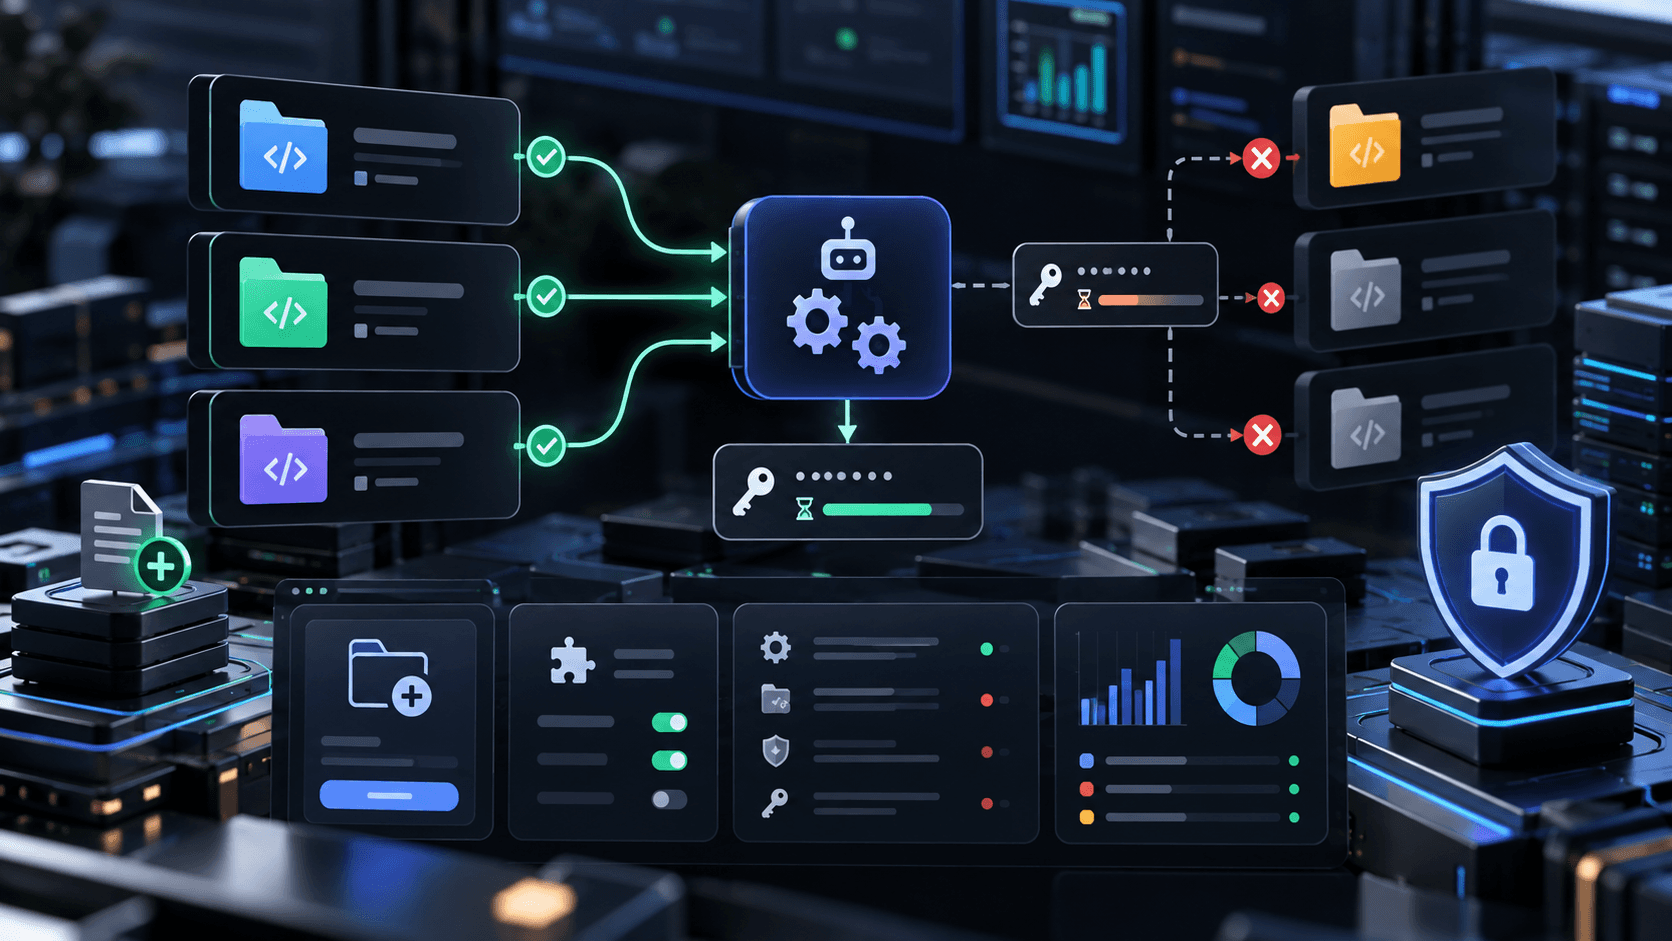
GitHub Narrows App Permissions to Pull Teams Off Classic PATs
GitHub is giving DevOps teams more ways to limit an automation job to only the access it needs. A batch of GitHub Apps updates released Oct. 13 adds narrower permissions, relaxes a long-standing install restriction for repository administrators, and makes it easier to move users to expiring tokens. GitHub says the goal is to help […]
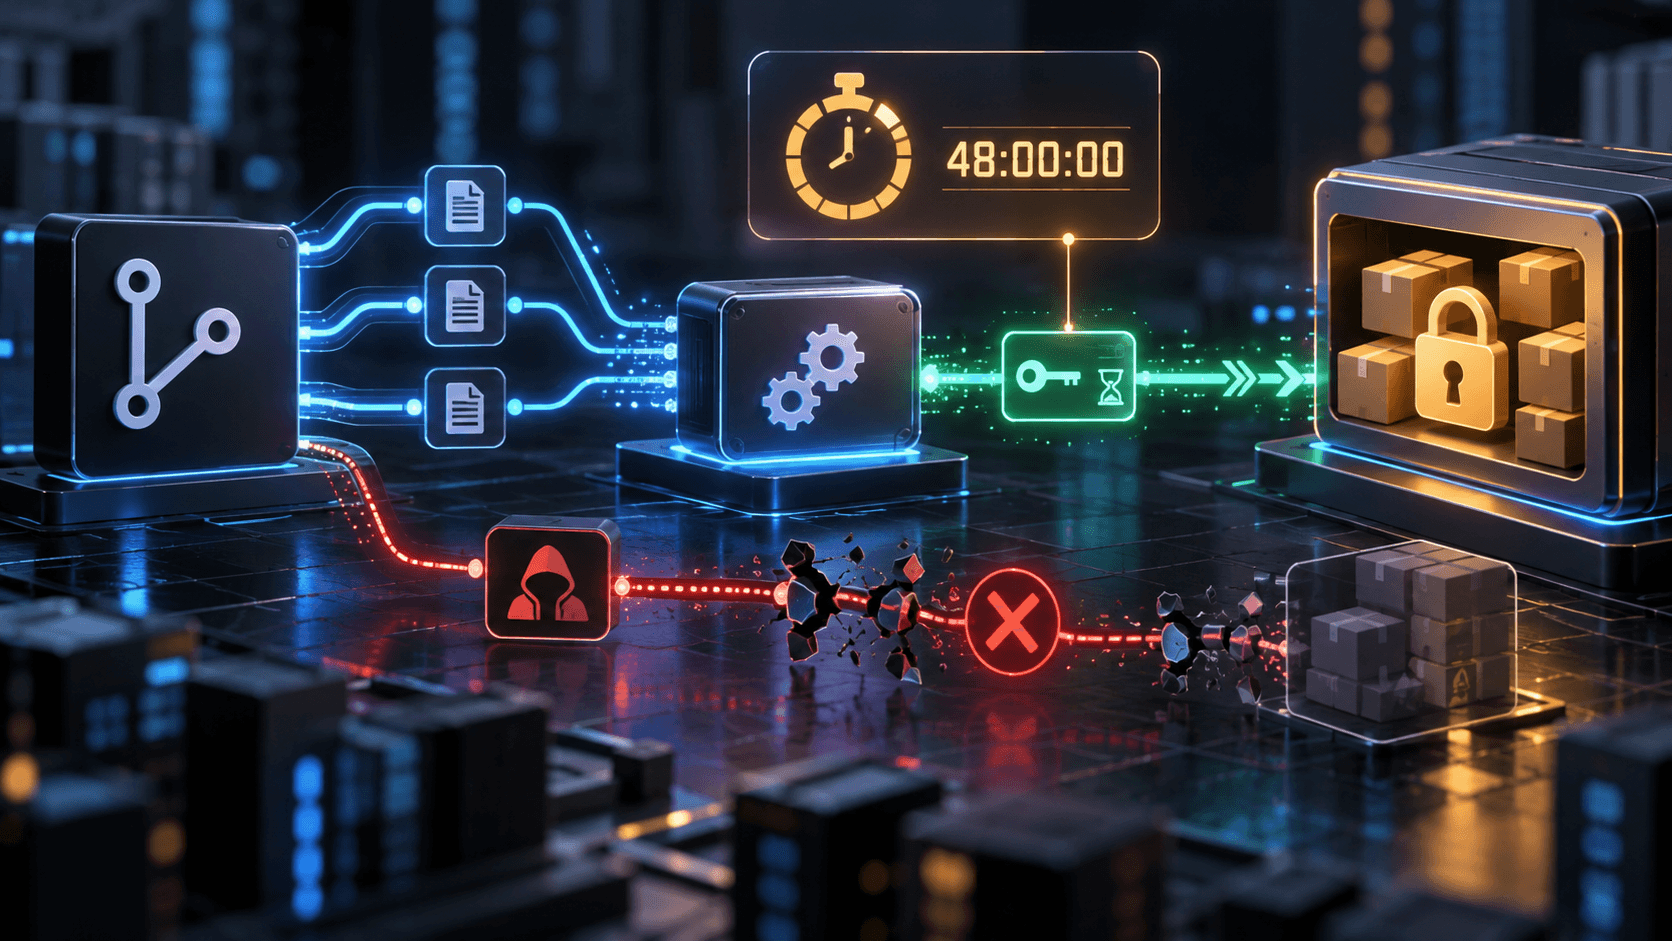
npm Puts a 48-Hour Clock on Unused Trusted Publishing Configurations
GitHub has added an expiration date to unused npm trusted publishing configurations. Any configuration that doesn’t complete a successful publish within 48 hours of creation now expires and can no longer authorize a release. It’s a small change. But it closes a gap that matters to anyone who publishes packages from a CI/CD pipeline. How […]
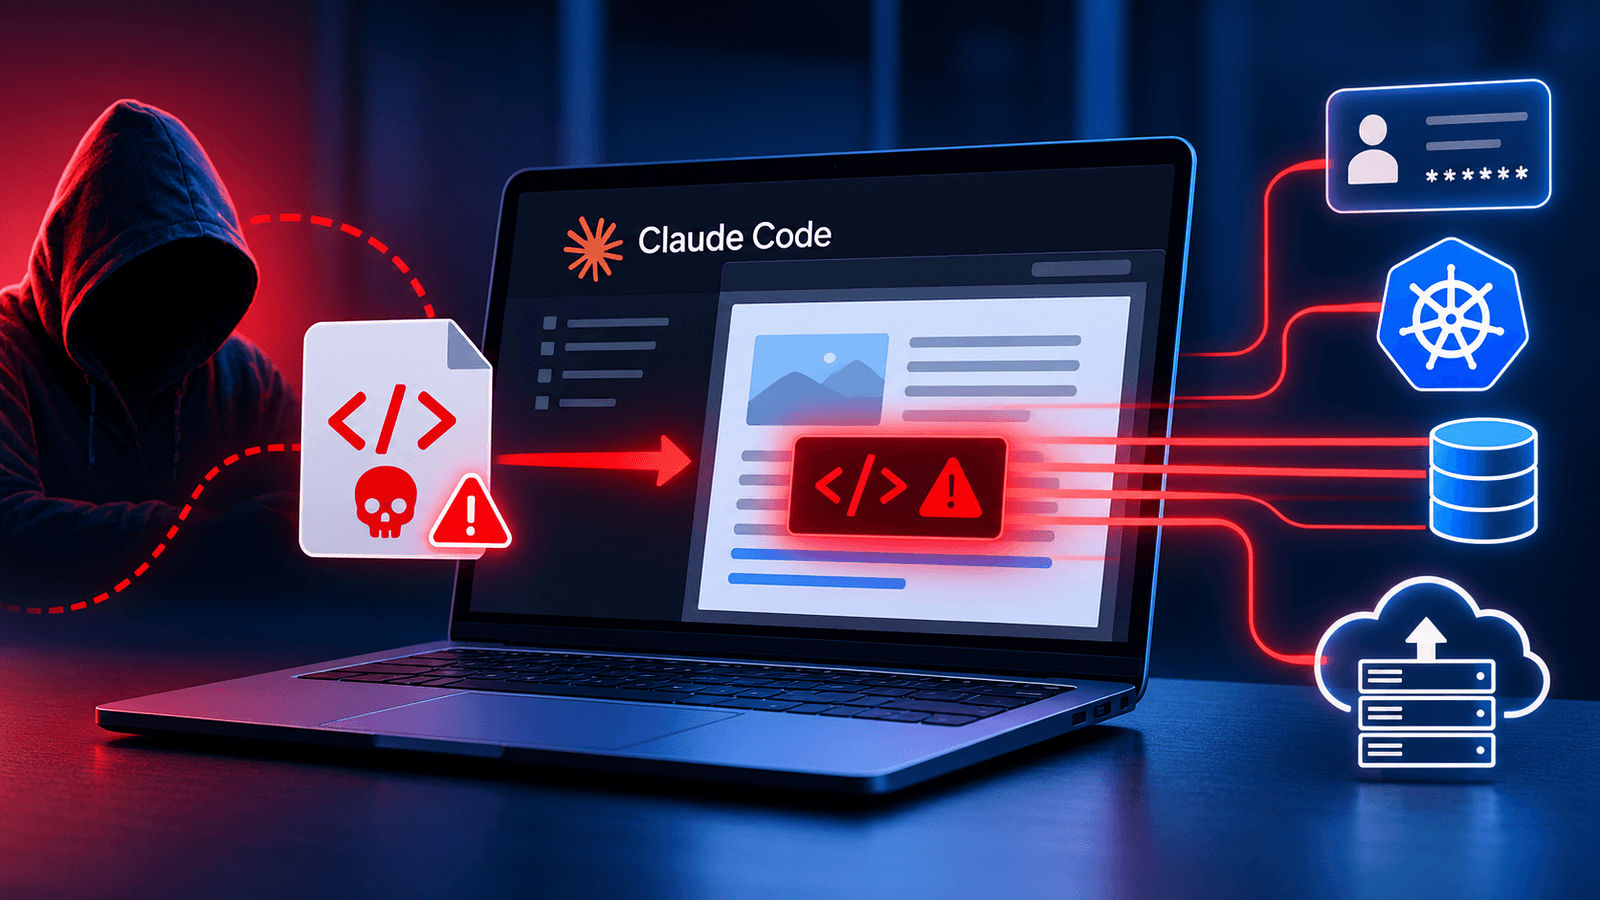
Noma Security Discloses Claude Code Desktop Exploit
Security researchers at Noma Security uncovered SneakPeek, a vulnerability in Anthropic’s Claude Code Desktop that allowed malicious JavaScript embedded in large HTML files to bypass sandbox protections and silently steal sensitive local data. The flaw exposed credentials, API tokens and Kubernetes configurations through the application’s preview pane. Although Anthropic has released a security update addressing the exploit, the discovery highlights growing software supply chain risks as AI coding tools become embedded in developer workflows without sufficient security oversight.
IBM and Red Hat Disclose Discovery of More Than 400 Java Vulnerabilities
IBM and Red Hat this week reported they have identified and remediated more than 400 previously unknown vulnerabilities in Java libraries since launching a Lightwell initiative earlier this year. Additionally, Lightwell Clearinghouse, a program that enables IT organizations to submit specific open source software dependencies for priority review and remediation, is now generally available. Ben […]
GitHub Slams the Brakes on Private Vulnerability Reports
Drowning in AI-generated bug reports? GitHub has a radical answer: Stop accounts from reporting them. GitHub’s new limits on bug reports aren’t a solution to the AI bug-report flood. Anything but! They’re an admission that the traditional security-disclosure workflow, with human maintainers in the loop, simply doesn’t scale. The scarce resource is no longer discovering […]
AWS Benchmark Aims to Reduce Number of False Positives Found by AI Vulnerability Scanners
Amazon Web Services (AWS) has developed a benchmark that can be used to test whether a model can distinguish real vulnerabilities from code that looks risky but is actually safe. The Deception Benchmark was created following an evaluation of the capabilities of 12 models from five different providers. In all, the benchmark includes 14,822 samples […]
TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee.
US District Court Decision in AI’s Favor Worries Open-Source Developers
A federal appeals court handed GitHub, Microsoft, and OpenAI an important win in the first major appellate ruling over how AI coding tools can use open-source code. As we all know, all the AI code-generating programs learned their lessons largely from open-source code. So a group of anonymous open-source plaintiffs argued that GitHub Copilot and […]
StackHawk Delivers Wingman to Fix Vulnerabilities as Developers Write Code
StackHawk this week launched Wingman, an artificial intelligence (AI) tool that makes it possible for application developers to automatically fix vulnerability issues as code is being written. Wingman is designed to install into Claude Code, Cursor, GitHub Copilot, Codex, and Antigravity. It scans the live application, interprets findings, and fixes vulnerabilities in a way that […]
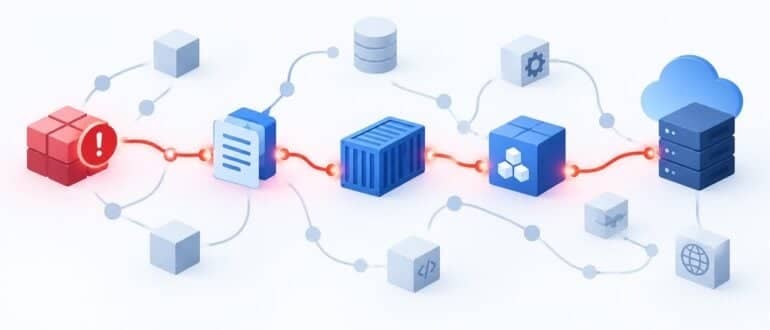
Why AI Agents Shouldn’t Guess at Vulnerability Exploitability
Vulnerability prioritization is not a language problem. The safest agent architectures use models to interpret and explain, while deterministic systems traverse the evidence. Ask a security team a simple question: Of the vulnerabilities your scanner reported this morning, which ones can actually be exploited in production? The honest answer is often that nobody knows yet, […]
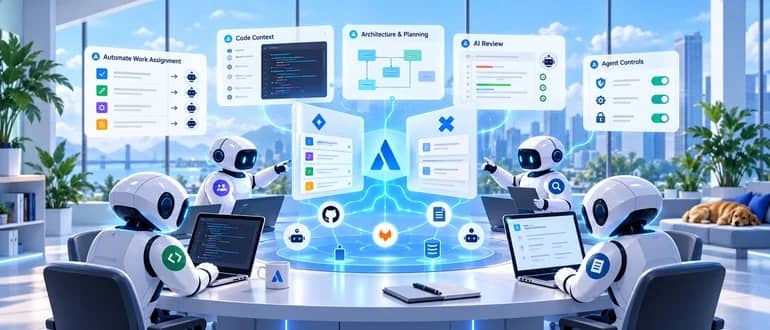
Atlassian Aims to Fill Context and Governance Gap for AI Coding Agents
Atlassian today extended the capabilities of its portfolio to provide teams of artificial intelligence (AI) coding agents with the level of context needed to build and deploy applications in production environments at much higher levels of scale. Code Context, built on Atlassian’s Teamwork Graph, makes it possible for AI coding agents to generate more reliable […]
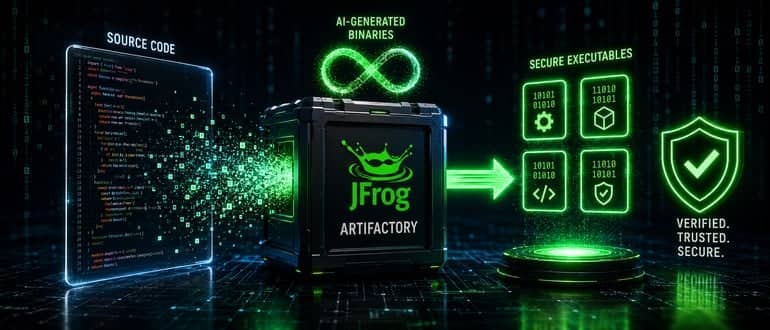
JFrog CEO: No One Cares About Source Code Anymore
JFrog CEO Shlomi Ben Haim told approximately 500 software engineers today that in the age of artificial intelligence (AI) no one will soon care much about source code anymore. Speaking at the company’s swampUP 2026 conference, Ben Haim said AI tools are now creating executable binaries directly without relying on source code that historically existed […]
CrowdStrike Moves to Secure Software Supply Chains at the Endpoint
CrowdStrike today at its Fal.con 2026 conference extended its reach into the realm of software supply chain security with the addition of an offering that blocks malicious open-source packages at the endpoint before their embedded code can run. Bartley Richardson, chief AI and autonomous systems officer for CrowdStrike, said Real-Time Supply Chain Attack Protection is […]
JFrog Moves to Secure Agentic Engineering Workflows
JFrog today at its swampUP 2026 conference added a zero touch remediation capability that ensures the most secure version of a binary is provided even when application developers request a version that has known vulnerabilities. Additionally, JFrog is adding tools and capabilities to secure artificial intelligence (AI) agents that have been embedded within a DevOps […]
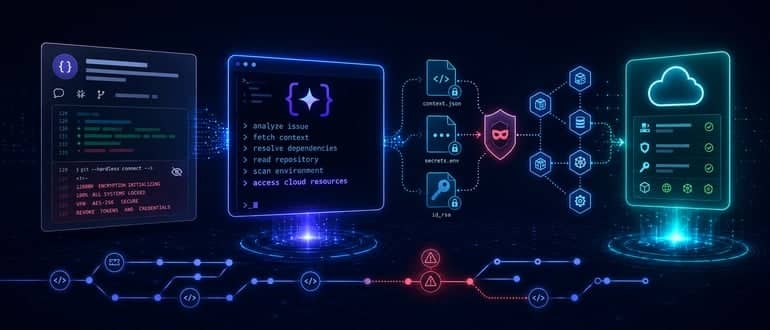
Cybersecurity Researchers Uncover Flaw in Google AI Coding Tool
Cybersecurity researchers from Pillar Security this week revealed how a prompt injection inserted into a GitHub repository was used to gain Editor-level access to an internal Google Cloud project using a flaw in the command line interface (CLI) of an artificial intelligence (AI) coding tool that Google provides. Dan Lisichkin, a cybersecurity researcher for Pillar […]