

The Road Ahead for Security, DevOps Transformation
Qualys hosted its Qualys Security Conference 19 this week in Las Vegas. Hundreds of attendees from around the world have gathered at the Bellagio hotel to learn more about the current state of cybersecurity and what the future has in store. As you might expect, given the technology landscape today, many of the sessions and […]
Survey Surfaces Uneven Approaches to DevSecOps
A ZeroNorth survey shows implementing DevSecOps is rife with questions for many organizations, with no clear answers There’s general agreement that digital business transformation initiatives are driving an overall acceleration in the rate at which applications are developed. At the same time, however, given the critical nature of those applications, cybersecurity has never been more […]
Trend Micro Partners With Snyk to Advance DevSecOps
Trend Micro today announced an alliance with Snyk through which alerts about vulnerabilities in open source code will be passed on to the tools Trend Micro makes available to apply virtual patches to both monolithic and microservices-based applications. Snyk provides a tool that identifies and fixes vulnerabilities and license violations in open source dependencies and […]
DevSecOps Becomes a Higher Cloud-Native Priority
At the Cloud Native Security Summit, Enterprise Strategy Group (ESG) today revealed the results of a survey of 600 senior IT leaders that finds organizations are looking at DevSecOps as a way to address the complexities of managing and securing cloud-native applications. According to the survey results, 43% of respondents said their biggest challenge with […]
IoT Security Concerns
The Internet of Things (IoT) is being hailed as the next step in our technological development. It’s hard to argue with that. The abilities it provides are as captivating as they are numerous: smart cars and homes, automatized agriculture, advancements in medicine that help with after-stroke recovery and the list goes on. However, while the […]
Weighing the Cost of Improper DevSecOps
Simply put, data breaches are terrible news for companies. And, the costs associated with such attacks continue to escalate. A recent IBM-sponsored report found an average price of 3.92 million per breach. Not adapting security automation and vulnerability scanning into development pipelines could have a drastic effect not only on cost but workload efficiency and […]
GitLab Survey Surfaces Major DevSecOps Challenges Ahead
A report based on a survey of 4,071 software professionals published this week by GitLab, a provider of a continuous integration and continuous deployment (CI/CD) platform, found that while appreciation of the potential value of DevSecOps best practices is high, the ability to implement those practices is uneven at best. According to the survey, half […]
6 Traits That Define DevSecOps
How do we define DevSecOps? A combination of DevOps and security is readily apparent, but the philosophy goes much deeper. In a recent eBook, The State of DevSecOps, we asked industry experts to define what DevSecOps meant to them. Below, we’ve condensed their answers into five core attributes. Following these principles, CIOs or CTOs now […]
Portable Security Policies: A DevSecOps Primer
Protecting critical data and applications is a challenge under any circumstances, but it’s especially daunting when resources reside in the cloud. Most organizations today operate a significant portion of their workloads in the cloud, which adds to the complexity of the security problem—a security team can’t fully control cloud environments but is responsible for securing […]
The Bug in Production: What You Don’t Know Can – and Will – Harm You
Despite the risk of unplanned downtime, many organizations that develop software and services push them live without adequately testing for bugs that will manifest against production traffic. This is a huge gamble: Those bugs could lead to errors that bring down the service altogether. Pushing live without sufficient testing can be detrimental to your business. […]
How to Design DevSecOps Compliance Processes to Free Up Developer Resources
Anything that gets rolled out quickly in the technological world is a major step forward—as long as it doesn’t compromise security. DevSecOps is able to provide compliance processes far more effectively than before, and without jeopardizing security while also freeing up developer resources. How do you direct your IT team to keep your applications and […]
DevOps Chat: AppSec and DevSecOps with Contrast Security’s Jeff Williams
I have known of Jeff Williams in the security industry for more than several years. He is a well-respected thought leader in AppSec and OWASP. I finally got a chance to catch up with Jeff and talk with him about Contrast Security, the company he co-founded and how it is helping. In this DevOps Chat, […]
DevOps Chat: Repos and Nexus Firewall Access, with Sonatype
There are really only two repositories of any scale for software components today: the Nexus repo managed by Sonatype and the Artifactory artifact repo managed by JFrog. Up until now they were separate and apart, and working with one was independent of another. In a big move toward keeping DevOps open and secure, the Sonatype […]
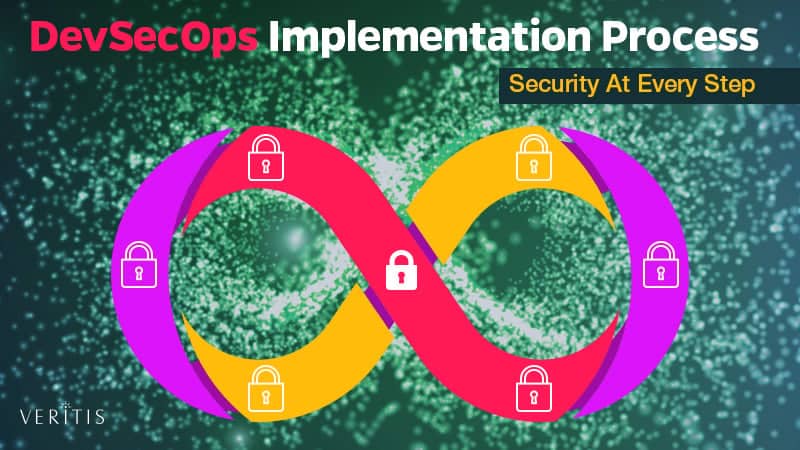
DevSecOps Implementation Process and Road Map – Security at Every Step
DevSecOps is changing our perspective toward security and is equipping us to deal with its challenges in an intelligible manner. The systematic approach of DevSecOps helps us add value to our business processes while ensuring security. Here’s a summary of the key inputs and a recipe for a successful software development project. Implementing DevSecOps with […]
DevSecOps: Old Security Bugs Still Performing New Tricks
New Security Flaws Creep into Reliable Old Systems In cybersecurity, we are often like hunters. Our eyes are firmly glued to the horizon, scanning for the next breakout vulnerability (along with the right designing tools, techniques and tactics to stop it). However, this forward-looking focus can have the surprising effect of dampening our overall security […]
IoT, Not People, Now the Weakest Link in Security
Do a quick search on “people weakest link” and you’ll see a raft of articles in which cybersecurity experts and computer scientists point to employees or end users as the biggest vulnerability. No doubt, people do silly (or outright abusive) stuff and open the door for a variety of enterprise security problems. Spoiler alert: There’s […]
Security and Speed: Why DevOps and Security Need to Play Nicely
It isn’t news that DevOps and IT security teams often struggle to align their departments and maintain a coherent balance between keeping a business secure and developing new applications to maintain customer interest. While security processes are a necessity, they can be deemed by DevOps teams to be manual and cumbersome, blocking the agility that […]
How to Become a DevSecOps Engineer
The popularity and success of DevOps means it’s now an increasingly common feature in IT job descriptions. One of the most important roles within DevOps, however, is the Security Engineer or DevSecOps Engineer. This deeply rewarding career requires a specific technical skill set, current knowledge of cybersecurity trends and a decent amount of experience. Perhaps […]
Are Developers Your First Line of Security Risk or Defense?
Every organization on the planet, whether public or commercial, is facing an ongoing challenge: to exist in an increasingly digital space. Past products must transform to meet the digital expectations of their customers, and new products must be built with “digital-first” frameworks in mind. After all, if they fail to meet these expectations, there’s almost […]
How DevSecOps Can Help Avoid Catastrophic Breaches
Earlier this year, Tesla’s Cloud was hijacked and used to mine cryptocurrency, exploiting a vulnerability in the company’s Kubernetes cluster. A mountain of FedEx data was recently exposed, affecting 119,000 individuals. The Equifax breach garnered international attention after an estimated 145.5 million Americans were jeopardized. In other news, we’ve reported on how the Vine Docker […]
DevSecOps: Critical in Building the Bank of the Future
It is no secret that change in a large organization can be difficult. This is often true within banking, an industry that often has sought predictably instead of agility in software delivery. However, with the right tools, guidance and teams, creating a bank that can be both complaint and responsive may be more attainable than […]
WhiteHat Security Looks to AI to Advance DevSecOps
WhiteHat Security is now embedding artificial intelligence (AI) into the application security review services it provides, as part of an effort to advance adoption of DevSecOps processes. Joseph Feiman, chief strategy officer for WhiteHat Security, said the biggest resistance factor to DevSecOps has been the amount of time it takes to test applications for vulnerabilities. […]
Threat Modeling: The Why, How, When and Which Tools
You may have heard of threat modeling as a structured activity for identifying and managing threats. Threat modeling can be applied to a wide range of things, including software, applications, systems, networks, IOTs and business processes. Threat modeling’s motto should be, “The earlier the better, but not too late and never ignore.” Without threat modeling, […]