

DevSecOps: Embedding a Security Practice into your DevOps Approach
It’s a no-brainer that the element of security cannot be compromised even to the smallest of extents in today’s competitive, fast-paced, modern technology-driven IT infrastructure. However, to keep up with the rapid developments of other processes in this agile world, security is often given relatively less importance and in some cases, even left behind. As […]
There’s No Such Thing as DevSecOps
Should DevSecOps be categorized separate from DevOps? After years of debate, few doubts remain about the viability of the public cloud for enterprise workloads. Enterprises are shifting to cloud-first and cloud-only strategies, looking to take advantage of all the good the public cloud has to offer. For applications built and deployed in the public cloud, […]
451 Research Report Highlights Value of DevSecOps for the CI/CD Pipeline
One of the compelling benefits of DevOps for many organizations is speed. Between breaking down silos, streamlining processes and automating routine tasks, the process of developing and deploying software can be significantly faster. A new report from 451 Research and Synopsys, however, points out the value of incorporating DevSecOps in the equation, especially with continuous […]
Simplify DevSecOps with a Zero Trust Approach
There are major cyberattacks and data breaches weekly, if not daily. Each incident is unique in some way, but one element common to almost all successful attacks is trust. Whether it’s a disgruntled employee conducting an insider attack, an attacker infiltrating the network using stolen credentials or an exploit that leverages a third-party vendor or […]
Barracuda Networks Survey: DevSecOps Is Hard
Organizations that have adopted DevSecOps processes may be making progress when it comes to improving cybersecurity, but it’s far from easy. A survey of 618 IT decision-makers conducted by Dimensional Research on behalf of Barracuda Networks, a provider of IT security software and appliances, finds half have adopted either DevOps, DevSecOps or a continuous integration/continuous […]
DevOps in the Cloud: Security’s Groundhog Day
Throughout the internet age, enterprise IT has given security a lower priority than qualities such as speed-to-deployment, scalability, availability and usability. We first saw this in the late 1990s and early 2000s, when IT teams rushed applications onto the web. Amid the glee surrounding the potential of fancy new internet architectures, few thought about the […]
How to Make Your Software HIPAA-Compliant
Creating software for the healthcare industry must always follow strict requirements and limits set by both state regulators and medical organizations. In this article, we will focus on becoming compliant with HIPAA (the Health Insurance Portability and Accountability Act of 1996) by building a proper IT solution for corresponding institutions, while also considering the HIPAA […]
DevSecOps and DevNetOps: New Heroes in the DevOps Saga
The evolution of DevOps is by no means done, but it’s safe to say that there is enough agreement and acceptance to declare it a hero. DevOps has helped glorify IT to the point where it’s no longer preventing business, nor a provider nor a partner of the business. Often IT is the business, or […]
SecOps: The Next Stride for DevOps
Global IT spending is now touching a figure of $4 trillion. In today’s technology-intensive environment, data is the biggest commodity, more valuable and powerful than ever. And like Peter Parker’s uncle Ben noted, “With great power comes great responsibility.” Security has always been a big concern for valuable things and IT is no exception. IT […]
Elasticsearch Ransomware Attacks Highlight Need for Better Security
Recently, reports surfaced that a large number of Elasticsearch servers fell victim to potential ransomware attacks. Ransomware is the type of malware a company doesn’t want on its systems or network. It takes systems hostage, most commonly by encrypting or stealing data, and exposes the owners to blackmail attempts. According to a report by the […]
Lean Security: How Better Development Can Protect Your Business
If companies are to reach their strategic goals—reducing time to market, boosting sales, improving product market fit and brand image, and cutting cybersecurity costs—then it’s time for a new outlook on software security. Today’s business leaders must learn to see security for what it is: A differentiating factor. Companies with reputations for secure developmental processes […]
The Cost of Not Building with Security in Mind
The unfortunate reality for today’s organizations is the fact that a security breach is bound to happen. Major breaches are happening with alarming frequency and fill the news headlines almost daily. And behind many of these major breach stories is a software vulnerability that has been exploited. There is a silver lining, however. Addressing security […]
Intuit’s DevSecOps: War Games and Culture Hacking
If you ever wanted to learn about Rugged DevOps (some call it DevSecOps), sit down for a spell with Shannon Lietz, Ian Allison and Scott Kennedy from Intuit. We discussed a number of important topics including internal war games, culture hacking, gamification of Rugged DevOps and starting as a small team. There are 100 gold […]
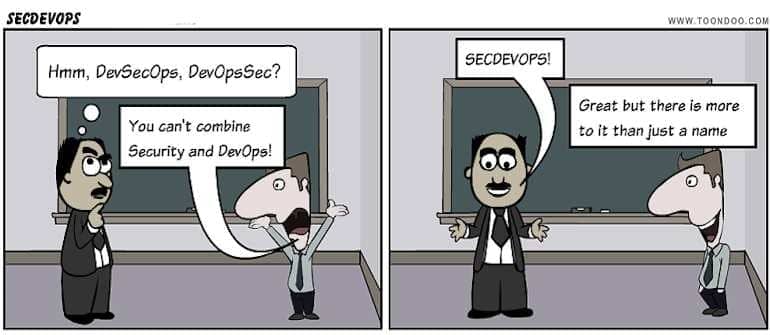
DevOps need to pay more attention to security
Ty Miller, founder of Threat Intelligence, suggests organisations adopting DevOps need to pay more attention to security. Over the last five years or so, the prevailing approach to IT security has changed – largely triggered by the activities of hacktivist groups such as Anonymous and LulzSec – and it is becoming an increasingly integrated part […]
Dev, Ops and Security Collaboration: Bring the body and the mind will follow
Complexity has a way of muddying even the clearest of waters, and this has certainly been the case with IT Operations. While Dev, Ops and Security teams share a common purpose, the silos between them are so deeply entrenched, it’s easy to see how they have forgotten that they are working towards the same end. […]
Hacking Your Auditor
No, not that kind of hacking, give me a little credit… Recently I was having a conversation with a consulting friend about DevOps, and he found himself in a bit of a tough situation. The organization he was working with was a pure cloud/DevOps shop, but one that was stepping into having the meet compliance […]
Why Baking Security Into the DevOps Framework is Vital to Its Success
I attended my first official DevOps conference in Israel in September 2013. But I was initially introduced to DevOps by my customers – firewall and network managers who, through their efforts to automate security policy management, found themselves dealing with a new and like-minded set of IT stakeholders – DevOps teams. They said DevOps was […]