

Continuous Security Key to Defending Your Data Well
Defending data isn’t easy. If it were, we wouldn’t see new data breach headlines on a weekly—or sometimes even daily—basis. That said, defending data also isn’t rocket science. A new report from Nuix highlights some of the major concerns with protecting data, and also illustrates some of the ways in which consistent vigilance is half […]
DevOps Security: Five steps to bridging the gap between teams
Enterprise security and DevOps teams have traditionally operated separately with little to no engagement, often making it difficult to quickly identify and respond to potential vulnerabilities in applications and software. In my last column, I highlighted the value of introducing security to the DevOps process to reduce bugs and vulnerabilities before code hits production. By […]
Why do you need to implement a DevOpsSec team?
Just 20 years ago, organizations relied on a single wall of defense to secure their applications and networks. Fast forward to 2015 and that large fence is no longer adequate. With the proliferation of mobile, cloud and SaaS technology adding to the complexity of ever-advancing systems and networks, it becomes much more important that teams […]
Making the Case for Secure, Defect-Tested Software Development
Creating a software security initiative in any organization is no easy feat. Often times, organizational culture or politics can provide development managers with a strong counterargument for implementing software security concepts. Unfortunately, building software without a consideration for security has become a less viable option given the increase in compliance pressures and widely publicized data […]
A DevOps Coders Time Allocation
Here are some other ROELBOB’s you might like A Unit Testing Dillema The Pink Slip Another Pink Slip Hot off the Press – Other great DevOps.com content DevOpsSec: 1 in 16 Chances CIOs Must Fight for Relevance in Face of Tech Storms Upcoming DevOps.com Events Webinar: SecDevOps: The Marriage of SecOps […]
Getting Rugged DevOps Right
Two Perspectives Jack, an accomplished application security pro, tells me, “The developers won’t talk to us. It’s like we speak a different language. They are releasing new builds so fast, how could they check each one for security vulnerabilities? We can’t move as fast as they do.” Then in the next moment, Diane, a DevOps […]
DevOpsSec: Survival is Not Mandatory
Deming, the patron saint of DevOps once advised, “It is not necessary to change. Survival is not mandatory.” To survive, application development teams are constantly pressured to deliver software even faster. But fast is not enough. The best organizations realize that security, quality and integrity at velocity are mandatory for survival. Hence, DevOpsSec My aim […]
All Systems Fail*
Vince Lombardi once said, “It’s not whether you get knocked down, it’s whether you get up.” But in today’s world of high velocity development and release practices, it’s also about how fast you can get up. Today, we are seeing more news about sites from major online retailers and service providers like HP, Target, PayPal […]
Bridging the gap between DevOps and Security
Security should be baked into the DevOps process, from tools to skills to collaboration. DevOps and security are not mutually exclusive. The problem with digital innovation is that considerations for compliance come later, after the product or service is on the market. From public cloud infrastructure to Internet of Things to mobile apps and even […]
What approach to application hardening is right for your organization?
There’s no shortage of readily available hacker tools and techniques and stories in the news about mobile app hacks for both the iOS and Android platforms. Fortunately, security solutions providers have responded swiftly and there are many approaches that one can leverage to harden an app that is “out in the wild.” For those of […]
Combining SecOps and DevOps
Security has to be top of mind for most any company that is moving, or has moved, to the cloud. And, businesses know they need to act swiftly to ensure that any new products or services they’re dreaming up do not expose them to risk. How can they do that when the fast-moving nature of […]
Avoiding Common AWS Security Risks
According to IBM’s Cyber Security Intelligence Index, 95% of all security incidents involve human error. That’s beyond significant, and when rapidly deploying multiple iterations in a DevOps shop, that means there are lots of opportunities to fail. Our own independent analysis based on customer configuration data shows that security control mechanisms Amazon Web Services (AWS) makes available […]
AWS re:Invent – New Releases Drive Cloud Security Innovation
The recent AWS re:Invent conference in Las Vegas saw the release of several new AWS services for security. Some of these announcements such as AWS Web Application Firewall and AWS Inspector seemed to take many in the security press and blogosphere by surprise. Cloud-native security companies like Evident.io however, weren’t surprised by these announcements. In fact, AWS […]
Upcoming SANS Webinar: Orchestrating Security in the Cloud
Organizations are increasingly migrating to cloud-based services to handle sensitive data and business processes, meaning security teams need to carefully review and understand what security controls are available to help protect them. Given the pace of cloud adoption, security teams need to increase security automation efforts and employ tools that can better secure their cloud […]
Alert Logic Cloud Insight brings cloud-based security to your cloud infrastructure
One of the primary driving forces behind DevOps is its fluidity. There is a domino-effect that cascades from the developers who create the apps to the IT admins who deploy and administer the apps to the individuals who download and use the apps and back again. Traditional security can’t keep pace so Alert Logic created […]
Alert Logic lends more agile, cloud-native security to DevOps architects
Amid the avalanche of research and product news emerging from this year’s Black Hat USA 2015 conference, held in Las Vegas this week, at least one vendor is attempting to advance a new solution aimed at empowering DevOps architects to streamline and improve security workflow. Houston-based Alert Logic announced the release of its Cloud Insight […]
The Software BOM Squad
In my previous post, “When Good Code Goes Bad“, I shared new research showing the average large development organization consumes over 15,000 known vulnerable and defective components annually. While we can’t stop software from going bad, there are practices from traditional manufacturers that we can use to improve our ability to recall and fix the “bad” […]
The Cost to DevOps: 27 Mufflers
Imagine Imagine that you are designing the 2016 Range Rover line of sport utility vehicles. Like all gas powered vehicles, each one needs an exhaust muffler. Range Rover likely has narrowed in on a preferred provider of mufflers. But imagine what would happen if the designers and factory line workers could pick from any one […]
Bring Your Own Exploit
Here’s a simple question: for each tool that your organization uses, have you (or someone else on your DevOps team) changed the default passwords? That should be a no-brainer, shouldn’t it? Of course you changed them! Or at least you changed them for the tools that looked like they would have default passwords. Well, OK, […]
Security Breaks DevOps – Here’s How to Fix It
The concepts of communication, collaboration, abstraction, automation and orchestration are cornerstones of the rapidly growing DevOps movement. At the same time reliance on virtualized infrastructure and Infrastructure-as-a-Service has exploded, making manual provisioning and management simply not feasible anymore; it takes too long and locks up too many resources. Modern DevOps methods and tools have emerged, […]
Stop whining about shadow IT and do something about it
Much has been written about shadow IT at the business unit and employee level where the proliferation of cloud applications has all but eliminated IT’s control over what applications are used in their organization. The explosion of public cloud technologies has caused an identical revolt amongst development teams who no longer want to—or need to—wait […]
Managing Open source software components
Building any software need lots of efforts including resources, time, money, etc. It is really a great pleasure when it goes live or gets released. In parallel, there is always a chance that bugs may put the release in a difficult condition even after multiple rounds of testing. Teams can fix bugs related to software features […]
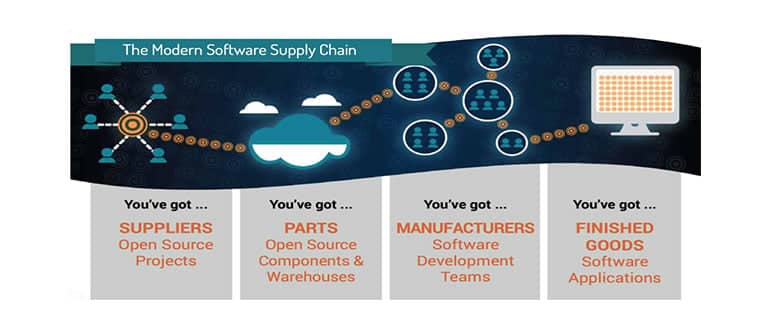
2015 State of the Software Supply Chain Report
In April of this year, I embarked on a six-week journey diving deep into an analysis of the world’s software supply chains. I evaluated the practices of 106,000 organizations, the 100,000+ suppliers they relied on, and the billions of software components that fueled their agile, continuous delivery and DevOps practices. The facts I discovered and […]